Security teams must protect collaboration platforms where thousands of messages, files, and integrations flow daily through channels that connect employees, contractors, and external partners. Attackers target these communication hubs through sophisticated techniques, such as compromised accounts masquerading as trusted colleagues, malicious OAuth (Open Authorization) apps requesting excessive permissions, and social engineering campaigns that exploit the speed of real-time messaging. These threats blend into normal collaboration patterns, such as those found in Slack, making detection particularly challenging without specialized behavioral monitoring.
Organizations need complete visibility across their Slack workspaces to identify anomalies before data exfiltration or account compromise occurs. Advanced threat detection extends beyond basic authentication to analyze communication patterns, application behaviors, and file-sharing activities that indicate potential security incidents.
This guide provides five proven practices that strengthen threat detection capabilities. Understanding how these attacks unfold, and the controls that catch them, is the starting point for closing that gap.
Key Takeaways
- Slack's real-time, authenticated environment gives attackers a direct path to sensitive data through compromised accounts, malicious OAuth apps, and social engineering that perimeter-focused tools cannot see.
- Signature-based security tools miss the behavioral anomalies that reveal a compromised account or an insider threat operating inside an already-trusted workspace.
- Complete audit logging, centralized security controls, and integrated compliance automation give security teams the visibility needed to catch incidents early and contain them fast.
- Connecting Slack activity to the broader security stack, through AI-powered behavioral analytics and enterprise infrastructure integration, turns isolated alerts into a coordinated response.
What Makes Slack Environments High-Value Targets for Attackers
Slack environments contain strategic planning discussions, customer data, and financial information accessible through a single compromised account. Enterprise implementations typically integrate with dozens of business applications, creating expanded attack surfaces through application programming interface (API) connections, OAuth apps, and webhook endpoints that each represent potential entry points for malicious actors. The consequences of a breach can be severe: in a breach that came to light in July 2024, a threat actor gained access to Disney's internal Slack workspace via a compromised employee computer, leaking 1.1TB of data from approximately 10,000 channels, including unreleased projects, financial data, credentials, and API links, ultimately leading Disney to announce it would stop using Slack entirely.
The platform's real-time messaging format creates optimal conditions for social engineering. Attackers impersonate trusted colleagues using familiar communication patterns, using existing channel context and ongoing conversations to craft convincing scenarios that employees rarely question. These targeted campaigns bypass traditional email security controls because they operate within an already-authenticated environment. Attackers increasingly extend social engineering attempts beyond email into voice calls, text messages, and workplace chat apps, widening the aperture security teams need to cover.
Security incidents on collaboration platforms trigger cascading impacts:
- Lost productivity during incident response
- Regulatory scrutiny for data exposure
- Erosion of employee trust in digital tools
The convergence of centralized sensitive data, extensive third-party integrations, and inherently trusted communication contexts turns these environments into high-value targets where a single compromise yields enterprise-wide access. The IBM Cost of a Data Breach Report 2025 puts the global average breach cost at $4.44 million, with breaches overall taking a mean of 241 days to identify and contain.
Why Traditional Security Approaches Fall Short for Slack Security
Traditional security controls rely on signature-based detection that misses behavioral anomalies indicating compromised accounts or insider threats within collaboration platforms. These conventional tools scan for known malware patterns while attackers operate through legitimate Slack features like sharing files, creating channels, and messaging teammates using authorized credentials.
Perimeter defenses protect against external threats but cannot detect malicious activity originating inside trusted workspaces. Once attackers gain access through stolen credentials or OAuth tokens, they move freely within authenticated environments where their actions appear normal to legacy security systems. The Cybersecurity and Infrastructure Security Agency (CISA) Scattered Spider advisory documented threat actors actively searching victim Slack workspaces for conversations about intrusions, and even joining incident remediation calls to monitor defensive activity in real time, something perimeter tools cannot detect.
Slack's real-time, conversational dynamics require behavioral analysis that understands context, communication patterns, and relationship graphs. Static pattern-matching cannot differentiate between legitimate urgent requests and sophisticated social engineering attempts that exploit workplace communication norms. Voice-based social engineering and AI-generated phishing content have both grown more convincing, increasingly eliminating the grammatical errors and awkward phrasing that once served as reliable warning signals. Modern threat detection must analyze subtle deviations in messaging behavior, access patterns, and integration usage to identify threats.
5 Best Practices for Slack Threat Detection
Closing the visibility gap in Slack takes a deliberate combination of monitoring, analytics, and integration that traditional perimeter tools were never designed to provide. The following practices give security teams the context and coordination needed to detect threats operating inside an already-trusted environment and contain them before they escalate.
1. Deploy Complete Audit and Accountability Controls
Enterprise Slack environments generate massive volumes of security-relevant events that require systematic monitoring for threat detection and compliance purposes.
Complete audit controls based on National Institute of Standards and Technology (NIST) frameworks turn this data into actionable intelligence. Organizations must collect real-time audit logs covering user authentication, file sharing, channel creation, and administrative actions across all workspaces. These logs feed into centralized security information and event management (SIEM) platforms that provide tamper-evident storage with cryptographic integrity protection. This keeps evidence admissible for investigations and compliance audits.
Behavioral analysis systems correlate these audit streams to detect suspicious patterns invisible to single-point monitoring. Unusual access sequences, bulk data downloads outside business hours, and administrative changes that deviate from established baselines trigger automated alerts. This multi-layered approach identifies insider threats and compromised accounts that traditional monitoring misses. The Ponemon/Sullivan Institute 2026 Cost of Insider Risks report found that the average annual cost of insider risk per organization now stands at $19.5 million with organizations that contain incidents in under 30 days spending an average of $14.2M compared to $21.9M for those taking over 90 days. Systematic audit and monitoring controls directly drive faster containment.
The combination of complete logging, centralized correlation, and behavioral analysis delivers three critical outcomes:
- Rapid threat detection through real-time alerting
- Simplified regulatory compliance reporting with complete audit trails
- Preserved forensic capabilities that support thorough incident investigations
2. Implement AI-Powered Behavioral Analytics
Traditional signature-based tools are unable to detect sophisticated insider threats, account compromise scenarios, or social engineering attacks that exploit Slack's conversational nature. AI-powered behavioral analytics addresses these gaps by learning normal communication patterns and identifying subtle deviations that signal malicious activity.
User and Entity Behavior Analytics (UEBA) establishes machine learning baselines for every user. These baselines include typical login times, communication frequency, channel participation, and file-sharing habits. When accounts suddenly access sensitive channels at unusual hours or download bulk data outside established patterns, the system triggers immediate alerts. This continuous learning approach adapts to legitimate behavior changes while maintaining sensitivity to genuine threats.
Advanced analytics engines examine multiple threat dimensions simultaneously:
- Natural language processing identifies phishing attempts hidden in casual conversation, a growing concern as generative AI shortens the time attackers need to craft a convincing message
- Graph analysis reveals unusual relationship patterns that suggest a compromised account
- Temporal analysis catches timing anomalies that indicate automated attacks or unauthorized access
These layered detection methods work together to surface threats that single-point analysis would miss.
This full behavioral approach improves security operations: false positives tend to drop as machine learning refines detection accuracy, while automated response capabilities contain routine incidents without human intervention.
3. Deploy a Centralized Security Control Framework
Security teams struggle to manage multiple collaboration platforms through separate administrative consoles, creating blind spots and inconsistent protection across communication channels.
A centralized security framework solves this problem by consolidating Slack, Teams, and other platform controls into one management system. Administrators configure security policies once and apply them everywhere: access controls, data loss prevention rules, and compliance settings automatically sync across all collaboration tools. This approach reduces the confusion of juggling multiple interfaces.
Centralized controls also automate routine security tasks:
- Access across connected platforms is revoked as soon as an employee leaves the company, without manual follow-up
- Security alerts from different collaboration tools flow into one dashboard for faster threat detection
- Compliance reports pull data from every connected platform automatically, saving hours of manual compilation
These unified systems reduce administrative work while helping consistent security policies protect conversations, files, and channels across the collaboration environment.
4. Support Regulatory Compliance Integration
Modern businesses must meet multiple compliance requirements across healthcare, privacy, and financial regulations. Each framework requires different controls, documentation, and reporting standards, which create operational complexity.
Integrated compliance systems manage these requirements through unified controls. Automated encryption protects sensitive communications across all channels. Data classification engines identify regulated information instantly, applying appropriate protection based on content type. Access controls adjust dynamically when financial data, health records, or personal information enters conversations.
Automation reduces the manual burden of routine compliance tasks:
- Sensitive messages receive encryption automatically
- Restricted documents trigger access limitations without administrator intervention
- External sharing stops when protected data is detected
- Compliance reports are generated on demand, documenting security measures for auditors and regulators
Organizations maintain continuous compliance through behind-the-scenes enforcement that protects data without disrupting workflows, freeing security teams to focus on strategic initiatives while automated systems handle routine compliance operations across Slack interactions.
5. Deploy Enterprise Security Infrastructure Integration
Security teams operate in silos when Slack threat detection remains disconnected from existing enterprise security tools. This isolation delays incident response and creates dangerous visibility gaps.
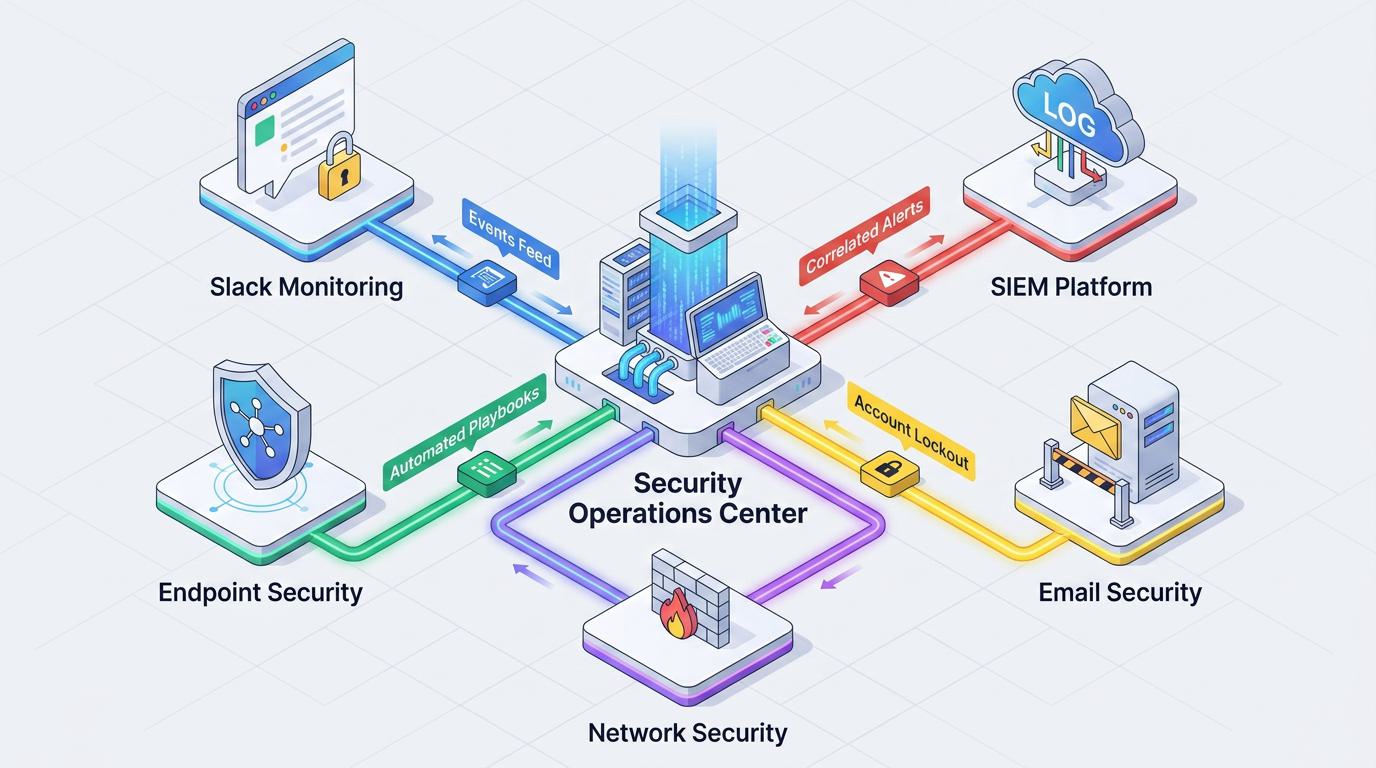
Integration frameworks connect Slack monitoring with an organization's broader security infrastructure. API connections feed Slack events directly into the SIEM platform, where they correlate with network, endpoint, and email security data. Suspicious Slack activity triggers automated playbooks that lock accounts, quarantine files, and alert security teams simultaneously.
This orchestrated approach improves incident response:
- A compromised account detected in Slack quickly triggers password resets across connected systems
- File-sharing violations launch automated investigations pulling data from multiple security tools
- Security teams see complete attack chains instead of isolated alerts
Organizations achieve faster threat containment through connected systems that share intelligence and coordinate responses automatically.
Building Resilient Slack Security Through Integrated Threat Detection
Slack and other collaboration platforms demand security built for how people actually communicate: in real time, across trusted relationships, and inside an already-authenticated environment. Behavioral analytics that learn normal patterns catch the account takeovers, insider risks, and social engineering attempts that signature-based tools miss, while centralized controls and compliance automation keep policy consistent across connected platforms without adding administrative overhead. Organizations that combine these capabilities gain the visibility to catch a compromise early and the coordinated response to contain it before it spreads.
Frequently Asked Questions
What Are the Most Common Slack Security Threats Organizations Face?
Organizations most often encounter compromised accounts used to impersonate trusted colleagues, malicious OAuth applications that request excessive permissions, and social engineering attempts that exploit the speed and familiarity of real-time messaging. Because these threats operate through legitimate, authenticated access, they frequently bypass security controls built for external, unauthenticated threats.
How Does Behavioral Analytics Improve Slack Threat Detection Compared to Traditional Tools?
Behavioral analytics builds a baseline of normal activity for each user, covering login times, communication patterns, and file-sharing habits, then flags deviations from that baseline. This approach catches account compromise and insider threats that signature-based tools miss, since those tools only recognize known malware patterns rather than unusual behavior on an already-authenticated account.
Can Slack Threat Detection Integrate with Existing Security Operations Tools?
Yes. API-based integrations connect Slack activity data with SIEM platforms and other security infrastructure, allowing Slack-based alerts to correlate with network, endpoint, and email security data. This gives security teams a unified view of an attack instead of isolated alerts scattered across different tools.
What Compliance Requirements Apply to Slack and Other Collaboration Platforms?
Collaboration platforms that carry healthcare, financial, or personal data are subject to the same regulatory frameworks that govern that data elsewhere, such as HIPAA, GDPR, or industry-specific financial regulations. Automated encryption, data classification, and access controls help organizations apply consistent protection to regulated information without manually reviewing every message.