Cloud access security brokers help organizations control how users and cloud data interact. As data spreads across SaaS applications and cloud infrastructure, teams need a consistent way to apply security policies beyond what cloud providers cover. A cloud access security broker (CASB) helps close that gap.
Key Takeaways
- A CASB gives organizations a way to apply consistent security controls across cloud applications and cloud data.
- Cloud access security brokers work through discovery and risk-based policy enforcement across multiple deployment models.
- The core functions of cloud access security brokers center on visibility, data security, threat protection, and compliance.
- CASB capabilities now commonly appear inside broader SSE and SASE platforms, but the underlying controls still matter for cloud security.
How Cloud Access Security Brokers Work
Cloud access security brokers work through cloud discovery followed by risk-based policy enforcement.
A CASB operates through a cycle of discovery, evaluation, and remediation, an approach NIST identifies as the original CASB use case focused on "preventing or minimizing the chances of shadow IT."
The process begins with discovery: identifying cloud applications that employees access, including unsanctioned services the IT team never approved. Once applications are discovered, the CASB evaluates their risk. The final step is remediation, where the CASB enforces policy by blocking requests or applying session controls.
Forward Proxy Intercepts Traffic From Managed Devices
A forward proxy sits directly in the network path between corporate endpoints and cloud services. It intercepts outbound requests in real time before they reach the cloud application, which means it can block a sensitive file upload or enforce encryption before data ever leaves the organization's control. Deployment typically relies on endpoint agents installed on corporate machines. Those agents route cloud-bound traffic through the CASB inspection layer automatically.
Because the proxy sees traffic inline, it supports policy actions such as blocking a request outright or allowing it with logging. It can also encrypt a file before it reaches the cloud service. Policy decisions happen without requiring the user to take additional steps. Forward proxy works best on managed corporate devices where the agent can be deployed. Personal laptops and phones may bypass it entirely, so organizations with significant bring-your-own-device populations need additional deployment modes.
Reverse Proxy Extends Coverage to Unmanaged Devices
A reverse proxy approaches the problem from the opposite direction, operating on the cloud application side rather than the endpoint. It works at the identity provider layer by inserting itself into the authentication flow: when a user authenticates through the organization's identity provider, the session is redirected through the CASB before reaching the cloud application.
No agent or configuration is needed on the user's device, which makes this architecture well suited for BYOD and contractor access, including partner organizations using their own hardware. This aligns with CISA hybrid identity guidance, which notes that public cloud access should include capabilities common to a CASB such as a reverse proxy.
Once the session routes through the reverse proxy, the CASB can apply granular session controls that go beyond simple allow-or-block decisions. These controls can include restricting downloads of sensitive files to viewing only and preventing uploads from unmanaged devices. Reverse proxy must be configured per application. It does not automatically cover every cloud service an employee might visit, so organizations typically pair it with other deployment modes to address blind spots across their SaaS portfolio.
API-Based Scanning Covers Data Already at Rest
API-based deployment connects directly to cloud providers through published APIs to scan files already stored in cloud repositories, review sharing permissions, analyze user activity logs, and audit historical cloud email content.
Because it works out of band, API scanning has no impact on network performance and functions regardless of which device a user is on. Historical data is within scope, including files and sharing permissions, plus collaboration content containing regulated data. API scanning runs after the data has already been uploaded. Remediation workflows usually quarantine flagged files or revoke sharing links, and may notify the security team for manual review rather than preventing the action in the first place.
Multimode Deployments Combine All Three Approaches
Because each architecture has distinct coverage gaps, many enterprise deployments combine all three simultaneously. Forward proxy handles real-time inspection on managed devices. Reverse proxy covers BYOD and remote access to sanctioned applications. API scanning audits data at rest wherever the proxy models have blind spots.
Organizations typically phase their rollout, starting with the mode that addresses their most pressing coverage gap and adding modes as device management maturity allows. The management complexity this introduces is real: security teams must maintain consistent policies across distinct enforcement mechanisms, ideally through a unified policy console rather than separate configurations for each mode. This expands coverage across combinations of device type and data state across application categories.
The Four Pillars of Cloud Access Security Brokers
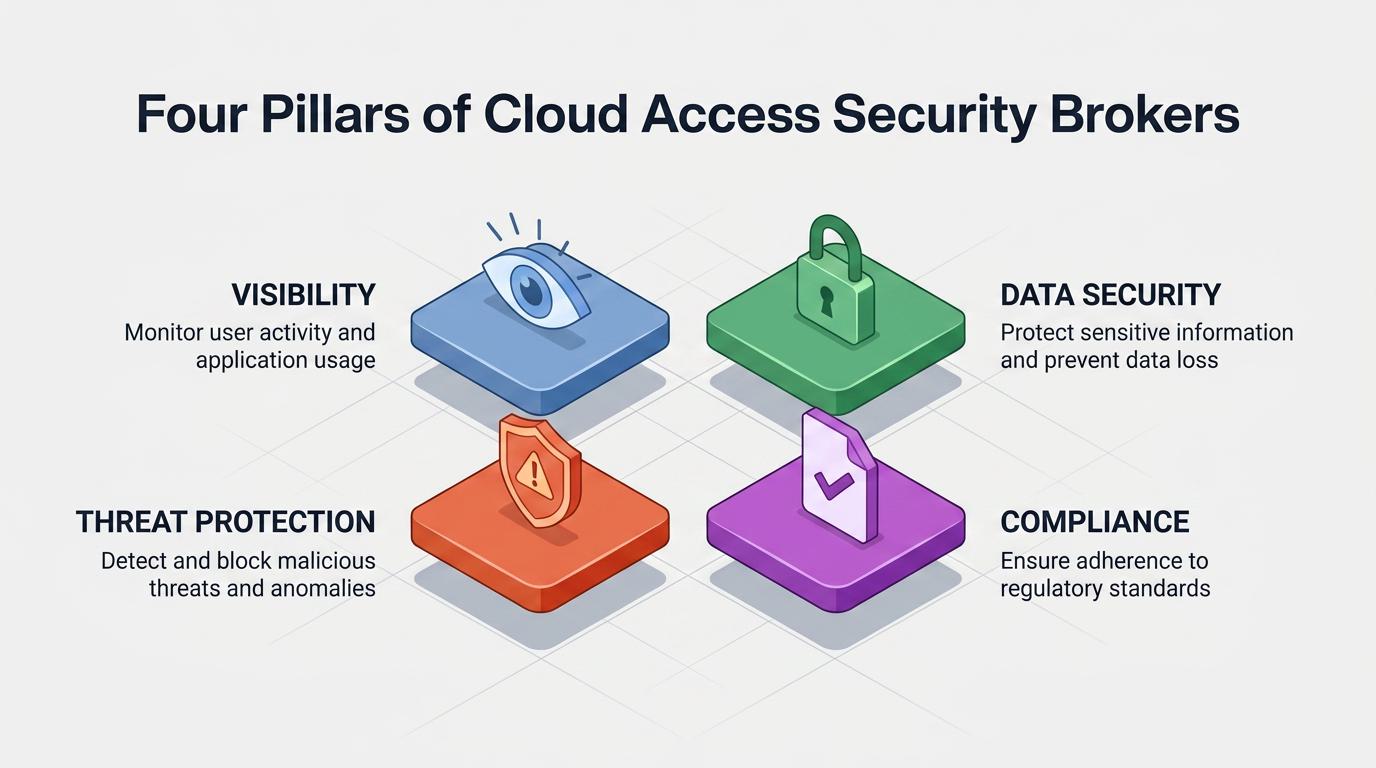
Cloud access security brokers are built around four core functions: visibility, data security, threat protection, and compliance.
Visibility Reveals Shadow IT and Usage Patterns
A CASB discovers cloud applications in use across the organization, including services that employees adopted without IT approval. Discovery works by analyzing traffic data and cloud provider connections. By correlating these inputs, the CASB builds an inventory of cloud services that employees actually use rather than only the subset IT has sanctioned.
Each discovered application receives a risk assessment. Beyond application discovery, visibility includes monitoring how those services are used: which users access them and from which devices, plus activity frequency and data involved. This user and device tracking helps security teams detect unusual activities and feeds directly into the other three pillars, since unknown services leave data protection, threat detection, and compliance enforcement incomplete.
Data Security Prevents Sensitive Information From Leaking
Data security applies data loss prevention policies, encryption, and access controls to protect sensitive information both in transit and at rest. A CASB's DLP engine scans content for patterns like Social Security numbers, credit card data, or proprietary documents, then enforces rules based on what it finds. Many solutions include policy templates mapped to common data types, while organizations can add patterns tailored to their own sensitive data formats.
Context-aware policies add precision beyond simple pattern matching. The CASB factors in the person performing the action and the device they are using, along with the risk score of the destination application, to determine the appropriate response. A finance team member downloading a quarterly report to a managed corporate laptop triggers a different response than an unknown device attempting to share that same report through an unsanctioned storage service. If a user tries to upload a file containing customer data to an unapproved platform, the CASB can block the upload or restrict sharing permissions. It can also encrypt the file.
Threat Protection Identifies Suspicious Behavior and Malware
Threat protection uses behavioral analytics and malware inspection to catch suspicious activity in cloud applications.
Threat protection uses behavioral analytics to detect activity that deviates from established baselines. The system monitors for anomaly indicators such as logins from distant locations within a short period, unusual download volumes, privilege changes, and access from IP ranges flagged by threat intelligence feeds.
When a user account suddenly logs in from an unfamiliar location and begins downloading large volumes of data, the CASB flags the anomaly, can force re-authentication, and alerts the security operations team. On top of behavioral detection, CASBs scan for malware in cloud applications, blocking infected files from being uploaded or shared. A CISA advisory recommends using a CASB to restrict access to public file-sharing services that attackers may use to exfiltrate data from a network.
Compliance Enforces Regulatory Requirements Automatically
Compliance features turn regulatory requirements into enforceable cloud security policies and audit evidence.
Compliance capabilities help organizations meet regulatory obligations like HIPAA, GDPR, PCI DSS, SOC 2, and CCPA by translating those requirements into enforceable policies. In practice, data residency controls work by blocking uploads to cloud regions outside approved geographies, so an organization can prevent sensitive data from being stored outside allowed regions.
CASB audit logs support compliance controls by giving auditors a clear evidence trail during assessments. Compliance teams can pull reports showing which users accessed which data and what policy actions the CASB applied, including the source devices involved. For organizations subject to multiple overlapping frameworks, the CASB can evaluate cloud activity against applicable requirements in a consistent way. This reduces the manual effort of maintaining separate compliance workflows. Continuous monitoring replaces periodic manual reviews: the CASB checks cloud activity against compliance frameworks and flags violations as they occur. Automated remediation can quarantine non-compliant files or revoke access until the violation is resolved.
Cloud Access Security Brokers Use Cases in Practice
Cloud access security brokers are most often deployed to solve recurring visibility and data protection problems, including compliance issues.
The most common CASB deployments address a set of recurring operational challenges.
- Shadow IT Discovery: Identifying unauthorized cloud applications and blocking them or steering users toward sanctioned alternatives.
- DLP Enforcement: Scanning files and messages for sensitive data patterns and blocking, encrypting, or quarantining content that violates policy.
- Account Compromise Detection: Flagging behavioral deviations that may indicate stolen credentials.
- Compliance Monitoring: Checking cloud activity against regulatory frameworks and generating audit-ready reports.
- User Behavior Analytics: Analyzing access and sharing patterns to identify insider threats or compromised accounts before data breaches occur.
- Malware Prevention: Scanning files uploaded to or downloaded from cloud applications for malicious content.
- Data Sharing Control: Auditing and restricting file-sharing permissions to prevent overexposed documents and revoke stale sharing links.
- Cloud Application Risk Assessment: Evaluating cloud services to inform allow-or-block decisions.
Benefits of Cloud Access Security Brokers
Cloud access security brokers help organizations centralize cloud security controls and reduce gaps between applications.
CASB deployments centralize cloud security management and close visibility gaps that arise when teams govern applications independently. Organizations define rules once, and the CASB applies them across SaaS applications. A single pane of visibility across cloud services means security teams can spot risk patterns that would be invisible when monitoring each application in isolation. Organizations subject to multiple regulatory frameworks can enforce consistent data handling rules and generate unified audit trails from one system.
Challenges of Deploying Cloud Access Security Brokers
Cloud access security brokers improve control, but they also introduce deployment and policy complexity that teams need to manage.
CASB deployments introduce operational complexity that organizations should plan for before committing to a rollout.
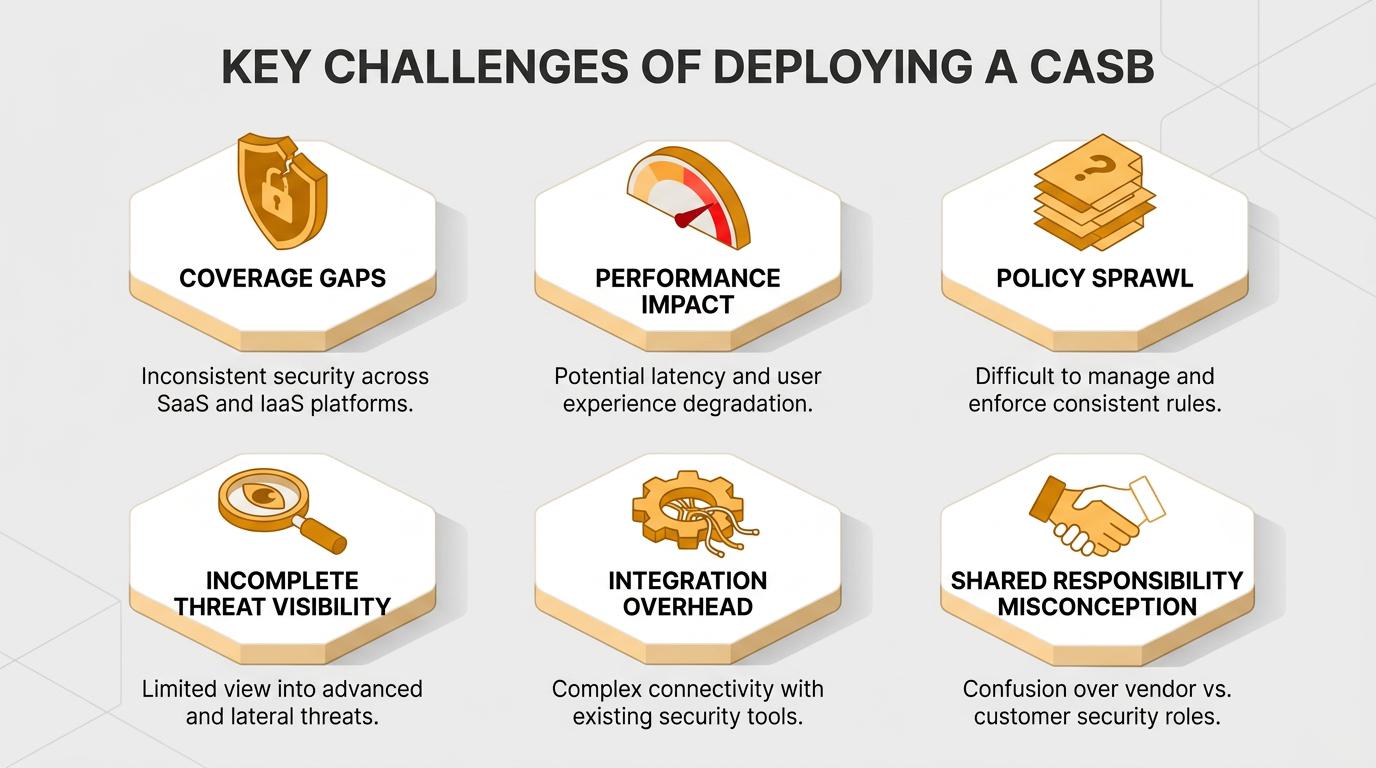
- Coverage Gaps Across Deployment Modes: No single deployment mode covers every scenario, so organizations often need multiple modes and added configuration overhead.
- Performance Impact on Inline Inspection: Forward and reverse proxies add latency to cloud traffic and can degrade the experience for latency-sensitive applications.
- Policy Complexity at Scale: As the number of cloud applications grows, so does the number of policies and exceptions across user groups. Without careful governance, policy sprawl creates conflicting rules.
- Incomplete Visibility Into Newer Threats: Traditional CASB inspection can miss some emerging cloud usage patterns and unsanctioned tools.
- Integration Overhead: Connecting the CASB to identity providers and SIEM platforms takes significant upfront effort, and misconfigurations can create gaps in event logging across existing security tools.
- Shared Responsibility Misconception: Many organizations assume their cloud providers already protect their data. The shared responsibility model means providers secure the infrastructure while the customer remains responsible for data usage policies and access controls, including compliance.
How Cloud Access Security Brokers Fit Into SASE and SSE
Cloud access security brokers now commonly operate as one layer inside broader converged security platforms.
Cloud access security brokers have evolved from a standalone product category into a component of larger converged platforms called Security Service Edge (SSE) and Secure Access Service Edge (SASE).
SASE positions CASB alongside secure web gateway, zero trust network access, firewall-as-a-service, and SD-WAN. SSE emerged as the security-only subset of SASE: the same stack minus the SD-WAN networking layer. NIST guidance defines SASE as a converged capability that includes CASB, SWG, NGFW, and ZTNA, and identifies CASB as a valid policy enforcement point within zero trust deployments.
Securing Data Where It Actually Lives
Cloud access security brokers help close the gap between where enterprise data lives and how organizations control it. Whether delivered as a standalone tool or as part of an SSE or SASE platform, the underlying functions still matter: visibility, policy enforcement, data protection, and compliance. Organizations that treat those functions as foundational are better positioned to keep pace with how employees actually use cloud services.
Frequently Asked Questions
What Are the Four Pillars of CASB?
The four pillars are visibility, data security, threat protection, and compliance.
What Is the Difference Between CASB and SASE?
A CASB provides data security, access control, and threat detection specific to cloud applications. SASE is a broader converged architecture that incorporates CASB alongside SWG, ZTNA, FWaaS, and SD-WAN into a single platform.
What Are the Different CASB Deployment Methods?
CASBs deploy in three modes. Forward proxy intercepts traffic in real time from managed devices. Reverse proxy works from the application side, covering unmanaged devices without endpoint software but requiring per-application configuration. API-based deployment scans data at rest and reviews activity logs but cannot prevent uploads in real time.
Is CASB Still Relevant?
Organizations still need shadow IT discovery, DLP enforcement, threat detection, and compliance monitoring for their cloud applications, even though standalone CASB products have consolidated into SSE and SASE platforms.