Key Insights
Advanced threat detection gives cloud email teams a way to evaluate suspicious messages by behavior, context, and intent instead of signatures alone. Basic filters catch bulk spam, malformed messages, and known malware signatures, but attacker emails often look legitimate and target specific people with business-relevant requests. This gap matters most for organizations that depend on email for high-stakes requests, since a single convincing message can lead to a fraudulent payment or a compromised account.
Key Takeaways
- Business email compromise (BEC), vendor fraud, and zero-day exploits often evade legacy filters by using clean text, trusted domains, and familiar names.
- Combining behavioral analysis, machine learning, and continuous monitoring helps security teams prioritize suspicious activity more effectively than signature-based detection alone.
- Advanced threat detection systems support compliance with the General Data Protection Regulation (GDPR), the Health Insurance Portability and Accountability Act (HIPAA), and the Payment Card Industry Data Security Standard (PCI DSS) through automated audit support and detailed forensic reporting.
- Choosing the right solution depends less on feature count and more on how well it integrates with existing tools, reduces false positives, and gives analysts clear evidence to act on.
What Is Advanced Threat Detection?
Advanced threat detection identifies malicious activity by analyzing behavior, context, and environmental patterns, especially within communication channels like email. It focuses on intent rather than known indicators alone, using machine learning and behavioral baselines to identify threats that evade traditional security tools.
These threats often appear benign on the surface. Business email compromise (BEC), vendor fraud, and zero-day exploits do not always rely on malware or suspicious links that legacy filters can easily identify. Instead, attackers exploit trust by using familiar names, known infrastructure, and legitimate-looking content.
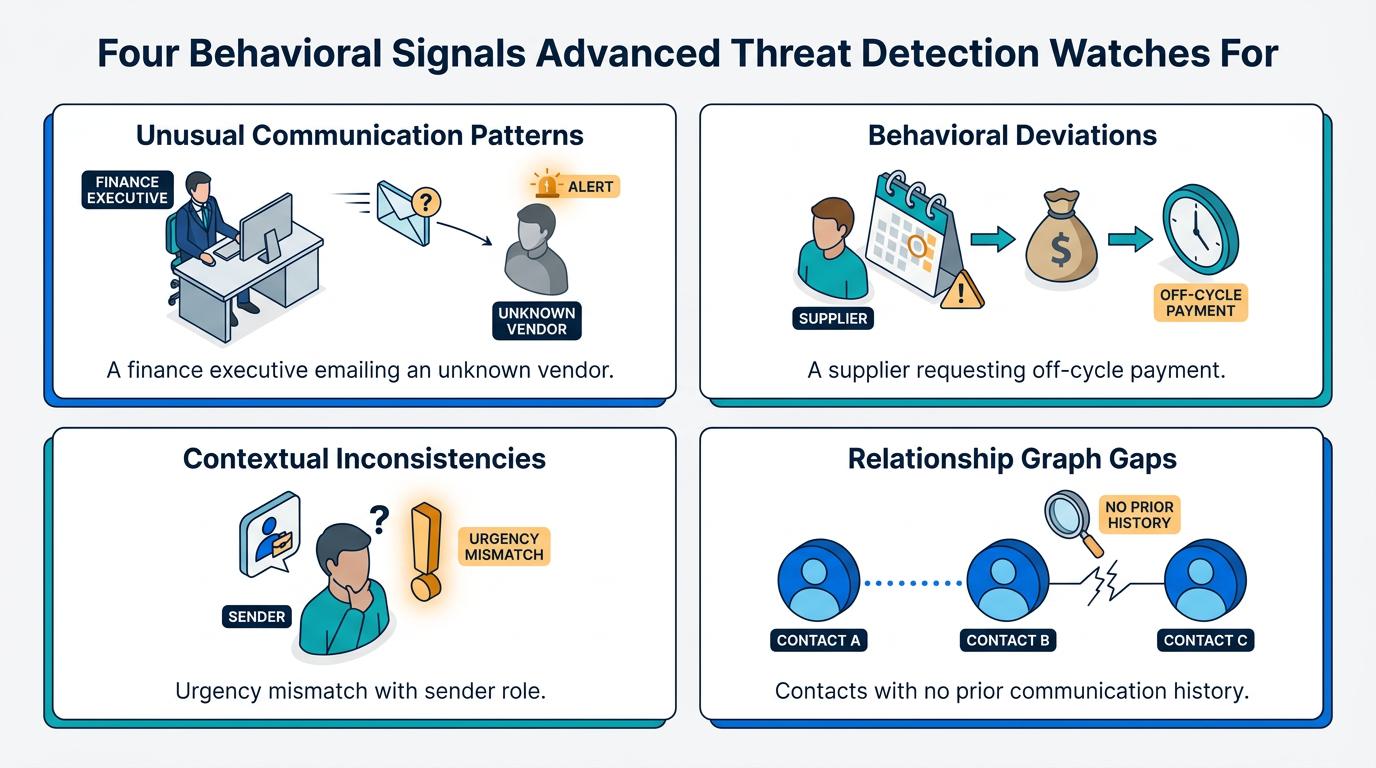
To detect these evasive threats, advanced systems look for subtle anomalies like:
- Unusual Communication Patterns: For example, a finance executive emailing a vendor they've never interacted with before.
- Behavioral Deviations: For example, a supplier requesting a payment outside normal billing cycles or in a different currency.
- Contextual Inconsistencies: For example, an email claiming urgency that's out of character for the sender's role or tone.
- Relationship Graph Gaps: For example, messages from contacts that technically exist but have no previous communication history with the recipient.
These signals are difficult to catch with static rules or traditional threat intel feeds alone.
This behavioral approach helps identify advanced email threats by analyzing signals such as identity, content, tone, and prior interactions to surface suspicious message patterns that traditional tools may miss. The result is a detection layer that adapts as attacker tactics change.
The Evolution of Cyber Threats
Cyber threats have shifted from basic intrusion attempts to organized campaigns that use trusted systems, social engineering, and legitimate tools. Criminal groups and nation-states continue to refine techniques such as fileless malware, supply chain compromise, and account takeover, which can challenge defenses that rely primarily on known signatures.
Attackers also use legitimate system tools to evade detection, which calls for threat detection systems based on behavioral patterns instead of known signatures.
Advanced Threat Detection Capabilities
Advanced threat detection combines artificial intelligence (AI) and machine learning (ML) to analyze large data sets and detect anomalies that human analysts may not see quickly enough. That context helps security teams act earlier instead of reacting after damage begins. These systems typically layer several capabilities together:
- Behavioral Baselining: Establishes normal patterns for user activity, device usage, and network behavior, then flags deviations that may indicate zero-day threats or compromised accounts.
- Layered Detection Methods: Compares evidence across behavioral, content, and infrastructure signals before escalating an incident, rather than relying on a single detection method.
- Continuous Monitoring: Tracks email, identity, and network activity together, giving analysts a clearer view of suspicious sequences as they unfold.
Together, these capabilities give analysts more context per alert, narrowing the gap between a routine anomaly and an active attack.
Sandboxing Analysis
Sandboxing can help analyze suspicious code in isolated environments so security teams can evaluate unknown threats safely. It remains useful for attachments, payloads, and malware samples that need controlled execution before analysts decide how to respond. In email security, sandbox verdicts can give analysts supporting evidence when a message carries a file or link that requires dynamic analysis. Some threats, however, use clean text, social engineering, or legitimate services and may not provide code for a sandbox to execute. That limitation shows why sandboxing works better as one layer in a broader detection program rather than as the primary control for email-borne risk. For more details on why message context matters, see secure email gateways and the gaps attackers exploit.
Behavioral Analysis and Machine Learning
Behavioral analysis establishes baseline activity and detects suspicious deviations, which helps security teams identify insider threats, account takeovers, and novel attacks that signature-based systems often miss. Machine learning improves that process by combining supervised learning on known threats with unsupervised learning that spots unexpected patterns. That combination matters more as attackers adopt generative AI: the FBI has warned that criminals use AI to craft "convincing messages tailored to specific recipients and containing proper grammar and spelling," removing the telltale errors that filters and trained users once relied on. In email environments, several behavioral patterns help analysts evaluate whether a message fits the relationship and business process it claims to represent:
- Workflow cadences
- Vendor interaction patterns
- Recipient behavior
- Timing
- Engagement flows
Real-Time Monitoring and Network Traffic Analysis
Continuous monitoring of network traffic, paired with email security best practices, helps surface advanced threats like lateral movement and command-and-control communications. Automation correlates events across data sources, which helps analysts distinguish isolated anomalies from suspicious sequences. This matters because sophisticated attacks often unfold across identity, endpoint, network, and email signals rather than a single obvious indicator. Security teams can use this broader visibility to prioritize investigations, reduce noisy alerts, and shorten the time between detection and response. For email security programs, network monitoring works best when paired with behavioral analysis of inbox activity and account behavior. That pairing gives analysts both infrastructure context and message-level context when they investigate a suspected compromise.
Benefits of Implementing Advanced Threat Detection
Advanced threat detection improves security posture, reduces financial and reputational risks, and supports regulatory compliance.
Security Posture Improvement
Advanced threat protection can help stop sophisticated threats such as zero-day attacks and fileless malware that evade traditional defenses. With business email compromise attacks continuing to rise, behavioral detection has become a baseline expectation for enterprise email security. According to the FBI's Internet Crime Complaint Center (IC3), BEC losses surpassed $3 billion in 2025. Advanced threat detection adds context that helps analysts rank suspicious messages, accounts, and relationships by business risk. Detecting anomalies also helps security teams identify insider threats and account takeovers earlier, reducing dwell time and associated damages. Earlier detection can also give incident responders more time to preserve evidence, contain compromised accounts, and coordinate with legal or compliance teams.
Financial and Reputational Risk Mitigation
Advanced threat detection reduces financial exposure by helping security teams prioritize suspicious activity before it disrupts operations. It supports several practical business outcomes:
- Analyst Focus: Teams spend less time on false alarms and more time investigating activity with meaningful risk signals.
- Revenue Protection: Analysts can focus on the messages, accounts, and workflows most likely to affect the business.
- Trust Management: Customers, partners, and regulators often judge organizations by how quickly they detect, investigate, and document incidents.
- Executive Reporting: Stronger detection and clearer reporting help leaders explain risk in business terms and maintain trust during investigations.
For Chief Information Security Officers (CISOs), that documentation can also support board discussions about risk reduction, staffing needs, and security investment priorities.
Compliance and Reporting Support
Advanced threat detection systems simplify meeting regulatory requirements like GDPR, HIPAA, and PCI DSS. Automated audit support reduces documentation work, while detailed forensics supports breach response and reporting. GDPR's breach notification window gives organizations 72 hours to report certain personal data breaches, making fast detection a practical dependency. PCI DSS guidance also emphasizes automated technical controls for phishing protection, not training alone. Adaptive compliance features help maintain alignment as regulations evolve, while investigation records give compliance officers clearer evidence for audits, policy reviews, and executive reporting. This matters when teams need to show what happened, when analysts acted, and which controls supported the response.
How to Select the Right Advanced Threat Detection Solution
Choosing an advanced threat detection solution depends on organizational needs, industry, existing infrastructure, and security team capabilities.
Organizational Needs Assessment
Security teams can assess cybersecurity requirements by mapping organization size, industry-specific threats, and the systems that carry sensitive communications. That assessment should identify security gaps, high-risk workflows, and areas where analysts lose time to manual review. A practical assessment typically covers:
- Total Cost of Ownership: Deployment effort, tuning requirements, incident response time, and the likely reduction in breach exposure.
- Email-Specific Risk Factors: Vendor communication patterns, executive impersonation risk, user-reported message volume, and the existing tools analysts use for triage.
This creates a practical baseline for comparing solutions by operational fit rather than feature volume alone, and it helps security leaders explain why a new control belongs in the existing architecture.
Vendor Offering Evaluation
Organizations can prioritize solutions that improve detection quality without adding another operational silo. Useful evaluation criteria include:
- Detection Methods: Solutions should combine multiple detection methods, accurate alerting, and low false positives.
- Integration Fit: Security teams can check for integration with existing platforms so a new control enhances current workflows rather than adding another silo.
- Evidence Quality: Usability and reporting features should support analysts, security leaders, and compliance teams with clear evidence and explainable decisions.
- Support Model: Vendors should provide customer support that helps teams validate detections, tune workflows, and prove value after deployment.
- Evaluation Process: Demos and controlled evaluations can help confirm whether the solution fits the organization's email environment and operational requirements.
During evaluation, teams can ask how the product explains suspicious messages, how it handles user-reported emails, and how investigation records flow into reporting processes.
Tools and Technology Fit
Effective solutions often include capabilities that help analysts review suspicious messages, investigate account behavior, and document decisions without adding unnecessary operational burden. Security teams can evaluate the technology mix across several areas:
- Core Capabilities: Automated response, customizable dashboards, behavioral detection, and integrated threat intelligence can support faster triage.
- Tool Compatibility: Compatibility with existing security tools remains critical because analysts need context without switching between disconnected consoles.
- Detection Coverage: Combining signature-based, behavioral, and machine learning detection maximizes coverage while reducing false alerts.
- Email Security Fit: For email-specific threats, teams can use email security tools and address cloud email threats through solutions that adapt to modern work environments.
- Operational Readiness: Security teams can evaluate whether deployment requires infrastructure changes, whether application programming interfaces (APIs) support cloud email workflows, and whether reporting aligns with incident response and compliance needs.
The right technology mix should help analysts improve investigations while fitting the team's existing security architecture.
Building a Threat Detection Program That Keeps Pace
Advanced threat detection works best as one layer in a broader security program, not a single control that replaces existing defenses. Pairing behavioral analytics with sandboxing, network monitoring, and clear evaluation criteria gives security teams the context to act on suspicious activity before it escalates. As attackers rely more on generative AI to remove the errors that once gave phishing away, the strongest programs will be the ones that keep testing detection methods against real attacker behavior instead of static rules.