Business email compromise (BEC) attacks rank among the most damaging cyberattacks facing organizations. According to the FBI's Internet Crime Complaint Center (IC3) annual report, BEC losses reached $3.05 billion in 2025.
Because BEC messages rarely rely on malware or malicious links, spotting an attack usually comes down to recognizing behavioral and contextual red flags before money or sensitive data moves.
Key Takeaways
Security teams can identify BEC attack red flags by correlating sender identity, request context, account behavior, and workflow deviations.
BEC messages often avoid malware, links, and known threat signatures.
Trusted accounts and familiar threads can make fraudulent requests appear legitimate.
Generative AI email trends make grammar less useful as a warning sign.
Verification controls remain central to BEC attack prevention.
13 BEC Attack Red Flags for Enterprise Teams
The following identifiers can help security teams recognize suspicious requests before money or sensitive data moves. Each red flag below reflects a distinct behavioral or contextual signal that, alone or combined with others, warrants closer review.
1. Sender Impersonation
Sender impersonation is one of the most reliable identifiers of a BEC attack because it exploits how quickly users trust what they recognize. Attackers use look-alike domain tactics, spoofed display names, and mismatched sender addresses to make a fraudulent email appear legitimate at a glance.
Common impersonation patterns include:
Look-Alike Domains: Slightly altered domains, such as adding a hyphen or swapping characters, for example, replacing an "l" with a "1."
Typosquatting: Small misspellings of known domains, such as a double letter.
Homograph Attacks: Attackers replace characters with look-alikes from other alphabets.
Spoofed Display Names: A familiar display name, such as "CEO John Smith," masks an external address.
Personal Email Substitution: An "internal" request comes from Gmail or Yahoo instead of the corporate domain.
These tactics work because many email clients emphasize the display name, and many recipients scan rather than verify. Teams can reduce risk by training users to expand and inspect sender details. They can also monitor Sender Policy Framework (SPF), DomainKeys Identified Mail (DKIM), and Domain-Based Message Authentication, Reporting & Conformance (DMARC) results alongside sender-domain anomalies.
2. Unusual Account and Sending Behavior
Observable changes in account and sending behavior can indicate account takeover activity (ATO), making related BEC attempts harder to detect. Attackers can use a trusted mailbox to orchestrate fraud from within an organization.
Security teams can watch for several concrete behavioral signals:
Unusual Timing: Emails sent outside the user's normal working hours, especially for financial requests.
Atypical Recipients: Messages to departments, vendors, or external recipients the sender rarely contacts.
Outbound Surges: A sudden increase in outbound messages or signs of internal phishing.
New Inbox Rules: Rules that delete, redirect, or auto-forward messages to external addresses.
Session and Device Anomalies: Unexpected sign-in activity, useful as supporting context rather than a standalone verdict.
Because these messages originate from real accounts, legacy email security controls may allow them through. Detection improves when teams establish concrete patterns for workflow cadences, recipient behavior, timing, vendor interactions, and engagement flows, then review deviations connected to sensitive business requests.
3. Urgent Requests for Confidential Information
Urgency paired with sensitive data protection concerns is a classic BEC pattern because it pressures recipients to act before verifying. Attackers use time constraints to reduce scrutiny and increase compliance.
Signals can include:
Urgent Language: The message uses terms such as "urgent," "immediate," "ASAP," or "important."
Deadline Pressure: The sender demands completion "by end of day" or says action is "required immediately."
Discouraged Verification: The sender says, "Do not contact me. I'm unavailable."
Implied Consequences: The message claims, "We'll miss compliance deadlines if this isn't handled now."
Requests for Secrecy: The sender says, "Please don't share this. It's confidential."
Channel Switching: The sender quickly asks to continue the conversation on a secondary encrypted mobile messaging app.
These messages often appear most believable when timed to real business events, including end-of-quarter closes, audits, active vendor onboarding, or construction and procurement cycles.
4. Inconsistent Communication Style
A shift in a sender's normal tone or structure can indicate impersonation or compromise, especially when paired with a sensitive request. The detailed writing cues associated with AI email trends appear in section 11, but stylistic mismatches remain useful supporting evidence.
Security teams can watch for tone mismatches such as:
A normally detailed executive email that turns vague and instruction-only
Uncommon sign-offs from a sender who never uses casual phrasing
A methodical finance leader requesting payment with minimal context
Missing shorthand, an unfamiliar greeting, or a sudden shift in reply cadence
Tone mismatches work best as supporting signals rather than standalone verdicts. Teams can combine them with anomalies in timing, recipients, request type, and workflow, such as an off-process wire transfer request. This contextual approach supports behavioral threat detection without treating writing style alone as proof of malicious intent.
5. Fraudulent Payment Requests
Payment manipulation is a primary objective of BEC, and small changes to payment instructions often have the greatest impact. Attackers frequently impersonate vendors, partners, or executives to bypass normal controls.
Common red flags include:
New Banking Details: The message announces "we've changed banks" or "use this new account" without formal notice.
Unusual Payment Methods: The request moves an established business relationship to gift cards, payment apps, or cryptocurrency.
Out-of-Character Authority: A leader asks someone outside finance to initiate a transfer without the normal approval path.
Payroll Diversion: A spoofed employee request asks HR or payroll to update direct deposit details, sometimes to a prepaid card account.
Account-Based Changes: An attacker accesses an employee account and alters payroll routing details directly.
These patterns align with common BEC tactics. Vendor-focused scams often appear as vendor fraud patterns, including fraudulent changes to payment instructions.
6. Spoofed Email Threads
Thread hijacking increases BEC success rates by leveraging existing trust and context. After compromising an account, attackers observe active conversations and inject a message at a moment that aligns with legitimate business activity.
Attackers commonly:
Map Relationships: They identify who approves payments and who executes them.
Mirror Style: They copy formatting, signature blocks, and reply cadence.
Reference Real Projects: They use accurate project names, invoices, or timelines.
Time the Ask: They intervene when a legitimate conversation reaches an approval point.
A message inside a familiar thread often receives less scrutiny. Security teams can correlate thread context with authentication results, reply timing, sender behavior, and changes in the type of request. Established vendor risk patterns can provide additional context, while account takeover detection can help surface activity from trusted mailboxes that no longer behave as expected.
7. Missing External Email Warnings
Unexpectedly missing "external sender" banners can be a BEC clue, especially when a message asks for money, credentials, or sensitive data. When a message appears external but lacks the usual warning, it warrants closer review.
Common ways attackers attempt to avoid banner cues include:
Look-Alike Domains: Small domain variations resemble the organization's domain.
Header Manipulation: Altered metadata influences how the message renders.
Compromised Accounts: A real internal mailbox sends the message after takeover.
Configuration Gaps: Tenant settings strip or inconsistently apply warnings.
Security teams can use this signal to initiate email header analysis and review authentication results rather than assuming the missing banner is only a mail client glitch. Because banners are a supporting control, organizations can pair them with enforced email authentication controls, behavioral analysis, and clear verification processes for sensitive requests.
8. Suspicious Attachment Types
Attachments are not required for BEC, but unusual file types can indicate a blended campaign that includes malware, credential theft, or initial access tooling. This pattern aligns with the MITRE ATT&CK Spearphishing Attachment technique.
Security teams can review:
Compressed Archives: Files such as .zip or .rar can conceal payloads.
Password-Protected Files: Encrypted attachments can evade automated inspection.
Uncommon Formats: File types such as .iqy or .iso can indicate an unusual delivery method.
Macro-Enabled Documents: The attachment prompts the user to "Enable Content."
A deviation from normal behavior can be as important as the attachment itself. For example, a vendor that regularly sends PDFs but suddenly sends encrypted archives creates a concrete behavioral mismatch. Teams can combine email forensics methods with signature-based threat detection and behavioral context to assess the sender, request, and attachment together.
9. Malicious Redirected Links
Redirect chains are a common BEC and phishing technique because the first visible domain can look legitimate while the final destination is malicious. MITRE ATT&CK catalogs the underlying technique as Spearphishing Link, and these attacks frequently use open redirects or trusted platforms to obscure the true endpoint.
Common tactics include:
Trusted Redirect Abuse: The attacker uses a reputable service as the first hop.
Multi-Hop Chains: Several redirects hide the final destination.
Parameter-Based Redirects: URL parameters disguise the intended target.
Even when a link looks familiar, security teams can inspect the full redirect path and correlate it with sender behavior, recipient targeting, and conversation context. Understanding open redirect techniques can help analysts distinguish legitimate forwarding behavior from suspicious chains. Teams can also examine how the link supports broader social engineering tactics, including credential theft or requests to re-authenticate.
10. QR Code Phishing in BEC Campaigns
QR-code phishing, or quishing, is a BEC-adjacent tactic that sidesteps many email link inspection controls. Attackers embed a QR code in an email or attachment and rely on the recipient scanning it with a mobile device.
An QR phishing advisory describes campaigns that deliver QR images as attachments or embedded graphics to evade URL inspection, rewriting, and sandboxing.
The encoded destination may not be visible to standard URL scanners, and a scan can route the victim onto a personal device outside corporate web controls. Security teams can apply the same scrutiny used for unsolicited login links, particularly when a QR code appears alongside urgency or a request to "re-authenticate."
Understanding QR code phishing and related multi-factor authentication (MFA) bypass methods can help teams build verification steps that do not depend on the channel or destination supplied in the message.
11. AI-Generated Impersonation Content
Generative AI enables more polished, personalized BEC lures, reducing the usefulness of grammatical or spelling errors as detection cues. In a AI fraud warning, the FBI IC3 states that these tools "can correct for human errors that might otherwise serve as warning signs of fraud."
Indicators of AI-assisted BEC include:
Polished but Generic Writing: Grammatically clean text lacks the sender's typical quirks.
Incomplete Familiarity: Accurate project references omit the shorthand, process detail, or interpersonal cues the sender normally uses.
Repeated Request Structure: Multiple employees receive similarly structured requests within a short timeframe.
Behavioral Misalignment: The request conflicts with the sender's normal timing, recipients, or workflow cadence.
Teams often get better results by focusing on behavioral alignment and request legitimacy. Generative AI email trends and established social engineering attack patterns provide useful context, but organizations can still verify the sender through a known channel that the message did not supply.
12. Multi-Channel Social Engineering in BEC Attacks
BEC increasingly spans cloud email and collaboration platforms, which can make an attack feel more credible and compress the response window. Verizon's 2026 Data Breach Investigations Report found that 41% of social engineering breaches involved social vectors other than email alone.
Attackers who compromise one identity often try to reinforce the story in Teams, Slack, or SMS. Common patterns include:
An attacker follows an email with a chat message that says, "Did you see my note? Need this processed now."
The conversation switches channels to avoid email scrutiny or banner cues.
The attacker targets executive assistants or finance approvers across multiple tools.
A compromised executive account plays still images or deepfake audio during a video meeting, then issues transfer instructions in chat or a follow-up email.
The primary security control point often remains the inbox. Abnormal's behavioral AI is designed to help identify the email and account-based components of these campaigns across cloud email and integrated platforms such as Slack threat detection. Organizations should pair this coverage with complementary controls for voice, SMS, and videoconferencing channels as part of broader social engineering defenses.
13. Adversary-in-the-Middle Attacks That Bypass MFA
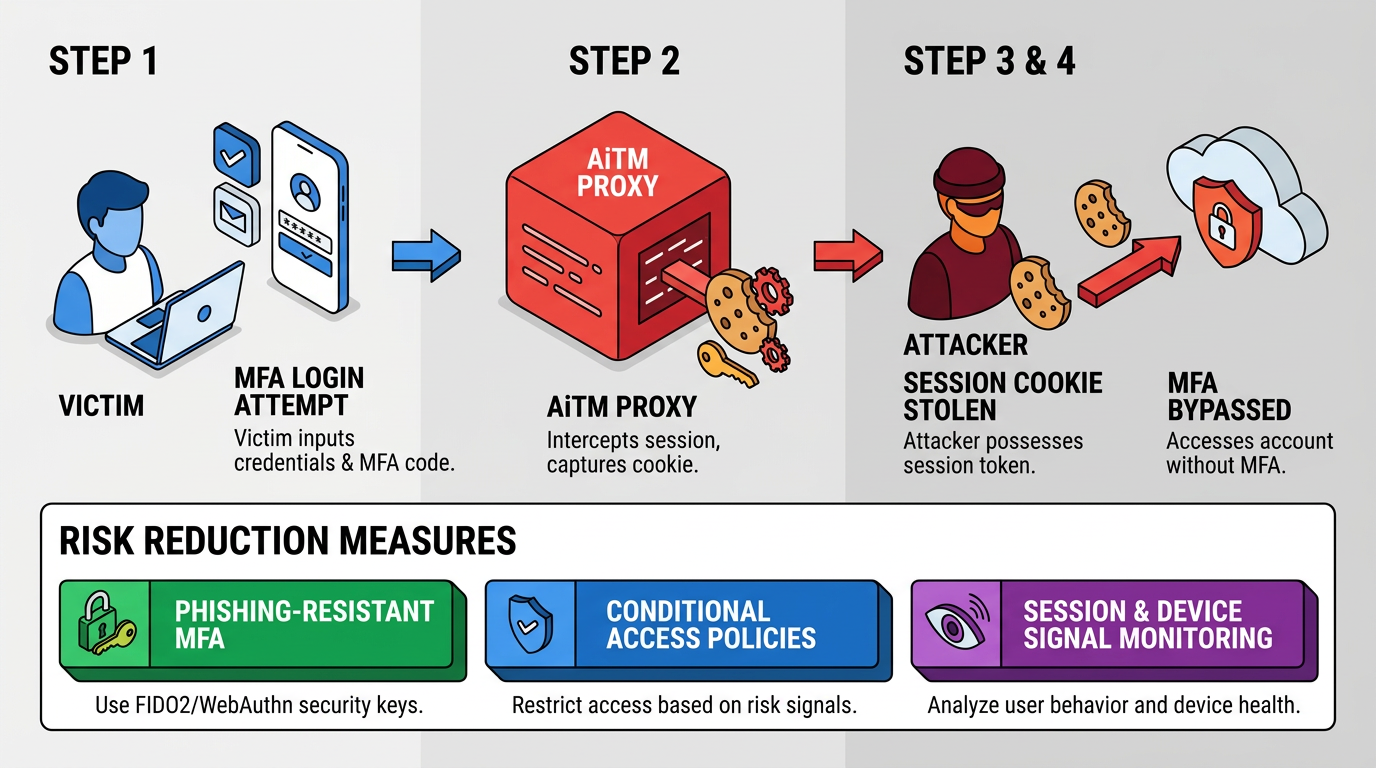
Adversary-in-the-middle (AiTM) phishing can enable BEC-driven account takeover by capturing session cookies alongside credentials, allowing attackers to bypass multi-factor authentication (MFA). In these campaigns, a proxy sits between the victim and the real login service, relaying authentication while harvesting the resulting session artifacts.
Once attackers capture a valid session cookie, they can replay it to authenticate as the compromised user without triggering another MFA prompt.
Once an attacker has a valid session, common post-compromise actions include:
Replaying Sessions: The attacker uses stolen session cookies to access cloud services.
Using Trusted Access: The attacker operates through the compromised identity and its authorized services.
Expanding Access: Captured credentials support additional sign-in attempts.
Risk reduction can include phishing-resistant MFA for high-risk roles, strong conditional access policies, and detection focused on session and device signals. Teams can review MFA bypass methods alongside account takeover detection to identify the email and identity activity surrounding a compromised session.
How to Defend Against BEC with Email Authentication
Enforcing email authentication controls reduces exposure to domain spoofing methods and strengthens BEC defenses. SPF, DKIM, and DMARC do not stop every BEC variant, including compromised internal accounts, but they can meaningfully reduce direct impersonation using an organization's domains. You can implement them in stages while confirming that legitimate email flows continue to operate correctly:
Sender Policy Framework (SPF): Publish DNS TXT records listing authorized sending IP addresses so receiving servers can verify sender legitimacy.
DomainKeys Identified Mail (DKIM): Sign outbound messages with strong keys and rotate them regularly so receivers can verify that messages were not altered in transit.
Domain-Based Message Authentication, Reporting & Conformance (DMARC): Begin with monitoring, move to quarantine, and then enforce reject after validating legitimate email flows.
Monitoring-only policies provide visibility without enforcement. Attackers can still spoof domains when receiving systems do not reject or quarantine messages that fail authentication.
How to Build a Framework for BEC Attack Red Flags
A workable BEC detection framework assigns clear detection and verification responsibilities across roles, which can speed triage and support audit readiness. Teams can combine AI-powered email security with documented approval controls and account takeover protection.
Each role owns a different slice of BEC defense, from strategy down to detection tuning. The table below maps where each function focuses and the key actions that fall to them:
Role | Focus | Key Actions
|
|---|---|---|
Chief Information Security Officer (CISO) | Integrating BEC detection into a broader security strategy | Combine SPF, DKIM, and DMARC with behavioral analysis; establish escalation paths and out-of-band verification; prioritize finance, executives, and vendor relationships; build playbooks with IC3 reporting and FBI Recovery Asset Team coordination. |
IT Security Manager | Putting detection systems into daily operation | Use AI-powered email security to surface behavioral deviations; monitor identity, session, and device signals; route high-risk workflow deviations for analyst review. |
Compliance Officer | Aligning detection with regulatory obligations and reporting | Map controls to SOX, HIPAA, GDPR, and PCI DSS; log detection events and verification steps for audits; fold BEC indicators into risk reporting; retain evidence of who verified each payment change, how, and when. |
Security Engineer | Configuring and tuning detection at the technical layer | Align monitoring to MITRE ATT&CK techniques (T1078, T1114.003, T1564.008); baseline normal timing, recipients, and vendor interactions; correlate authentication failures with behavioral signals; audit for hidden inbox and forwarding rules. |
Together, these engineering practices turn isolated BEC indicators into a repeatable triage process.
Reduce BEC Attack Risk with a Layered Approach
Individual BEC signals become more useful when teams evaluate them together rather than in isolation. Organizations can combine enforced email authentication, MFA bypass risk controls, behavioral detection, and verification training built around real approval workflows.
Abnormal's AI-native platform is designed to analyze cloud email behavior, identity signals, and supported collaboration activity to help surface signs of social engineering. It integrates alongside existing security infrastructure and can enhance the current security stack without requiring a rip-and-replace approach. For campaigns that include voice, SMS, or videoconferencing, organizations should use complementary controls beyond email security.
The 2026 Gartner® Peer Insights™ Voice of the Customer for Email Security named Abnormal a Customers' Choice. Want to see how it works? Book a demo and explore how Abnormal can help protect your inbox from BEC attacks.
Frequently Asked Questions
What Makes Business Email Compromise Different From Standard Phishing?
Standard phishing often relies on malicious links or attachments sent broadly, while BEC typically avoids malware altogether and instead uses impersonation and social engineering to manipulate one specific employee into acting on a fraudulent request, most often a wire transfer or a change to payment details.
Can Multi-Factor Authentication Fully Stop BEC Attacks?
Multi-factor authentication reduces the risk of account takeover, but adversary-in-the-middle phishing kits can intercept session cookies and bypass MFA entirely. MFA works best alongside behavioral monitoring and verification steps that don't depend on the channel supplied in a suspicious message.
What Should An Employee Do After Spotting A Possible BEC Red Flag?
Employees can pause before acting on the request and verify it through a known contact channel, such as a phone number already on file, rather than replying to the email or using contact details the message itself provides.
How Quickly Should A Suspected BEC Incident Be Reported?
Suspected BEC attempts should be reported to the security team right away, since fraudulent wire transfers can be difficult to recover once funds clear. Organizations can also file a report with the FBI's Internet Crime Complaint Center (IC3) as part of incident response.