Key Insights
Threat mitigation strategies using behavioral AI shift detection from static pattern matching to analysis of normal user, vendor, and application behavior. Email remains a primary entry point for cyberattacks, and payload-less messages can appear legitimate because they contain no known malicious signature. Behavioral context helps security teams evaluate deviations in communication patterns, identity activity, and workflow cadence. This approach complements preventive controls by helping surface suspicious activity that signature-based detection tools may not recognize.
This article explores how behavioral baselines, framework alignment, automated response, and continuous learning fit together into a working email defense. We also provide practical guidance on where behavioral analysis closes gaps that preventive controls leave open and how to measure the result against a recognized standard.
Key Takeaways
Behavioral baselines give email threat mitigation the context needed to surface payload-less business email compromise (BEC) and vendor fraud that signature-based tools may miss.
Mapping detection, response, and recovery to the NIST Cybersecurity Framework functions helps security leaders show where behavioral analysis fits alongside existing controls.
Deviations in identity activity, authentication methods, and communication patterns can support proportionate account remediation.
API-native remediation can quarantine malicious messages and create audit logs that support compliance reporting.
Analyst verdict tagging, threat intelligence, and model refinement help maintain detection accuracy as attacks and business behavior change.
Align Threat Mitigation Strategies with the NIST Cybersecurity Framework 2.0
Email threat mitigation controls span prevention, detection, response, and recovery, and the National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF) gives security leaders a shared vocabulary for placing behavioral analysis within a wider control program.
Map Detection to the Framework
NIST describes its CSF DETECT function in one sentence: "Possible cybersecurity attacks and compromises are found and analyzed." Its continuous monitoring category adds that organizations monitor personnel activity and technology usage to find potentially adverse events.
Preventive controls such as secure email gateways (SEGs) and multi-factor authentication methods (MFA) reduce the volume of attacks that reach a mailbox. Legacy controls often struggle with payload-less social engineering and authenticated account abuse, so Abnormal's behavioral AI adds a detective layer that evaluates suspicious deviations in cloud email and identity activity. This mapping positions behavioral analysis as a complement to existing preventive controls rather than a replacement for them.
Connect Response and Recovery
The functions that follow prevention correspond to distinct operational capabilities:
Detect: Baselines for users, vendors, and applications, combined with risk scoring for deviations, help security teams find and analyze anomalies across email and collaboration services.
Respond: NIST describes this function as "Actions regarding a detected cybersecurity incident are taken." Proportionate response can include message quarantine and account actions based on the severity and context of the event.
Recover: Teams closing an incident can restore normal account operation, verify that access settings remain secure, and retain evidence of the actions taken.
Mapping capabilities this way lets a chief information security officer (CISO) show a board or auditor how each control supports a named framework function without repeating the operational details covered in later sections.
Build Behavioral Baselines for Threat Mitigation Strategies
Behavioral baselines support threat mitigation by mapping normal workflow cadences, vendor interaction patterns, recipient behavior, timing, and engagement flows across the email environment.
Model Identity and Message Patterns
Modeling identity and message patterns means building a profile of what normal looks like for every user, vendor, and application an organization emails with. The AI engine builds these profiles by connecting to a cloud email environment through application programming interface (API) integration, without requiring MX record changes or endpoint agents.
The model evaluates several categories of context:
Identity Signals: Session, device, authentication, and other behavioral signals help establish how an account typically operates.
Message Signals: Email authentication results, reply-to domains, routing paths, cadence, tone, and recipient patterns provide context for each message.
Vendor Patterns: The timing and tone of invoice-related emails help the model identify sudden requests to change banking details or communication workflows.
Together, these signals create context for identifying suspicious activity without relying only on rules or known signatures.
Score Deviations in Context
Context helps the model surface risks that email gateways may not recognize. The engine compares current supplier activity with established profiles, helping surface vendor email compromise even when a message arrives through an authenticated channel and contains no malicious attachment. The engine observes normal traffic to establish baselines without requiring teams to create signatures. After those baselines stabilize, the engine scores email, login, and application activity against learned patterns. A significant deviation can raise the risk score and initiate a configured response.
This design gives security teams a behavioral view of BEC email attacks and supplier risk. Preventive controls continue handling known threats alongside it.
Detect Threats Through Anomaly Analysis
Anomaly analysis helps security teams identify subtle deviations early enough to investigate and contain suspicious email or account activity.
Identify Account Compromise
A compromised user rarely signals distress directly. Instead, session, device, authentication, and other behavioral signals may diverge from the account's established patterns. The platform compares current activity with the user's historical patterns and assigns risk when the behavior diverges.
For example, when an executive account shows session behavior that differs sharply from its established profile, the engine can flag the event for review. Depending on configured policy and risk tolerance, the response may initiate approved account-containment actions or quarantine suspicious outbound messages. These signals can help identify account takeover fraud and executive impersonation attacks. Remediation stays proportionate to the available evidence.
Analyze Vendor and Language Signals
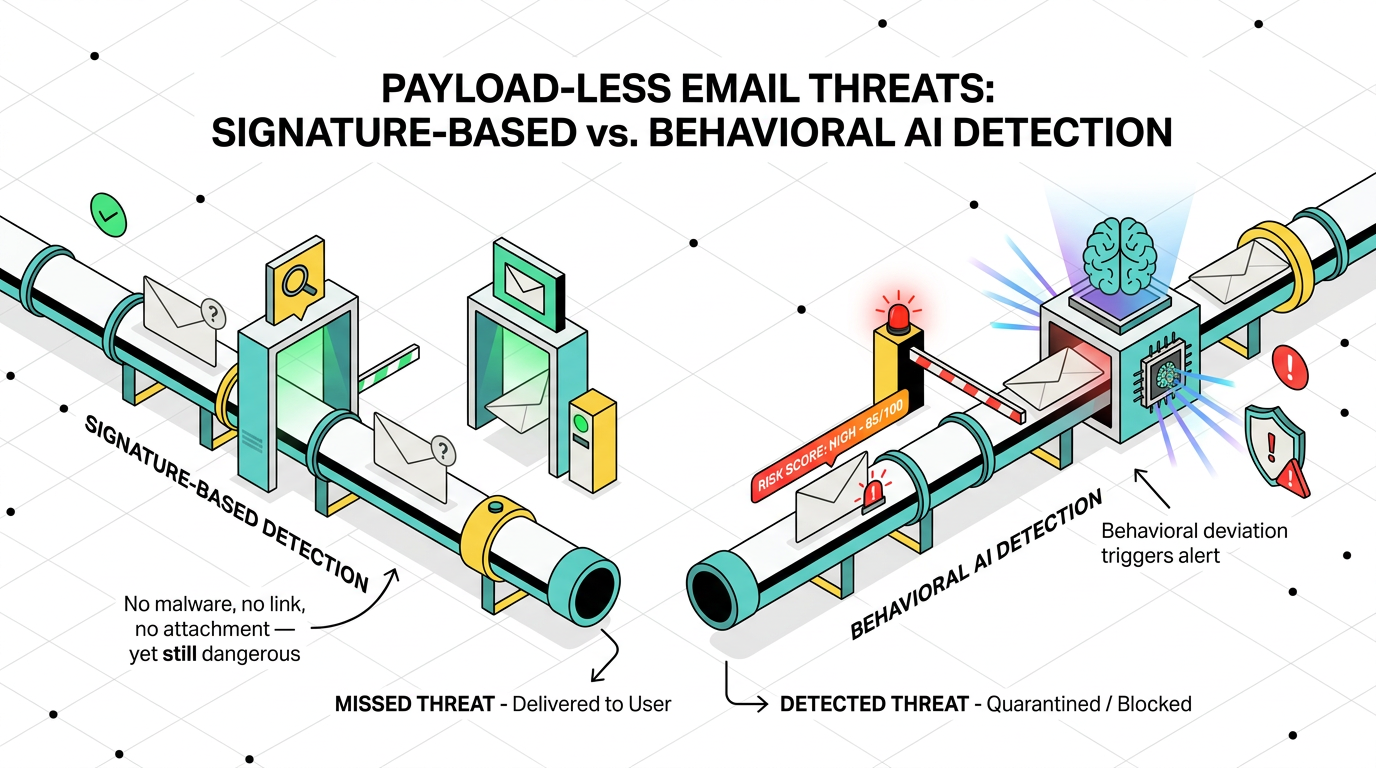
Analyzing vendor and language signals means comparing the tone, timing, and phrasing of invoice-related email against what's normal for that supplier. Finance teams exchange a high volume of invoice emails with trusted partners, so fraudulent wire requests can appear routine to rule-based filters. The AI models the normal tempo, recipients, and language style of each supplier's email, then scores deviations in context. A request to route funds to a new bank, paired with an altered sender domain, can trigger an alert even when the message contains no malware or suspicious links. An incident card with prior communication context gives finance a basis for holding the payment while the team investigates.
AI-generated phishing messages can mirror internal tone, abbreviations, and urgency cues. Language analysis evaluates sentiment and intent, weighs atypical phrases against the sender's usual diction, and helps identify incongruities. Scoring semantic intent can surface new social engineering attacks that keyword filters have not encountered.
Automate Investigation and Accelerate Response
Automated scoring can reduce repetitive review by directing analysts toward messages with the clearest indicators of risk.
Prioritize High-Risk Messages
The engine grades inbound and internal email as it arrives by evaluating sender history, identity context, linguistic tone, and payment-request behavior associated with BEC. It promotes messages that deviate sharply from an established baseline.
This email threat triage reduces queue noise and gives analysts more time to investigate suspicious activity. Continuous model refinement and analyst feedback also help limit repetitive alerts that have already received a benign verdict. Clear prioritization supports a more focused workflow without implying that automation replaces analyst judgment. Teams can still review the evidence, adjust policy thresholds, and escalate incidents that require broader investigation.
Connect Investigation Workflows
After the engine identifies a high-risk email, APIs can send the enriched event to the security information and event management (SIEM) and security orchestration, automation, and response (SOAR) platforms the team already uses. SIEM correlation searches place email alerts beside endpoint and identity telemetry. SOAR playbooks can initiate approved response actions and update incident status.
Investigation outcomes flow back into the platform and inform later triage decisions. This integration complements the existing security operations center workflow and reduces the manual effort required to connect email, identity, and endpoint evidence.
Execute API-Driven Remediation Without Disruption
API-driven remediation can contain malicious email and compromised accounts. It does this with minimal changes to mail routing and user workflows.
Contain Email and Account Risk
API-native email remediation uses native cloud connections to support automated quarantine for messages that show high-risk deviations. Based on configured policy, quarantine can remove a malicious message from affected inboxes. Legitimate traffic stays in place.
For a compromised account, remediation can initiate configured account-containment actions. Administrators can choose whether these actions run automatically or wait for manual review, which keeps the response aligned with the team's risk tolerance and change-control requirements. This approach can reduce exposure to phishing email attacks without requiring the organization to replace its existing email gateway or redesign mail flow.
Preserve Audit Evidence
The platform logs remediation steps with metadata such as who initiated the action, the timestamp, and the indicators that triggered it. This evidence helps teams satisfy audit requirements and document how they applied data protection controls during an incident.
The platform can send these logs to a SIEM, where analysts correlate email events with endpoint and identity systems. Keeping response evidence in established reporting workflows supports faster investigations and gives compliance teams a clearer record of control operation. Defined logging and retention practices turn remediation activity into reusable incident and audit evidence rather than a separate reporting task.
Strengthen Defenses Through Continuous Learning
Continuous learning helps detection models adapt as attack methods, organizational structures, and supplier relationships change.
Capture Analyst and Threat Feedback
Feedback enters the detection process through several channels:
Analyst Verdicts: Analysts tag repetitive false positives or overlooked threats, and those verdicts inform later scoring decisions.
Threat Intelligence: Intelligence on phishing kits, vendor fraud tactics, credential-stuffing campaigns, and compromised vendor accounts adds context for emerging attack patterns.
Model Refinement: Updated behavioral patterns help the engine account for legitimate changes in user, vendor, and application activity.
Analyst verdicts preserve local operational context. Threat intelligence and model updates account for shifts in attack methods and legitimate business activity. This feedback supports later triage without replacing analyst review. These channels combine local operational knowledge with broader threat context, which helps the model distinguish business change from suspicious behavior.
Recalibrate Models and Controls
The model refines its understanding of users and vendors as teams reorganize, communication patterns shift, and suppliers change. Those updates support email anomaly detection and help reduce repeated false positives. The same refinement also helps surface new lures, including AI-written messages.
Security teams can also audit suppression rules and automated actions on a regular schedule to confirm that they still match regulatory mandates and risk tolerance. This review gives analysts a way to validate automation, adjust exceptions, and document policy decisions. Combining model refinement with human oversight keeps continuous learning tied to operational evidence rather than treating adaptation as an unmonitored process.
Transform Email Security into Adaptive Defense
Behavioral AI turns email security from a static filter into an adaptive layer that evaluates normal patterns across users, vendors, and applications. By flagging meaningful deviations, it can help teams identify threats that rules and signatures may not recognize. Automated investigation and remediation reduce response steps. Continuous learning helps maintain detection quality as attack methods and business behavior change.
Abnormal works alongside existing SEGs and integrates with SIEM and identity tools, adding behavioral context to the current security stack. Customers named Abnormal a Customers' Choice in the 2026 Gartner® Peer Insights™ Voice of the Customer for Email Security.
Ready to strengthen defenses against BEC, vendor fraud, and account takeover attacks? Book a demo to see how behavioral detection can support your email security program.
Frequently Asked Questions
How Does Behavioral AI Detect Business Email Compromise (BEC) Attacks That Contain No Malicious Payload or Links?
Behavioral AI flags payload-less BEC by comparing each message against a learned profile of how a given sender normally communicates, including timing, recipients, tone, and typical requests. When a message mimics a trusted sender but diverges sharply from that baseline, the engine assigns a risk score even though no attachment, malware, or malicious link is present. This context-driven approach surfaces social engineering that traditional filters, built to match known threat signatures, are not designed to catch.
What Is the Difference Between Signature-Based Email Detection and Behavioral AI-Based Detection, and When Should Each Be Used?
Signature-based detection matches messages against a database of known malicious patterns and hashes, making it efficient at blocking commodity threats but limited against novel attacks that lack an existing signature. Behavioral AI instead learns what normal communication looks like for each user, vendor, and application, then flags deviations regardless of whether a signature exists. The two work best together: signatures handle high-volume known threats at scale, and behavioral analysis catches payload-less fraud, account compromise, and newly crafted social engineering.
How Do Behavioral AI Email Security Platforms Integrate With Existing Secure Email Gateways (SEGs) and SIEM/SOAR Tools Without Disrupting Mail Flow?
Behavioral AI platforms connect to cloud email through APIs rather than MX record changes, so the existing SEG continues to filter inbound mail while behavioral analysis reads messages, user activity, and identity signals as a detective layer on top. Enriched events flow to SIEM and SOAR through the same APIs, letting correlation searches combine email alerts with endpoint and identity telemetry and letting playbooks trigger approved response actions. Remediation such as message quarantine or account containment runs through those API connections, preserving current mail routing and security tool investments.
How Does the NIST Cybersecurity Framework 2.0 Map to Behavioral AI Email Defense Capabilities Across Detect, Respond, and Recover Functions?
Behavioral AI maps to Detect by treating identity and workflow monitoring as continuous rather than event-triggered, closing the gap left when SEGs and MFA complete their one-time checks. It supports Respond by using risk scoring to drive proportionate action, from message quarantine to account restriction or analyst escalation, and supports Recover by preserving evidence trails that confirm containment and inform compliance review. This mapping gives security leaders a framework-aligned vocabulary for discussing detection coverage, response proportionality, and incident recovery with audit committees and regulators.
What Feedback Mechanisms Help Reduce False Positives in Behavioral AI Email Security Systems Over Time?
False positive reduction depends on several loops working together: analyst verdict tagging that encodes local operational context, threat intelligence that validates indicators against broader attack activity, and user-reported feedback that captures messages automated systems misjudged. Model refinement digests those signals to update behavioral baselines for legitimate shifts such as new vendor relationships, reorganizations, or seasonal communication patterns. Regular policy audits round out the loop by letting teams review suppression rules and thresholds against operational outcomes rather than theoretical risk.