Key Insights
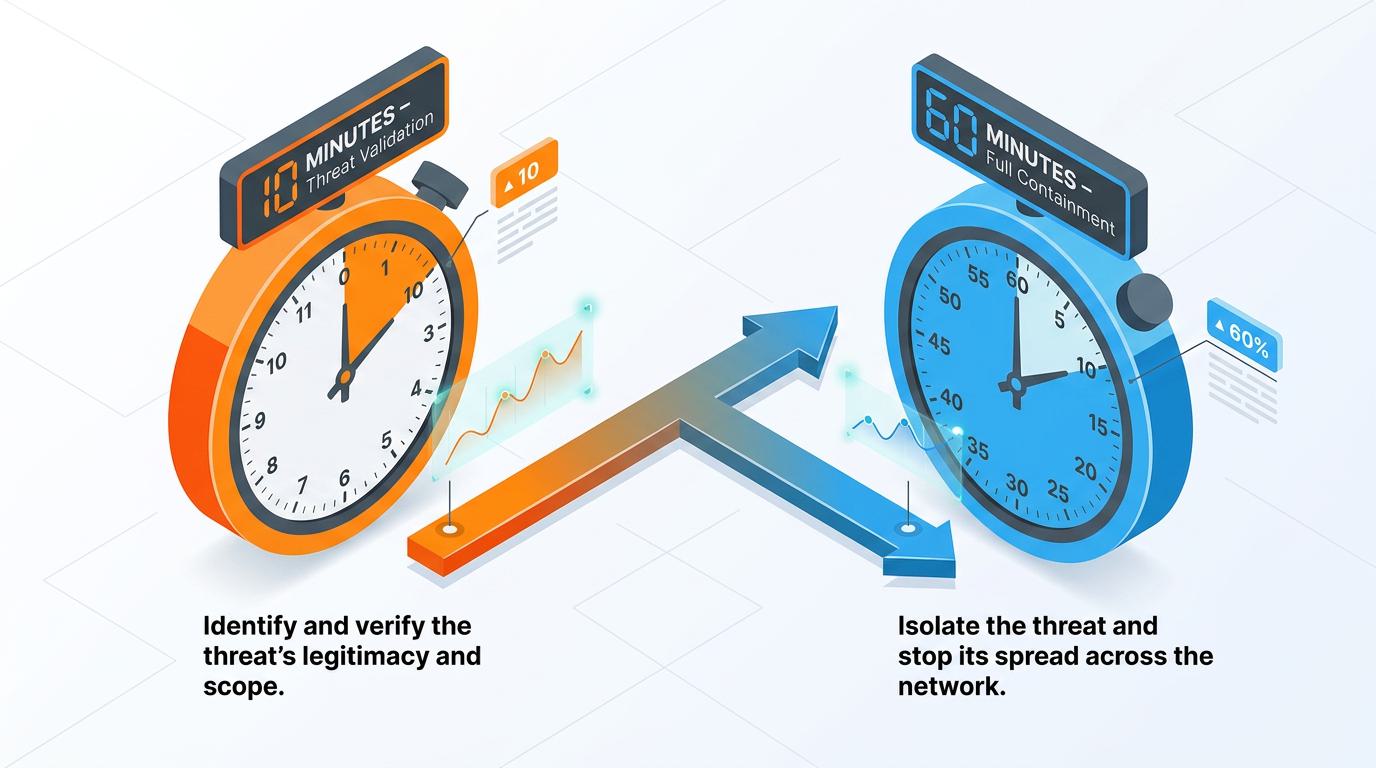
Ransomware groups can encrypt entire networks in under an hour, and business email compromise (BEC) attacks unfold in real time, yet most organizations still take days or weeks to detect intrusions. The 10/60 framework brings detection speed in line with attack speed, setting two actionable targets: validate a threat within 10 minutes and fully contain it within 60. Meeting both benchmarks turns security incidents from business disasters into manageable events, giving security leaders a concrete way to measure whether their response program actually works under pressure.
Key Takeaways
- The 10/60 framework sets two response benchmarks: validating a threat within 10 minutes and containing it within 60.
- Detection speed determines how much damage an attacker can do before a security team steps in.
- Consistent containment within the one-hour window depends on automated playbooks, not manual effort alone.
- Organizations sustain 10/60 performance through ongoing investment in tools, training, and repeatable processes rather than one-time fixes.
Core Elements of the 10/60 Framework
The 10/60 framework gives security teams two actionable benchmarks: validate a threat within 10 minutes and contain it within 60. This model focuses on realistic goals that drive faster, more effective response. To consistently hit these targets, organizations must simplify tools, improve coordination, and eliminate bottlenecks.
These are the core elements that make 10/60 achievable:
- Start With Rapid Validation: Confirming a threat within 10 minutes requires clear triage workflows and immediate access to relevant data. Analysts need contextualized alerts, unified visibility, and reduced noise so they can act without delay.
- Prioritize Fast Containment and Recovery: The 60-minute window calls for more than detection: teams must isolate compromised assets, remove malicious access, and initiate system recovery quickly. Delayed action gives attackers time to entrench and expand, turning minor intrusions into major breaches.
- Eliminate Technology and Process Barriers: Many security teams still rely on siloed tools, manual investigation steps, and limited automation, barriers that make 10/60 performance nearly impossible. Alert fatigue, slow correlation across systems, and fragmented response workflows create costly delays.
- Invest in People and Preparedness: Even with advanced tooling, skilled analysts and disciplined playbooks are essential. Ongoing training, well-documented procedures, and routine exercises prepare teams to act under pressure and reduce time-to-containment in real-world scenarios.
Reaching 10/60 requires more than speed: it takes a response model that is fast, focused, and repeatable, one that aligns technology, process, and people so threats get contained before they escalate. That alignment is what reduces impact and reinforces resilience.
Why Faster Detection Matters
Faster detection limits the damage attackers can cause. The quicker a threat is identified, the less time it has to escalate privileges, move across systems, or steal sensitive data. Catching a breach in its first minutes often means stopping it before any serious harm is done.
Despite this, many organizations still take weeks or months to detect an intrusion. According to Mandiant's M-Trends 2026 report, the global median attacker dwell time reached 14 days, giving intruders ample time to operate unnoticed. Shrinking that lag between compromise and discovery is exactly what the 10/60 framework is built to do.
Many attacks move faster than typical detection cycles allow:
- Phishing: Can lead to credential theft and cloud access within minutes.
- Ransomware: Can begin encrypting files in well under an hour.
- Business Email Compromise and Insider Threats: Can unfold before monitoring systems ever register suspicious behavior.
Modern attackers increasingly rely on automated toolkits to speed up lateral movement and data exfiltration, and traditional defenses often struggle to keep pace. Real-time analytics and automated investigation are now essential to reach the ten-minute detection goal. Cutting off threats early also keeps the cost of response under control.
How Swift Response Minimizes Risk
Stopping a threat within the first hour prevents it from spreading. Quick containment blocks key attacker actions like moving laterally, stealing data, escalating privileges, or launching ransomware before they cause real damage.
That containment follows a set sequence:
- Isolate and Suspend: Isolate affected systems and suspend compromised accounts.
- Capture Evidence: Preserve forensic evidence before systems are altered further.
- Remediate: Remove malware and fix the exploited vulnerabilities.
- Restore: Bring clean systems back online while keeping key stakeholders informed throughout so response stays coordinated.
Manual steps alone rarely meet the one-hour target. Automated playbooks in Security Orchestration, Automation, and Response (SOAR) and Endpoint Detection and Response (EDR) platforms can isolate networks or reset compromised credentials as soon as a threat is confirmed. Context, such as affected systems, attack method, and business priority, gets surfaced immediately so analysts can act faster.
Shrinking this breakout window reduces the impact, cost, and recovery time of an incident, and every minute saved shows up directly in the numbers. The IBM 2025 report found that breaches contained within 200 days cost an average of $3.87 million, compared to $5.01 million for those that took longer. That $1.14 million difference is a clear illustration of why the 60-minute mark matters, turning response from recovery into prevention.
Strategies to Achieve 10/60 in Your Organization
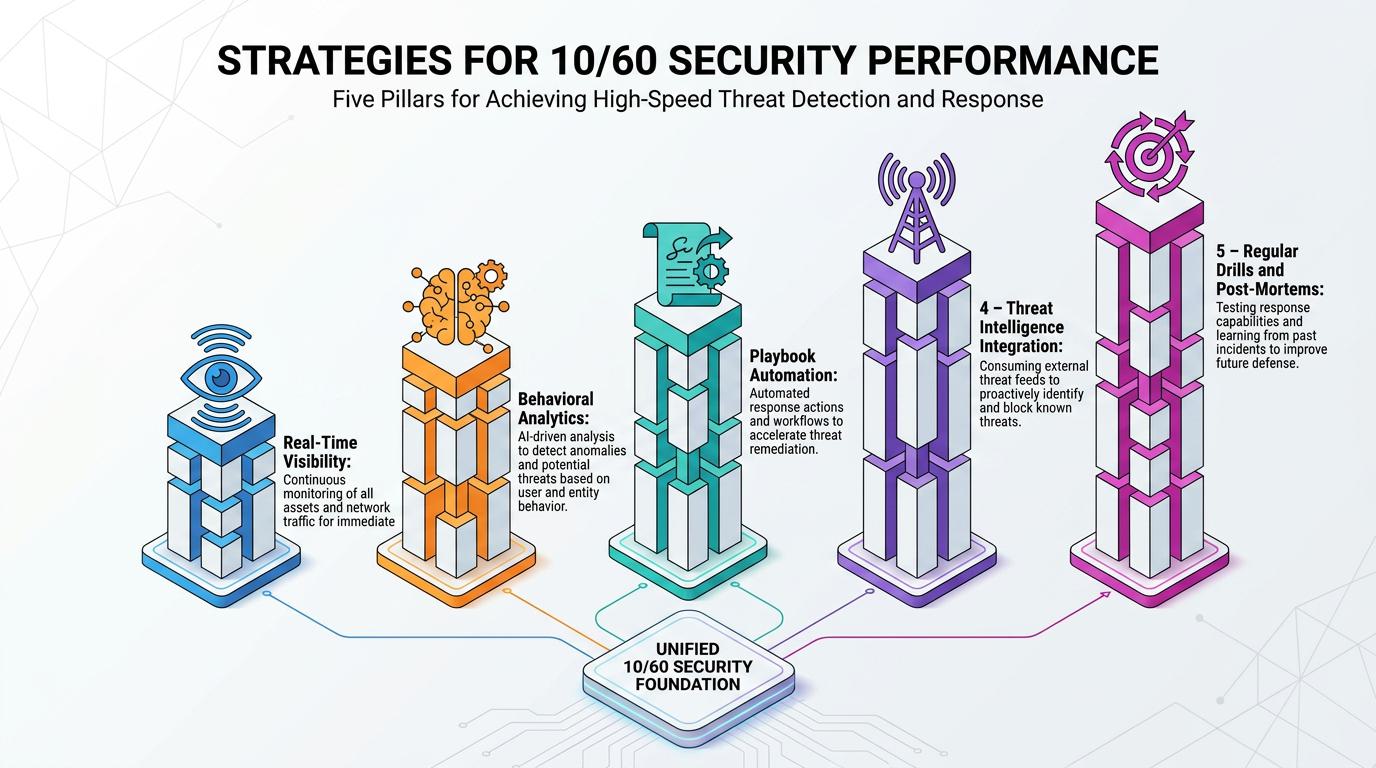
Hitting the 10/60 benchmark, detecting threats within 10 minutes and containing them within 60, requires a strong foundation for incident response, built on visibility, automation, preparation, and discipline. These strategies build the speed and structure needed to respond with confidence.
- Deploy Real-Time Visibility Across Your Entire Environment: Feed telemetry from endpoints, networks, and cloud services into a centralized console. This unified view ensures alerts appear quickly and provides the context needed to identify privilege abuse, lateral movement, or malware activity before it spreads.
- Shift From Rule-Based Filters to Behavioral Analytics: Use platforms that learn normal activity patterns and highlight subtle deviations, such as off-hours logins or unauthorized file transfers. These systems reduce false positives and help analysts focus on high-impact threats.
- Turn Playbooks Into Muscle Memory: Document every response step, assign clear responsibilities, and pre-authorize actions like isolating devices or disabling accounts. Consistent use of scripted procedures shortens decision time and prevents escalation during critical incidents.
- Infuse Threat Intelligence Into Detection and Response: Automate the flow of attacker tactics, techniques, and indicators into your security stack. Correlating fresh threat data with internal activity improves accuracy and speeds up threat validation.
- Drill Regularly and Refine After Every Incident: Run tabletop exercises each quarter to validate workflows, surface process gaps, and reinforce team readiness. Follow every drill or incident with a post-mortem, update your playbooks, and retrain staff to strengthen future response efforts.
Consistent 10/60 performance doesn't come from one-time changes. It grows through deliberate practice, ongoing adjustment, and a commitment to continuous improvement.
Key KPIs for 10/60 Framework Success
You prove progress toward the 10/60 benchmark by measuring a small set of time-based indicators and sharing them with leadership in plain business language. These include:
- Mean Time to Detect (MTTD) measures how long, on average, it takes to surface a new threat. Many organizations run far longer than the 10-minute target, a shortfall that only real-time monitoring and automation can close.
- Mean Time to Investigate (MTTI) tracks the minutes between detection and a validated understanding of scope and impact. Ten minutes is the goal; anything longer erodes precious containment time.
- Mean Time to Respond (MTTR) represents the clock that matters most to the business: how quickly you fully contain or eradicate the threat. Your target is 60 minutes, far below the multi-day response times some organizations still experience with legacy processes.
- Dwell Time measures total attacker presence in the environment. The global median sits at 14 days, as noted earlier, and driving that number toward zero limits data loss and legal exposure.
- False Positive Rate tracks the percentage of alerts you dismiss as benign. Lowering it frees analysts to focus on high-fidelity events and accelerates every other metric.
Track these KPIs against an initial baseline, chart improvement quarterly, and benchmark against established frameworks. Then translate each gain into business terms executives care about, such as fewer outages, smaller breach-response bills, and stronger compliance posture. Packaging that story consistently is what secures budget for the automation, staff, and training that keep an organization on pace for 10/60.
Speed Is the Best Defense You Can Build
The 10/60 framework works because it turns broad security goals into two numbers a team can rally around. Meeting them takes more than better tools. It takes clear triage workflows, automated playbooks, and people trained for the moment an alert fires. Organizations that shrink the distance between detection and containment change what a security incident means for their business, and a potential crisis becomes a contained, manageable event.