A cloud-era shadow IT policy must govern employee-provisioned services beyond traditional procurement, network, and identity controls. Effective governance combines continuous discovery, risk-based review, approved alternatives, and lifecycle oversight. None of that works without visibility into where these tools actually enter the organization, and for most companies that entry point is the inbox.
This article looks at why traditional shadow IT policies fall short against cloud adoption, how email quietly fuels the spread of unsanctioned tools, and what a modern governance framework looks like in practice. For security teams, getting this right is the difference between managing risk deliberately and discovering it after regulated data has already left the building.
Key Takeaways
Cloud services shift shadow IT governance from one-time procurement to continuous oversight.
Phishing drives most social-engineering-based cloud adoption, and legacy shadow IT policies were never built to govern it.
Employees can activate cloud services with a corporate email address outside established review processes.
Shadow AI has become a measurable driver of breach risk, with unsanctioned AI tools implicated in a fast-growing share of security incidents at breached organizations.
Email invitations and authorization grants can spread unmanaged access across teams.
Where Traditional Shadow IT Policies Fall Short in Cloud Environments
Traditional shadow IT policies rely on multi-week procurement cycles, network-based security barriers, and centralized login systems that IT manages. Few of those assumptions hold against email-based registration.
Four failure modes recur:
Instant Provisioning Can Evade Procurement Controls: Employees can activate services before established approval processes begin. Workflows built around manager sign-off, security review, and vendor assessment become less effective when an employee can adopt a collaboration platform or analytics tool before IT reviews it.
Single-Click Authorization Can Operate Outside Network Controls: Consent screens that grant apps access to corporate resources sit outside many network-based security tools. Standard remediation steps such as resetting passwords or requiring multifactor authentication may not address an external application's existing authorization grant.
Email-Based Invitations May Evade User Management Systems: Self-registration through application invitations can occur outside corporate identity management systems. These accounts may not appear in an IT-managed directory or enter standard identity governance and offboarding workflows.
Credit Card Provisioning Can Evade Financial Controls: Per-user pricing models can start with free tiers and scale automatically without purchase orders. Individual employees provision accounts, invite teammates, and grow spending well before finance notices, which undermines the procurement oversight legacy policies assume.
Together, these failure modes shift shadow IT governance away from a single procurement checkpoint and toward continuous oversight of applications, identities, permissions, data, and spending.
The Email Connection: How Shadow IT Spreads Through Inboxes
Email remains a primary entry point for shadow IT because employees receive application invitations, trial offers, and authorization requests that create ungoverned software usage without IT visibility or security review. According to Verizon's 2026 Data Breach Investigations Report (DBIR), phishing appeared in 66% of social engineering incidents — one more reason a policy built around procurement checkpoints misses so much of how these tools actually arrive.
Identity attacks can use malicious Open Authorization (OAuth) apps, abuse of legacy authentication, device code phishing, and adversary-in-the-middle (AiTM) techniques to seek persistent, covert access. Consent phishing and device code phishing can arrive as lures resembling routine app invitations or meeting requests, so the same inbox behavior that spreads legitimate tools can also spread malicious ones. Would a security team actually notice the difference between a real collaboration-tool invite and a consent-phishing lure built to look like one?
Below are three mechanisms that drive email-based shadow IT adoption.
1. Authorization Requests Create Persistent Third-Party Access
Authorization requests embedded in email can turn a routine user action into persistent third-party access. Attackers create pretexts that convince users to grant applications access to corporate data, and the resulting OAuth tokens can remain valid after the original interaction ends. Social engineers craft requests that appear legitimate, often mimicking trusted productivity tools or posing as vendor and executive requests, and employees may grant broad permissions without reading the scopes.
Once the target clicks the link and authorizes the application, the threat actor can gain access tokens with the requested scopes and refresh tokens for persistent access to the compromised account. Even a user who rejects an initial request may encounter a redirected phishing attempt. Policies therefore need to cover app consent, requested scopes, authorization ownership, and token revocation rather than treating the password as the only control point.
2. Colleague Invitation Chains Create Viral Spread
Colleague invitation chains can spread an unapproved application across teams before IT identifies the first account. Individual employees receive emails with social proof from trusted colleagues and subsequently invite their own teams, creating rapid unauthorized adoption. A single employee joining an unapproved collaboration platform triggers invitation emails to an entire department. Each recipient can add another network, and the tool may spread across several departments before IT sees any sign of it.
Accounts created this way can sit outside corporate identity governance. They may not enter the managed directory, inherit the organization's access policies, or trigger standard offboarding when someone leaves. The resulting population of ghost accounts can retain shared files and workspace access after the business relationship changes. Discovery processes should therefore connect invitation activity with application inventory, account ownership, role changes, and offboarding reviews.
3. Free Trial and Freemium Models Use Corporate Emails
Free trial and freemium models use the corporate inbox as a low-friction route to application adoption. These services may treat a corporate email address as an identity credential, which lets individuals provision accounts and upload data to third-party infrastructure before any security assessment occurs. Employees can reach full-featured platforms without IT oversight, often uploading customer records, financial projections, or proprietary intellectual property to providers that never underwent a security review.
Those uploads open data exfiltration paths that may not be inventoried. Free tiers can also encourage employees to invite teammates, expand usage, and create paid commitments before procurement or finance evaluates the service. A cloud-era policy can address this pattern by connecting discovery to data classification, vendor assessment, spending review, and a rapid path toward approved alternatives when the underlying business need is legitimate.
How AI Agents Amplify Shadow IT Risks
AI agents can turn shadow IT from a containment challenge into an enterprise-wide vulnerability by executing tasks along pathways that traditional controls were not designed to watch. Shadow AI is already a measurable share of that exposure: among organizations that experienced a breach, the share of security incidents involving unauthorized or ungoverned AI tools more than doubled year over year to 43%, according to IBM-sourced data reported by Cybersecurity Dive.
Three dynamics drive the exposure:
Security Through Obscurity Offers Less Protection: Sensitive information may remain protected in practice because employees cannot easily locate it. AI agents remove much of that friction, and a single prompt may surface confidential files that an agent with broad permissions can then move somewhere IT has never inventoried.
The Innovation Paradox: Organizations face a difficult choice as employees adopt AI tools to work faster. Banning AI outright can stifle innovation and competitiveness, while permissive approaches can create compliance violations and regulatory exposure.
Agent Sprawl Outpaces Inventory: Guidance on agent sprawl recommends discovering and categorizing agents across applications, including agents that come from shadow AI tools rather than sanctioned ones.
Organizations can implement structured guardrails that enable safe experimentation rather than broadly restricting AI adoption. This approach can transform shadow IT into visible, manageable innovation while maintaining security boundaries that protect sensitive data and support regulatory compliance. A selective approach also gives security teams a way to distinguish low-risk assistance from agents that access confidential data or execute consequential business actions.
Modern Shadow IT Policy Framework
A modern shadow IT policy treats unsanctioned adoption as business demand and channels it securely, since blocking cloud adoption outright can push it further out of view. A cloud-era framework rests on five components.
Continuous Discovery and Inventory
Continuous discovery gives security teams a current view of cloud applications, authorization grants, and email-driven adoption. No single method catches everything, so effective programs combine several data sources at once:
Network Traffic Analysis: Automated tools identify cloud application use by analyzing traffic patterns to cloud destinations.
Authorization Monitoring: Connection-based discovery tracks the application permissions employees grant through email-driven consent flows.
Email Threat Detection: Security tools flag phishing and account-compromise activity that often accompanies unsanctioned service adoption.
Cloud Access Security Brokers (CASBs): These sit between users and cloud services, providing visibility into sanctioned and unsanctioned usage across the enterprise.
Log Aggregation: Login patterns pulled from identity systems reveal which external services employees access using corporate credentials.
The National Institute of Standards and Technology (NIST) calls for current and automatically updated inventories of the internal and external software, services, and systems an organization uses, and names shadow IT identification as one reason to maintain them. Combining these data sources helps teams find applications that any single discovery method might miss.
Risk-Based Assessment
Risk-based assessment helps organizations balance an application's business value against its security and compliance exposure. Structured processes can score discovered applications using standardized frameworks that compare risk factors with business justification. Application security reviews evaluate login mechanisms, data protection standards, compliance certifications, and vendor security posture. Data classification alignment gives sensitive information appropriate protection regardless of platform, focusing security resources on genuine data protection risks instead of blanket application blocking.
Tiering makes this workable at cloud scale. A human resources (HR) assistant answering policy questions carries less risk than an autonomous agent making hiring decisions, and review depth should track that difference. The same logic applies to software as a service (SaaS) generally. Map data classification levels such as public, internal, confidential, and regulated to scrutiny tiers. Organizations can automate approval for tools that touch only public or internal data and reserve full vendor review for applications that handle regulated records or connect to systems of record. This governance model directs review effort toward the applications with the greatest potential impact.
Selective Enablement Strategy
Selective enablement gives employees approved ways to meet business needs without routing every request through a lengthy review. Effective policies pair vetted catalogs with rapid provisioning: self-service for pre-approved tools and a clear exception workflow for legitimate requirements the catalog does not cover. Fast-track provisioning reduces the friction that drives shadow IT adoption while retaining oversight.
The workflow can assign an application owner, identify the data classification involved, and route higher-risk requests to security, privacy, or legal review. It can also define what happens when a trial becomes a paid service or expands to another department. Pairing the catalog with security awareness training on consent prompts and app invitations gives employees a way to recognize social engineering requests worth refusing. This model channels demand toward reviewed services without treating employees who identify useful tools as policy violators.
OAuth Token and Identity Lifecycle Governance
OAuth token and identity lifecycle governance connects third-party access to ownership, role changes, and offboarding. OAuth tokens granted to SaaS integrations require documented ownership and revocation procedures. A series of supply-chain incidents followed the same pattern: attackers breached a third-party integration provider, took customer-authorized OAuth tokens, and used them to pull customer relationship management (CRM) and support-case data from downstream organizations.
The tokens were legitimate customer-authorized grants that sat outside an inventory, scope review, or expiry schedule. A cloud-era policy can record who authorized each integration, what data it can reach, and which business process depends on it. Teams can tie revocation to offboarding and role changes, limit scopes to what the integration actually uses, and review inactive grants. These controls establish tokens and nonhuman identities as lifecycle-managed access.
Regulatory Obligation Mapping
Regulatory obligation mapping connects each discovered application with the contractual and data-handling requirements its use may trigger. Unsanctioned SaaS tools create compliance exposure when regulated data lands in services that have not completed legal, privacy, or security review. Two regulations recur most often in this mapping exercise:
Regulation | Regulated Data | Cloud-Use Requirement
|
|---|---|---|
General Data Protection Regulation (GDPR) | Personal data of EU individuals | Legal teams assess whether a newly discovered processor relationship has the required governing terms before approving continued use |
Health Insurance Portability and Accountability Act (HIPAA) | Electronic protected health information (ePHI) | A covered entity may use a cloud service to store or process ePHI only when it enters into a HIPAA-compliant business associate agreement with the provider |
A shadow file-sharing account holding patient data may lack that agreement entirely. Mapping newly discovered applications to the regulations their data triggers can route regulated-data requests to legal before provisioning and create documentation for later audits. Together, these five components turn ad hoc discovery into a governance program — but only if security teams can see how a service enters the organization in the first place.
How Behavioral AI Discovers Shadow IT Through Email
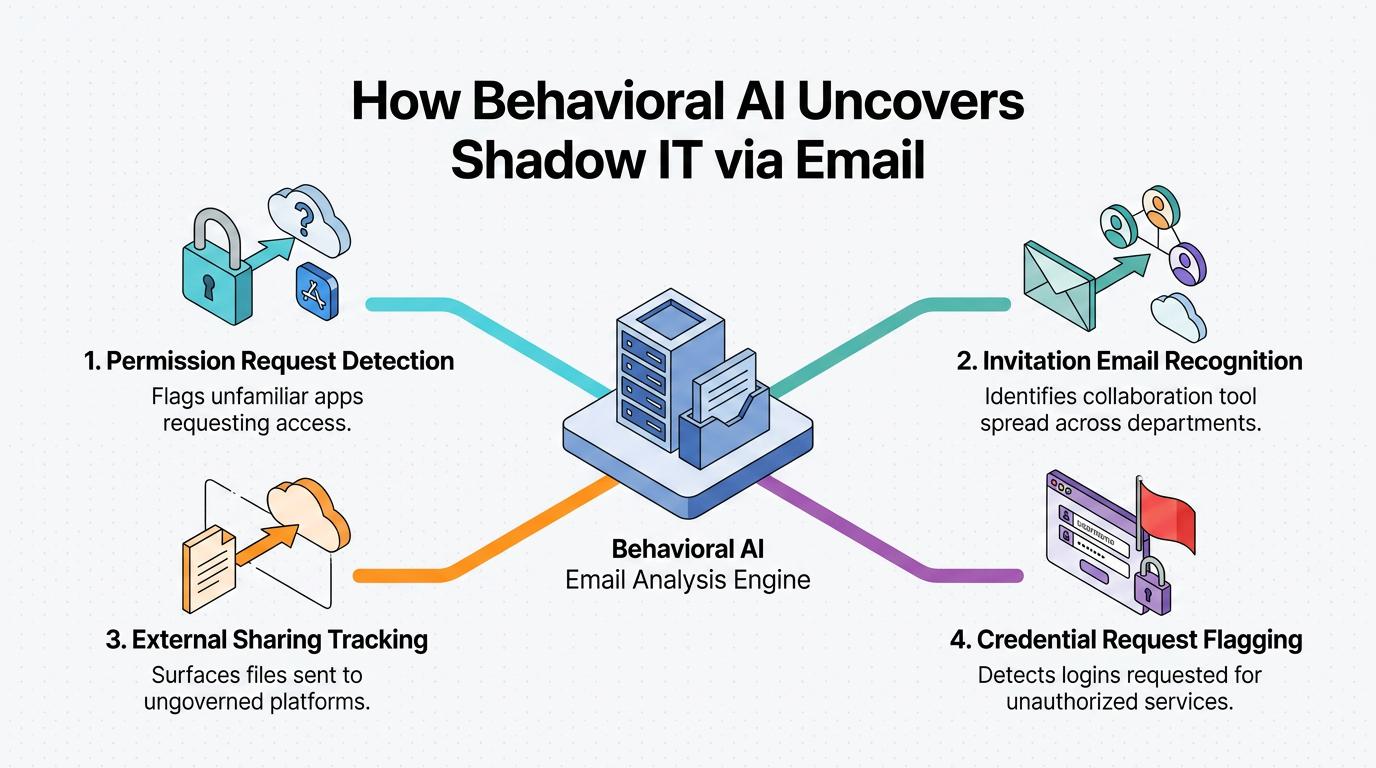
Abnormal uses behavioral AI to help surface shadow IT through email permission requests, app invitations, credential requests, and file-sharing activity. Because Abnormal connects to Microsoft 365 and Google Workspace through application programming interfaces (APIs), it works alongside the existing email gateway (SEG) and identity controls and adds a complementary layer. It examines email content, sender information, and behavioral signals so security teams can receive earlier warning of suspicious adoption patterns.
The system watches for specific email patterns that can signal unauthorized app usage:
Permission Request Detection: Behavioral AI is designed to recognize when unfamiliar applications ask for access through email. It weighs sender and behavioral signals against the access being requested, separating legitimate business apps from unapproved services asking for excessive permissions.
Invitation Email Recognition: Behavioral AI is designed to identify invitation emails from collaboration platforms by recognizing typical invitation language and sender addresses. Security teams can see when a tool starts spreading across departments.
External Sharing Tracking: Behavioral AI helps surface employees sending company documents to outside platforms. It weighs file attachments, external recipients, and sharing frequency to find data moving to ungoverned services.
Credential Request Flagging: Behavioral AI can help flag emails requesting login credentials for services outside company identity systems, so teams can address unauthorized credential sharing early.
Together, these email-focused signals can complement application, network, identity, and procurement data by showing how an unapproved service first enters the organization and begins spreading between employees.
Building Your Cloud-Era Shadow IT Governance Strategy
Cloud-era shadow IT governance works when organizations make secure adoption easier and assign clear ownership for discovery, assessment, approval, and access reviews. Implementation can begin by identifying accountable teams, connecting existing data sources, defining review tiers, and setting measurable timelines for resolving discovered applications.
The path forward combines continuous discovery, risk-based assessment, selective enablement, lifecycle governance for tokens and identities, and email threat detection working together as one governance program. This approach gives employees a practical route to adopt useful cloud services while giving security, procurement, and compliance teams the visibility and ownership they need.
Gartner named Abnormal a Customers' Choice in the 2026 Gartner® Peer Insights™ Voice of the Customer for Email Security. Ready to discover hidden shadow IT risks in your email environment? Get a demo to see how Abnormal's behavioral AI helps surface unauthorized software adoption through email analysis.
Frequently Asked Questions
What Are Common Examples of Shadow IT?
Common examples include file-sharing services signed up with a corporate email, generative AI assistants used to summarize internal documents, unsanctioned messaging or collaboration platforms adopted by a single team, browser extensions granted access to work accounts, and personal cloud storage used to move files between devices. Each of these can look harmless in isolation but tends to accumulate quietly across departments until sensitive data ends up in services no one has reviewed.
Who Is Responsible for Managing a Shadow IT Policy?
Responsibility is usually shared rather than owned by a single team. Security typically leads discovery, risk assessment, and enforcement, while IT owns the sanctioned catalog and identity controls. Procurement and finance oversee vendor and spending controls, legal and privacy handle regulatory review, and business unit leaders own the demand side by surfacing legitimate tool needs. A functional policy names an accountable owner for each of these steps so nothing falls between roles.
Is Shadow IT Always a Bad Thing?
Not necessarily. Shadow IT usually reflects a real business need that sanctioned tools do not meet, which is useful signal for IT and security teams. The risk is not the demand itself but the lack of visibility, review, and lifecycle controls around the tools employees adopt. A modern policy treats shadow IT as an input to the catalog and procurement process rather than a violation to punish, which encourages employees to raise needs earlier rather than route around IT entirely.
How Do You Measure the Success of a Shadow IT Policy?
Useful metrics fall into a few categories: discovery coverage (how many applications, OAuth grants, and email-driven signups the program identifies), time to review (how quickly discovered applications move through risk assessment), remediation outcomes (revoked tokens, offboarded accounts, applications migrated to sanctioned alternatives), and demand signals (requests routed through the catalog versus adopted independently). Tracking these over time shows whether the policy is shifting adoption toward reviewed channels rather than simply cataloging exposure after the fact.