Key Insights
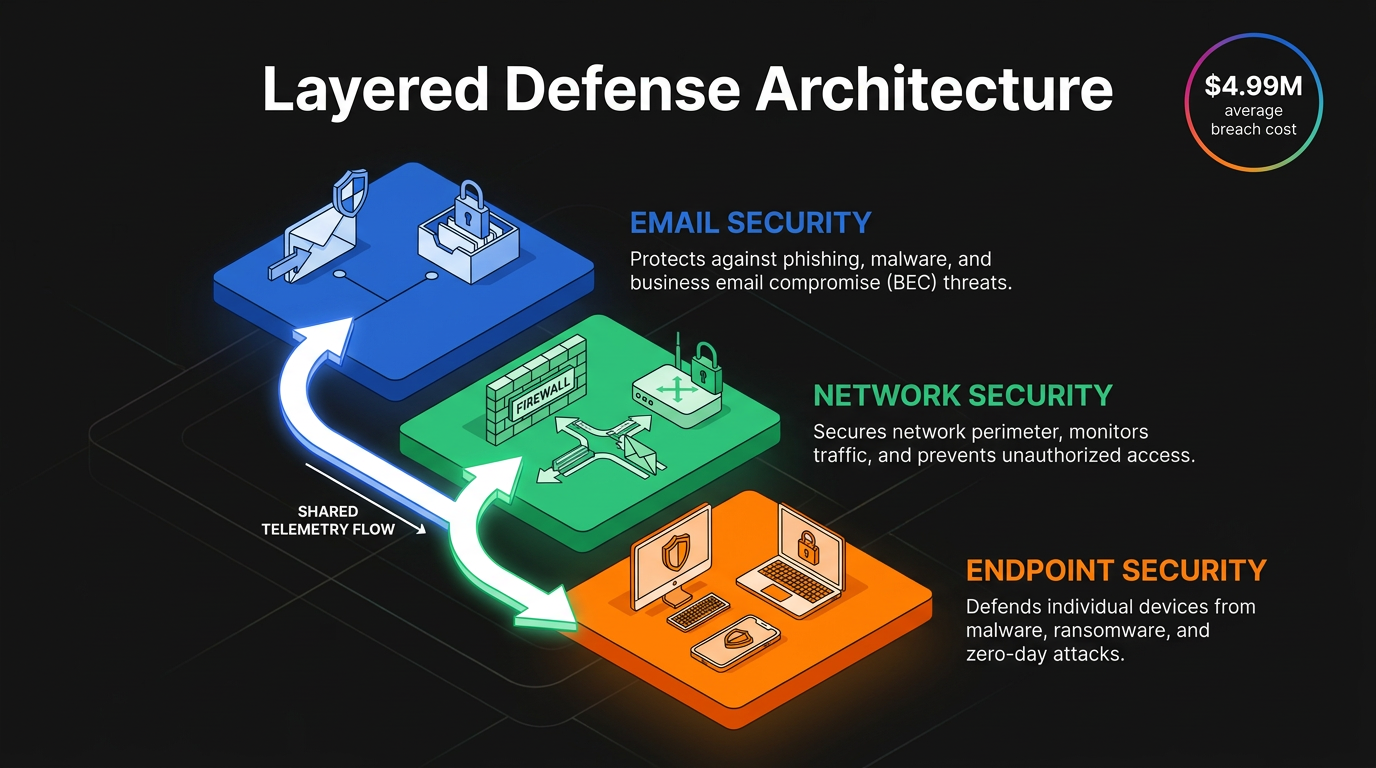
Effective cybersecurity solutions center on three core technologies: endpoint protection, network security, and email security. With the IBM breach cost report putting the global average breach cost at $4.99 million, the stakes call for precision over proliferation.
Knowing what to do after a common phishing attack matters. Prevention through a layered defense architecture matters more. These technologies form a security foundation in which each layer complements the others and closes gaps attackers exploit. Deploying them correctly can reduce risk, satisfy compliance requirements, and maintain visibility without budget bloat or tool sprawl.
Key Takeaways
Endpoint protection combines preventive controls with behavioral detection and response on laptops, servers, and mobile devices.
Network security uses segmentation, traffic inspection, encryption, and access controls to restrict unauthorized movement.
Email security addresses phishing, business email compromise (BEC), credential theft, and other inbox-based attacks.
Shared telemetry across security layers gives analysts clearer context and supports faster, more consistent incident response.
1. Endpoint Cybersecurity Solutions
Endpoint protection controls keep laptops, servers, and mobile devices connected to your network from becoming entry points. A single unmanaged device with stale patches can give an attacker a foothold that downstream tools may not see until data starts moving. An Endpoint Protection Platform (EPP) blocks known threats with next-generation antivirus, device encryption, and application control. Endpoint Detection and Response (EDR) monitors what slips past prevention, flags unusual behavior, and quarantines compromised hosts.
Platforms that merge both engines can stop commodity malware and identify fileless exploits, common living-off-the-land attacks, and insider abuse risks without requiring separate agents.
Imagine a situation where a marketing employee receives a portable document format (PDF) invoice that appears legitimate. The EPP scans the file after download and allows it because no known malware signatures match it. When the employee opens the PDF, it executes a PowerShell script that attempts to contact a command-and-control server. The EDR component flags the behavior, blocks the network connection, quarantines the endpoint, and alerts the security team. The team investigates, identifies a zero-day attack technique, and pushes new detection rules to other endpoints.
Why It Matters
Downtime after ransomware and wiper attacks erodes revenue and customer trust while increasing recovery costs. Abnormal's AI-driven attack research tracks a related trend: as attackers automate targeting and social engineering, security teams are compressing the time between detection and containment.
Detailed endpoint telemetry records process launches, file changes, isolation actions, and other response events. That record gives chief information security officers (CISOs) clear board-level metrics, helps information technology (IT) teams reduce manual investigation work, and provides compliance officers with evidentiary trails for Health Insurance Portability and Accountability Act (HIPAA) or Payment Card Industry Data Security Standard (PCI DSS) reviews.
Key Features to Look For
These capabilities separate an endpoint platform that reduces risk from one that only generates alerts:
Behavioral Analytics: Pair behavioral machine-learning antivirus with scoring that judges each process by intent as well as signature.
Ransomware Guards: Rapid file-change detection paired with automated rollback limits how much data an encryption routine can damage before the platform isolates the host.
Application Allow-Listing and Exploit Protection: Allow-listing blocks unapproved executables. Exploit protection hardens browsers, office suites, and legacy applications that rarely receive patches.
Centralized Dashboards: A centralized management console provides visibility across endpoint fleets and lets teams push updates from one interface.
Together, these features support prevention, investigation, containment, and recovery without forcing analysts to switch constantly between disconnected tools.
Expert Tips
These practices can help security teams get more value from endpoint protection investments:
Teams can start with a cybersecurity risk assessment to identify devices that handle sensitive data or access privileged networks, then prioritize those assets.
Enabling automated patch management for operating systems and common applications can close exploitable gaps before attackers scan for them.
Requiring multi-factor authentication (MFA) controls at logon and during privilege escalation can limit the damage caused by stolen credentials.
Streaming endpoint alerts into a security information and event management (SIEM) platform can help teams prioritize host isolation and preserve endpoint evidence for investigation.
Applied together, these steps strengthen endpoint coverage while giving analysts clearer evidence for investigation and compliance reporting.
2. Network Cybersecurity Solutions
Network cybersecurity solutions should block, inspect, and verify traffic to help prevent attackers from reaching sensitive data or moving between systems unnoticed. This layer works with endpoint protection by adding controls at the perimeter and between internal resources. Cloud gateways, edge firewalls, and secure virtual private network (VPN) connections determine which connections reach the environment. Inside, segmentation divides the corporate local area network (LAN) into tightly scoped zones, while microsegmentation extends those boundaries to individual workloads. Continuous monitoring then watches east-west traffic for subtle signs of compromise.
Consider, for example, a finance employee working remotely who connects to the corporate network through a VPN. The perimeter firewall authenticates the connection with MFA and validates the device's security posture before allowing access. Later, the same account attempts to reach engineering servers outside its normal scope. The network security system flags the unexpected lateral movement attempt, restricts access, and alerts the security team to investigate a possible account compromise.
Why It Matters
Attackers often enter through a vendor's compromised software update or a partner's unsecured cloud account, then pivot across flat networks. The Verizon Data Breach Investigations Report found that supply-chain breaches tied to a third party doubled to 30% of incidents. Once inside, ransomware crews can move laterally, encrypt backups, and exfiltrate data for double extortion.
Segmentation helps determine whether a supplier incident remains isolated or reaches internal systems. Automation also reduces the time IT teams spend maintaining access control lists on legacy hardware. Compliance officers gain evidence of PCI DSS and Sarbanes-Oxley Act (SOX) controls, including encryption in transit, access logs, and segmentation records.
Key Components
A modern network security architecture rests on these building blocks:
Firewalls: These systems filter packets, perform stateful inspection, and enforce segmentation boundaries. Next-generation models inspect application context, allowing payroll traffic while rejecting the same protocol from an unknown host.
Intrusion Detection and Intrusion Prevention Systems: Intrusion detection systems (IDS) and intrusion prevention systems (IPS) analyze flow records and payloads. An IDS alerts analysts to anomalies. An IPS automatically blocks malicious sequences that match high-confidence detection logic.
Identity-Aware Access Controls: These controls authenticate identities when users or devices request sensitive resources. Policies can assess device health, time of day, assigned role, and resource sensitivity before granting minimal permissions.
Strong Encryption: Transport Layer Security (TLS) protects web traffic. Organizations can extend encryption to application programming interfaces (APIs), remote management ports, and file transfers.
These components create overlapping checkpoints that constrain access while preserving the network visibility analysts need during an investigation.
Expert Tips
These practices can help turn an open network into a series of controlled checkpoints:
Security teams can map critical assets, then write least-privilege firewall rules that expose only required ports and protocols.
Organizations can require remote employees to connect over VPN or identity-aware remote access services with MFA enforced.
Segmenting production, development, and administrative networks can make it harder for a single phished credential to cross security boundaries.
Teams can schedule regular penetration tests and vulnerability scans, then feed the findings into IPS signatures and access policies.
Regular validation keeps network controls aligned with infrastructure changes rather than leaving policies frozen at their original deployment state.
3. Email Cybersecurity Solutions
Email cybersecurity solutions help prevent high-impact threats, including phishing attacks targeting employees and business email compromise attacks, from reaching employee inboxes. This pillar complements endpoint and network defenses because email remains one of the most common attack vectors. Modern platforms combine spam and phishing filters, attachment sandboxing, authentication checks, and continuous behavioral analysis. Legacy filters searched for known malicious domains. Criminals now create one-time URLs and AI-written messages that resemble legitimate correspondence.
For instance, picture a chief financial officer (CFO) who receives an email that appears to come from the chief executive officer (CEO) and requests an urgent wire transfer. The email security platform checks the sender against Domain-based Message Authentication, Reporting, and Conformance (DMARC) records and identifies a slightly misspelled domain. The platform quarantines the message and notifies the security team and CFO. After reviewing the incident, the team creates new detection rules, conducts targeted training, and strengthens wire transfer verification procedures.
Why It Matters
Email carries an outsized share of the financial damage from cybercrime. The FBI Internet Crime Complaint Center (IC3) put BEC losses above $3 billion, second only to investment fraud.
For CISOs, detailed reporting from the email layer demonstrates diligence to boards and auditors. For IT managers, machine-learning filters can reduce false positives that would otherwise overwhelm help-desk queues. Compliance officers gain immutable logs that connect blocked messages to policy controls, which simplifies PCI DSS and HIPAA audits. Abnormal complements existing email security infrastructure by applying behavioral AI to email and identity signals.
Key Features to Look For
The email controls below address both the credential-theft side of phishing and the social engineering behind BEC:
Strong Authentication: MFA for mailboxes can help ensure that stolen passwords alone do not grant access.
End-to-End Encryption: Encryption keeps sensitive data unreadable while it moves between organizations.
AI-Driven Anti-Phishing Engines: These tools evaluate sender reputation, identify look-alike domains, and detonate suspicious attachments in isolated sandboxes.
Protocol Enforcement: Sender Policy Framework (SPF), DomainKeys Identified Mail (DKIM), and strict DMARC policies reduce an attacker's ability to spoof a trusted domain.
Behavioral Analytics: These controls learn user and vendor interaction patterns, so an unexpected payment request or unusual login can trigger additional review.
SIEM or Security Orchestration, Automation, and Response (SOAR) Integration: Alerts can flow into SOAR or SIEM workflows for broader incident response.
A balanced email security program combines these controls instead of relying on a single authentication protocol, content filter, or user training program.
Expert Tips
These controls can help turn email from an easy entry point into a more difficult one:
Organizations can publish a reject-level DMARC policy, consistent with the Cybersecurity and Infrastructure Security Agency's federal email security directive, to reduce domain spoofing.
Requiring MFA across mailboxes and re-verifying access after a phishing incident can help contain compromised credentials.
Teams can run regular simulated phishing drills, then coach employees who click a suspicious link or open a rogue attachment.
Security teams can review executive and finance mailboxes regularly because those accounts often attract BEC attempts and contain sensitive information.
These practices connect technical controls with user behavior, incident response, and authentication policies rather than treating inbox protection as an isolated function.
Build an Integrated Cybersecurity Foundation
Endpoint, network, and email security form the backbone of a credible defense strategy, and they deliver the most value when they share telemetry. When an EDR alert, a segmentation violation, and a quarantined email appear in one timeline, an analyst can trace a campaign from initial access through an attempted lateral movement attempt. Shared least-privilege policies and coordinated detection across the layers create a feedback loop that helps teams close gaps before attackers exploit them.
Integration does not require every control to come from the same platform. Security leaders can focus on consistent identity policies, compatible event formats, and tested response procedures. An effective foundation gives analysts context to act and compliance teams reliable evidence.
Of the three layers, email carries the most financial exposure and the hardest detection problem, which is where Abnormal fits into the stack. Abnormal applies behavioral AI to cloud email and identity signals, modeling how each employee, vendor, and workflow normally behaves so it can surface socially engineered attacks that pass authentication and slip past signature-based controls. It integrates with Microsoft 365 and Google Workspace through API, complementing existing endpoint, network, and gateway investments rather than replacing them, and feeds alerts into the SIEM and SOAR workflows that tie the three layers together.
That approach is reflected in customer feedback: Abnormal was named a Customers' Choice in the 2026 Gartner® Peer Insights™ Voice of the Customer for Email Security, the only vendor to earn the distinction three consecutive times. To see how behavioral AI closes the email gap in your layered defense, book a demo with the Abnormal team.
Frequently Asked Questions
How Do You Integrate Endpoint, Network, and Email Security Telemetry Into a Single Timeline Without Purchasing All Tools From the Same Vendor?
Route events from each layer into a SIEM or SOAR platform that normalizes data using a common taxonomy such as MITRE ATT&CK, with aligned user identities, device names, and timestamps across sources. From there, write cross-layer detection rules that trigger when endpoint, network, and email anomalies appear in the same user session, and validate the pipeline periodically with simulated attacks to confirm the kill chain reconstructs accurately as vendors update log formats.
What Is the Recommended Priority Order for Implementing These Three Cybersecurity Layers if a Business Has Limited Budget and Resources?
Budget-constrained organizations should typically start with email security, since it addresses the attack vector responsible for most successful breaches and requires less infrastructure than a full endpoint or network rollout. Endpoint protection comes next for assets handling sensitive data or privileged access, followed by network segmentation and monitoring to contain threats that bypass the first two layers. Organizations facing sector-specific threats or compliance mandates may need to adjust this order based on their own risk assessment.
How Does Behavioral AI in Email Security Differ From Traditional Rule-Based Filtering When Detecting Sophisticated BEC Attacks?
Rule-based filters rely on predefined signatures and known malicious domains, which attackers sidestep by registering fresh domains, mimicking legitimate senders, and sending clean messages that pass SPF and DKIM validation. Behavioral AI treats communication context itself as a detection signal, learning the workflows, timing, and vendor relationships that define normal activity so it can flag a wire transfer request that falls outside those patterns even when every authentication check passes.
What Specific Compliance Evidence Do Endpoint, Network, and Email Security Tools Need to Generate for HIPAA and PCI DSS Audits?
Both frameworks require immutable, timestamped records that auditors can correlate across systems. For HIPAA, that generally means encryption logs, role-based access records, and audit trails covering any system that stores or transmits protected health information. For PCI DSS, evidence centers on vulnerability scans, patch and firewall rule reviews, intrusion detection histories, and secure transmission records for cardholder data.
How Can Small and Mid-Sized Businesses Implement Network Segmentation and Microsegmentation Without Dedicated Security Staff?
Smaller teams can lean on managed detection and response providers or cloud-based security platforms to handle policy configuration and monitoring on their behalf. Software-defined networking tools with pre-built segmentation templates let non-technical administrators apply least-privilege rules through guided interfaces, and cloud-native environments simplify microsegmentation further because hypervisors enforce workload isolation through identity and policy tags rather than physical network changes. Starting with basic VLAN separation for guest wireless, point-of-sale, and administrative networks lets a team expand into microsegmentation as resources permit.