Key Insights
Identity-based attacks surged 32% in the first half of 2025, according to the Microsoft Digital Defense Report 2025, with Microsoft 365 accounts a frequent target as attackers chase credentials that unlock cloud and productivity environments.
That sustained targeting fuels Microsoft email scams: phishing messages, fake account alerts, billing notices, and token-abuse lures crafted to pass as legitimate Microsoft 365 communications. Today's variants have moved well past misspelled senders and clumsy login pages, extending into session-layer compromises, abuse of trusted services like SharePoint and OneDrive, and AI-polished content that closely mirrors real business workflows.
This guide breaks down the most common Microsoft email scams, the detection signals that still hold up when linguistic red flags disappear, and the containment steps that matter most after a credential or session is captured. The guidance also covers where traditional email gateways fall short against identity-layer attacks and which layered controls close those gaps before a single compromised account becomes a wider intrusion.
Key Takeaways
Attackers who complete an adversary-in-the-middle (AiTM) or device code flow hold valid session cookies or refresh tokens, so containment depends on revoking sessions rather than resetting passwords alone.
Lures delivered through genuine SharePoint and OneDrive services pass sender and domain reputation checks, which leaves communication context as the main remaining detection signal.
Generative AI has removed many grammar and formatting errors that content filters and user training once relied on, shifting useful detection signals toward behavior and context.
Fake IT support campaigns can move from inbox flooding to Teams calls and remote access tools, making email one component of a broader intrusion.
Models that evaluate workflow cadences, sender-recipient patterns, and timing can surface deviations where delivery-layer tools have limited visibility.
Why Microsoft Email Scams Keep Working at Scale
Microsoft email scams keep working because they combine brand trust, user urgency, and attack methods that often leave few traditional indicators behind. Microsoft 365's broad footprint gives attackers a familiar surface, and users are conditioned to act quickly on Microsoft-branded alerts. The threat has also grown more accessible, with commercial phishing-as-a-service kits and rented infrastructure that imitate familiar login experiences.
These campaigns put pressure on defenses that depend on spoofed sender domains and other known indicators. Attackers can instead use trusted services, authenticated sessions, and convincing business context to make malicious messages appear legitimate.
Top 8 Microsoft Email Scam Variants Security Teams Should Know
Microsoft email scams now span multiple techniques, from credential theft to token abuse and trusted-service impersonation.
1. Fake Account Alerts
Attackers send emails that mimic Microsoft security notifications, warning of unauthorized sign-in attempts or unusual account activity. These messages pressure recipients into clicking a link to verify their account, leading to Microsoft credential-harvesting pages designed to mirror the Microsoft login experience. The urgency exploits the same instinct that makes legitimate security alerts effective.
2. Fake Billing Notices
These messages impersonate Microsoft 365 billing or renewal services, claiming a subscription is expiring or that Microsoft applied an incorrect charge. Attackers direct recipients to fraudulent payment or refund portals. The financial pressure these scams create often overrides the urge to verify through official channels.
3. Fake Support Messages
Scammers posing as Microsoft Support claim to resolve non-existent issues, directing users to call fake service numbers or install remote access tools. Some campaigns initiate email bombing, flooding a target's inbox to create confusion, then follow up with a spoofed IT department call or a Microsoft Teams message offering to help. Microsoft threat intelligence has documented ransomware attack operators using this sequence to talk employees into granting Quick Assist or similar remote sessions. The phone interaction adds a layer of perceived legitimacy that email alone cannot provide.
The primary control point remains the inbox, where the initial flood and the follow-up lure arrive. Email security tools can help with that component. Organizations should also pair them with Teams external-access restrictions and remote-access tool policies to cover the non-email channels these campaigns use.
4. Session Hijacking Through AiTM
AiTM phishing deploys a reverse proxy between the victim and Microsoft's real authentication portal, relaying the entire login flow, including multi-factor authentication (MFA) challenges. The attacker captures the session cookie after MFA completion, gaining access without ever needing the user's password directly.
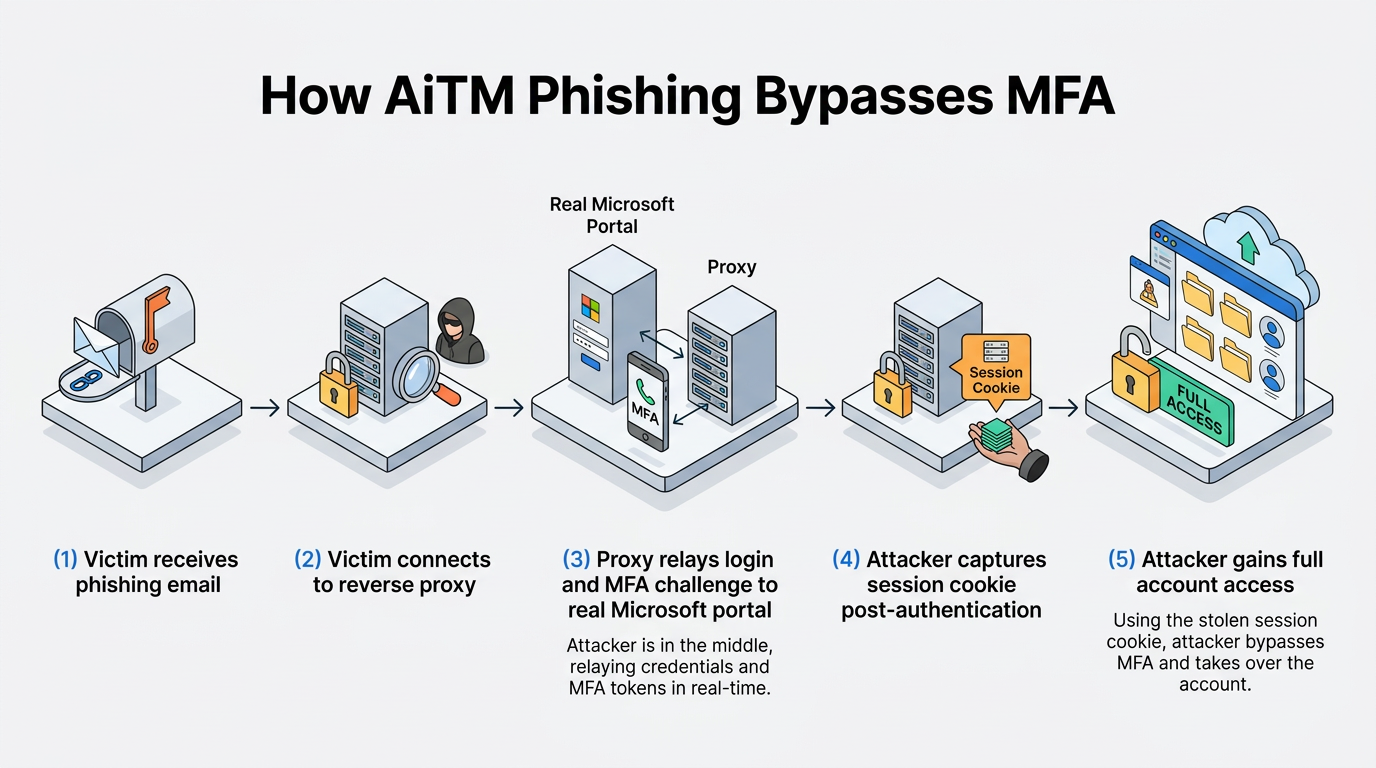
Because the compromise occurs post-authentication at the session layer, delivery-layer tools may have no malicious artifact to evaluate; security teams instead detect it through unusual session behavior after sign-in. Recent analysis of the Mirage2FA AiTM phishing kit found it delivering its proxy through HTML attachments and stealing post-authentication sessions, which is why a password reset alone may not end the intrusion.
5. Device Code and OAuth Consent Phishing
Device code and OAuth consent phishing use two token-based paths:
Device Code Phishing: Device code phishing exploits the OAuth device authorization flow, manipulating victims into entering an attacker-generated code at Microsoft's legitimate device login page and unknowingly granting the attacker access tokens. Because the page is genuine, there is no fake URL to inspect. A device code phishing analysis describes how the resulting refresh tokens survive a password reset unless administrators explicitly revoke them.
OAuth Consent Phishing: OAuth consent phishing takes a different path: tricking users into authorizing malicious third-party applications that receive persistent access to mailbox data, through a real consent screen hosted by a legitimate identity provider such as Microsoft. Consent grants persist until an admin revokes the app's access.
Microsoft offers a managed Conditional Access policy that blocks device code flow and recommends it wherever the organization doesn't need the feature.
6. QR Code Phishing
QR code phishing encodes malicious URLs within QR code images rather than displaying them as clickable links. Email security tools that scan only for suspicious URLs may find nothing to flag. The attack also shifts to the victim's mobile device, usually outside enterprise endpoint protections and belonging to the employee, not the company.
Documented campaigns have used QR codes embedded in PDF attachments, branded as HR communications or salary updates, to redirect victims to credential-harvesting pages impersonating Microsoft 365 login portals. Some newer kits route QR lures to Microsoft's legitimate device sign-in page.
7. AI-Generated Spear Phishing
Attackers are using generative AI to craft phishing emails that remove common grammatical errors, awkward formatting, and generic greetings traditionally used as detection signals. AI-generated lures mirror professional communication patterns with high semantic plausibility, so distinguishing them from legitimate Microsoft messages by reading alone is difficult. When linguistic red flags are gone, content-based filtering loses much of its signal.
One documented campaign described by Microsoft showed AI-generated code obfuscating a phishing payload within an SVG file, producing a structurally novel artifact that challenged signature-based detection. Microsoft's Security Copilot assessed the code as "not something a human would typically write from scratch due to its complexity, verbosity, and lack of practical utility."
Microsoft's takeaway from that case is that AI does not fundamentally change the core artifacts detection systems rely on, so Microsoft favors models that evaluate multiple dimensions rather than the payload alone.
8. Native Phishing in SharePoint and OneDrive
Attackers abuse legitimate Microsoft services like SharePoint and OneDrive as phishing delivery infrastructure. Because lures originate from trusted Microsoft domains, they pass sender and domain reputation checks, and advice to inspect sender domains offers little help when that domain is genuinely sharepoint.com.
In January 2026, Microsoft reported a multi-stage AiTM campaign that led to business email compromise (BEC) in the energy sector. The attackers sent phishing emails from compromised partner accounts, used authentication-gated SharePoint URLs, and carried subjects mimicking document-sharing workflows, then created inbox rules for persistence before moving into BEC across multiple victim organizations. Microsoft noted that these authentication flows on trusted infrastructure "frequently evade traditional email-centric detection mechanisms."
Why These Attacks Evade Current Defenses
The detection gap in modern Microsoft scams reflects a structural mismatch between where attacks originate and where most defenses operate.
Email gateways (SEGs) operate primarily at the delivery layer, evaluating sender reputation, URL reputation, and attachment signatures. Many of the variants above carry none of those indicators, which creates blind spots across several areas:
No Traditional Malicious Indicators: Many of these scams contain no malware, no known-bad URL, and often no spoofed domain, leaving delivery-layer tools little to flag.
Compromise at the Identity Layer: Compromises that begin with a stolen session or token play out at the identity layer, where delivery-focused tools have limited visibility and can lead to a serious data breach.
Abuse of Trusted Infrastructure: Attackers route phishing through SharePoint, encode URLs in QR codes, and hijack authenticated sessions through AiTM proxies, all of which can evade delivery-layer checks.
AI-Polished Content: Generative AI removes the linguistic red flags that content-based filters rely on. Microsoft recommends weighting behavioral signals, delivery infrastructure, and message context over linguistic patterns.
These gaps call for a different detection model. Security leaders evaluating their Microsoft 365 security posture should ask whether their SEG can surface compromise signals with no known-bad artifact to find.
How to Recognize a Suspicious Microsoft Email
The most reliable detection heuristics are losing value as attackers shift to trusted infrastructure, so security teams should help users evaluate multiple signals together.
Several indicators remain useful when evaluated in context:
Suspicious Sender Addresses: The full email address, not just the display name, may reveal subtle email domain variations such as @micros0ft.com or unexpected subdomains. However, this check offers no protection when the sending domain is genuinely sharepoint.com or office365.com.
Mismatched or Hidden Links: Hovering over links before clicking can surface redirects through unfamiliar or shortened URLs. Legitimate Microsoft links typically resolve to microsoft.com or office.com, though QR code phishing often bypasses this check.
Urgent or Threatening Language: Messages pressuring immediate action around account closures, unauthorized charges, or subscription expirations warrant scrutiny, though AI-generated phishing has reduced this signal's reliability with professionally toned lures that carry no urgency cues.
Requests for Credentials or Codes: Microsoft does not request passwords, credit card numbers, or MFA codes via email. An unsolicited request to enter a short code on a Microsoft sign-in page can indicate Microsoft credential phishing activity.
Unexpected Attachments: Microsoft rarely sends unsolicited attachments in security or account-related communications. PDFs containing QR codes and HTML attachments that open a login form are specific patterns to note.
Spoofed Sender Indicators: In Outlook, a "via" tag or question mark signals that email authentication could not verify the sender or that the identity differs from the From address. Only work or school accounts display this indicator.
When in doubt, users can open a new tab and go directly to account.microsoft.com rather than clicking any link within the email.
How to Respond to a Suspicious Microsoft Email
Fast reporting, session revocation, and persistence checks can reduce the impact of a Microsoft email scam that reaches an inbox. Users who receive potentially fraudulent Microsoft messages can take these reporting steps:
Outlook: Avoid interacting with links or attachments and use the Report button rather than forwarding or engaging with the email directly.
Other Email Clients: Send the message as an attachment, not a forwarded message, to phish@office365.microsoft.com.
Microsoft Teams: Report the message from the More actions menu.
Security Notice Verification: Microsoft sends legitimate account security notices from account-security-noreply@accountprotection.microsoft.com.
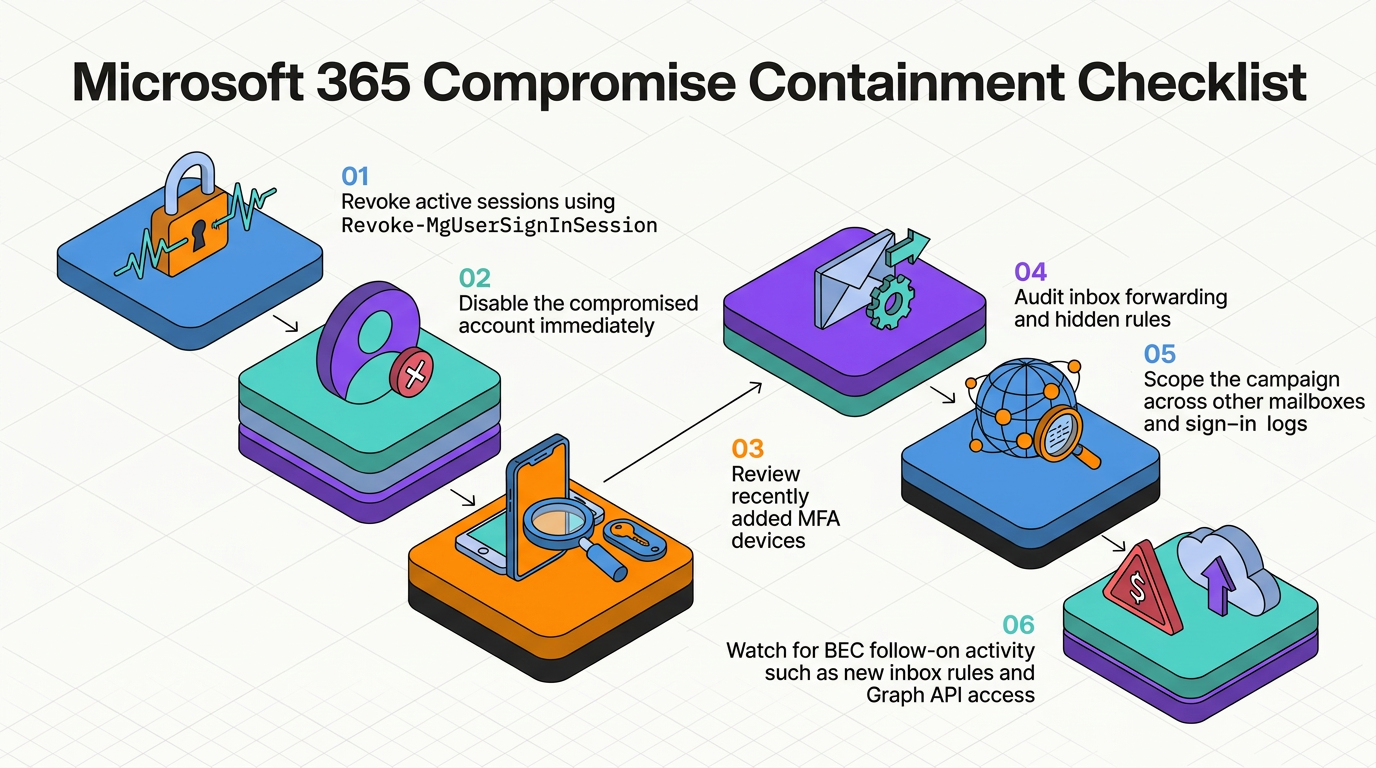
For confirmed or suspected credential exposure, session revocation matters more than a password reset because session cookies and refresh tokens captured in AiTM and device code attacks may remain valid until administrators explicitly revoke them. Initial triage can cover these steps:
Revoke Sessions: Microsoft's compromised-account guidance pairs the Revoke-MgUserSignInSession cmdlet with disabling the account for immediate containment.
Review Recently Added MFA Devices: Attackers commonly add their own devices to maintain persistent access after initial compromise.
Review Inbox Forwarding Rules: Forwarding rules, including hidden rules, are another common persistence mechanism.
Scope the Campaign: Search other mailboxes for the same sender, subject line, and URLs, and review sign-in logs for the affected accounts.
Watch for Follow-On Activity: An analysis of the ARToken device code platform lists new inbox rules and unusual Microsoft Graph access among the BEC follow-on indicators.
This reduces the chance an attacker keeps access after the password changes.
At the organizational level, response playbooks may include purging suspicious messages from affected mailboxes, blocking identified malicious sender domains, and auditing OAuth application consent in Entra ID. Restricting user consent to verified publishers and blocking device code flow through Conditional Access where unneeded can close two of the token-theft paths above.
Phishing-resistant MFA, such as FIDO2 security keys or passkeys, can further reduce exposure to the session-layer attacks password-based authentication leaves open. Collaborate with your help desk staff and IT administrators to start a team-wide rollout. Together, these controls support faster containment across email and identity layers.
Strengthen Your Microsoft 365 Security with Behavioral AI
Defending against Microsoft email scams requires layered controls that combine user awareness, strong authentication, and detection that does not rely on static rules. Traditional email security solutions still play a role, but they often struggle with the social engineering and session-layer attacks that define modern phishing.
Abnormal's Behavioral AI approach helps close that gap by modeling workflow cadences, sender-recipient patterns, and engagement flows on top of existing email infrastructure, surfacing deviations that may signal a potentially compromised account. This shifts detection from message content to communication context, covering gaps where delivery-layer tools have limited visibility.
Abnormal was named a Customers' Choice in the 2026 Gartner® Peer Insights™ Voice of the Customer for Email Security, the only vendor to earn the recognition three consecutive times. Abnormal is designed to detect sophisticated email threats that rule-based tools often miss.
Book a demo to see how Abnormal strengthens Microsoft 365 security.
Frequently Asked Questions
How Do Adversary-in-the-Middle (AiTM) Phishing Attacks Bypass Multi-Factor Authentication, and What Specific Steps Should Security Teams Take to Contain Them?
AiTM phishing inserts a reverse proxy between the victim and Microsoft's real authentication service, capturing the session cookie Microsoft issues after a completed login and MFA challenge. That cookie grants access without the password or MFA device. Containment starts with revoking active sessions via the Revoke-MgUserSignInSession cmdlet, then auditing recently added MFA devices, inbox rules, and Graph API activity for signs of continued access. FIDO2 security keys remove this vulnerability by binding authentication to hardware an AiTM proxy cannot intercept.
How Can Security Teams Detect and Respond to Phishing Attacks That Use Legitimate Microsoft Services Like SharePoint and OneDrive as Delivery Infrastructure?
Because the sending domain is genuinely sharepoint.com or onedrive.com, detection has to shift from domain reputation to behavior: unfamiliar external senders, authentication-gated links outside normal collaboration patterns, or document access from unexpected locations shortly after a link is sent. Conditional access policies requiring extra verification for external shares, alerts on unusual Graph API activity, and a review of sharing permissions on flagged files help close the gap, since these campaigns often chain into business email compromise.
How Does Behavioral AI-Based Email Security Differ From Traditional Secure Email Gateways in Detecting Modern Microsoft Email Scams That Lack Traditional Malicious Indicators?
Secure email gateways check each message against known-bad signatures, sender reputation, and URL blocklists, which gives them little to flag when a message arrives through genuine SharePoint infrastructure or a completed, valid login. Behavioral AI instead models how a user and organization normally communicate, so a message from an unfamiliar contact requesting unusual credential verification outside business hours can register as an anomaly even when every static check passes, extending coverage into the identity and session layers where gateway-style tools have limited visibility.