MITRE's Adversarial Tactics, Techniques, and Common Knowledge (ATT&CK Framework) is a knowledge base of adversary behaviors observed across the cyberattack lifecycle. MITRE first modeled ATT&CK during its Fort Meade Experiment, an internal research project that tested whether endpoint telemetry and analytics could improve post-compromise detection, and later published the framework. The framework has since become a standard reference for security teams defending against sophisticated threats that target enterprise IT, cloud services, mobile devices, and industrial control systems.
By categorizing attacker tactics, techniques, and procedures, ATT&CK gives security teams a shared vocabulary for threat detection, incident response, and defensive planning. Security teams that adopt this shared vocabulary move faster from raw threat intelligence to detection engineering, closing the gap between what adversaries actually do and what a given defense actually catches.
Key Takeaways
MITRE ATT&CK organizes observed adversary behavior across enterprise IT, cloud, mobile, and industrial control system (ICS) environments.
Technique entries connect behavior to mitigations, Detection Strategies, platform-specific Analytics, and examples from named threat groups and campaigns.
The ATT&CK Navigator helps chief information security officers (CISOs) visualize coverage and lets compliance officers map National Institute of Standards and Technology (NIST) SP 800-53 controls to specific techniques.
Why Is the MITRE ATT&CK Framework Essential for Cybersecurity?
The MITRE ATT&CK Framework gives security teams a documented account of how adversaries operate, which turns detection, response, and budget decisions into evidence-based work. Teams tracking evolving cybersecurity threats can use this catalog of observed behavior to defend against complex threats that chain several techniques together.
Here are the main advantages security teams can expect from the MITRE ATT&CK Framework:
Outlines Attack Patterns: ATT&CK lays out common attack patterns based on real incidents and named threat groups, so teams can prepare for the moves adversaries have already used against organizations like theirs.
Helps Plan a Budget: ATT&CK highlights which attack techniques are most relevant to an environment, so teams can prioritize the investments with the largest effect and avoid spreading resources across every possible threat.
Provides a Reality Check: Strategies grounded in documented attacker behaviors stay relevant as adversaries change tooling and targets.
Improves Communication: The framework supplies standardized terminology for threat discussions. Technique IDs give teams a consistent reference point, and the same IDs appear in government advisories and vendor reports, so external intelligence lines up with internal telemetry more easily.
These advantages support smarter decisions, more precise responses, and stronger coordination across cybersecurity teams.
What Are the MITRE ATT&CK Matrices?
The MITRE ATT&CK Framework provides distinct matrices that map attacker behaviors across enterprise, mobile, and industrial environments. Each matrix applies the same tactic-and-technique structure to a different set of platforms, so a cloud security engineer and an operational technology engineer can each work from a view scoped to the systems they defend.
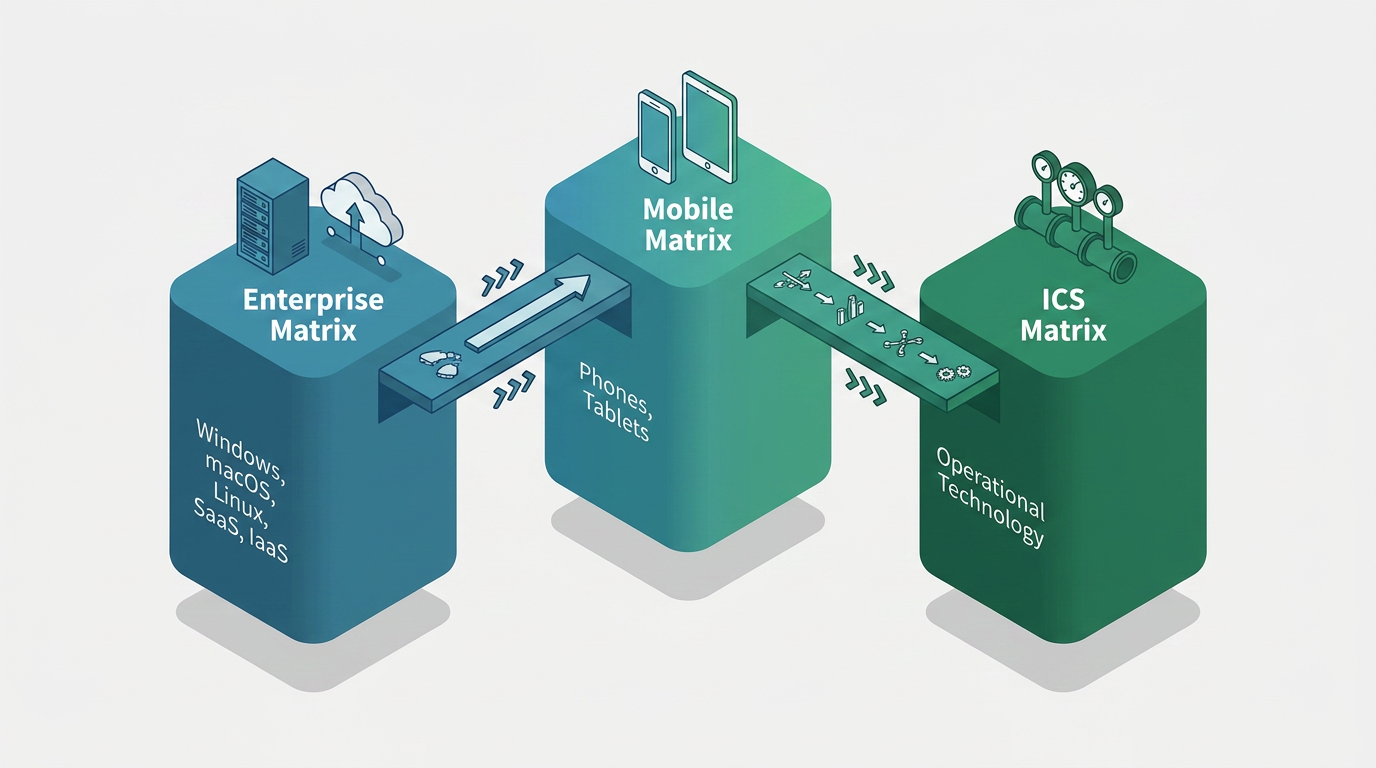
Enterprise Matrix
The Enterprise Matrix is the broadest, covering:
Windows, macOS, and Linux
PRE (pre-compromise reconnaissance and resource development activity)
Office Suite
Identity Provider
Software as a Service (SaaS)
Infrastructure as a Service (IaaS)
Network Devices
Containers
ESXi
Each platform has its own sub-matrix for targeted analysis, and MITRE updates the matrix with techniques drawn from real-world attack observations.
The Office Suite sub-matrix deserves attention from anyone responsible for email threats. MITRE scopes it to cloud-based office suites where email, chat, and document collaboration sit together. Techniques that play out in a mailbox, shared document, or chat channel live here, alongside the Identity Provider and SaaS sub-matrices that cover the login and token abuse that often follows a successful phish.
Security teams use the Enterprise Matrix to evaluate protection across operating systems and cloud services, develop detection strategies for each platform, and concentrate resources on the highest-risk techniques.
Mobile Matrix
For organizations with mobile priorities, the Mobile Matrix focuses on threats unique to mobile devices. It applies the same tactic-and-technique structure used elsewhere in ATT&CK, so a mobile security team works from tactic columns it already recognizes, populated with techniques scoped to phones and tablets. Mobile environments introduce distinct challenges, and attackers employ tactics that differ from traditional endpoints.
The Mobile Matrix guides teams in strengthening mobile device management, improving app security, and detecting mobile-specific threats.
Industrial Control Systems Matrix
The ICS Matrix covers operational technology used in critical infrastructure, and it includes tactics with no enterprise equivalent, such as Inhibit Response Function and Impair Process Control. According to the v19 release notes, ATT&CK v19 introduced sub-techniques to the ICS Matrix, which helps operational technology teams distinguish variations of adversary behavior while preserving the common ATT&CK vocabulary used across enterprise and mobile environments.
Primary Tactics and Techniques of MITRE ATT&CK
Tactics describe what an attacker wants to achieve at each stage of an intrusion, and techniques describe how the attacker achieves it. The MITRE ATT&CK Framework pairs the two so that security teams can anticipate threats, focus defensive effort, and improve detection and response across the full attack lifecycle.
Access and Foothold Tactics in MITRE ATT&CK
Tactics are the strategic objectives attackers aim to accomplish during an intrusion, the "why" behind each step, such as gaining initial access or evading detection. The Enterprise Matrix organizes the attacker's process into 15 tactics as of ATT&CK v19. The first group of tactics covers preparation, entry, execution, and maintaining a foothold:
Reconnaissance: Adversaries gather target information to identify weaknesses and plan the attack.
Resource Development: Adversaries acquire or set up tools, infrastructure, or accounts to support attacks.
Initial Access: Adversaries gain entry through methods like spearphishing, exploits, or valid credentials.
Execution: Adversaries run malicious code or commands on the target system.
Persistence: Adversaries maintain access after reboots or credential changes.
Privilege Escalation: Adversaries gain higher-level permissions to reach sensitive data or full system control.
Stealth: Adversaries hide or blend in with normal activity to evade detection.
Defense Impairment: Adversaries actively break defensive capabilities, such as logging or security tooling.
Expansion and Outcome Tactics in MITRE ATT&CK
The remaining tactics describe how adversaries deepen access, move through an environment, collect information, maintain control, and achieve their intended outcome:
Credential Access: Adversaries steal account credentials to support lateral movement and deeper access.
Discovery: Adversaries explore the network to learn about the environment, users, and defenses.
Lateral Movement: Adversaries move through the network to compromise additional systems or resources.
Collection: Adversaries gather data they want to steal, such as documents, credentials, or keystrokes.
Command and Control: Adversaries maintain communication channels between compromised systems and their infrastructure.
Exfiltration: Adversaries transfer stolen data out of the network to attacker-controlled locations.
Impact: Adversaries disrupt or destroy systems through actions like ransomware deployment, data destruction, and financial theft.
Together, these tactics provide a consistent way to describe an adversary's objectives across the intrusion lifecycle.
Techniques in MITRE ATT&CK
Techniques form the core of the MITRE ATT&CK Framework and represent the specific methods attackers use to achieve their objectives.
Each technique documents a real-world attack method observed across multiple threat campaigns. Under Initial Access, the Phishing technique breaks into sub-techniques for attachments, links, third-party services, and voice. Each technique entry includes affected platforms, mitigations, detection strategies, and procedure examples drawn from named threat groups and campaigns.
ATT&CK v19 added a technique that maps directly onto email fraud. T1684: Social Engineering covers trust-based manipulation of users, and its Impersonation sub-technique describes adversaries posing as a trusted person or organization in business email compromise (BEC) and email fraud campaigns to deceive victims into sending money or divulging information that ultimately enables Financial Theft.
Detection Strategies in MITRE ATT&CK
ATT&CK v18 replaced single-sentence detection notes with structured Detection Strategy and Analytic objects.
A Detection Strategy describes the adversary behavior to look for at a high level and points to platform-specific Analytics that spell out the detection logic, with each Analytic linked to the log sources and Data Components that supply the evidence. For Phishing (T1566), the parent-level detection strategy correlates inbound email carrying attachments or URLs with new process execution afterward, while separate analytics cover delivery through identity providers and SaaS chat platforms.
What Is the MITRE ATT&CK Navigator?
The ATT&CK Navigator is a web-based tool for building custom, annotated views of the ATT&CK matrices, and it supports Enterprise, Mobile, and ICS ATT&CK in a single instance. Security teams use it to turn the raw knowledge base into a picture of their own coverage, threats, and plans.
The Navigator's principal feature is the layer. MITRE's project documentation describes layers as "custom views of the ATT&CK knowledge base," such as showing only the techniques for a particular platform or highlighting techniques a specific adversary is known to use. Within a layer, users can color-code cells, add comments, and assign numerical scores to techniques. The tool is open source, and teams can use a hosted instance or run it inside their own network.
The Navigator also fits into threat hunting and incident response, where analysts map observed attacker actions onto the matrix, anticipate likely next steps, and compare layers to produce insights that guide roadmap decisions.
Applications of the MITRE ATT&CK Framework
Email remains one of the most common attack vectors, and the stakes are measurable. The Federal Bureau of Investigation's Internet Crime Complaint Center (FBI IC3) recorded $3.05 billion in BEC losses for 2025.
Here are some applications of the MITRE ATT&CK Framework:
Threat Intelligence Integration
The ATT&CK framework adds context to threat intelligence by tying adversarial behaviors to the techniques relevant to a given organization. Teams can focus response efforts on high-risk techniques and build environment-specific threat models from documented adversary tactics. When intelligence indicates spearphishing campaigns targeting an industry, security teams can prioritize relevant techniques, such as Spearphishing Attachment (T1566.001) or Spearphishing Link (T1566.002), and move from theoretical threats to specific technique implementations.
ATT&CK also separates phishing that delivers code from phishing that harvests data. T1598: Phishing for Information sits under Reconnaissance rather than Initial Access, and MITRE defines the difference plainly: "Phishing for information is different from Phishing in that the objective is gathering data from the victim rather than executing malicious code." Its sub-techniques mirror those of T1566 across service, attachment, link, and voice activity.
SOC Optimization and Email Security
For Security Operations Centers (SOCs), the framework supports alert triage through technique mapping and improves detection rules based on documented adversarial behaviors. Email security applications benefit from focusing on initial access techniques, especially phishing (T1566), with targeted detection for email-specific attack vectors.
After an attacker compromises an account, Internal Spearphishing (T1534), under Lateral Movement, describes attackers sending malicious content from a trusted internal account to reach more users. The technique can also travel through collaboration platforms. Preventive controls may struggle with this activity because it abuses legitimate system features, which places more emphasis on detection and hunting.
A SOC that tags alerts with these IDs can correlate a phishing alert, suspicious login, and internal forwarding rule from the same account into one incident. Pairing techniques sharpens the hypothesis further: sign-ins from unfamiliar locations or impossible-travel patterns on an account that also shows a new mailbox forwarding rule, mapped to Valid Accounts (T1078) and Email Collection (T1114.003), may describe a takeover in progress. This technique-based approach gives analysts a defined behavior to test, the telemetry needed to evaluate it, and a consistent way to record the result across triage, hunting, and incident response.
AI-Driven Security Integration
Modern AI security tools can complement the ATT&CK framework by using machine learning to spot behaviors that map to documented techniques. Abnormal's behavioral AI models how an organization communicates across cloud email and integrated collaboration tools. It is designed to help surface messages that break established workflow cadences, vendor interaction patterns, recipient behavior, timing, and engagement flows, even when those messages carry no known-bad indicator. Examples include wiring instructions sent outside business hours or a sudden change to a vendor's banking details.
Abnormal focuses on the email, identity, and account-based components it can observe. Techniques that play out in traditional IT environments, industrial control systems, payment platforms, or voice channels require their own controls and detection engineering.
How to Implement the MITRE ATT&CK Framework
Successful implementation of the MITRE ATT&CK Framework follows a step-by-step approach that starts with an organization's environment and ends in a repeatable reassessment cycle. Here are the steps teams can take:
1. Inventory Your Environment and Controls
Teams can begin by documenting the critical assets, systems, and telemetry that need protection, then mapping the security tools already covering them. An inventory of the organization's critical assets and systems establishes where an attacker could find value and where controls may be thin, and it can extend to network architecture, cloud services, identities, email systems, and operational dependencies. Cataloging current security tools alongside those assets, including which logs each tool produces and how analysts access them, gives the team a single view of where evidence exists and where it does not.
Mapping those controls to relevant ATT&CK techniques turns the inventory into a coverage picture that distinguishes prevention, detection, investigation, and response, since a tool's association with a technique does not prove that it covers every procedure. The v18 detection model ties each Analytic to a specific log source, so recording data retention, ownership, and collection gaps helps teams tell a deployed control apart from a control that actually produces usable evidence. The Cybersecurity and Infrastructure Security Agency's (CISA) Best Practices, produced with the MITRE ATT&CK team, give analysts step-by-step instructions for consistent mapping.
2. Assess Threats and Prioritize Gaps
Teams can then identify the threats most relevant to their industry, size, geographic location, and technology environment, and rank the resulting coverage gaps by risk. Industry-specific threat reports and previous security incidents reveal recurring entry points, targeted assets, and adversary behaviors that deserve priority, while external threat intelligence adds context about campaigns, threat groups, and techniques observed against similar organizations. Connecting each relevant threat to documented ATT&CK techniques, rather than maintaining a general list of concerns, gives security, compliance, and business stakeholders a shared threat profile they can revisit as systems and adversary behavior change.
That profile then feeds gap prioritization. Useful ranking criteria include potential impact, likelihood of exploitation, exposure of affected assets, available telemetry, and the feasibility of remediation in terms of time, resources, and complexity, which separates urgent blind spots from lower-priority gaps the organization can accept or monitor. Teams can combine those inputs with business impact and control maturity to create a defensible remediation queue.
3. Start Small and Focused
Teams can begin with a manageable subset of techniques instead of attempting to cover the entire ATT&CK framework at once. Priority should go to techniques that address the highest risks unique to the organization. A practical starting point is a single tactic category, such as Initial Access, which covers how attackers first gain entry into systems. This focused approach lets teams build expertise, validate their mapping process, and show early wins before expanding scope.
MITRE's Getting Started resources advise against chasing full coverage: "Don't try to achieve 100% coverage."
4. Develop an Implementation Roadmap
Teams can translate priorities into a practical, step-by-step plan with realistic timelines, assigned owners, required resources, and defined validation criteria. MITRE publishes major releases plus smaller updates in between, so aligning roadmap reviews with the release cadence helps prevent new techniques from sitting unmapped for an extended period. The Mappings Explorer from the MITRE Center for Threat-Informed Defense publishes control mappings, including NIST SP 800-53, as downloadable Navigator layers that teams can use as a starting point instead of building every mapping from scratch.
Version tracking also belongs in the roadmap. The Center for Threat-Informed Defense's mapping guidance warns that control mappings fall behind as techniques advance, so scheduling that work makes framework maintenance predictable and proactive.
5. Apply ATT&CK to Email Security
Email remains a primary entry point for cyberattacks, so integrating ATT&CK into an email security strategy can produce practical early value. Teams can map email-specific techniques, such as Phishing (T1566), to current controls and extend the mapping to techniques that follow a successful lure: Internal Spearphishing (T1534) for lateral movement, Email Collection (T1114) for data theft, and Impersonation (T1684.001) for fraud.
MITRE places BEC under Financial Theft (T1657) in the Impact tactic, and its detection strategy calls for spotting fraudulent invoices, vendor impersonation, and BEC-style payment redirections through email and document analytics. Teams can use that chain to identify gaps in detection, prevention, investigation, and response.
Operationalizing the MITRE ATT&CK Framework
The MITRE ATT&CK Framework replaces assumptions about adversaries with documented behavior that security teams can translate into controls, detections, tests, and measurable improvement. Continuous monitoring, reassessment, and adaptation help keep pace with changing adversary TTPs and give the CISO a coverage trend line to bring to the board.
Abnormal's behavioral AI analysis complements the framework's focus on unusual behaviors associated with specific email techniques, and it integrates with existing email security infrastructure, security information and event management (SIEM) tools, and response workflows to add a detection layer without replacing them.
See how Abnormal's behavioral AI is designed to help identify email attacks mapped to specific ATT&CK techniques, particularly those in the Initial Access tactic. Book a demo with our team.
Frequently Asked Questions
Is MITRE ATT&CK Free to Use?
MITRE ATT&CK is freely available online and doesn't require a license or subscription. MITRE, a nonprofit that operates federally funded research centers, maintains the knowledge base as a public resource for the security community, and community contributions help keep technique entries current across releases like v18 and v19.
How Is MITRE ATT&CK Different From the Cyber Kill Chain?
The Cyber Kill Chain describes an intrusion as a fixed, linear sequence of high-level phases. ATT&CK instead catalogs hundreds of specific techniques within each tactic and doesn't assume an attack moves through stages in strict order. That granularity is what lets a team map a specific detection or mitigation to a specific adversary behavior, rather than to a general stage of attack.
Does MITRE ATT&CK Replace a SIEM or EDR Platform?
No. ATT&CK is a knowledge base and a shared vocabulary, not a detection tool, so it doesn't collect logs, generate alerts, or block anything on its own. Teams use it to structure the analytics inside a SIEM, EDR platform, or email security tool, mapping the alerts those systems already generate to specific tactics and techniques.
How Often Does MITRE Update the ATT&CK Framework?
MITRE has typically shipped major ATT&CK releases about twice a year, with smaller updates in between as new techniques and threat intelligence emerge. The move from v18's Detection Strategy overhaul to v19's Defense Evasion split, released in April 2026, reflects that cadence. Teams that maintain Navigator layers or control mappings should plan to revisit them each release.