Security awareness training teaches employees how to resist attacks aimed at them by recognizing and reporting suspicious activity. One rushed click or approved login prompt can let an attacker bypass a firewall, putting employees at the center of defense.
The stakes are steep. Attackers increasingly go after people instead of firewalls, because a single rushed decision can hand over more access than months of scanning for a software flaw. Instruction has to produce reliable decisions under pressure, not just a certificate of completion.
Key Takeaways
Training reduces risk only when it changes what employees do, so behavior metrics deserve more weight than completion certificates.
Programs should combine realistic simulations, role-specific content, immediate feedback, and frequent reinforcement throughout the year.
Several U.S. regulations require workforce training in specific industries, and recent updates make social engineering mandatory content.
Human awareness works alongside technical controls, while a blame-free reporting culture turns employees into an early warning system.
What Is Security Awareness Training?
Security awareness training develops the knowledge and practiced skills employees need to handle information safely under pressure. Awareness gets people to notice a risk, while training gives them the skill to act on it. A full learning program gives everyone basic awareness and matches training to the tasks each person performs. Specialist security and privacy roles receive deeper education.
A structured security awareness program combines these levels in recurring form so everyone can spot social engineering attempts aimed at them. Programs aim to produce behavior change that holds up over time, such as a finance clerk who pauses before approving a changed bank account. In practice, the program must carry that pause from a quiz into a convincing real request.
Why Do You Need Security Awareness Training?
Security awareness training matters because attackers reach people more reliably than they defeat technology, and regulators increasingly require organizations to address that risk.
The 2026 Data Breach Investigations Report found the human element present in 62% of breaches, whether through clicking a phishing lure, a reused password, or a successful pretext. Social engineering attacks, including business email compromise (BEC) and pretexting, bypass technical controls. A message that appears to come from a chief executive officer (CEO) or trusted vendor can push an employee to wire funds without tripping an alert, and tailored impersonation attempts now also arrive by text message and voice call.
Regulation turns that operational risk into a formal responsibility. Rules covering healthcare providers under the Health Insurance Portability and Accountability Act (HIPAA), payment card merchants under the Payment Card Industry Data Security Standard (PCI DSS), some financial firms under the Federal Trade Commission (FTC) Safeguards Rule, and some federal contractors require workforce training. The New York financial services regulation mandates at least annual training that includes social engineering content, effective November 1, 2023. PCI DSS made phishing and social engineering content mandatory under Requirement 12.6.3.1 as of March 31, 2025, while federal law requires annual training for anyone with access to federal systems.
How Does Security Awareness Training Work?
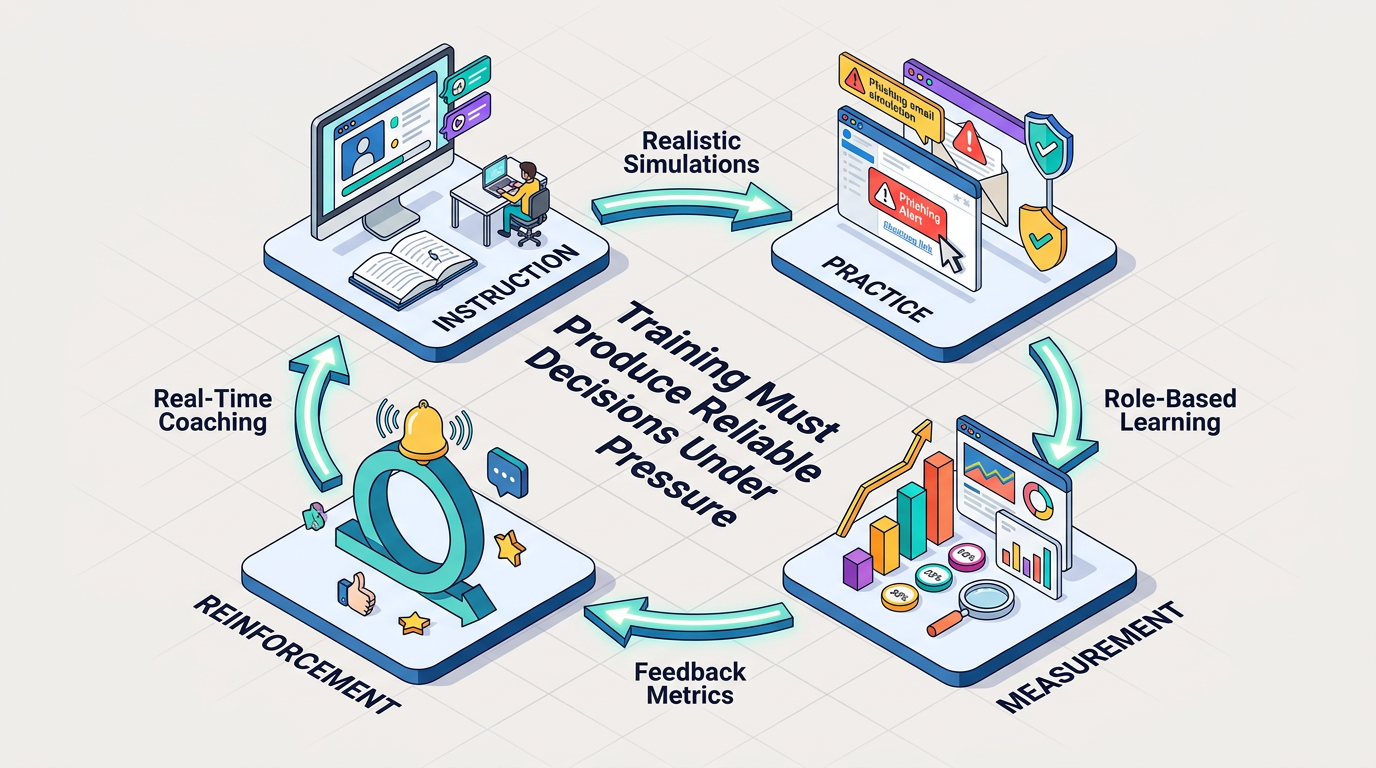
Security awareness training works through a recurring cycle of instruction, practice, measurement, and reinforcement. Formats include self-paced modules and tabletop exercises that walk a team through a simulated ransomware incident. Repetition matters because employees need to apply recognition and reporting skills during unexpected, time-sensitive decisions.
That repetition takes three connected forms: realistic simulations, role-based practice, and real-time coaching.
Realistic phishing simulations send harmless test emails to see how employees react, and anyone who clicks receives immediate feedback explaining what they missed. Scenarios deliver the most value when they reflect threats the organization actually faces, since generic lures teach people to catch only generic lures. Mature programs also tier lure difficulty because a program that runs only easy tests produces a flattering click rate and overstates resilience.
Role-based learning then adapts that practice to different responsibilities. Finance and payments teams need scenarios built around vendor invoice fraud tactics and bank detail changes, while information technology (IT) administrators need a heavier focus on credentials and help desk security. Executives need examples of the personalized impersonation attempts they attract. Coaching can target the people and roles flagged by the data.
Real-time coaching completes the cycle by delivering guidance when an employee meets a potential threat rather than weeks later in a module. An inline prompt can identify warning signs in a suspicious message, while a short explanation can appear the instant someone clicks a simulated lure. This approach connects instruction to the decision that triggered it, so the lesson is specific and immediately useful.
Key Components of an Effective Security Awareness Training Program
No single component carries a security awareness program on its own. Risk data without goals produces activity without direction; goals without feedback and leadership support rarely change behavior; and even the best content fails if employees fear reporting their mistakes. The seven components below reinforce one another, so a gap in any one weakens the rest.
A mature program brings all seven together:
Risk Assessment: Incident and simulation data show where employees are exposed. Help desk tickets can reveal additional pressure points, including executive impersonation tactics and scanned quick response (QR) codes; a retailer's priorities differ from a hospital's.
Defined Goals and Metrics: Programs benefit from defining success before launch and capturing a baseline for the selected metric. Success may concern reporting behavior or a regulatory deadline, while reporting metrics can include a rising report rate and a shorter time to report.
Blended Delivery: Small businesses can run online modules plus simulations, while enterprises can add role-based content and executive briefings on top of the baseline.
Recurring Cadence: New hires complete initial training early, an annual module sets the baseline, and short reinforcement pieces spread through the year keep pace with changing threats.
Immediate Feedback: Simulations paired with instant, specific coaching support retention because the seconds after a failure provide a valuable teaching moment.
Leadership Participation: Executives who complete the same modules and discuss the results signal that security is a shared responsibility.
Blame-Free Reporting: A blame-free culture promotes quick action. Employees who fear punishment for a click may hide it, and a manageable mistake can then become an incident.
When these components work together, security awareness training stops being a compliance checkbox and starts producing measurable behavior change. The result is a workforce that recognizes threats faster, reports them sooner, and gives the security team a fighting chance to contain incidents before they escalate.
Security Awareness Training Program Maturity Stages
Security awareness training programs rarely leap from nothing to a mature capability. They move through recognizable stages, and each stage sets the foundation for the next: a compliance-focused program builds the reporting channels that behavior change relies on, and behavior change is the raw material culture is built from. Skipping stages tends to produce activity without lasting effect, which is why honest self-assessment matters more than aspiration.
Most programs move through five stages:
Non-Existent: No formal program exists, and employees are never told they are targets, so the first sign of trouble is usually an incident that already happened. Nobody owns the problem, and an employee who suspects something has nowhere to report it.
Compliance-Focused: Training runs annually or ad hoc to satisfy an audit, and completion rate is the metric that matters.
Awareness and Behavior Change: The program identifies top human risks, adds role-based content, and reinforces learning continually. Programs that focus on a few high-impact behaviors, such as reporting suspected social engineering attempts, typically show measurable behavior change within the first year.
Long-Term Culture Change: Security becomes embedded organization-wide, and behavior holds when no campaign is running. Human resources, communications, and operations share ownership with the security team, and the shift takes years.
Optimization and Resilience: The program connects to business outcomes, and metrics move from training activity to human time to detect and time to recover from incidents. Leadership reviews human risk next to other operational risks instead of treating it as a training report.
Knowing the current stage is the practical value of this model. A program at stage two that sets stage-five metrics will miss them and lose credibility, while a program that has quietly reached stage three can make the case for the investment needed to sustain culture change. The goal is not to reach stage five quickly but to advance one stage at a time without losing the habits built at the last one.
What Topics Should Security Awareness Training Cover?
Security awareness training should cover a shared foundation for every employee and a rotating set of scenarios based on attacks currently in circulation.
Foundational Security Topics: The core curriculum covers phishing and unknown attachments, passwords and multi-factor authentication (MFA), social engineering tactics and malware, data handling and acceptable use, and physical security. It also explains removable media and common insider threat indicators. Incident reporting deserves particular emphasis because employees need to know exactly whom to contact and which details to provide.
Emerging Attack Topics: Deepfake audio and video now appear in executive impersonation, and a cloned voice clip can make a fraudulent payment request sound legitimate. Criminals also use artificial intelligence (AI) tools to make those requests more convincing. The Federal Bureau of Investigation's (FBI) Internet Crime Complaint Center (IC3) recorded more than $3 billion in BEC losses in its 2025 Annual Report, the second-largest loss category of the year.
QR code phishing attacks and text messages move lures onto personal phones outside managed email. The same off-channel logic drives help desk impersonation attempts aimed at password or MFA resets and MFA fatigue attacks that flood users with push prompts. Employees should verify requests through a channel they looked up themselves.
How to Measure the Effectiveness of Security Awareness Training
Training effectiveness appears first in simulation and reporting behavior, then in the effect human decisions have on real incidents.
Leading indicators come from realistic phishing simulations and reporting tools:
Report Rate: The share of recipients who flag a simulated phishing or social engineering message, capturing proactive behavior.
Time to Report: How quickly a flagged message reaches the team; a report within minutes gives the team a chance to pull it from other inboxes.
Click Rate: Belongs on the dashboard with caveats, since a rate near zero usually means simulations are too easy.
Repeat-Click Rate and Credential Entry Rate: Repeat-click rate identifies who needs coaching, while credential entry rate shows how far a simulated compromise went.
Lagging indicators measure whether behavior change reached the business. Programs track confirmed incidents that began with a human action, such as a payment sent after an executive impersonation attempt, along with the time required to contain them. These numbers move slowly, but leadership can connect them more directly to operational risk than training completion.
The largest randomized controlled trial of anti-phishing training to date, run by UC San Diego and the University of Chicago over eight months, found that embedded phishing training barely moved click rates. Recently completing annual training also had no measurable association with whether an employee failed a simulation. The same study found that most employees barely engaged with the training in the first place: three-quarters spent a minute or less on it, and a third closed it immediately without reading any of the material. Because recognition skills also tend to fade within months without reinforcement, programs should provide frequent short exposures throughout the year.
Security Awareness Training and Regulatory Compliance
Security awareness training is an explicit requirement under several sector-specific US rules, although the mandated frequency and content vary widely. These include the HIPAA Security Rule, PCI DSS, the FTC Safeguards Rule, and the New York Department of Financial Services (NYDFS) cybersecurity regulation. The National Institute of Standards and Technology's (NIST) current guidance on cybersecurity and privacy learning programs, published in September 2024, and its Cybersecurity Framework 2.0 place general and specialized awareness training within the Protect function. NIST SP 800-50 Revision 1 was published on September 11, 2024, confirming this date.
Regulation or Standard | Who It Covers | Training Requirement | Stated Frequency |
|---|---|---|---|
HIPAA Security Rule | All workforce members of covered entities, including contractors and volunteers | Security awareness and training program for all workforce members | Periodic; annual training is a common implementation |
PCI DSS | All personnel | Formal program with phishing and social engineering content required since March 31, 2025 | Upon hire and at least every 12 months |
FTC Safeguards Rule | All personnel, with ongoing specialized training for information security staff | Awareness training program | As necessary |
NYDFS Cybersecurity Regulation | Entities regulated by NYDFS | Awareness training that includes social engineering | At least annually |
Federal Information Security Modernization Act (FISMA) | Federal agency personnel and contractors with system access | Security awareness training | Annually, by statute |
Cybersecurity Maturity Model Certification (CMMC) Level 2 | Defense contractors handling controlled unclassified information | Role-based risk awareness, role-based training, and insider threat awareness | Not fixed in the model text |
Sarbanes-Oxley and the Securities and Exchange Commission's (SEC) 2023 cybersecurity rules set a general expectation of reasonable safeguards but contain no explicit training mandate. Compliance can establish a baseline for a security awareness program, but it does not show by itself whether employees can resist phishing and social engineering.
Common Mistakes in Security Awareness Training Programs
Most failed security awareness programs share a common root: they optimize for what is easy to measure rather than what actually reduces risk. Audit-focused program design often neglects employee behavior and business resilience, and the mistakes below tend to appear together — a program that treats annual training as sufficient usually also chases click rate and punishes the people who fail it. Recognizing the pattern is the first step to breaking it.
The seven mistakes below appear most often:
Treating Annual Training as Sufficient: A yearly module meets several regulations but sits at only the second of five maturity stages.
Chasing Click Rate Alone: Easy simulations say little about resilience against harder lures, and click rate can mislead program owners when viewed alone.
Punishing People Who Click: Employees who fear punishment for a click may stop reporting, which removes an important early warning.
Ignoring Repeat-Clicker Data: Treating everyone identically spends coaching time on people who already behave well.
Assuming Training Stops Everything: Some attacks need no user action, and well-built targeted attacks fool careful people. Training remains one defensive layer.
Overloading Employees: Long, generic, repetitive content produces fatigue and gives employees little reason to retain the material.
Skipping High-Risk Roles: Executives, finance staff, help desk agents, and contractors need scenarios beyond the general curriculum.
Avoiding these mistakes does not require a larger budget so much as a shift in what the program is trying to accomplish. A program that measures behavior instead of completion, coaches instead of punishes, and treats training as one layer among many will outperform a bigger program built around the audit calendar.
Security Awareness Training vs. Security Culture
Security awareness training is an activity the organization runs, while security culture is the set of shared habits that persists when no training is running. A program can post excellent completion rates inside a culture where an executive's urgent payment request is never questioned. Without supportive habits, a finance approver may process a changed bank account without a callback because nobody in that office has ever been thanked for slowing a payment down. Culture appears in unprompted behavior: employees file suspicious phishing reports without a simulation, and managers thank colleagues whose reports turn out to be false alarms. It also appears when teams challenge finance-focused impersonation attacks without waiting for permission.
From Annual Module to Everyday Habit
Frequent short exposures, feedback after failure, role-matched content, and a blame-free reporting path address weaknesses in annual-only training. Identify the program's current maturity stage and select one high-impact behavior to improve over the next six months.
Frequently Asked Questions
How Often Should Employees Receive Security Awareness Training?
Employees generally need an annual baseline plus shorter reinforcement throughout the year. New hires also benefit from early training so reporting and verification habits form before they encounter a real request.
Does Security Awareness Training Actually Work?
It can work when employees complete relevant, interactive training and receive repeated opportunities to practice. Completion alone does not establish that behavior changed.
Is Security Awareness Training Required by Law?
Requirements depend on the organization and industry. HIPAA, the FTC Safeguards Rule, NYDFS regulation, FISMA, PCI DSS, and CMMC include training obligations for covered workforces.
Why Isn't Annual Security Awareness Training Enough?
Recognition skills fade between sessions. Attack methods also change, leaving long gaps in which employees receive no practice. Short reinforcement keeps important decisions familiar.
What Happens If I Fail a Phishing Simulation?
A well-run program uses an initial failure as a teaching opportunity and provides immediate contextual instruction. A well-run program may respond to repeated failures with additional coaching.