Key Insights
For decades, the phishing playbook was straightforward: send a suspicious email, hope someone clicks. But attackers have learned that the inbox alone no longer closes the deal. They've added a voice on the other end of the line.
Welcome to TOAD phishing, short for Telephone-Oriented Attack Delivery. By stitching together email, SMS, and a live phone call, attackers transform a static message into an unfolding conversation that feels personal, urgent, and disarmingly legitimate.
It's a meaningful turn in the threat landscape. As phishing has matured into more sophisticated and harder-to-detect campaigns, TOAD attacks sit at the front of that curve, built specifically to exploit human vulnerabilities that traditional email filters and security gateways were never designed to address.
What Makes TOAD Phishing Different?
TOAD phishing is an advanced social engineering attack that uses telephone interactions as its primary attack vector, typically combined with communication channels like email and SMS.
TOAD phishing attacks feature several distinguishing characteristics:
- Multi-Channel Coordination: Attackers use email, phone, and SMS to craft a cohesive and convincing narrative.
- Human Interaction Exploitation: Attackers use voice conversations to manipulate victims through social dynamics and psychological triggers.
- AI-Driven Impersonation: Attackers use deepfake voice technology to impersonate executives and execute sophisticated AI-powered phishing schemes.
- QR Code Manipulation: Attackers use Quishing (QR phishing) to redirect victims to credential harvesting websites.
- Hybrid Attack Sequencing: Attackers execute step-by-step tactics across multiple platforms to reinforce deception.
- Caller ID Spoofing: Attackers display legitimate-looking phone numbers, often mimicking actual company lines.
The scale of this threat is significant. In a recent analysis of email-based threat detections across enterprise environments, TOAD accounted for nearly 28% of all gateway-bypassing detections, according to Dark Reading.
How Do TOAD Phishing Attacks Occur?
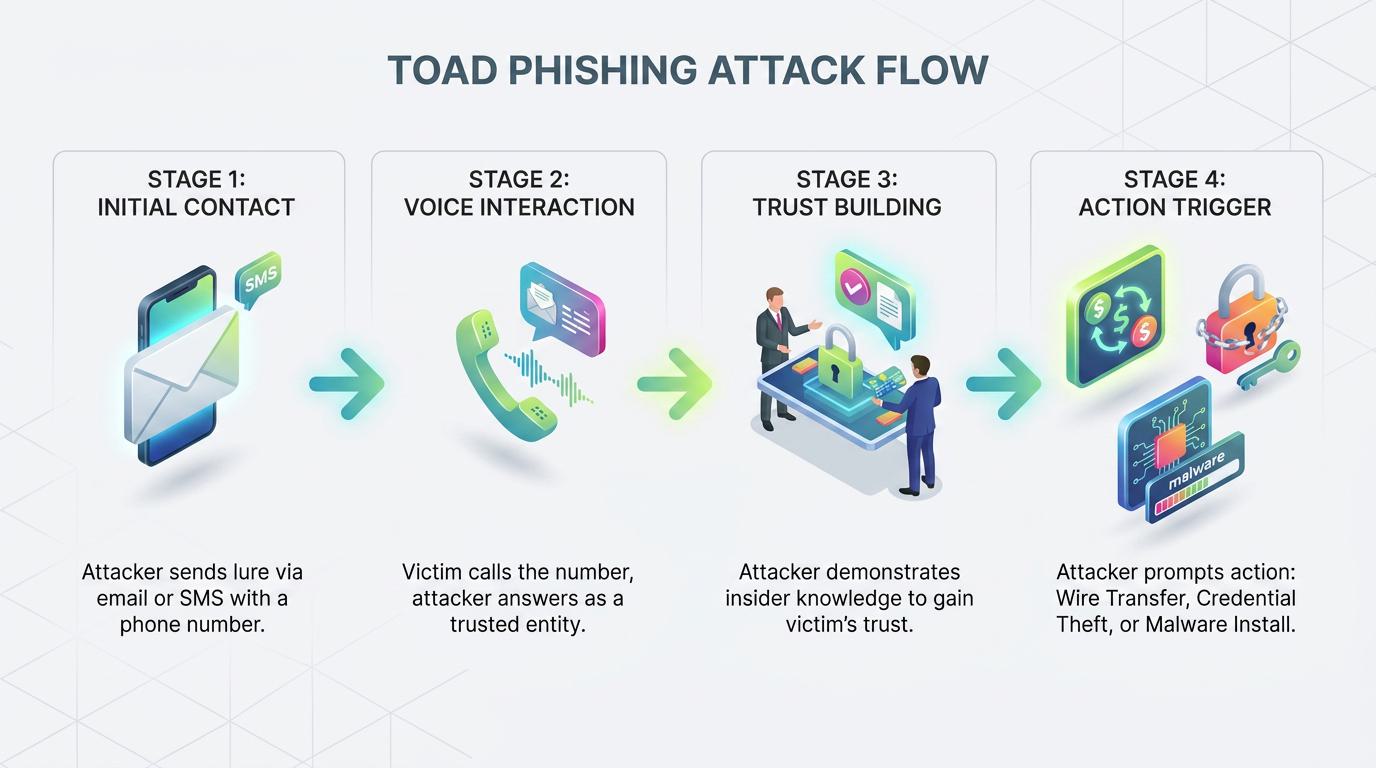
TOAD phishing follows a predictable pattern that moves from written contact to voice-based persuasion.
- Initial Contact: A compelling email or SMS message includes an urgent request or alarming notification.
- Voice Interaction: A phone call references the initial message, adding credibility.
- Trust-Building: Attackers demonstrate knowledge about the victim or company to build trust.
- Action Trigger: Attackers request sensitive information, financial transactions, or the installation of malware.
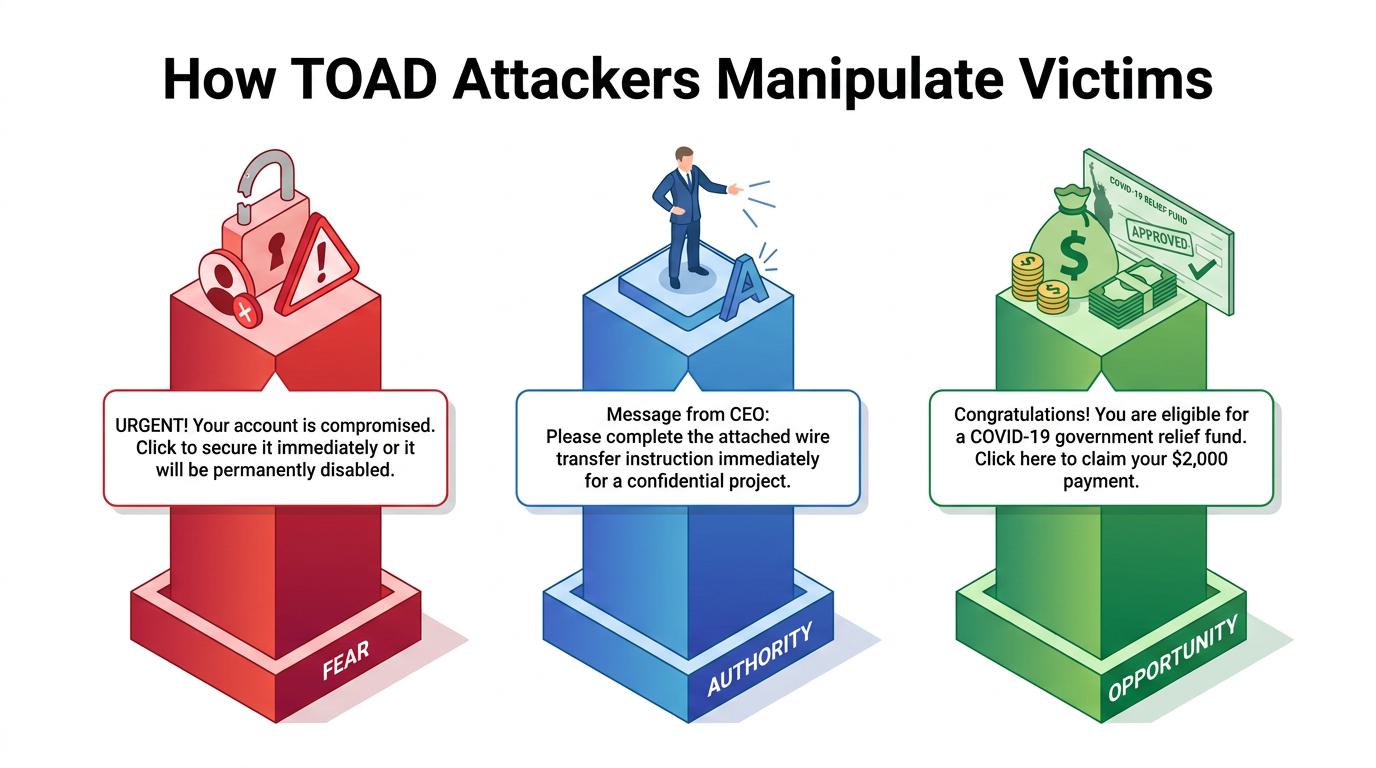
Attackers often spoof caller IDs to create a false sense of legitimacy, and they lean heavily on emotional triggers to push victims toward action. Fear is a common lever, with attackers using scare tactics like telling victims that their accounts have been compromised.
Authority plays an equally powerful role, as attackers impersonate authoritative figures and issue executive orders that employees feel pressured to follow. In other cases, attackers manufacture a sense of opportunity, exploiting financial struggles by offering fake financial relief programs to lure victims in.
Some high-profile attacks have started using AI-generated deepfakes for voice and video impersonation of company executives, leading to significant financial losses.
For example, a finance employee at UK engineering firm Arup's Hong Kong office was scammed after a video call with deepfake versions of the company's CFO and staff, exposing the growing threat of AI-driven scams. The employee was the only real participant on a video conference where the other attendees appeared to be deepfake recreations of real colleagues, as the newspaper reported.
While these campaigns increasingly blend email with voice calls, text messages, and even deepfake video, the primary control point remains the inbox. Behavioral AI helps detect the email and account-based components of these scams, while organizations should pair this with additional controls for voice, SMS, and videoconferencing channels.
Why Detecting TOAD Phishing Is Crucial
Detecting TOAD phishing attacks is crucial because these attacks often bypass security measures and leave victims unaware of their compromised status until damage is done.
What's at Stake When TOAD Attacks Go Undetected
When a TOAD attack slips past defenses, the damage compounds quickly across financial, operational, and brand dimensions. That's why early detection matters so much, each hour an attack goes unnoticed translates into deeper losses. Organizations typically face three primary types of damage:
- Financial Losses: TOAD phishing attacks frequently lead to direct monetary theft through wire transfers, business email compromise (BEC), or ransomware deployment. The FBI IC3 2025 Annual Report indicates BEC schemes resulted in losses of $3.04 billion in a single year.
- Data Breaches: These attacks excel at credential harvesting, with compromised accounts appearing legitimate because the actual account owner provided their information. A successful TOAD phishing attack provides attackers with persistent access to systems while evading detection.
- Reputational Damage: When attackers impersonate an organization's brand or executives, the resulting loss of customer trust persists long after the attack. IBM research identifies lost business, revenue, and customers among the damaging effects of successful cyberattacks.
Why Undetected TOAD Attacks Create Serious Compliance Exposure
Detection isn't just about stopping fraud in the moment, it's also about limiting the regulatory fallout that follows. The longer a TOAD attack goes unnoticed, the greater the compliance exposure becomes, because these attacks can involve stolen credentials, impersonated executives, voice recordings, and AI-generated deepfakes.
Compliance teams need clear policies for how employees verify sensitive requests, document incidents, and escalate suspected compromise. The legal exposure can extend well beyond the original phishing message when attackers use telecom channels or synthetic media to pressure employees into action.
Two compliance concerns stand out in particular. The first involves telecommunications violations, since using voice recordings in phishing schemes could run afoul of telecom regulations. The second relates to the rise of AI-generated deepfakes, which introduce new legal challenges; under the European Commission's AI Act, for example, deployers of AI systems that generate deepfake content must disclose that the content has been artificially generated.
What Are the Detection and Prevention Strategies for TOAD Phishing?
Effective TOAD phishing defense requires a layered strategy that combines technical controls, employee awareness, and out-of-band verification.
Detection Methods for TOAD Phishing
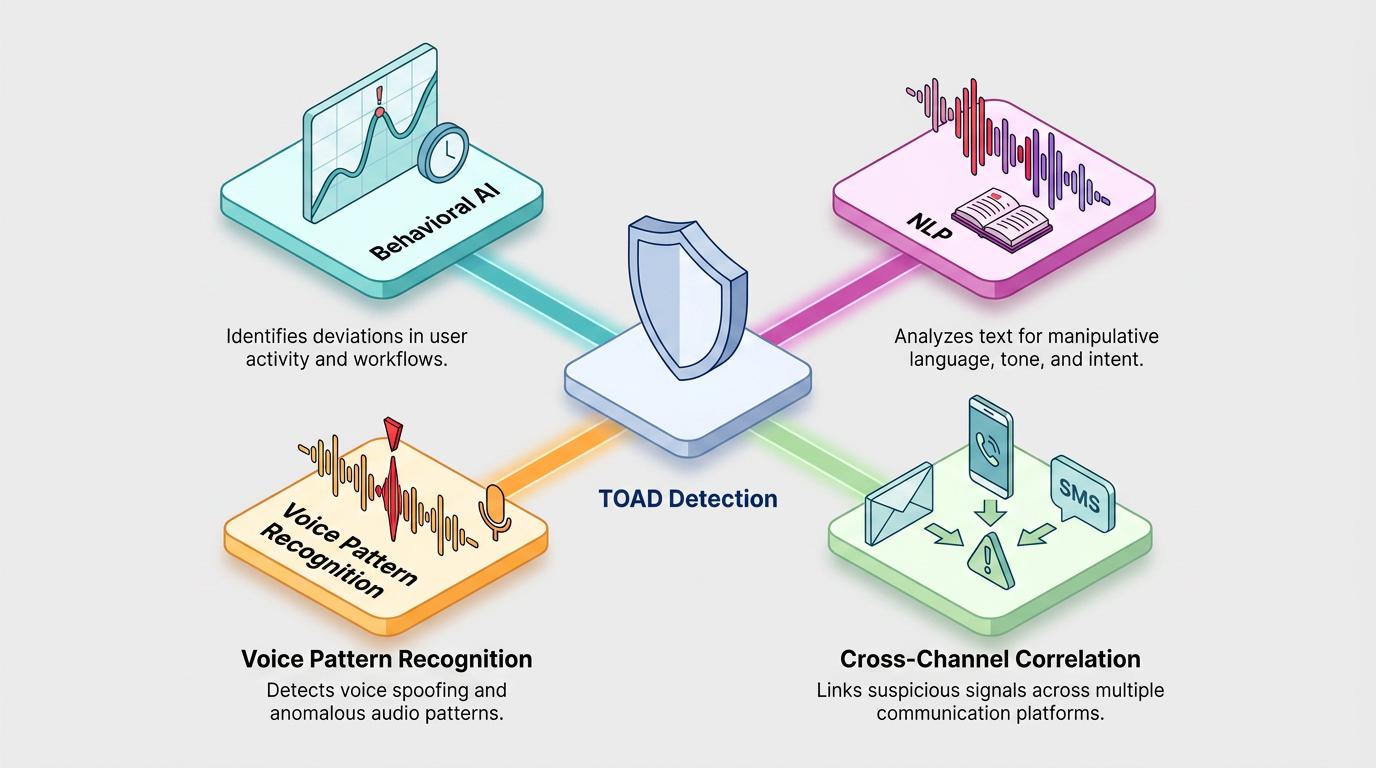
Leading organizations use several techniques to detect TOAD phishing:
- Behavioral AI: Abnormal applies behavioral AI to email-borne threats and account-based signals. Its cybersecurity tools use behavioral AI to track concrete patterns like workflow cadences, vendor interaction patterns, recipient behavior, timing, and engagement flows, helping surface deviations such as wiring instructions sent outside business hours.
- Natural Language Processing (NLP): NLP systems analyze linguistic patterns in communications to flag inconsistencies.
- Voice Pattern Recognition: Voice-focused controls can identify synthetic voices or voice patterns that don't match known legitimate callers.
- Cross-Channel Correlation: Effective detection integrates data across email, phone, and messaging platforms to identify coordinated attacks.
The need for these methods is reinforced by independent research cited by the World Economic Forum, which found that untrained human deepfake detection accuracy was not significantly above chance. That finding supports automated detection that does not rely primarily on human recognition.
Mitigation Techniques Against TOAD Phishing
Organizations can implement several strategies to reduce TOAD phishing attack success rates. Employee training programs are a strong foundation, as regular simulations of TOAD phishing attacks and employee training help staff recognize warning signs; continuous simulations with immediate feedback tend to produce stronger results than annual compliance-driven training.
On the technical side, implementing strong multi-factor authentication, DMARC email authentication, and call filtering technologies creates multiple barriers against TOAD phishing attacks.
Process improvements add another layer of protection, since establishing verification procedures for high-value requests, such as wire transfers, that operate outside the initial communication channel can help neutralize TOAD phishing tactics.
Finally, cultural development matters just as much as tools and processes, creating an environment where employees feel empowered to question suspicious requests, even from apparent authority figures, reduces successful social engineering attacks.
Integrating Security Tools for a Comprehensive Defense Against TOAD Phishing
TOAD phishing defense works better when email security, SIEM, endpoint, and threat intelligence workflows share context across the systems security teams already operate.
Automation Benefits for TOAD Phishing Detection
Automated security tools that apply AI in cybersecurity provide several critical advantages against TOAD phishing attacks. AI can help surface attack patterns earlier in the attack sequence, enabling faster analysis, and automation can help reduce breach costs compared to manual processes, according to IBM analysis.
Automated response protocols can isolate compromised accounts or block suspicious communications without waiting on human intervention, while continuous monitoring across relevant channels allows automated systems to detect attack patterns that human analysts might miss.
On top of all this, automated security playbooks for common TOAD phishing scenarios support uniform and timely action across the organization. When defenders can respond consistently and quickly, the window attackers have to escalate access or move funds shrinks considerably.
Tools That Can Help Prevent TOAD Phishing
Stronger TOAD phishing prevention can come from integrating multiple security tools into a cohesive ecosystem. This collaborative approach gives security teams more context than any isolated control:
- Email Security Platforms: Threat detection systems can help identify phishing attempts before users engage with them.
- Security Information and Event Management (SIEM) Systems: SIEM systems use platform integrations to correlate events across channels, identifying suspicious patterns early.
- Endpoint Detection Tools: Monitor unusual device behavior, flagging potential compromise after suspicious interactions.
- Shared Threat Intelligence: Continuously updates defense systems with emerging TOAD phishing tactics, keeping organizations ahead of evolving threats.
Abnormal integrates seamlessly with existing systems like Microsoft 365 and Google Workspace, enhancing the effectiveness of your current security stack against the email and account-based components of these multi-channel attacks. By applying behavioral AI to model how your organization communicates, the platform helps surface the unusual sequences that signal a TOAD attack in progress.
Staying Ahead of Evolving TOAD Phishing Threats
More attackers are using AI-generated content and deepfakes, making TOAD attacks more difficult to detect. Security teams can reduce exposure by connecting inbox detection, account-based signals, verification workflows, and employee reporting into one repeatable operating model.
Organizations that integrate cross-channel security systems stand a stronger chance of combating these sophisticated hybrid threats. With the right tools and training, security teams can reduce the impact of these attacks and maintain a strong defense against evolving phishing tactics.
Abnormal is recognized as a Leader in the Gartner® Magic Quadrant™ for Email Security Platforms. Ready to see how Abnormal protects your inbox from sophisticated multi-channel attacks? Book a demo today.