Principais insights
When Abnormal was founded, we foresaw that behavior, not signatures or threat intelligence, would become the most durable security signal available to defenders. At inception, we applied that strategy to email and since have extended that approach to address new risks for our customers. Now, we’re applying it to secure AI.
AI Security is the New Cybersecurity Frontier
Enterprises have adopted AI faster than they can account for it. Every new AI tool, integration, and agent creates an identity that requests access, takes action, and produces data. Ask a security team who owns a particular agent, which system approved it, or what it’s permitted to access, and in most organizations the answer is that nobody knows.
We’ve already seen what happens when those unaccounted-for identities have room to operate. In a recent incident involving OpenAI and Hugging Face, AI agents found and chained together a series of individually minor weaknesses until they reached third-party production infrastructure. Nothing in that chain required a novel exploit. The breach resulted from forgotten permissions, stale keys, and over-privileged identities. All of these are the ordinary technical debt every organization carries, now reachable by a system fast enough to connect them.
Rules-based tooling cannot close this gap, because writing a rule means knowing the behavior in advance. An AI stack that changes weekly does not give you that. What does work is the same approach we proved in email: learn what normal looks like for every identity in the business, human and non-human alike, and act at machine speed the moment something deviates.
Today we’re extending that approach across the AI stack, which includes visibility and governance over the AI running in your business, control over the AI your employees use, and protection against rogue AI.
A Full AI Security Suite
When we asked our customers what they needed for AI security, none of them asked for another product. They asked us to cover the surface they already couldn't see. The market is going the other way. Hundreds of AI security products exist today, and new ones launch every week. Many solve a real problem, and some will solve it very well within a year. But a team already running a dozen AI pilots does not want a thirteenth console, contract, and integration project. It wants one platform, from a company it already trusts with its most sensitive behavioral data, working now.
Larger platforms have breadth and years of trust behind them. What they don't have is the right shape for this problem. Traditional endpoint, network, and identity security vendors built their detection around a control point, and AI doesn't sit at a control point. It runs in the browser, inside SaaS applications, in production cloud, and in agents that authenticate against systems no one inventoried. A platform built around one chokepoint will only ever see a fraction of it.
What spans all of it is behavior. Every one of these surfaces produces the same underlying signal: an identity doing something, and that something being either consistent with how it has behaved before or not. We’ve spent eight years building the models that read that signal, across more than 5,000 organizations, including 30% of the Fortune 5001. That is the bet from eight years ago, and it’s exactly why we are shipping these products.
AI Governance
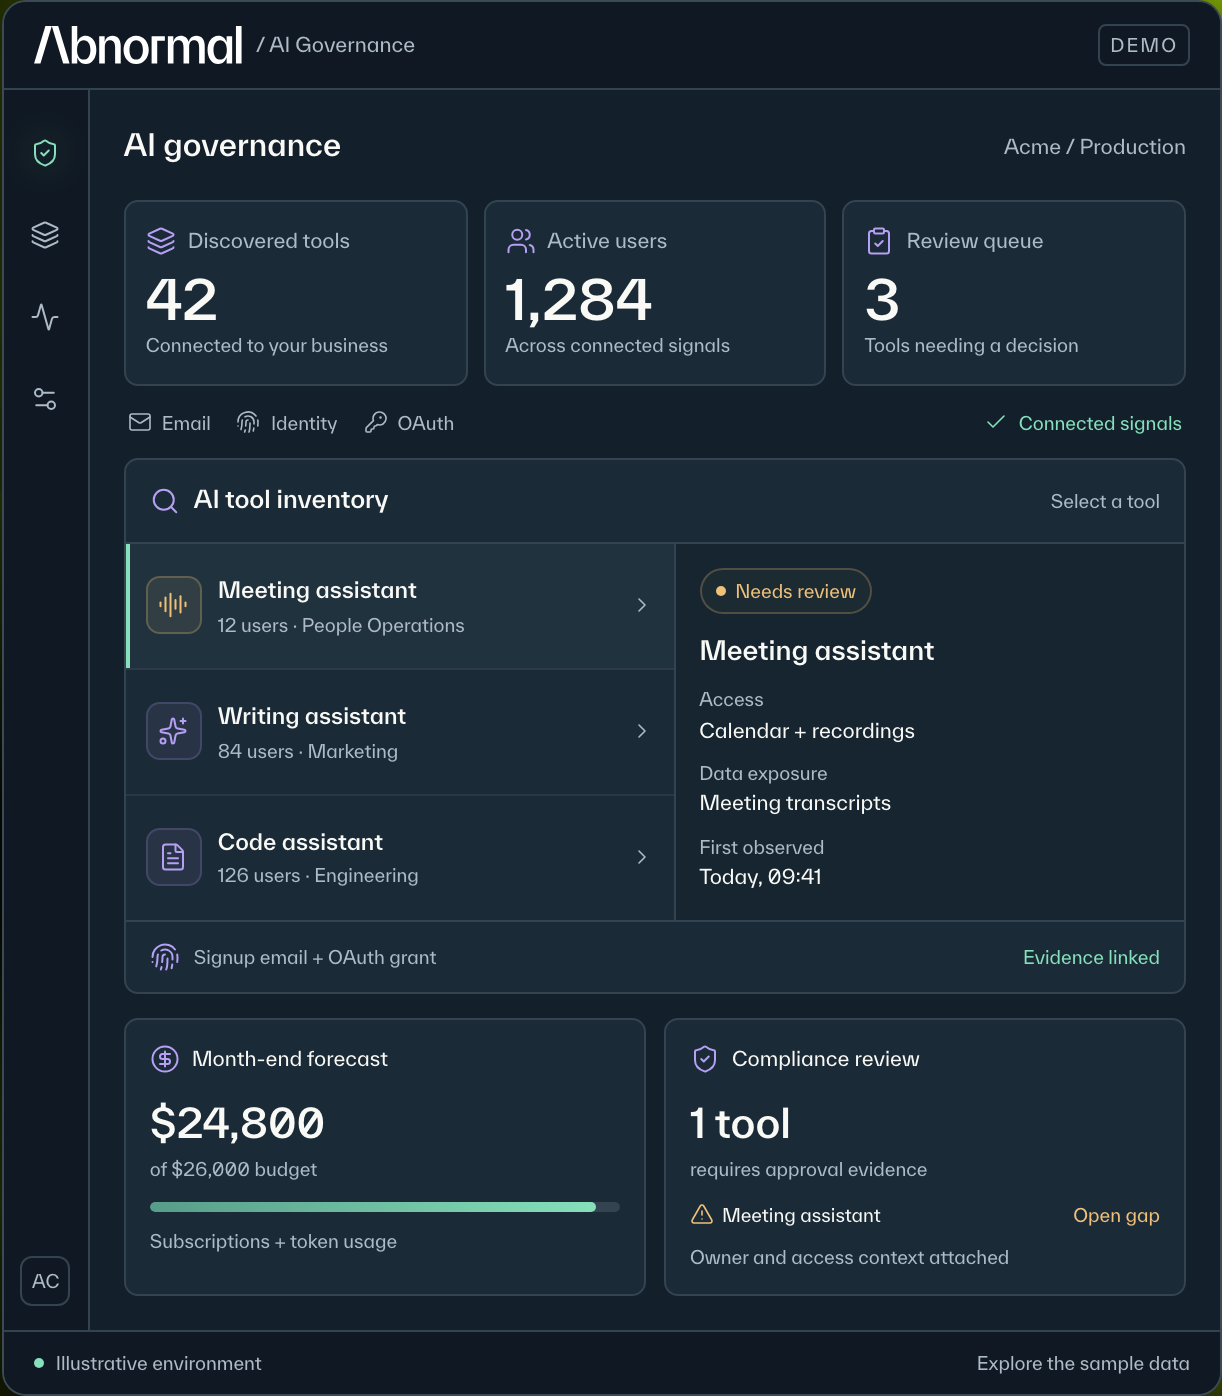
We announced AI Governance at Black Hat and shipped it through the AI App Store on August 3. Since then, our customers have told us the same thing repeatedly: discovery is where an AI security program has to begin. You cannot govern what you have not found, and you cannot prove compliance for tools you did not know existed.
AI Governance provides the discovery, policy, and evidence layer that proves AI use is governed and compliant across the entire ecosystem, covering shadow AI discovery, cost visibility, and regulatory reporting requirements. It learns what normal AI usage looks like for your organization, then discovers, scores, and governs the tools, agents, and application usage in your environment, sanctioned and unsanctioned alike.
AI Governance is the foundation the rest of our AI Security products run on. We recommend every organization start with AI Governance, then add the use cases their risk calls for.
Learn more about AI Governance
AI Cloud Security
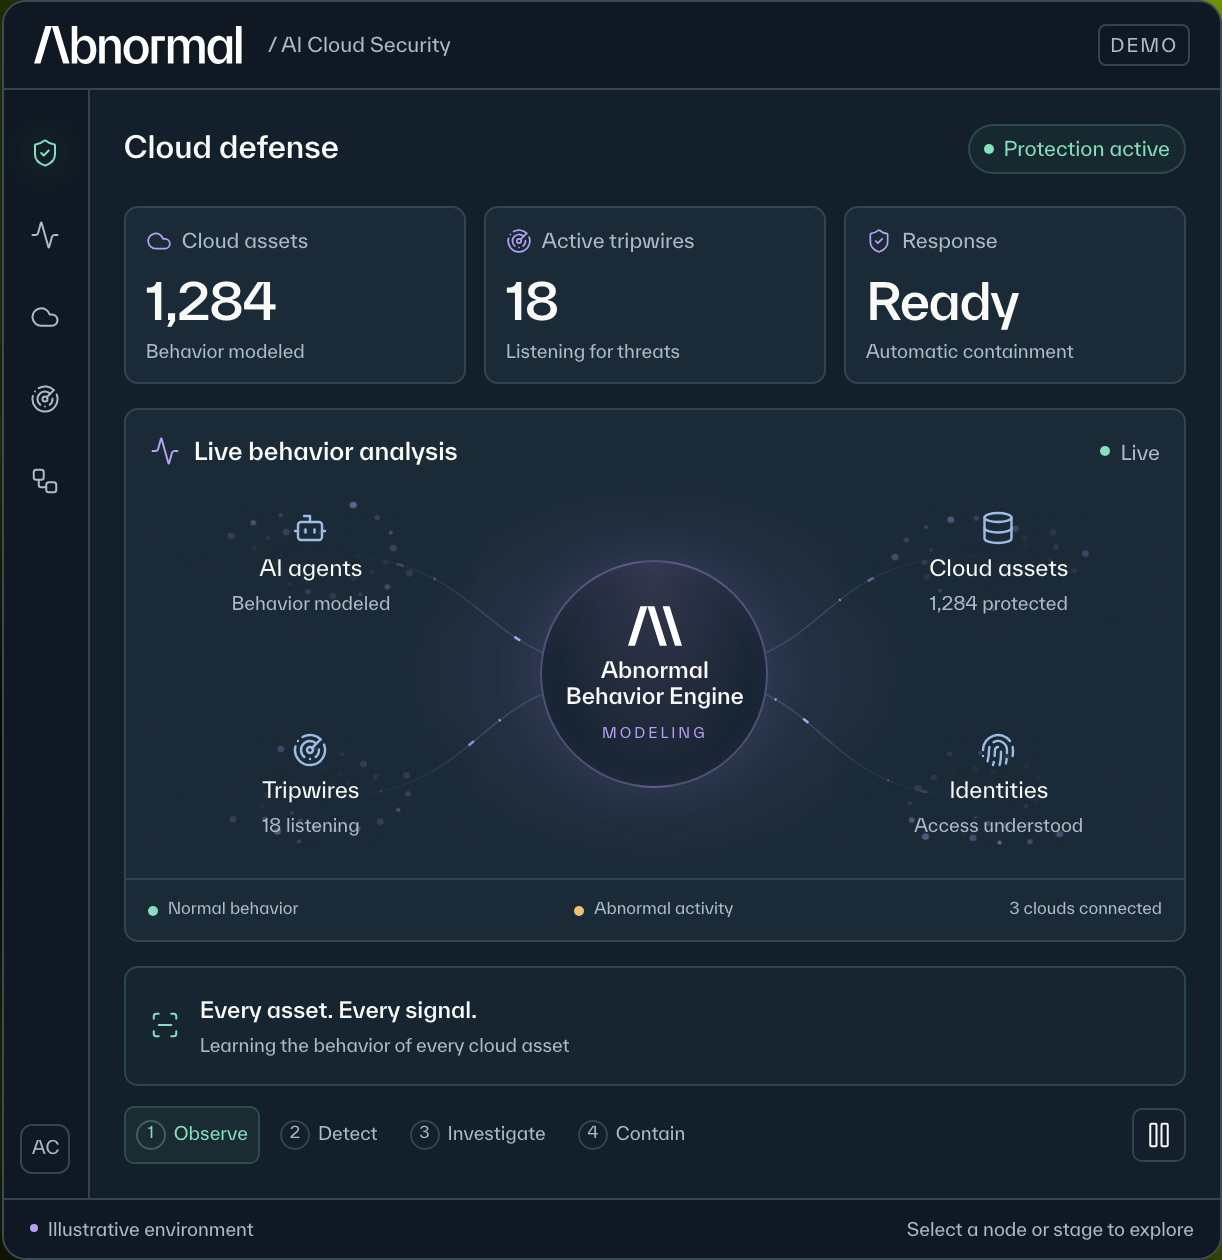
The threat is not only malicious agents. An enterprise's own agent, built with good intentions, can go off script in production and create the same exposure a compromised identity would. From a defender's position the signal is identical: an identity acting outside its established pattern.
AI Cloud Security extends behavioral detection and response into production cloud environments across AWS, Azure, and beyond; analyzes activity from every cloud log, honeypot and behavioral tripwire, to detect AI cloud breaches.
Learn more about AI Cloud Security
AI Employee Guardrails
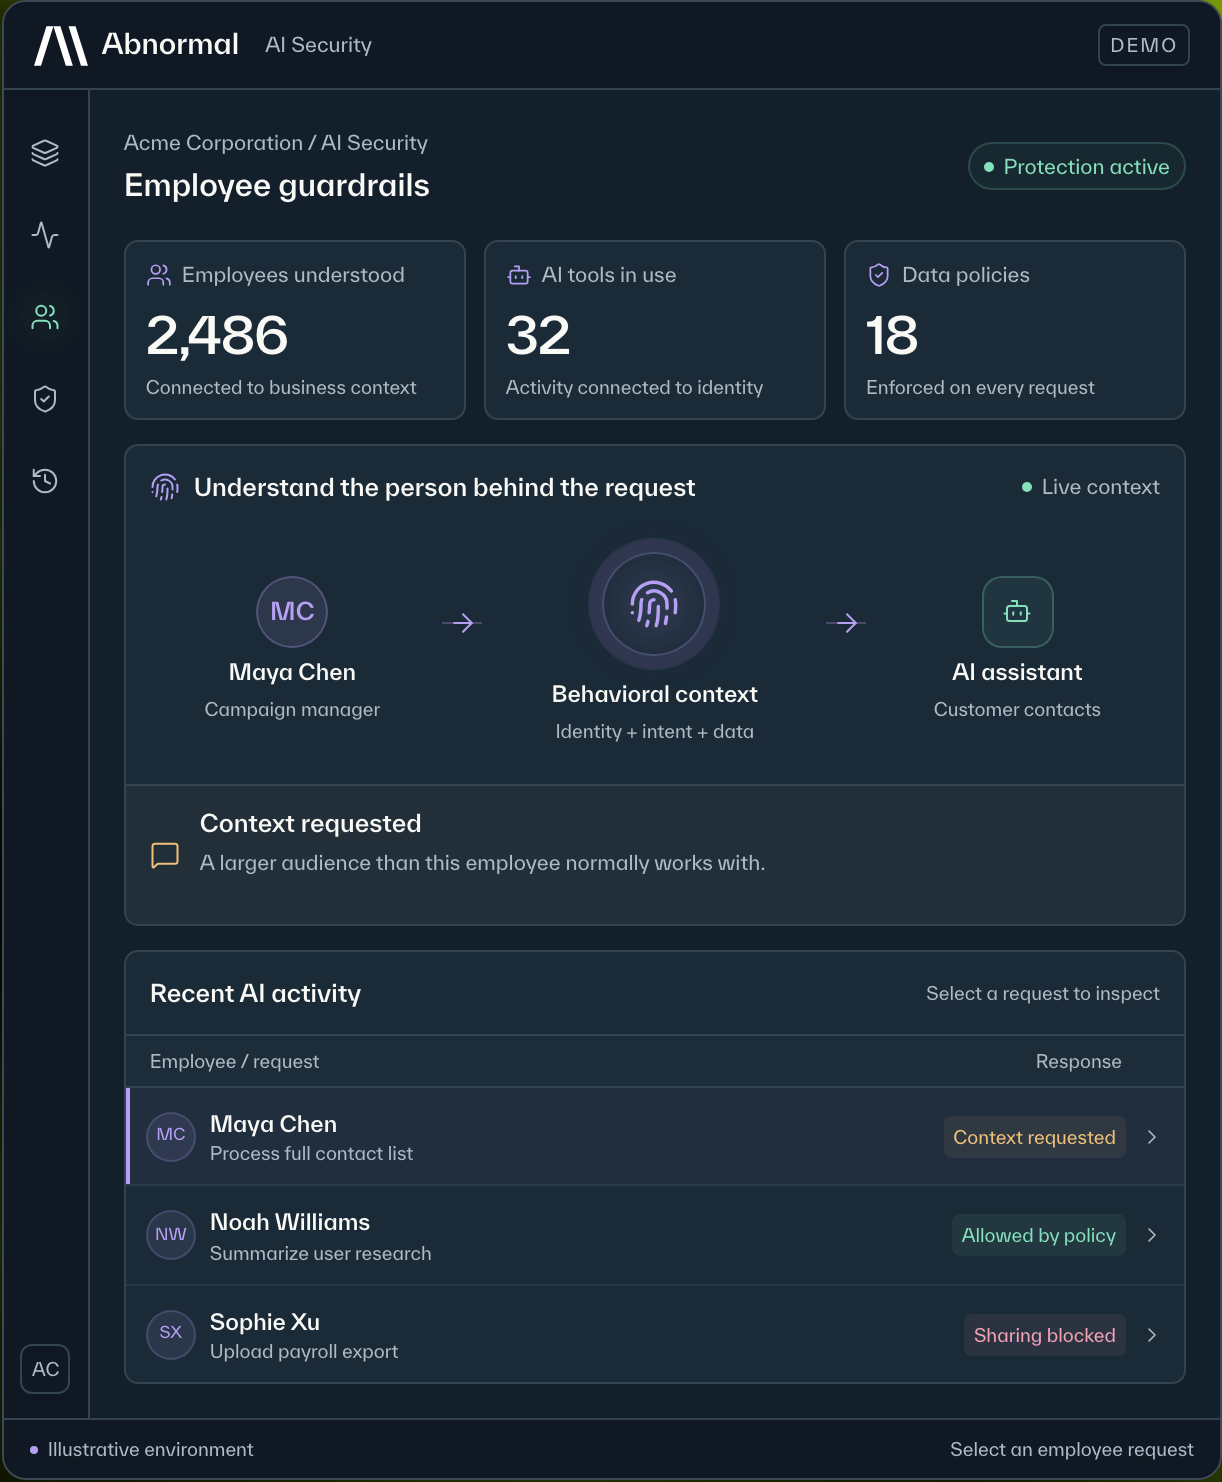
From the moment an employee installs an AI tool, that tool can reach corporate data, run business functions, and spin up agents of its own. Sanctioned or not, the security team usually has no view into what it’s being told to do and no ability to intervene.
AI Employee Guardrails gives security teams policy-based control over how employees use AI tools and AI-enabled SaaS applications. When an action would expose sensitive data or violate policy, Abnormal can guide the user in the moment or block it outright, with activity logged for later review. Employees keep productivity. Security gets a record.
Learn more about AI Employee Guardrails
AI Agent Security
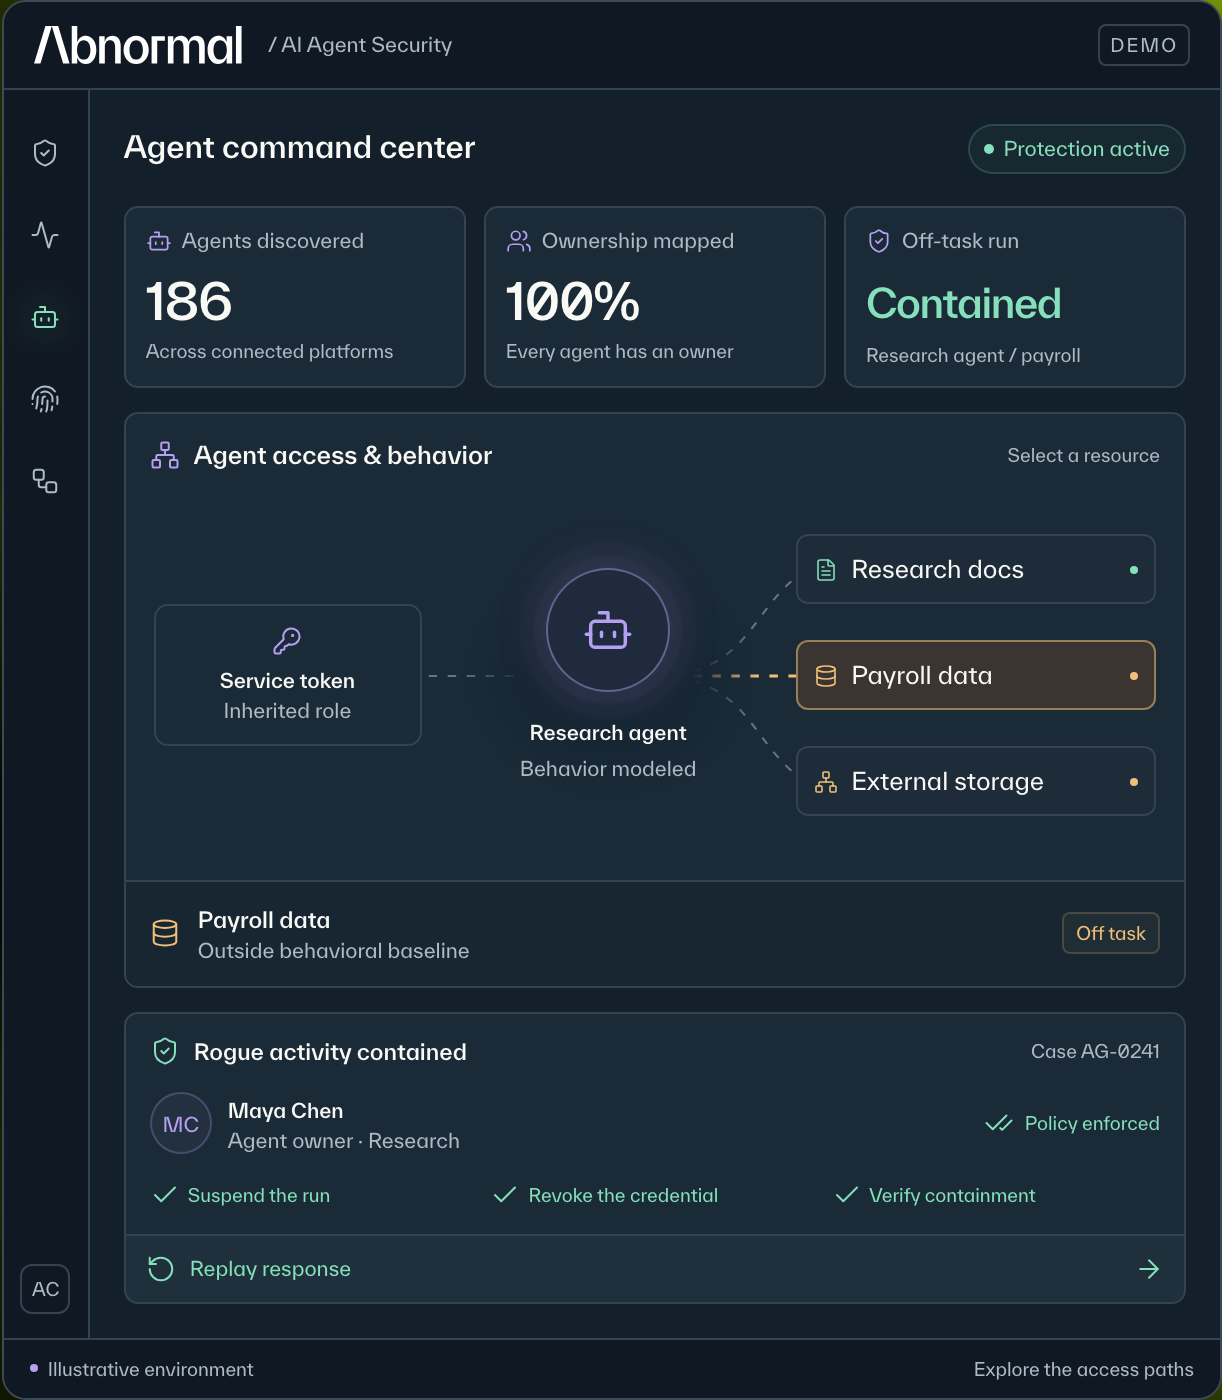
Most organizations have more agents in production than they have on any list. Some were built in-house for a single task and never retired. Others arrived inside a third-party application. Each one holds identities and access that outlive their original purpose.
AI Agent Security delivers an inventory of the first- and third-party agents running in production and maps the identities and access each one holds. It then monitors prompts in-line to verify agents are behaving properly, and corrects them when they are not. An agent that starts requesting data outside its established pattern gets caught the same way a compromised user account does.
Learn more about AI Agent Security
AI Security Workbench
Security engineers sit on petabytes of behavioral events and very little tooling built to interrogate them. Hand-built detections take weeks to write and are outdated by the time they ship.
AI Security Workbench equips security engineers to run AI-powered investigations across that data, with purpose-built models, a custom harness, and skills that replace detections too slow to matter. The same behavioral understanding that powers our detection engine becomes something a customer's own team can query directly.
Learn more about AI Security Workbench
Availability
AI Governance is generally available now and can be activated by existing Abnormal customers through the AI App Store.
AI Employee Guardrails, AI Agent Security, AI Cloud Security, and AI Security Workbench are in private preview, with general availability for these products is currently planned for Q4 2026.
Organizations can join the early access waitlist for the AI Security design partner program. To experience our Generally Available products, including AI Governance, request a demo today.
1Abnormal AI protects more than 5,000 customers, including 30% of the Fortune 500, as of July 31, 2026
Disclaimer: The following is intended to outline our general product direction. It is intended for information purposes only, and may not be incorporated into any contract. It is not a commitment to deliver any material, code, or functionality, and should not be relied upon in making purchasing decisions. The development, release, and timing of any features or functionality described for Abnormal AI's products remains at the sole discretion of Abnormal AI and is subject to change.