Key Insights
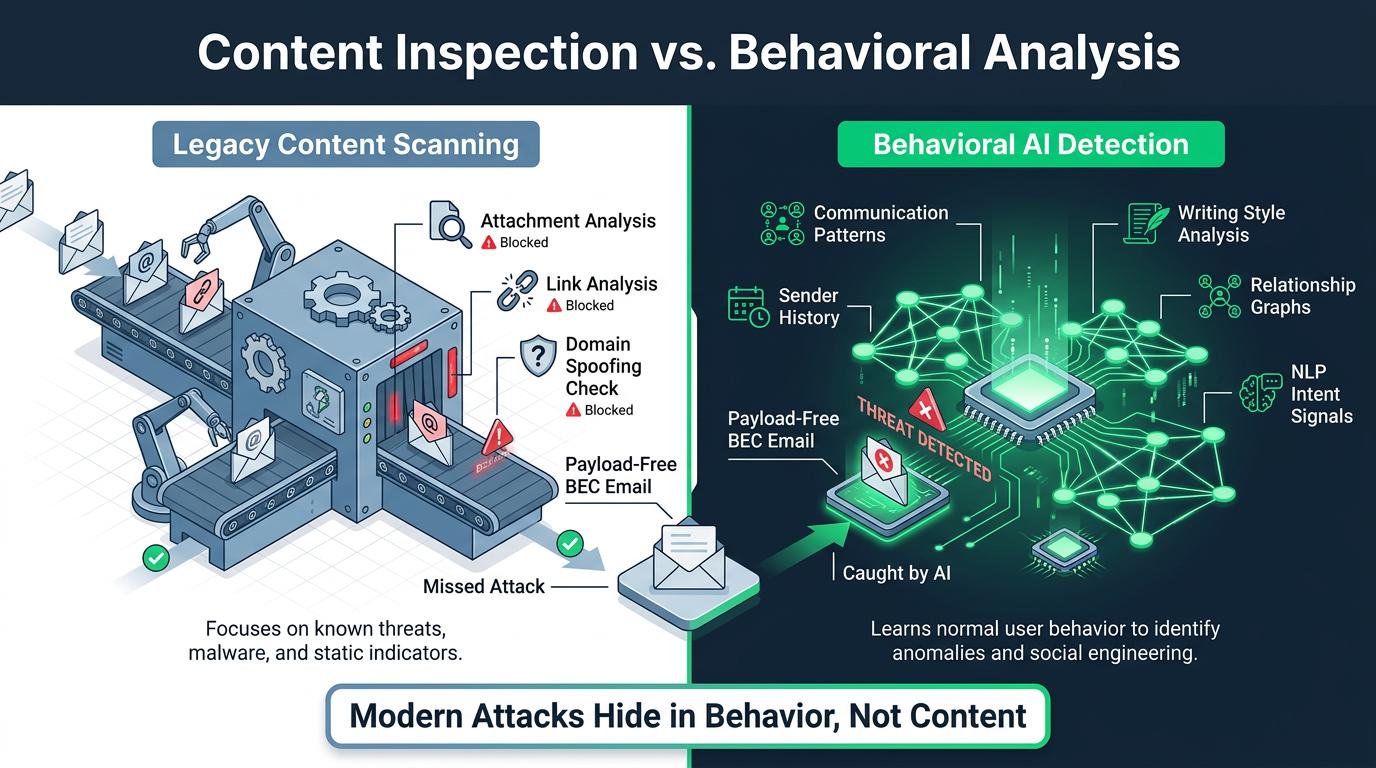
Most inbound email threat protection still works the way it did a decade ago: it reads the content of a message and looks for something bad inside it, whether that is a malicious attachment, a known-bad link, or a spoofed domain. That model is now the weakness. The attacks that cost organizations the most carry no payload to scan, and they are written by AI to read like normal business correspondence. KnowBe4 found a 47.3% increase in attacks slipping past Microsoft and secure email gateways in a single year.
The gaps below share one root cause: tools that inspect content cannot see intent. Closing them takes behavioral AI that models how people and relationships actually behave, layered on top of the controls you already run.
Payload-Free Attacks Slip Past Inbound Email Filters
The most damaging inbound threats contain nothing for a scanner to catch. Business email compromise (BEC) and spear phishing messages carry no malware and no malicious links. They rely on persuasive text that borrows a trusted identity and asks for a wire transfer or sensitive data.
Picture a finance manager who gets a note that reads exactly like her CFO's: same phrasing, same signature, a routine request to release a vendor payment before the end of the day. Nothing in that message trips a filter, because there is nothing technical to trip. Attackers study reporting lines and communication habits first, then write the request to match them. The FBI's IC3 report calls BEC the most financially destructive enterprise-targeted cyber threat in the United States, with losses reaching $3.05 billion in 2025. Once a request like that is approved, the loss and the data exposure spread across departments before anyone notices.
Behavioral analysis reads the situation a scanner can't. AI models normal communication patterns for each sender, including who they email, how often, and how they write, then flags the message that breaks the pattern. Natural language processing (NLP) weighs intent, catching the sudden shift to urgency that tends to precede fraud. That turns an invisible, payload-free request into a security event a team can act on. The same blind spot widens the moment an attacker stops impersonating a trusted identity and starts using a real one.
Identity Misuse and Account Takeover
A compromised account defeats content inspection entirely, because the message really does come from a trusted person. When an attacker gets past multifactor authentication and sends mail from a genuine inbox, every control that leans on sender reputation waves it through.
The exposure here is broad. Verizon's 2025 Data Breach Investigations Report found stolen credentials remain one of the most common paths into a breach, and account takeover attacks are rising year over year as credential theft feeds the next wave of internal attacks. Once inside, an attacker reads real threads and replies in context, which is exactly what makes the follow-on messages so hard to spot.
Behavioral modeling watches for the account acting unlike itself. AI compares session and device signals against each user's history, and anomaly detection surfaces unusual sending patterns that suggest the mailbox is no longer in the owner's hands. NLP compares new messages against prior ones and catches style deviations rules never encoded, while adaptive risk scoring can trigger a response often before significant damage occurs. When the compromised identity belongs to a supplier rather than a colleague, the same trust exploitation reaches straight into your payment process.
Where Inbound Email Protection Misses Vendor Compromise
Vendor and supply chain attacks weaponize a relationship your filters are built to trust. Vendor email compromise turns an established supplier thread into invoice fraud, a quiet change to banking details, or a redirected payment.
This is the fastest-moving version of the trust problem. Verizon's DBIR found the share of breaches involving a third party doubled in a year, from 15% to 30%. According to the Association for Financial Professionals, vendor imposter fraud was cited by 45% of organizations in 2024, up sharply from 34% the year before. Because these messages come from, or convincingly mimic, a real business relationship, they arrive looking like traffic you have exchanged safely for years.
Behavioral analysis grounds detection in how a specific vendor actually behaves: the cadence of invoices, the usual approvers, the accounts payments normally go to. AI flags the deviation, such as banking details that change midstream or a payment request that arrives outside the normal cycle. NLP catches subtle wording inconsistencies, and relationship mapping flags a message that sits out of context for that account. That helps surface fraud in a trusted thread before the payment leaves. Attackers know how convincing these messages already are, and generative AI is making the next ones cheaper and faster to produce.
Generative AI Is Widening the Inbound Threat Gap
Generative AI removes the last tells that used to give phishing away. Attackers now produce fluent, tailored phishing campaigns at volume, without the awkward phrasing or spelling mistakes that once flagged a message as suspect.
The shift is already measurable. KnowBe4's Phishing Threat Trends Report found that 82.6% of phishing emails observed between late 2024 and early 2025 used AI-generated content. The UK's NCSC assessed that generative AI can already support convincing interaction with victims, including lure documents free of the language errors that used to reveal phishing, and that this capability will keep growing. When the words on the page look flawless, any defense that judges a message by its content is reading the wrong signal.
Defensive AI has to read behavior instead. Real-time models weigh each message against the sender's history and flag the deviation even when the writing is clean. NLP parses intent rather than surface polish, and continuous retraining on fresh telemetry helps close detection gaps as tactics change. The harder problem is that raising sensitivity against threats this convincing tends to bury teams in false alarms.
False Positives That Drain Security Teams
False positives are the hidden cost of fighting these gaps with rules. Every unnecessary alert pulls an analyst off a real investigation, and past a certain volume the genuine threats simply get lost in the queue.
The strain shows in the numbers. The 2025 SANS survey on detection and response found roughly three-quarters of organizations rank false positives as their top detection challenge, and the share reporting "very frequent" false positives climbed year over year. Rule-based systems create this problem by design: they can only ask whether a message matches a known-bad pattern, so anything unusual gets flagged, and the noise compounds until real threats hide inside it.
Behavioral baselining cuts the noise at its source. Instead of matching messages against a static rule, AI builds an updated model of normal for each sender and flags only what breaks it. Feedback loops fold in analyst decisions and user-reported messages, refining the model so the same false alarm doesn't keep resurfacing. The result is fewer, higher-confidence alerts, which is the only version of detection that scales against AI-era volume.
Close Inbound Email Threat Protection Gaps with Behavioral AI
The five gaps trace back to one thing: legacy tools read content, and modern attacks hide in behavior. Abnormal helps close that gap with behavioral AI that models normal activity across messages, identities, and business relationships, then surfaces the deviations content inspection misses. It connects directly to Microsoft 365 and Google Workspace through APIs, so it adds detection without MX record changes or new hardware, and extends protection to Slack, Teams, and Zoom.
Key capabilities include:
- Behavioral AI engine that learns how users and vendors normally communicate, then isolates the anomalies.
- API-based, out-of-band deployment that preserves mail flow while adding deep inspection and response.
- Cross-channel coverage that unifies detection across email and connected collaboration tools.
Abnormal is designed to layer onto the controls you already run, not replace them, filling the gaps that content-based tools leave open against AI-driven attacks. Recognized as a Leader in the Gartner® Magic Quadrant™ for Email Security Platforms, the platform is built to give security teams back the time that alert noise and payload-free attacks quietly drain.
Ready to close the critical gaps in your inbound email threat protection? Get a demo to see how Abnormal catches the sophisticated attacks legacy tools miss.