Compromised credentials are login details that end up in an attacker's hands through phishing, malware, or a previous data breach. A valid username and password are not proof that the person entering them is the account's real owner, so attackers who obtain a working login can walk into an email account, cloud application, or identity system through the front door. What that access unlocks, and how long it lasts, depends on what a security team can see in the activity that follows the login itself.
The path from a stolen password to a full account takeover unfolds in stages, each with its own signals and each with a narrowing window for containment. Recognizing that progression turns a silent compromise into a detectable event, and detection is what separates a contained incident from a costly breach.
This guide covers where compromised credentials come from, the five stages attackers move through once inside, the behavioral signals that expose misuse of a trusted account, and the response steps that close the window before a foothold becomes a breach.
Key Takeaways
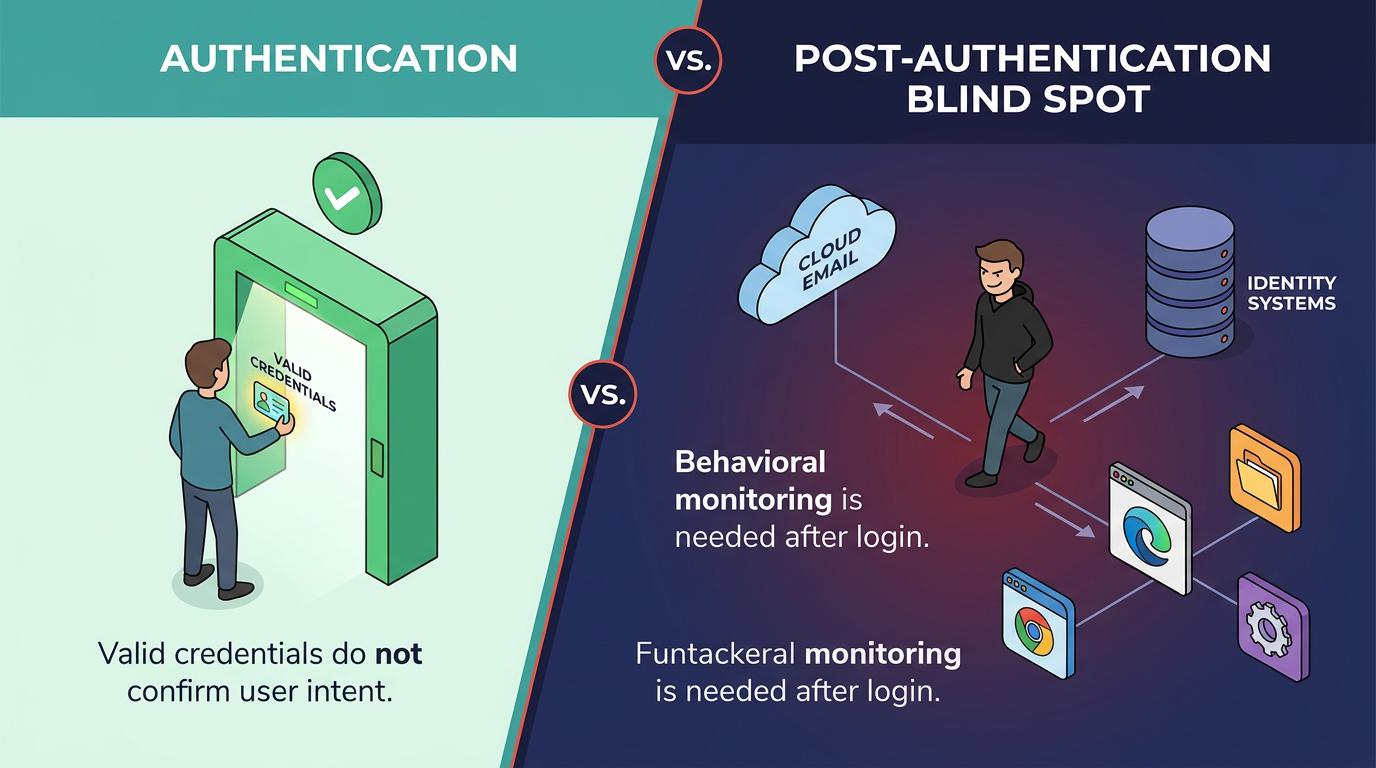
Compromised credentials exploit a basic authentication blind spot: a valid login does not independently establish the user's intent. Security teams therefore need context from activity that follows authentication.
Stolen credentials can give attackers the access rights and permissions assigned to a compromised account.
Session theft and malicious app permissions may preserve access after a password reset or multi-factor authentication (MFA) challenge.
Abnormal's behavioral AI is designed to help surface suspicious cloud email, identity, session, and supported collaboration activity. It complements existing security controls rather than replacing them.
How Do Compromised Credentials Bypass Traditional Security Controls?
This post-authentication blind spot lets compromised credentials pass controls that validate the presented credential. Credential abuse was the initial access vector in 13% of breaches analyzed in the 2026 Verizon Data Breach Investigations Report (DBIR), ranking behind vulnerability exploitation.
Valid credentials can unlock the access rights assigned to local, domain, and cloud accounts. Attackers may then use overlapping permissions to move between accounts and systems, depending on the environment and available controls.
Attackers may also evade multi-factor authentication using several methods that target the authentication step itself rather than the underlying credential:
Adversary-in-the-Middle (AiTM) Proxies: Relay a live login session through an attacker-controlled proxy to capture the resulting session token.
Device Code Phishing: Trick a user into approving a device authorization request the attacker initiated.
OAuth Consent Phishing: Get a user to grant a malicious app permissions through the legitimate OAuth consent flow.
Service Account Abuse: Use a non-human account's credentials, which often carry broad permissions and lighter monitoring.
Session Token Theft: Steal an active session token directly, bypassing the login step entirely.
None of these methods require the attacker to repeat the original login process, which is what lets them preserve authenticated access after a password reset or MFA challenge.
Abnormal is designed to help surface suspicious behavior in cloud email, identity activity, and supported collaboration platforms. Network access, endpoint activity, and cloud infrastructure misuse remain broader risks that require complementary identity, security information and event management (SIEM), endpoint, cloud, and network controls.
Where Do Compromised Credentials Come From?
Compromised credentials commonly originate from phishing, infostealer activity, underground access markets, and credential replay. Three supply chains frequently support account takeover attempts:
Phishing-as-a-Service Kits: Kits such as Tycoon 2FA can relay a victim's login through a reverse proxy and capture a post-MFA session for cloud email accounts. Abnormal's threat intelligence team documented a voicemail-themed variant that used an AiTM proxy to support credential and session theft. Law enforcement disruption may interrupt this infrastructure, but operators can rebuild domains and resume activity.
Infostealer Logs: A Cybersecurity and Infrastructure Security Agency (CISA) advisory describes how LummaC2 malware infiltrates victim environments and exfiltrates sensitive information across critical infrastructure sectors. Criminal markets can resell harvested credentials, cookies, and related access data as ready-made entry points.
Credential Stuffing: Attackers replay username and password pairs exposed in earlier breaches. Password reuse can turn a credential compromised in one environment into a working key for another account.
Email remains a common delivery mechanism for credential phishing, while malware and credential markets expand the available supply. Organizations can reduce exposure by combining phishing prevention, strong identity controls, session monitoring, password hygiene, and post-authentication behavioral analysis.
The Five Attack Stages After Credential Compromise
Credential compromise can lead to a recognizable sequence of reconnaissance, escalation, lateral movement, exfiltration preparation, and persistence. Each stage requires controls aligned with the system where the activity occurs, as reflected in the National Institute of Standards and Technology (NIST) incident response guidance.
1. Initial Access and Environment Reconnaissance
Following a successful compromise, attackers may map network structure, identify trust relationships, catalog security systems, and search for useful accounts. MITRE ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) documents attempts to list valid accounts, usernames, or email addresses as Account Discovery.
Cloud email can still provide related context when the compromised identity begins communicating in unexpected ways. A newly compromised account might contact unfamiliar recipients, request access information, or initiate password-reset conversations outside established workflows. Abnormal is designed to help surface those email and account-based deviations. Investigators can compare those requests with the user's established communication patterns and identity-provider events to determine whether the activity merits escalation.
2. Privilege Escalation Through Email
Compromised email accounts can support privilege escalation by giving attackers a trusted channel for password-reset requests, help desk manipulation, and access requests. A CISA advisory on Scattered Spider describes how attackers gather reset-specific information and use spearphishing calls to persuade help desk personnel to reset passwords or transfer MFA tokens.
Voice-based manipulation requires controls beyond email security. Within cloud email, however, Abnormal can help identify suspicious account-based communication surrounding the attempt, such as unusual reset requests, atypical recipients, or messages that depart from established workflow cadence. Combining those signals with identity-provider events and help desk procedures gives investigators stronger context than either source provides alone. Organizations should pair behavioral email protection with verification processes that resist social engineering across email, voice, and other channels.
3. Lateral Movement Across Systems
Attackers with established access may move through network resources, shared credentials, or trusted internal communication channels. Inside cloud email, this behavior can appear as Internal Spearphishing, where an adversary uses a compromised account to target colleagues within the same organization. Similar account-based attacks may extend into supported collaboration platforms where deployed.
Abnormal is designed to help surface unusual recipient behavior, shifts in engagement flows, and suspicious messages sent from trusted accounts. These observations can provide evidence of the email or collaboration component of lateral movement. Remote access connections, service account activity, host-to-host movement, and access to systems outside a user's normal scope fall outside this communication-layer visibility. Security teams can correlate those alerts with collaboration threats to build a fuller incident timeline.
4. Data Exfiltration Preparation
Attackers may identify valuable repositories, assess data sensitivity, and prepare collection or transfer methods before exfiltration. MITRE describes email-focused collection through Remote Email Collection, which covers attempts to gather information from cloud or server-based mailboxes.
Bulk repository access, systematic file searches, and unusual data queries occur within storage, endpoint, or cloud systems and require controls for those environments. Abnormal does not replace that monitoring. Its role is to help surface suspicious cloud email and account behavior that may accompany preparation, including changes in recipient patterns, workflow timing, or engagement flows. Correlating those observations with telemetry from the affected environments can help investigators recognize a developing incident. This layered approach extends email threat detection without attaching email security claims to repository activity it does not observe.
5. Persistence Mechanism Installation
Attackers may try to maintain access across system interruptions and credential changes by creating accounts, adding cloud credentials, registering devices, changing roles, or establishing alternative access paths. MITRE groups many of these techniques under Account Manipulation. These identity and infrastructure changes require monitoring from the systems that manage them.
The email component of persistence may include continued use of a trusted mailbox, suspicious internal messages, or account-based workflows that no longer match the legitimate user's patterns. Abnormal is designed to help surface related identity signals, session and device signals, and changes in account-based communication. A Scattered Spider advisory also describes attackers registering their own authentication methods after compromise. Identity providers, cloud security tools, and endpoint controls should investigate and contain those broader persistence mechanisms.
Common Behavioral Signals That Indicate Compromised Credentials
Abnormal's behavioral AI is designed to evaluate cloud email, identity, session, and supported collaboration activity for deviations that may indicate account takeover. Seven generalized signal categories help security teams interpret that activity without relying on unconfirmed technical inputs:
Identity Signals: Changes in account activity may indicate that a trusted identity is operating differently from its established behavior. These signals become more useful when paired with suspicious email actions.
Session and Device Signals: Unexpected session and device signals can add context to cloud email activity, especially when the account also initiates unusual requests or conversations.
Recipient Behavior: A compromised account may contact atypical recipients, expand its recipient list, or target colleagues who do not normally participate in its workflows.
Timing Patterns: Messages, access requests, or sensitive conversations outside an account's established timing patterns may warrant additional review.
Workflow Cadence: Attackers may disrupt familiar approval, payment, password-reset, or vendor interaction patterns as they try to exploit the account's authority.
Engagement Flows: Changes in who initiates conversations, how recipients respond, or how a request progresses through an organization can help surface suspicious activity.
Communication Changes: Shifts in message content, sending frequency, tone, or account-based requests may indicate misuse of a trusted identity.
Abnormal can apply this context across cloud email and supported technology integrations. When an incident extends beyond those surfaces, organizations should correlate these observations with telemetry from the affected environments.
How Behavioral AI Baselines Normal Account Activity
Abnormal's behavioral AI builds context from observable cloud email and account-based patterns, then uses deviations to help identify activity that may warrant investigation. The model focuses on deviations in workflow cadence and recipient behavior.
For example, a compromised account might begin sending password-reset requests to unfamiliar recipients, introduce new payment instructions outside its usual workflow, or contact internal users who rarely interact with the account. Each event may appear plausible in isolation. Behavioral context makes the combination more informative by comparing current activity with the account's established patterns and relevant peer behavior.
Machine learning supports profiles that adapt as legitimate work patterns change. Risk scoring can combine observed deviations and peer context into a clearer view of account risk. This approach helps security teams distinguish routine variation from behavior that merits review without claiming visibility into unrelated endpoint, repository, or network activity.
Abnormal applies this model through account takeover protection, which covers email and account-based components of credential stuffing, token theft, and lateral phishing. It complements existing security controls rather than replacing them.
How to Create an Automated Response to Credential Compromise Incidents
Automated response workflows can help contain compromised accounts while preserving the context investigators need. Effective playbooks coordinate email security, identity systems, and orchestration tools according to the organization's response policies.
Revoke Active Sessions
Session revocation can terminate active access associated with a compromised account and invalidate the session states an attacker relies on for persistence. NIST's session guidance recommends reauthentication, session termination, or support notification when potential fraud appears during a session.
Abnormal's account takeover protection is designed to support actions such as revoking sessions and blocking access when compromise indicators meet configured response criteria. Identity systems remain responsible for enforcing session and authentication changes across their environments. Coordinating these actions can reduce the time an attacker retains access while keeping response decisions aligned with organizational policy, risk tolerance, and investigation requirements.
Reset Compromised Credentials
Response workflows can trigger a credential reset after security teams or automated controls identify sufficient evidence of compromise. Resetting the password alone may not address stolen sessions, malicious app permissions, or attacker-controlled authentication methods, so playbooks should coordinate resets with session revocation and identity review.
NIST response controls support structured containment and recovery actions. Organizations can use those controls to define approval thresholds, assign ownership, and document the sequence of response steps. Abnormal can provide email, identity, and behavioral context to help inform the workflow, while identity platforms execute credential and session changes. This division keeps the response aligned with the capabilities and authority of each system.
Preserve Investigation Evidence
Containment workflows should preserve relevant evidence before response actions alter the account state. Authentication logs, session details, email activity, and behavioral indicators can help investigators reconstruct what changed, whom the attacker targeted, and how the attacker used the trusted identity.
Security orchestration can coordinate evidence collection and response across email security, identity systems, SIEMs, and other controls. Maintaining an ordered timeline supports incident analysis, audit documentation, and follow-up remediation. It also helps teams distinguish the activity Abnormal observed in cloud email and supported account surfaces from evidence collected by endpoint, cloud, identity, or network tools. That separation produces clearer findings and avoids overstating any individual control's visibility.
Strengthen Post-Authentication Credential Security
Post-authentication monitoring helps security teams recognize visible misuse of a trusted account after a successful login.
Abnormal is designed to surface suspicious post-authentication activity through deviations in recipient behavior and account-based communication across its supported surfaces.
This layered model gives security teams a practical way to investigate compromised credentials without treating one technology as a complete defense. It can also support faster containment, clearer incident timelines, and more consistent audit evidence when teams coordinate detection and response across the security stack.
Named a Customers' Choice in the 2026 Gartner® Peer Insights™ Voice of the Customer for Email Security, Abnormal helps organizations identify compromised credentials and support account takeover response.
Ready to see how behavioral detection can help? Book a demo of Abnormal today.
Frequently Asked Questions
What Is the Difference Between Compromised Credentials and Account Takeover?
Compromised credentials are the stolen or exposed login details themselves, such as a username and password, a session token, or an authentication cookie. Account takeover is what happens when an attacker actually uses those credentials to access and control the account. A credential can be compromised without ever being used, but every account takeover starts with some form of compromised credential or session.
Can Multi-Factor Authentication Fully Stop Account Takeover From Compromised Credentials?
Multi-factor authentication blocks many credential-based attacks, but it does not stop every path to account takeover. Techniques such as adversary-in-the-middle proxies, device code phishing, and session token theft are designed specifically to work around MFA rather than through it, which is why security teams pair MFA with monitoring for the account behavior that follows a login.
Does Resetting a Password Stop an Active Account Takeover?
A password reset alone often does not end an active account takeover. If an attacker still holds a valid session token, has registered their own MFA method, or has granted a malicious application access to the account, those footholds can survive a password change. Effective containment typically pairs a credential reset with session revocation and a review of connected applications and authentication methods.
What Should a Company Do Immediately After Discovering Compromised Credentials?
Security teams typically move to revoke active sessions, reset the affected credentials, and preserve logs and other evidence before those actions change the account's state. Coordinating these steps across email security, identity systems, and security orchestration tools helps limit an attacker's window of access while keeping a clear record for the investigation that follows.