Actualizaciones de producto
Novedades
Lanzamientos recientes
Know What AI Is Running in Your Organization: AI Governance Now Available as a Standalone Product
AI Governance is now available as a standalone product, bringing the Behavioral Security Platform trusted by more than 5,000 organizations to the questions you're being asked about AI: Which AI tools and agents are in use? What can they access? And what are you spending on them?
Leer el artículo del lanzamientoRight Message, Wrong Person: When Legitimate Emails Become Data Breaches
A trusted contact can still be the wrong recipient. Discover how Abnormal’s Misdirected Email Prevention uses behavioral AI to catch recipient mistakes before confidential information reaches the wrong person.
Leer el artículo del lanzamientoThe AI Security Suite Powered by Behavioral AI
Abnormal’s AI Security suite gives enterprises visibility and governance over the AI running in their business, control over the AI their employees use, and protection against AI-driven attacks being used against them.
Leer el artículo del lanzamientoProactive Identity Risk Reduction for the Attacks That Matter
ISPM prioritizes identity misconfigurations based on real attack risk, helping security teams address the gaps attackers are most likely to exploit.
Leer el artículo del lanzamientoActualizaciones diarias
Semana del 2 nov 2026
- 7 nov 2026Identity SecurityNueva funcionalidad
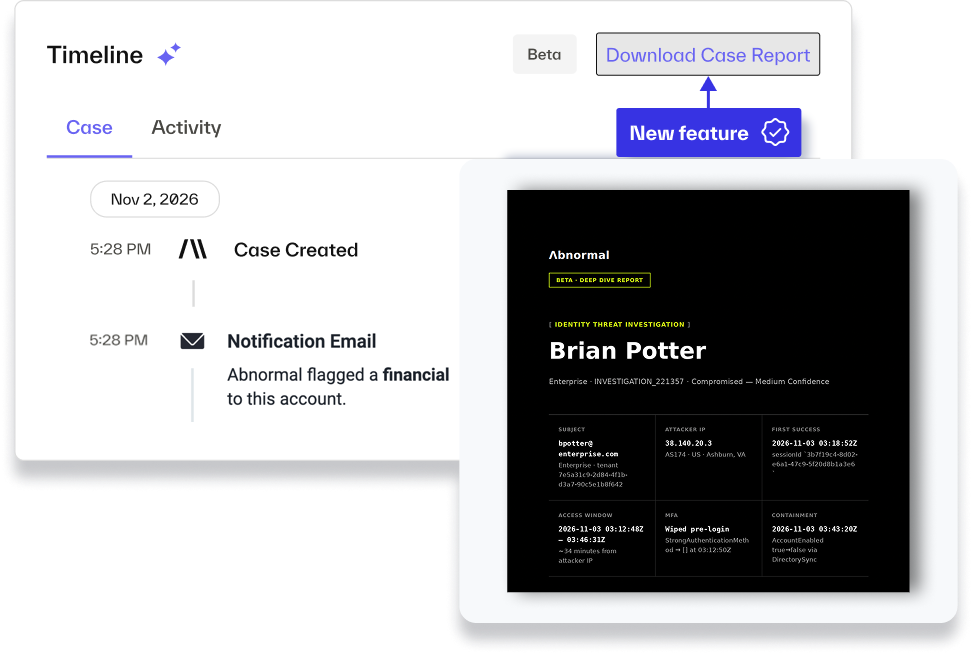
Case Reports for Identity Threat Protection
Identity Threat Protection now includes an AI agent that investigates every case after detection. It reviews the user’s recent activity, including interactive and non-interactive sign-ins, suspicious email, and admin changes. It pulls signals the initial detection didn’t weigh and re-evaluates the ones already on the case. When it finds that a low-confidence case looks like a real compromise, it can raise that case to medium confidence.
With this release:
Find compromise activity in signals the initial detection didn’t weigh, such as non-interactive sign-ins, email, and admin activity in one view.
Based on investigation, the AI agent may raise case confidence from low to medium confidence and sends the associated notifications
Understand why a case was raised, with case promotion added to the case timeline and a plain-language reason drawn from the agent’s investigation
Review the agent’s verdict, key evidence, timeline, and primary indicators of compromise (IOCs) in one report, without rebuilding the investigation yourself
Download the report as a PDF from the case view to share with your team or attach to an email
The AI investigation agent helps analysts focus on the cases most likely to be real and shows its work. If you’ve configured auto-remediation for medium-confidence cases, promoted cases follow that configuration.
- 6 nov 2026Identity SecurityNueva funcionalidad
SharePoint and OneDrive Activity Detection
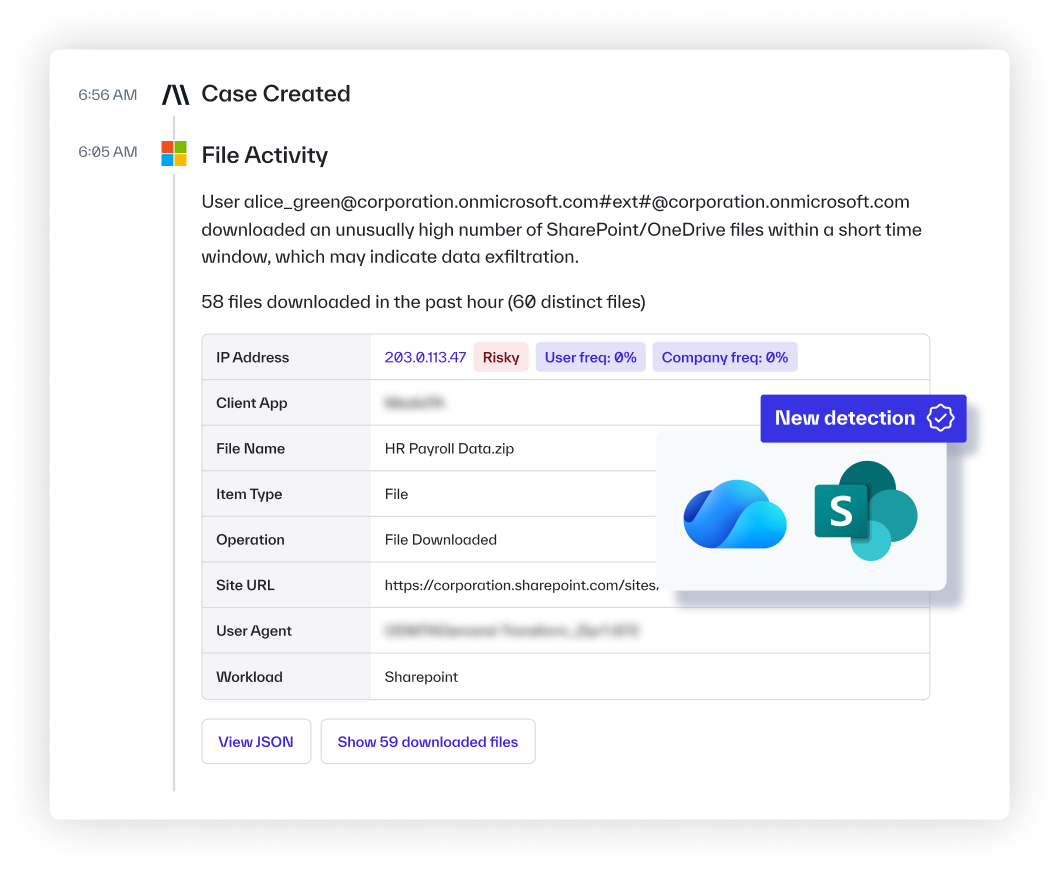
Identity Threat Protection now detects suspicious file activity in SharePoint and OneDrive.
A compromised account rarely stops at the inbox. Attackers go after your files next, searching for sensitive items and then pulling data down in bulk. Now your team can catch that activity as it happens and investigate it as part of one case, instead of piecing it together across tools.
With this release:
— Catch mass downloads and deletions that look like automation, before an attacker walks out with your files
— Spot scripted or programmatic file access by a compromised account
— Spot searches for sensitive keywords in SharePoint, an early sign an attacker is hunting for data to steal
— Investigate file activity in the same case as related sign-in signals, with no stitching together of separate alerts
Security teams can now see data theft in progress and respond before sensitive files leave the organization.
- 4 nov 2026AI Phishing CoachNueva funcionalidad
Custom Sender Domains for AI Phishing Coach
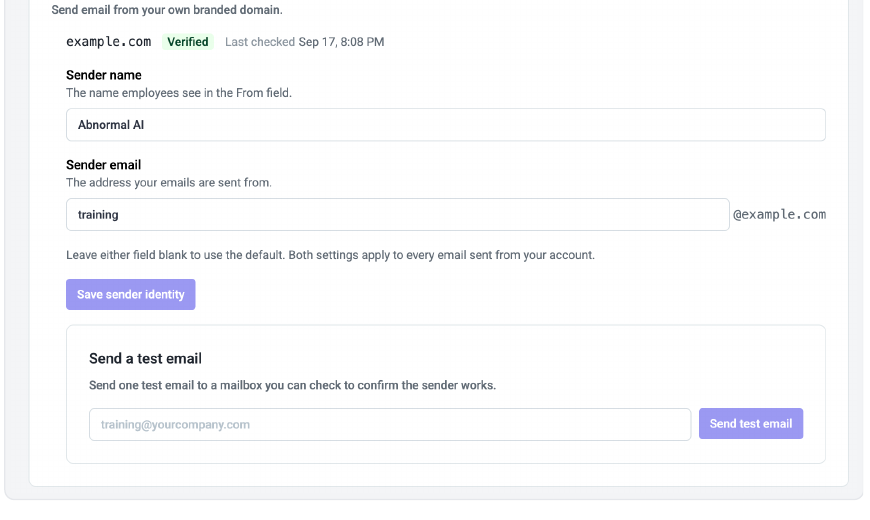
Instead of arriving from an Abnormal AI address, AI Phishing Coach emails can come from a domain or subdomain you control, with the sender name and address you choose. The portal generates the DNS records you need, verifies the domain, and lets you send a test email before employees see anything.
With this release:
Send phishing simulations, Just-in-Time Coaching, video training, reminders, invitations and acknowledgments from your custom domain
Authenticate the domain with generated SPF, DKIM and DMARC records
Set the sender name and address, then confirm them with a test email
Your awareness program now look like it is coming from the security team. Simulations look like the email employees actually receive, while coaching and training arrive from a sender they already trust.
To get started, see Configure a Custom Sender Domain for AI Phishing Coach.
- 4 nov 2026Inbound Email SecurityMejora
Custom Rules Replace Safelist and Blocklist with More Granular Control
With Custom Rules you can:
Define more precise policies: Combine 50+ message attributes with AND/OR logic and exclusions, including authentication results, domain age, subject patterns, and attachment types.
Test before enforcing: Validate rules against historical messages from the last 10-30 days, test in passive mode against real mail before enforcing, and keep unfinished rules in draft.
Control access: Use role-based permissions to manage who can view, create, and edit rules.
Gain greater visibility: Track rule changes, monitor match counts and see which rules acted on specific messages.
What to expect:
On November 11, existing Safelist and Blocklist entries will automatically migrate to Custom Rules in passive mode, and Safelist and Blocklist becomes delete-only. Your existing lists will continue to enforce during a seven-day review period. On November 18, migrated rules will become active and the legacy lists will be retired. No action is required to maintain your existing policies
- 3 nov 2026AI Phishing CoachNueva funcionalidad
Know Who to Coach, Delivered on Your Schedule
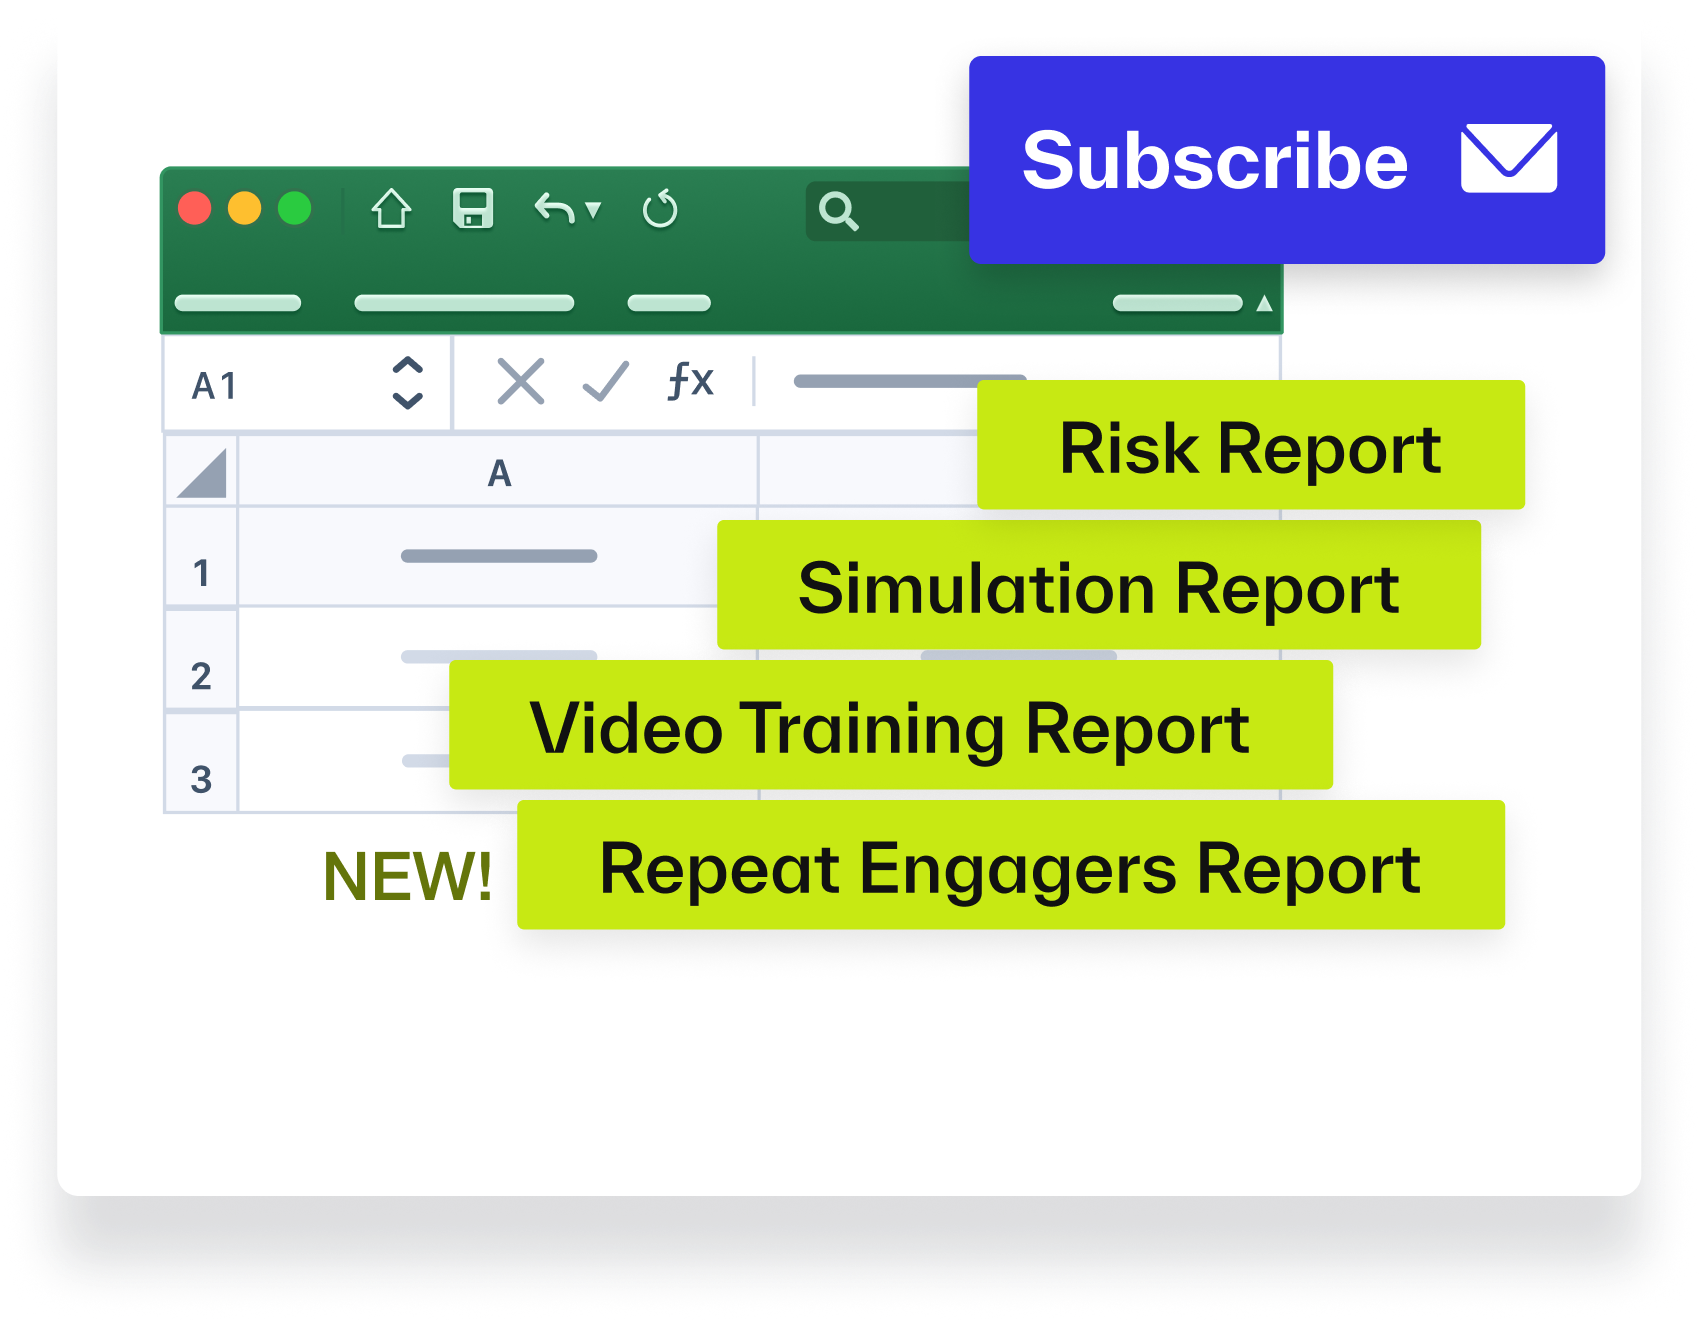
Instead of pulling the same reports by hand every week or month, subscribe to the AI Phishing Coach reports you need and get them delivered automatically. A one-time click and repeat risky behavior can look the same in a standard report, so the new Repeat Engagers report shows exactly who keeps engaging and where coaching matters most.
With this release:
Subscribe to the Executive, Simulation, Training and Risk reports
Each recipient gets one email per period with only the reports they subscribe to
The new Repeat Engagers report lists employees who engaged with simulations consecutively, along with their overall engagement rate. Run it on demand or add it to a Simulation subscription.
Every report becomes evidence of progress, delivered on schedule to the people who need to see it.
Semana del 26 oct 2026
- 30 oct 2026DetectionMejora
Esta semana en detección
Weekly Detection Enhancements - Week of October 30
Strengthened detection of malicious links across supported URL-hosting platforms, with stronger remediation of URL-based attacks.
Improved detection of brand impersonation messages that use visual deception to evade text-only analysis.
Expanded detection coverage for compromised-sender attacks with a newly launched Sender Compromise model.
- 29 oct 2026Identity SecurityNueva funcionalidad
Track Identity Posture Over Time
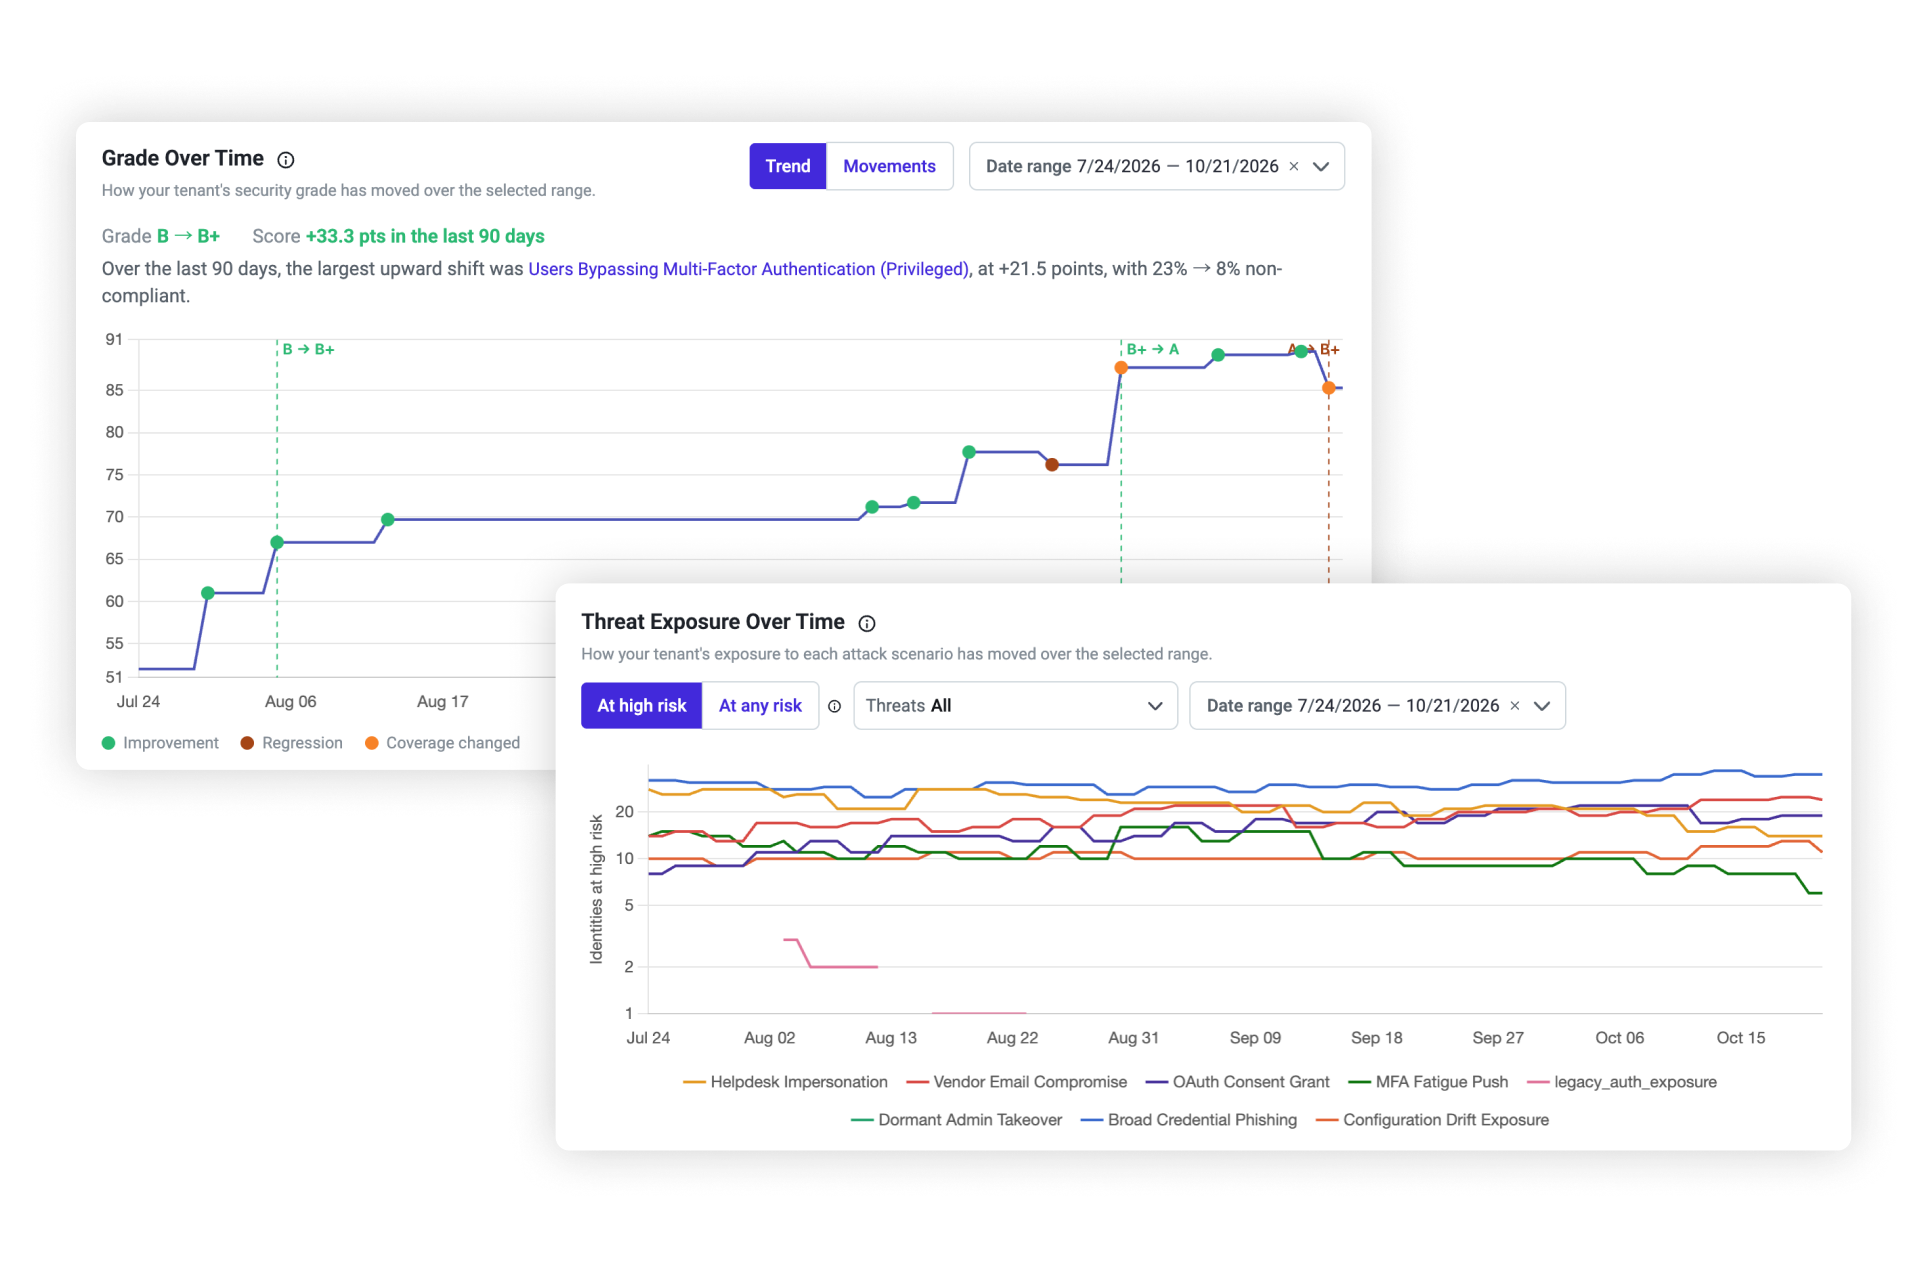
Identity Threat Protection now shows how your ISPM security grade and threat exposure change over time.
A point-in-time grade tells you where you stand today, but not whether your remediation work is paying off. Now admins can see how their posture has moved across a date range and how exposure to each attack scenario has changed along the way.
With this release:
— Track your security grade and score over time, with markers for improvements, regressions, and coverage changes
— See identities at high risk or at any risk for each attack scenario, such as Helpdesk Impersonation, Vendor Email Compromise, and MFA Fatigue Push, and filter by threat
— Review up to 180 days of history, or less if you deployed Identity Threat Protection more recently
Security teams can now show leadership measurable progress and catch regressions as they happen.
- 29 oct 2026Identity SecurityNueva funcionalidad
Helpdesk Reset Risk Factors
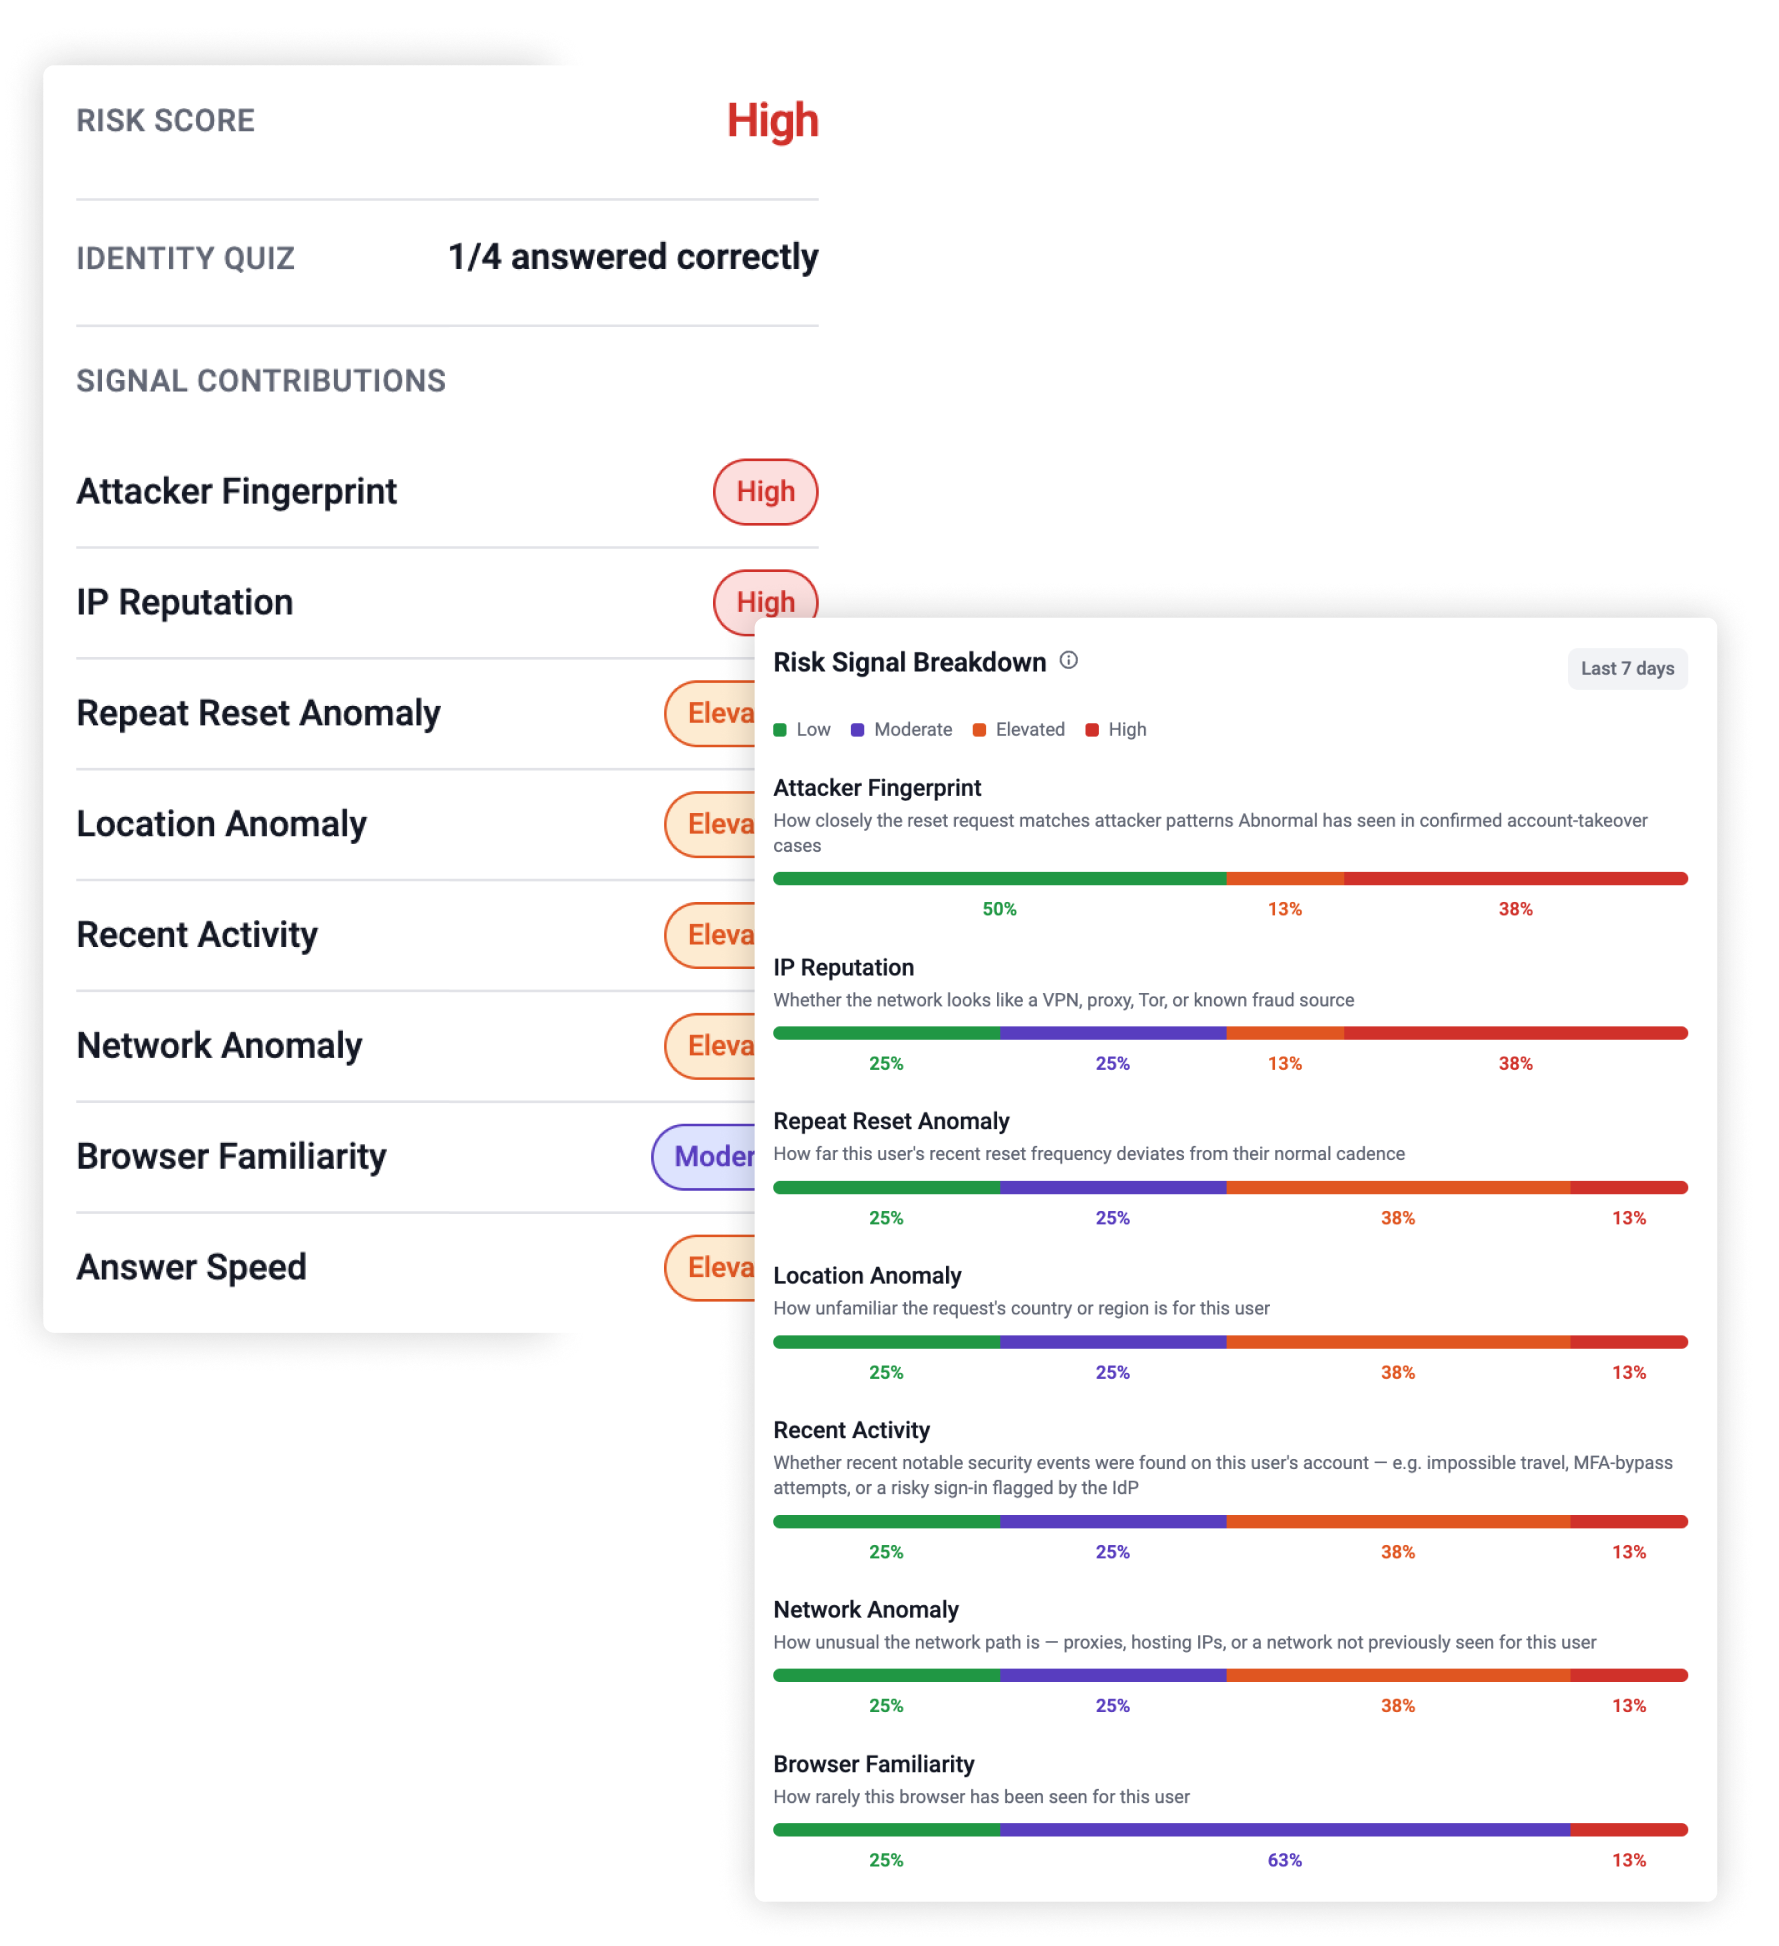
Identity Threat Protection now shows the risk signals behind each Adaptive Identity Reset risk score.
A risk rating is only useful if your team can see what’s behind it. Now help desk and security teams can expand any reset and see which signals contributed to the score, without having to guess why a request was flagged.
With this release:
— Expand any reset to see the signals behind its risk score, alongside the identity quiz result
— Review each signal’s rating (Low, Moderate, Elevated, or High), with plain-language definitions of what each one measures
— See the overall reset risk score on the same four-tier scale
Help desk teams can act with confidence on every reset request and explain why a request was flagged.
- 27 oct 2026AI Data AnalystNueva funcionalidad
New and Enhanced AI Data Analyst Experience
AI Data Analyst is the conversational AI data analyst built into the Abnormal platform: ask a question by email or work conversationally in the portal, and get an answer grounded in your own Abnormal environment, typically within 15 minutes. Every response ties back to your actual threats blocked, people protected, and risk surfaced.
With this release:
Schedule recurring or one-time reports with smart defaults, or turn any question into an ongoing report with Schedule as Custom Report. Pick a frequency and AI Data Analyst derives the reporting window.
Track every report and conversation in one place with the new Report Repository, including versioned downloads and full history.
Manage reporting across every tenant from a single view, built for MSSPs and multi-tenant customers.
AI Data Analyst turns the questions your CISO and security team ask every day into answers you can act on, and turns those answers into reports that keep running on their own.
- 26 oct 2026AI Phishing CoachMejora
Simplified Settings for AI Phishing Coach
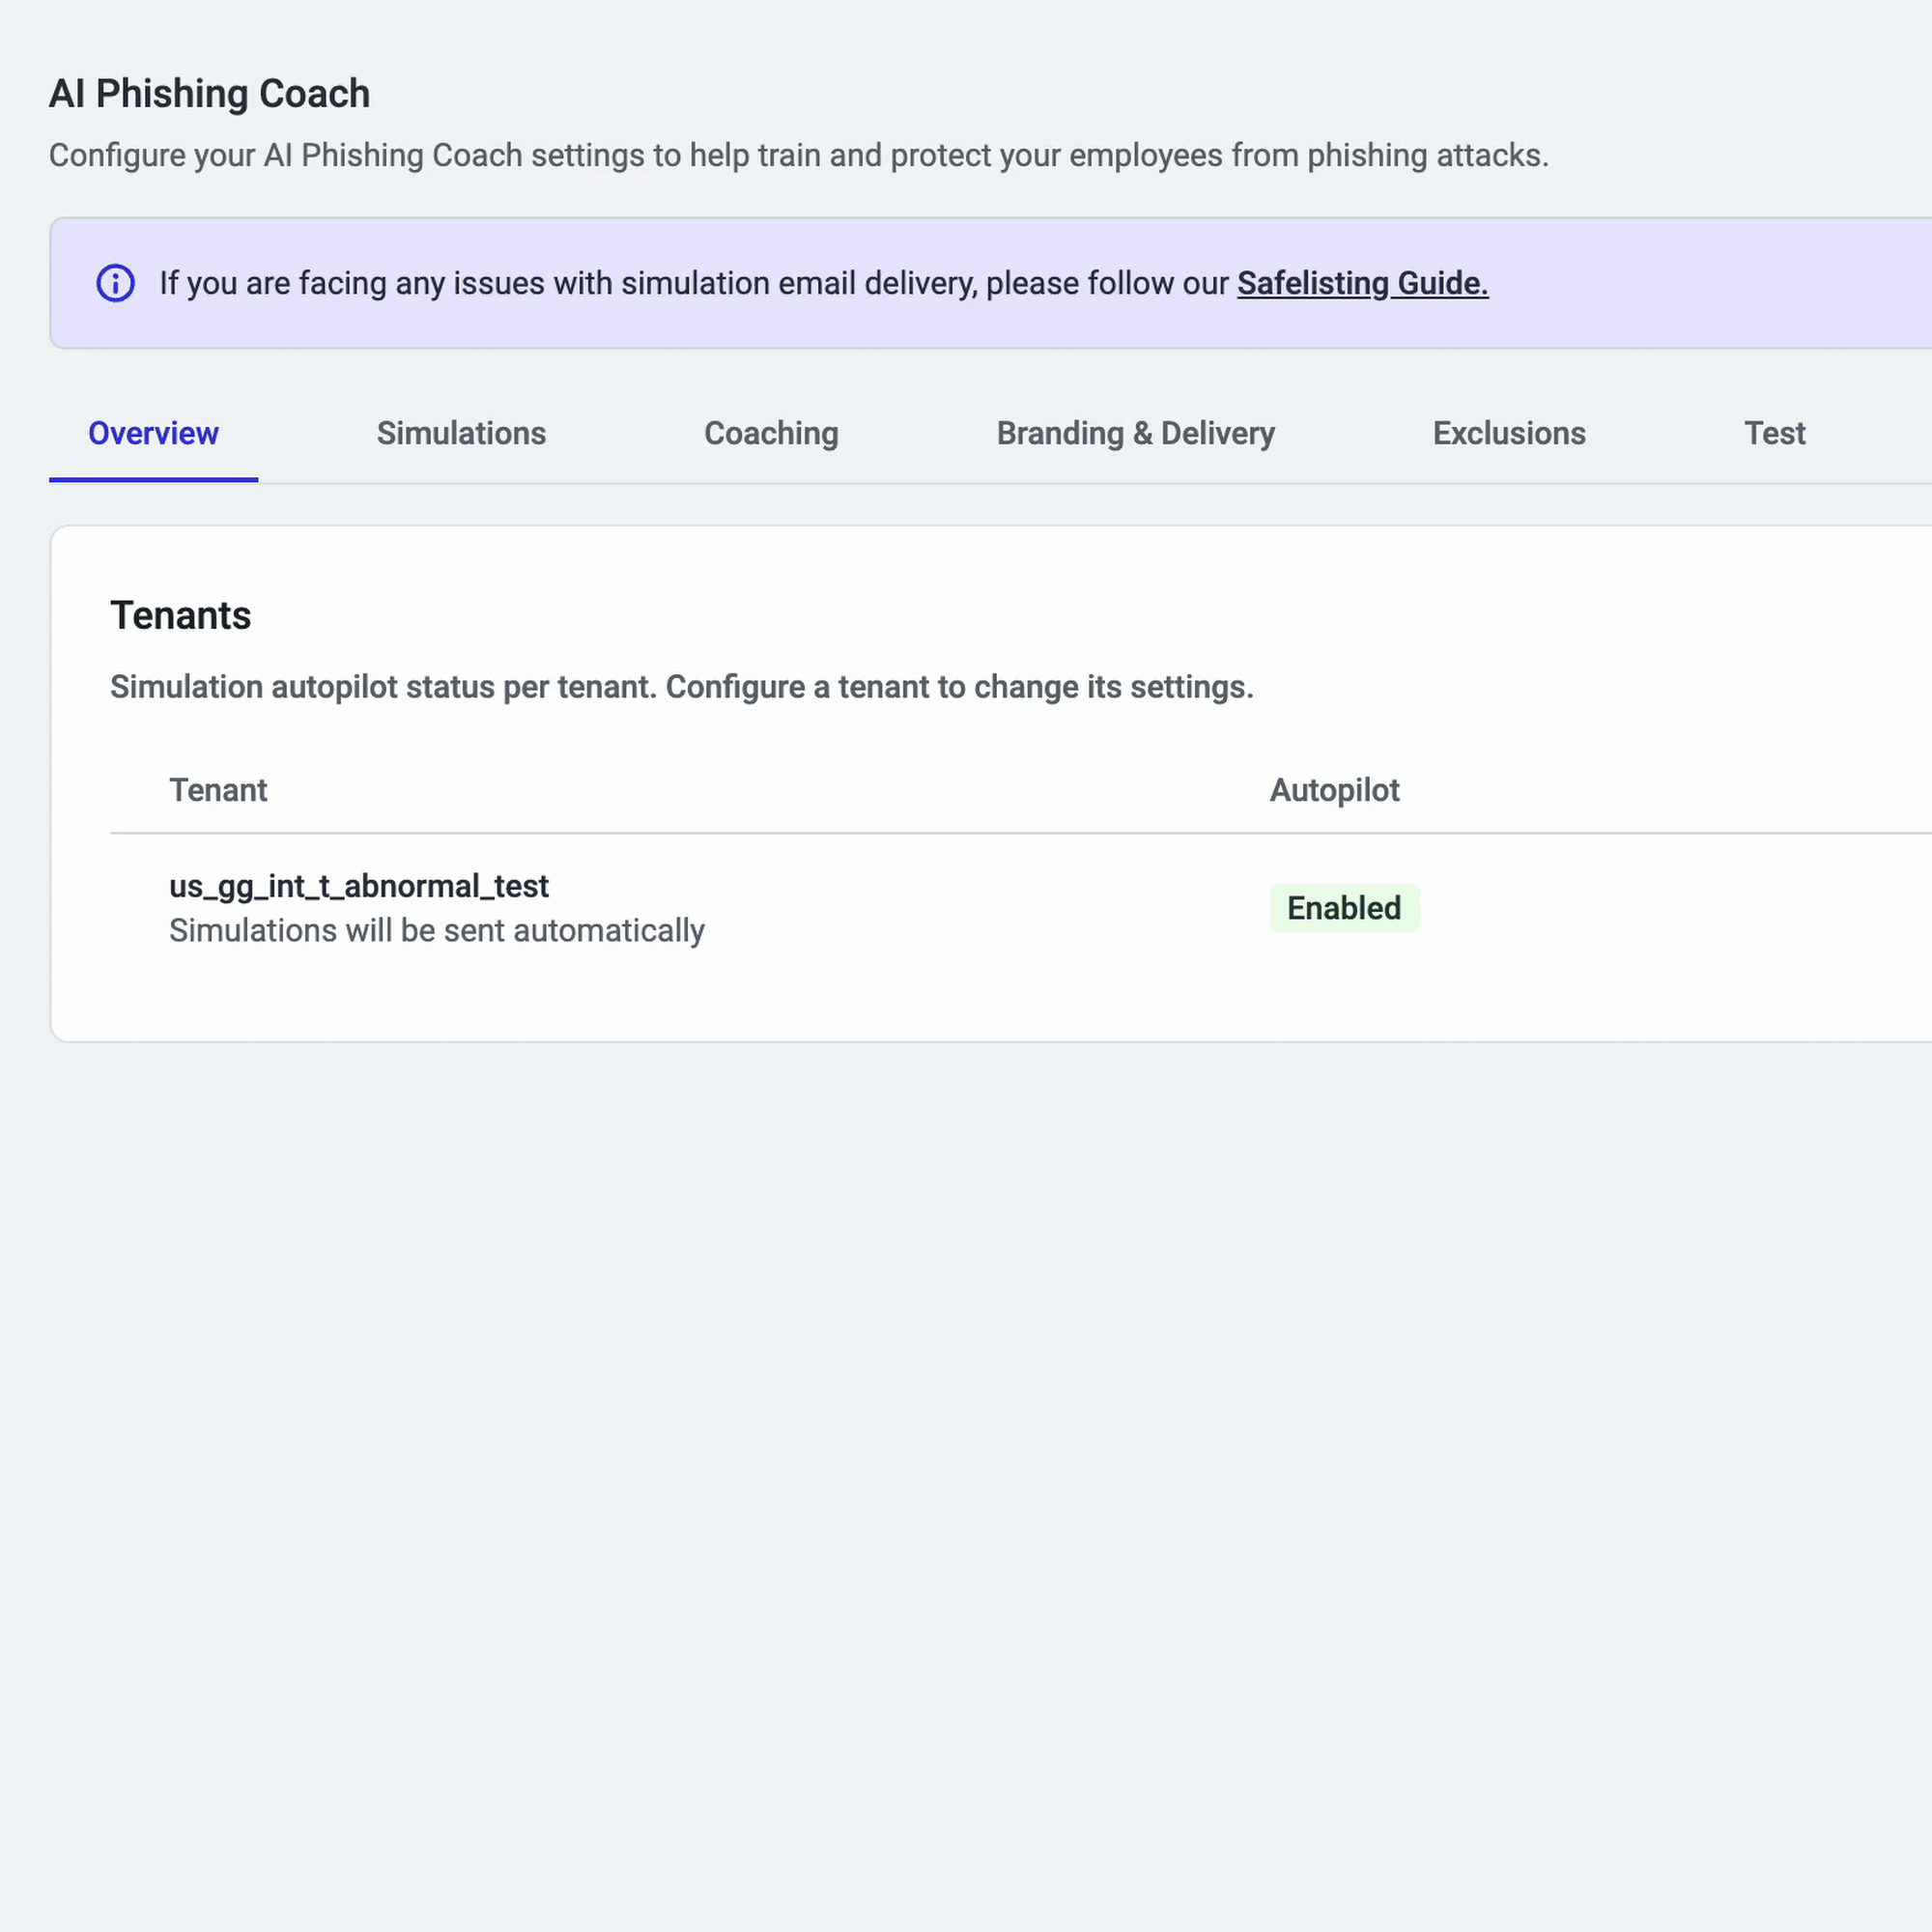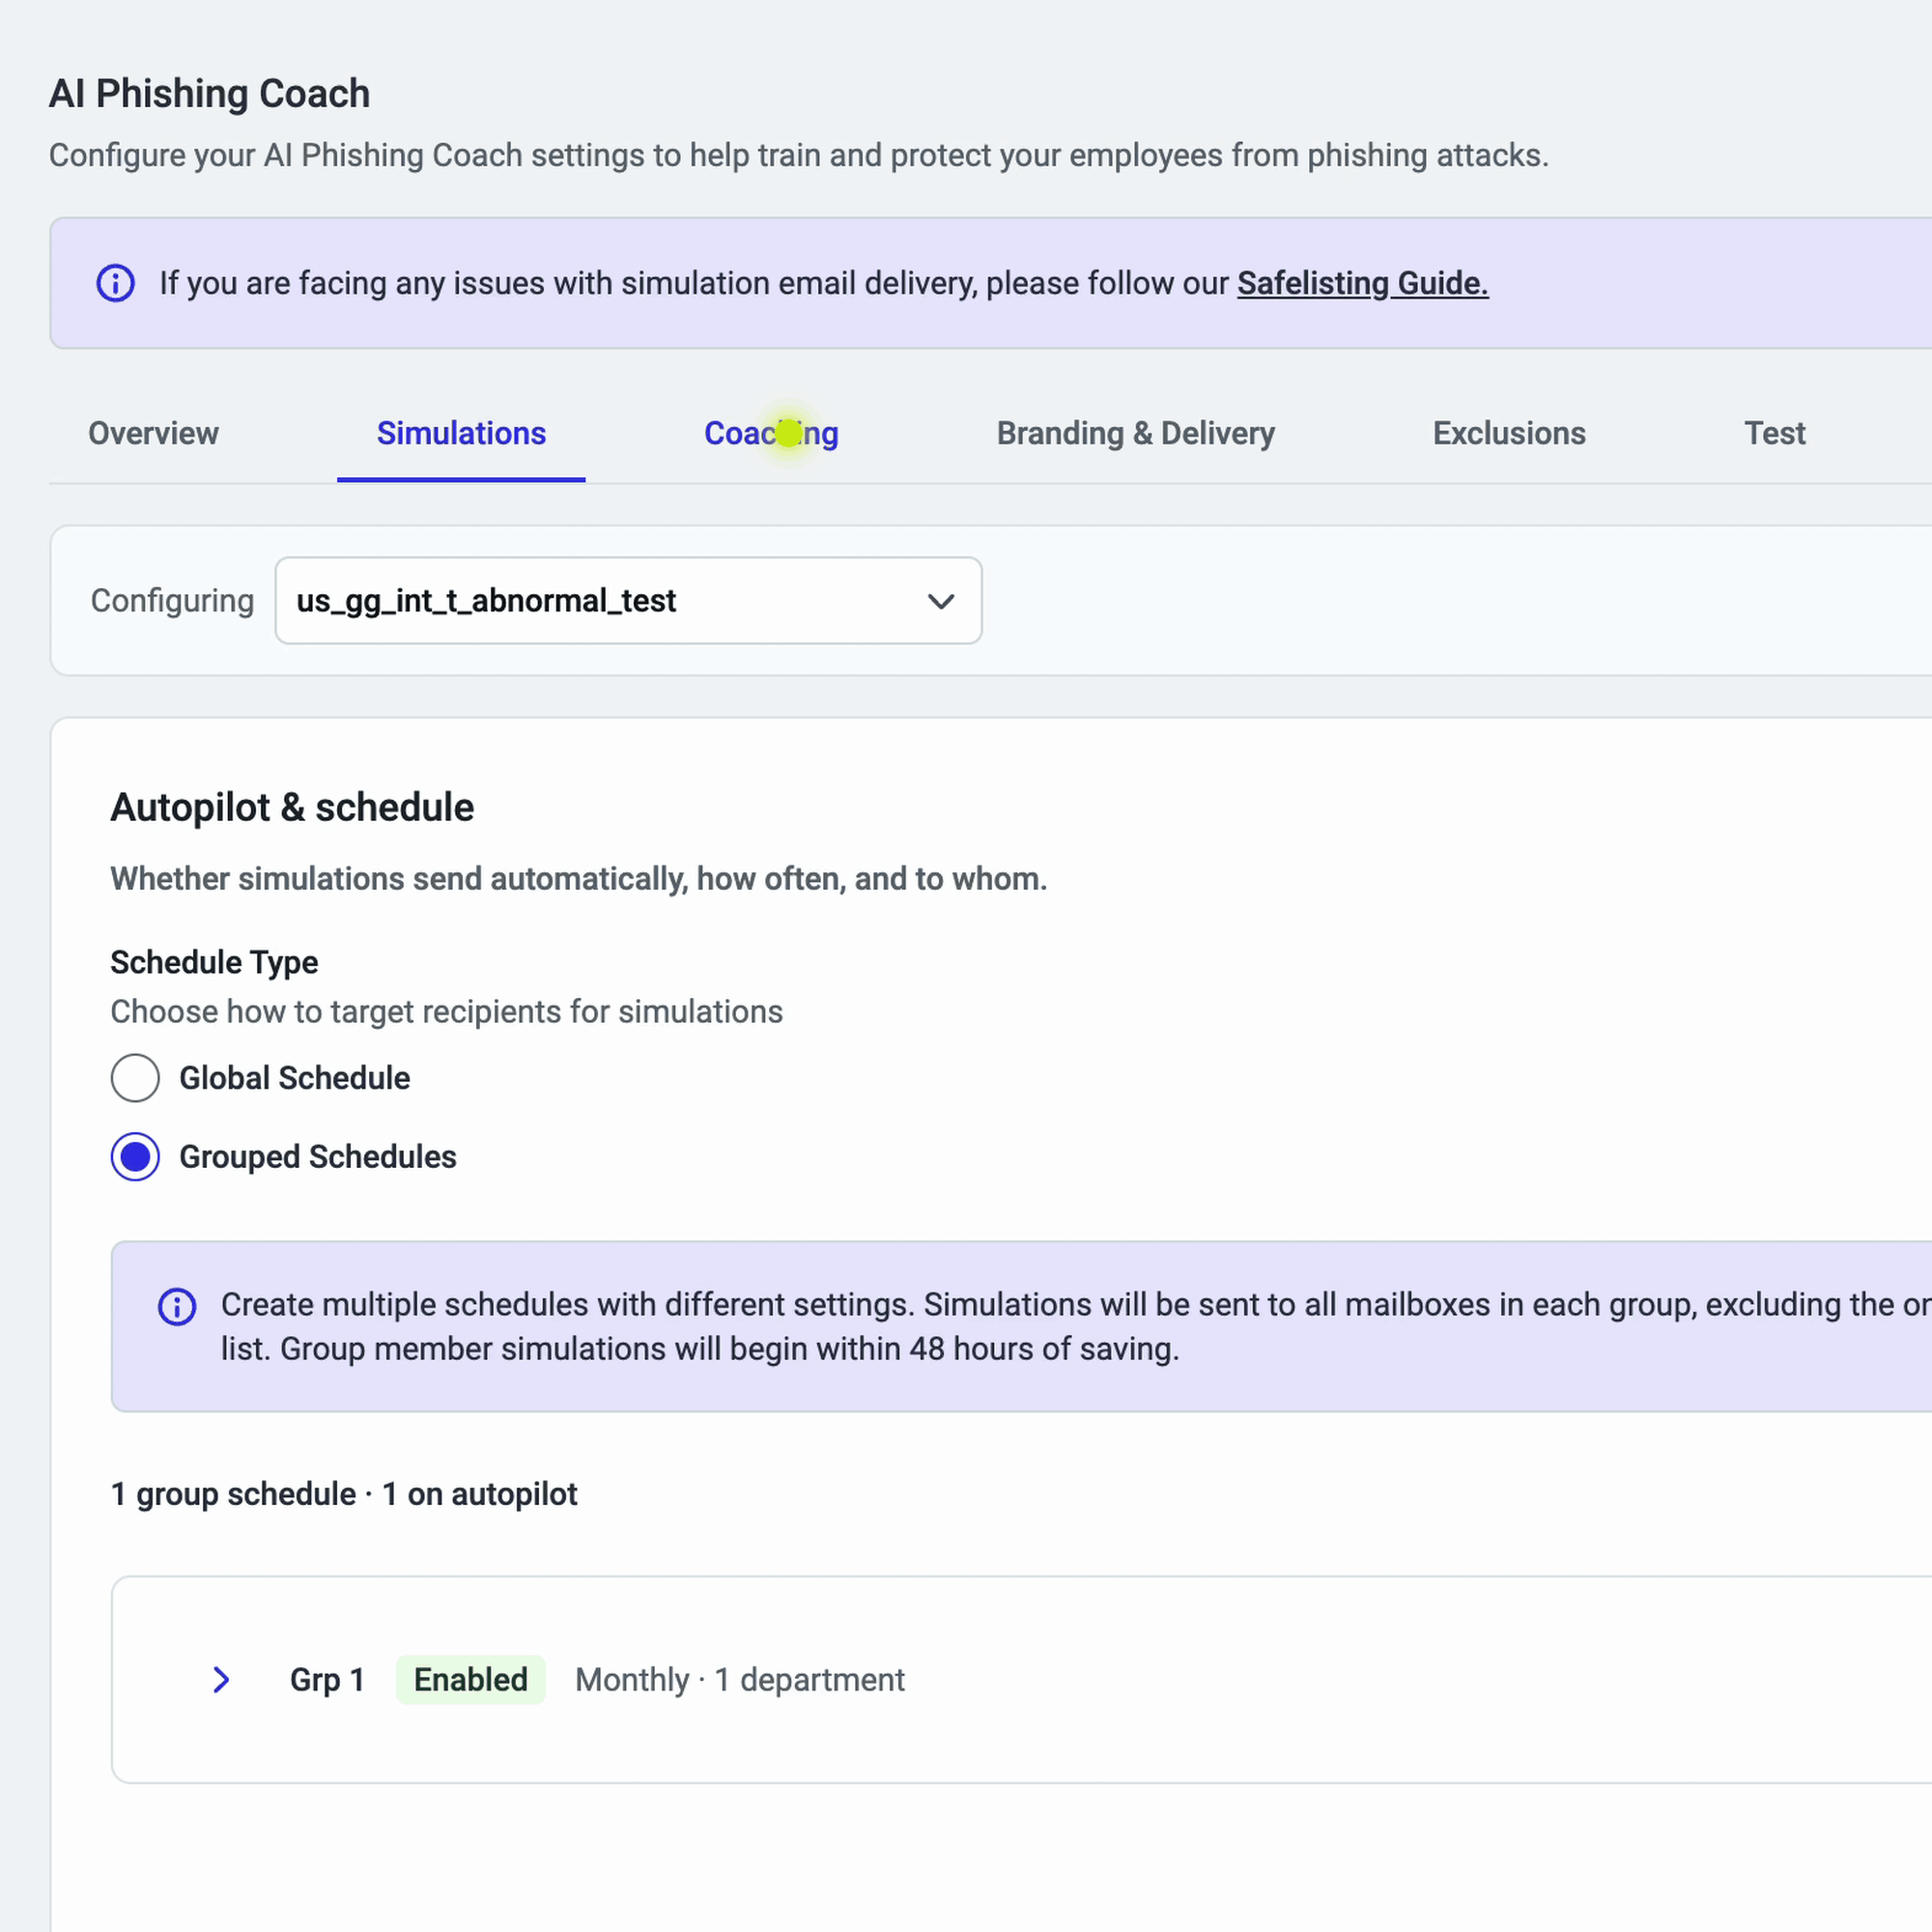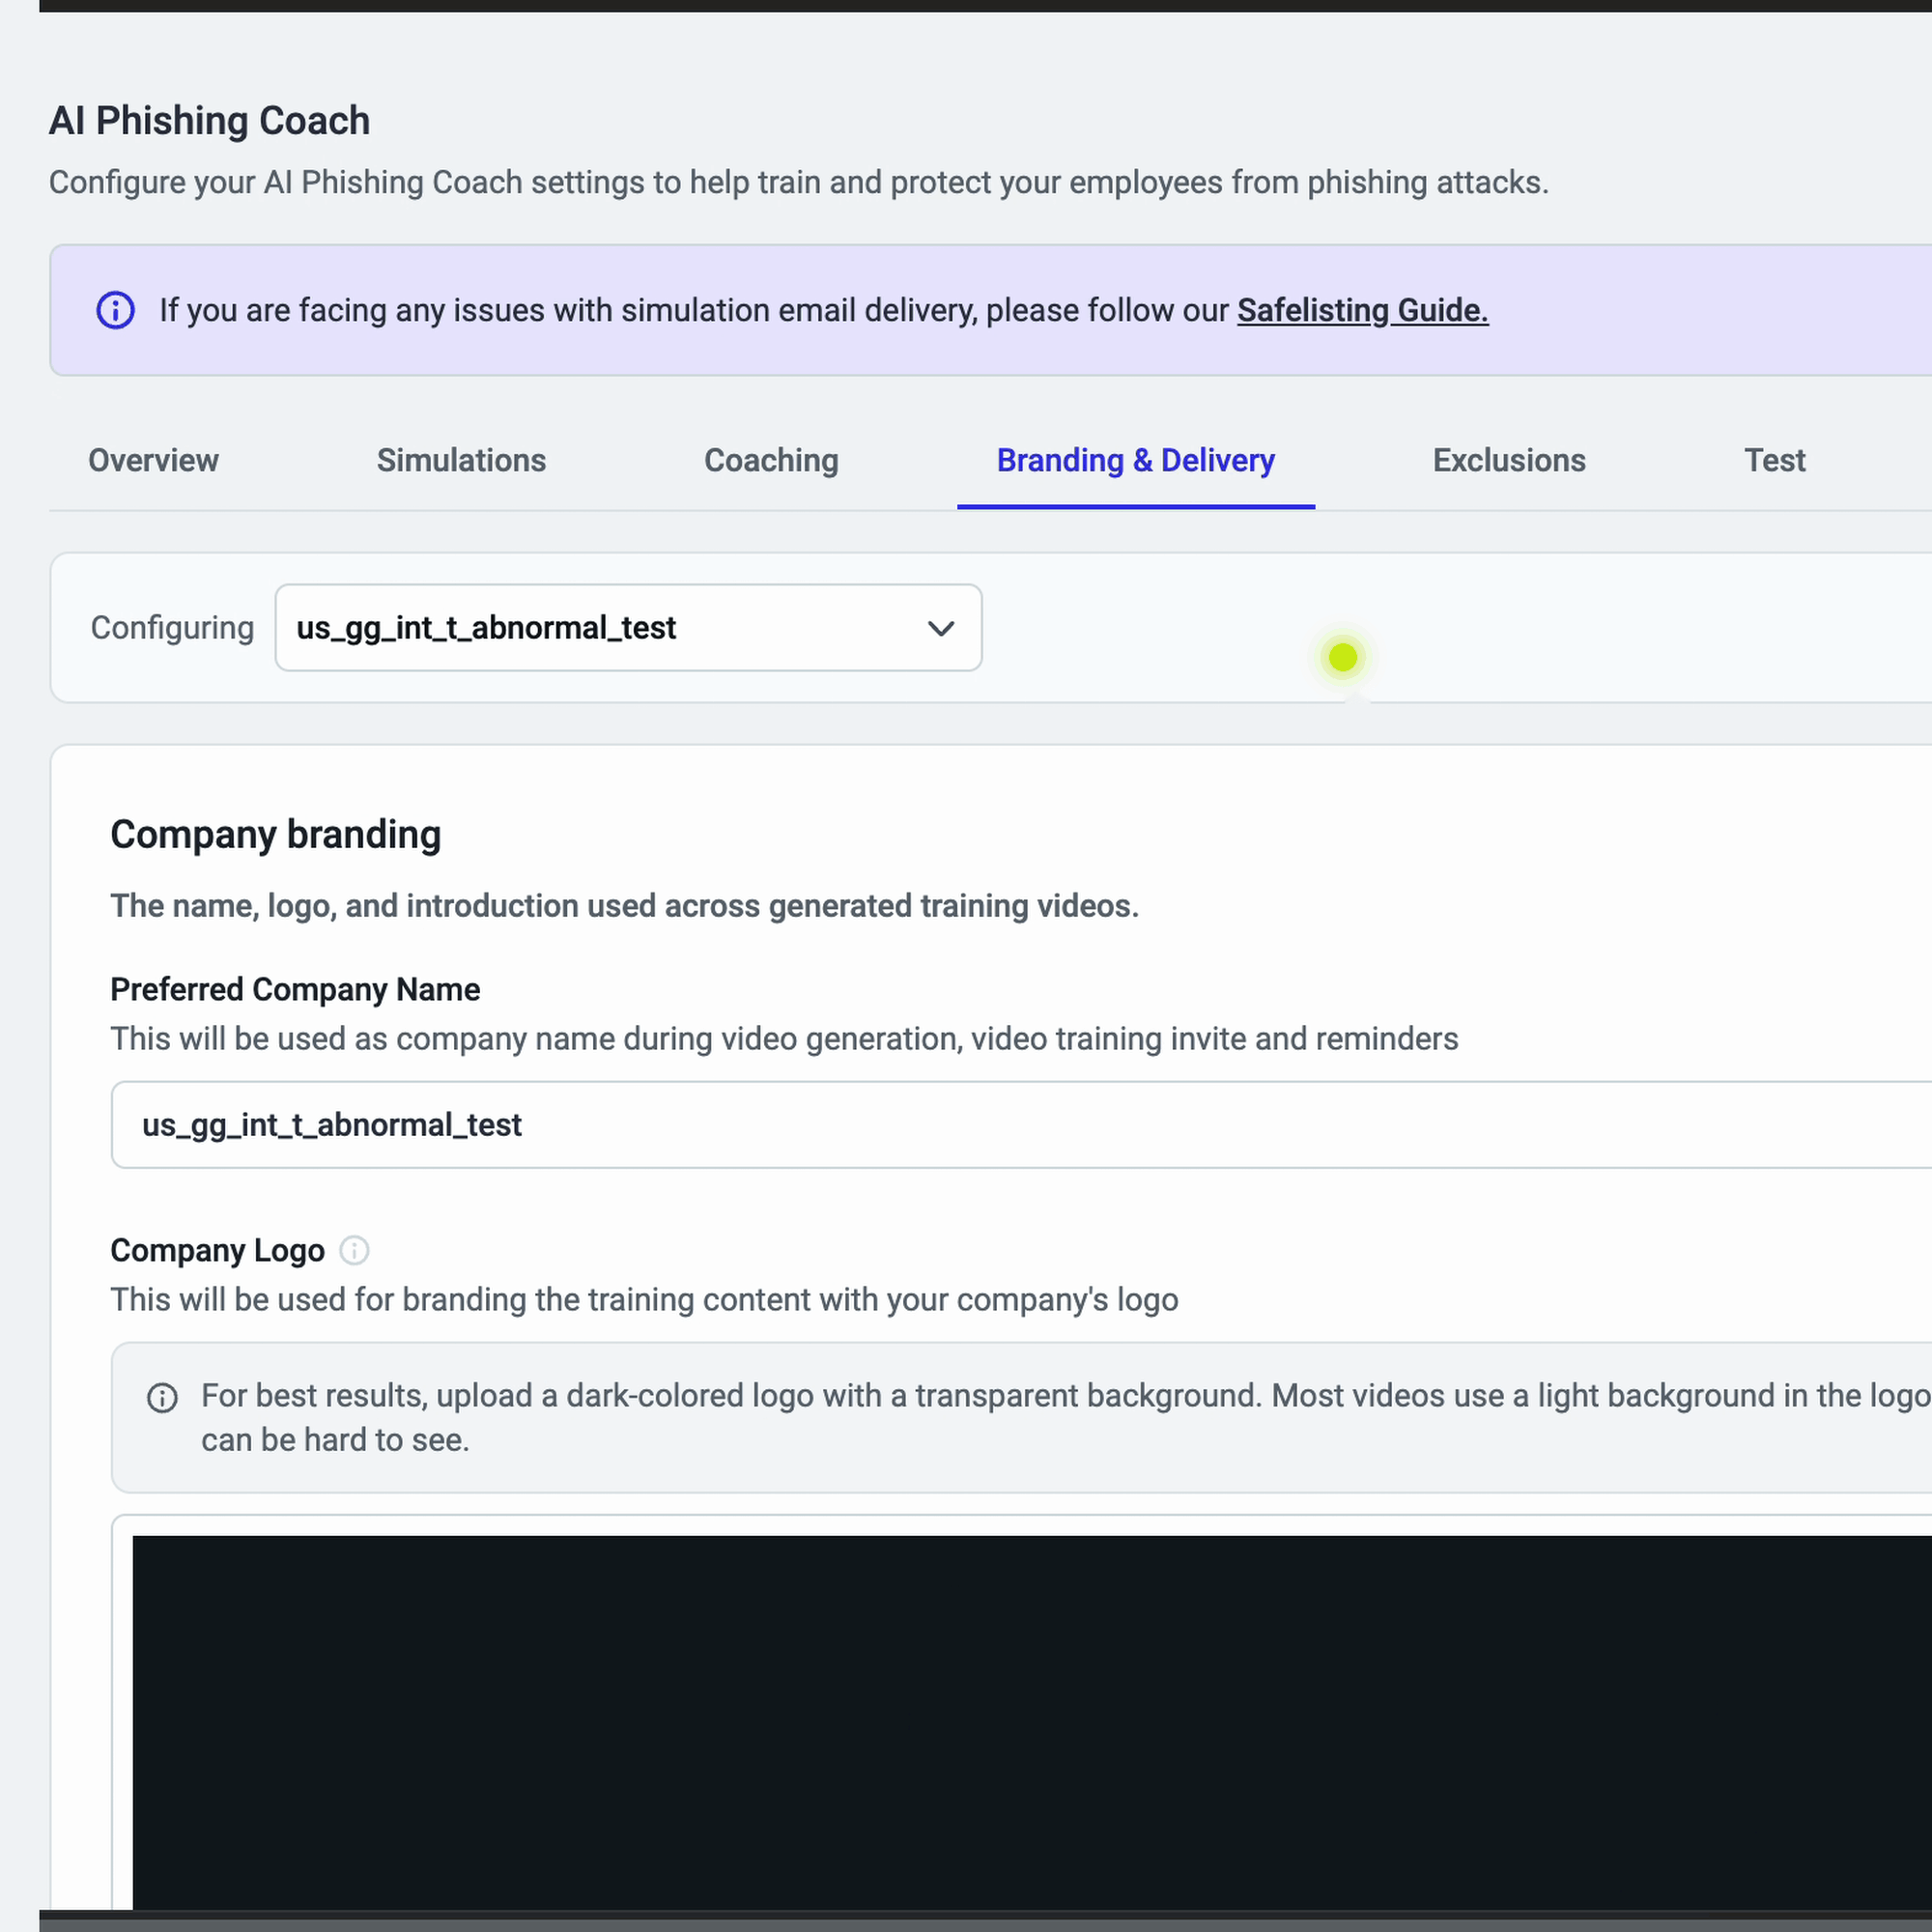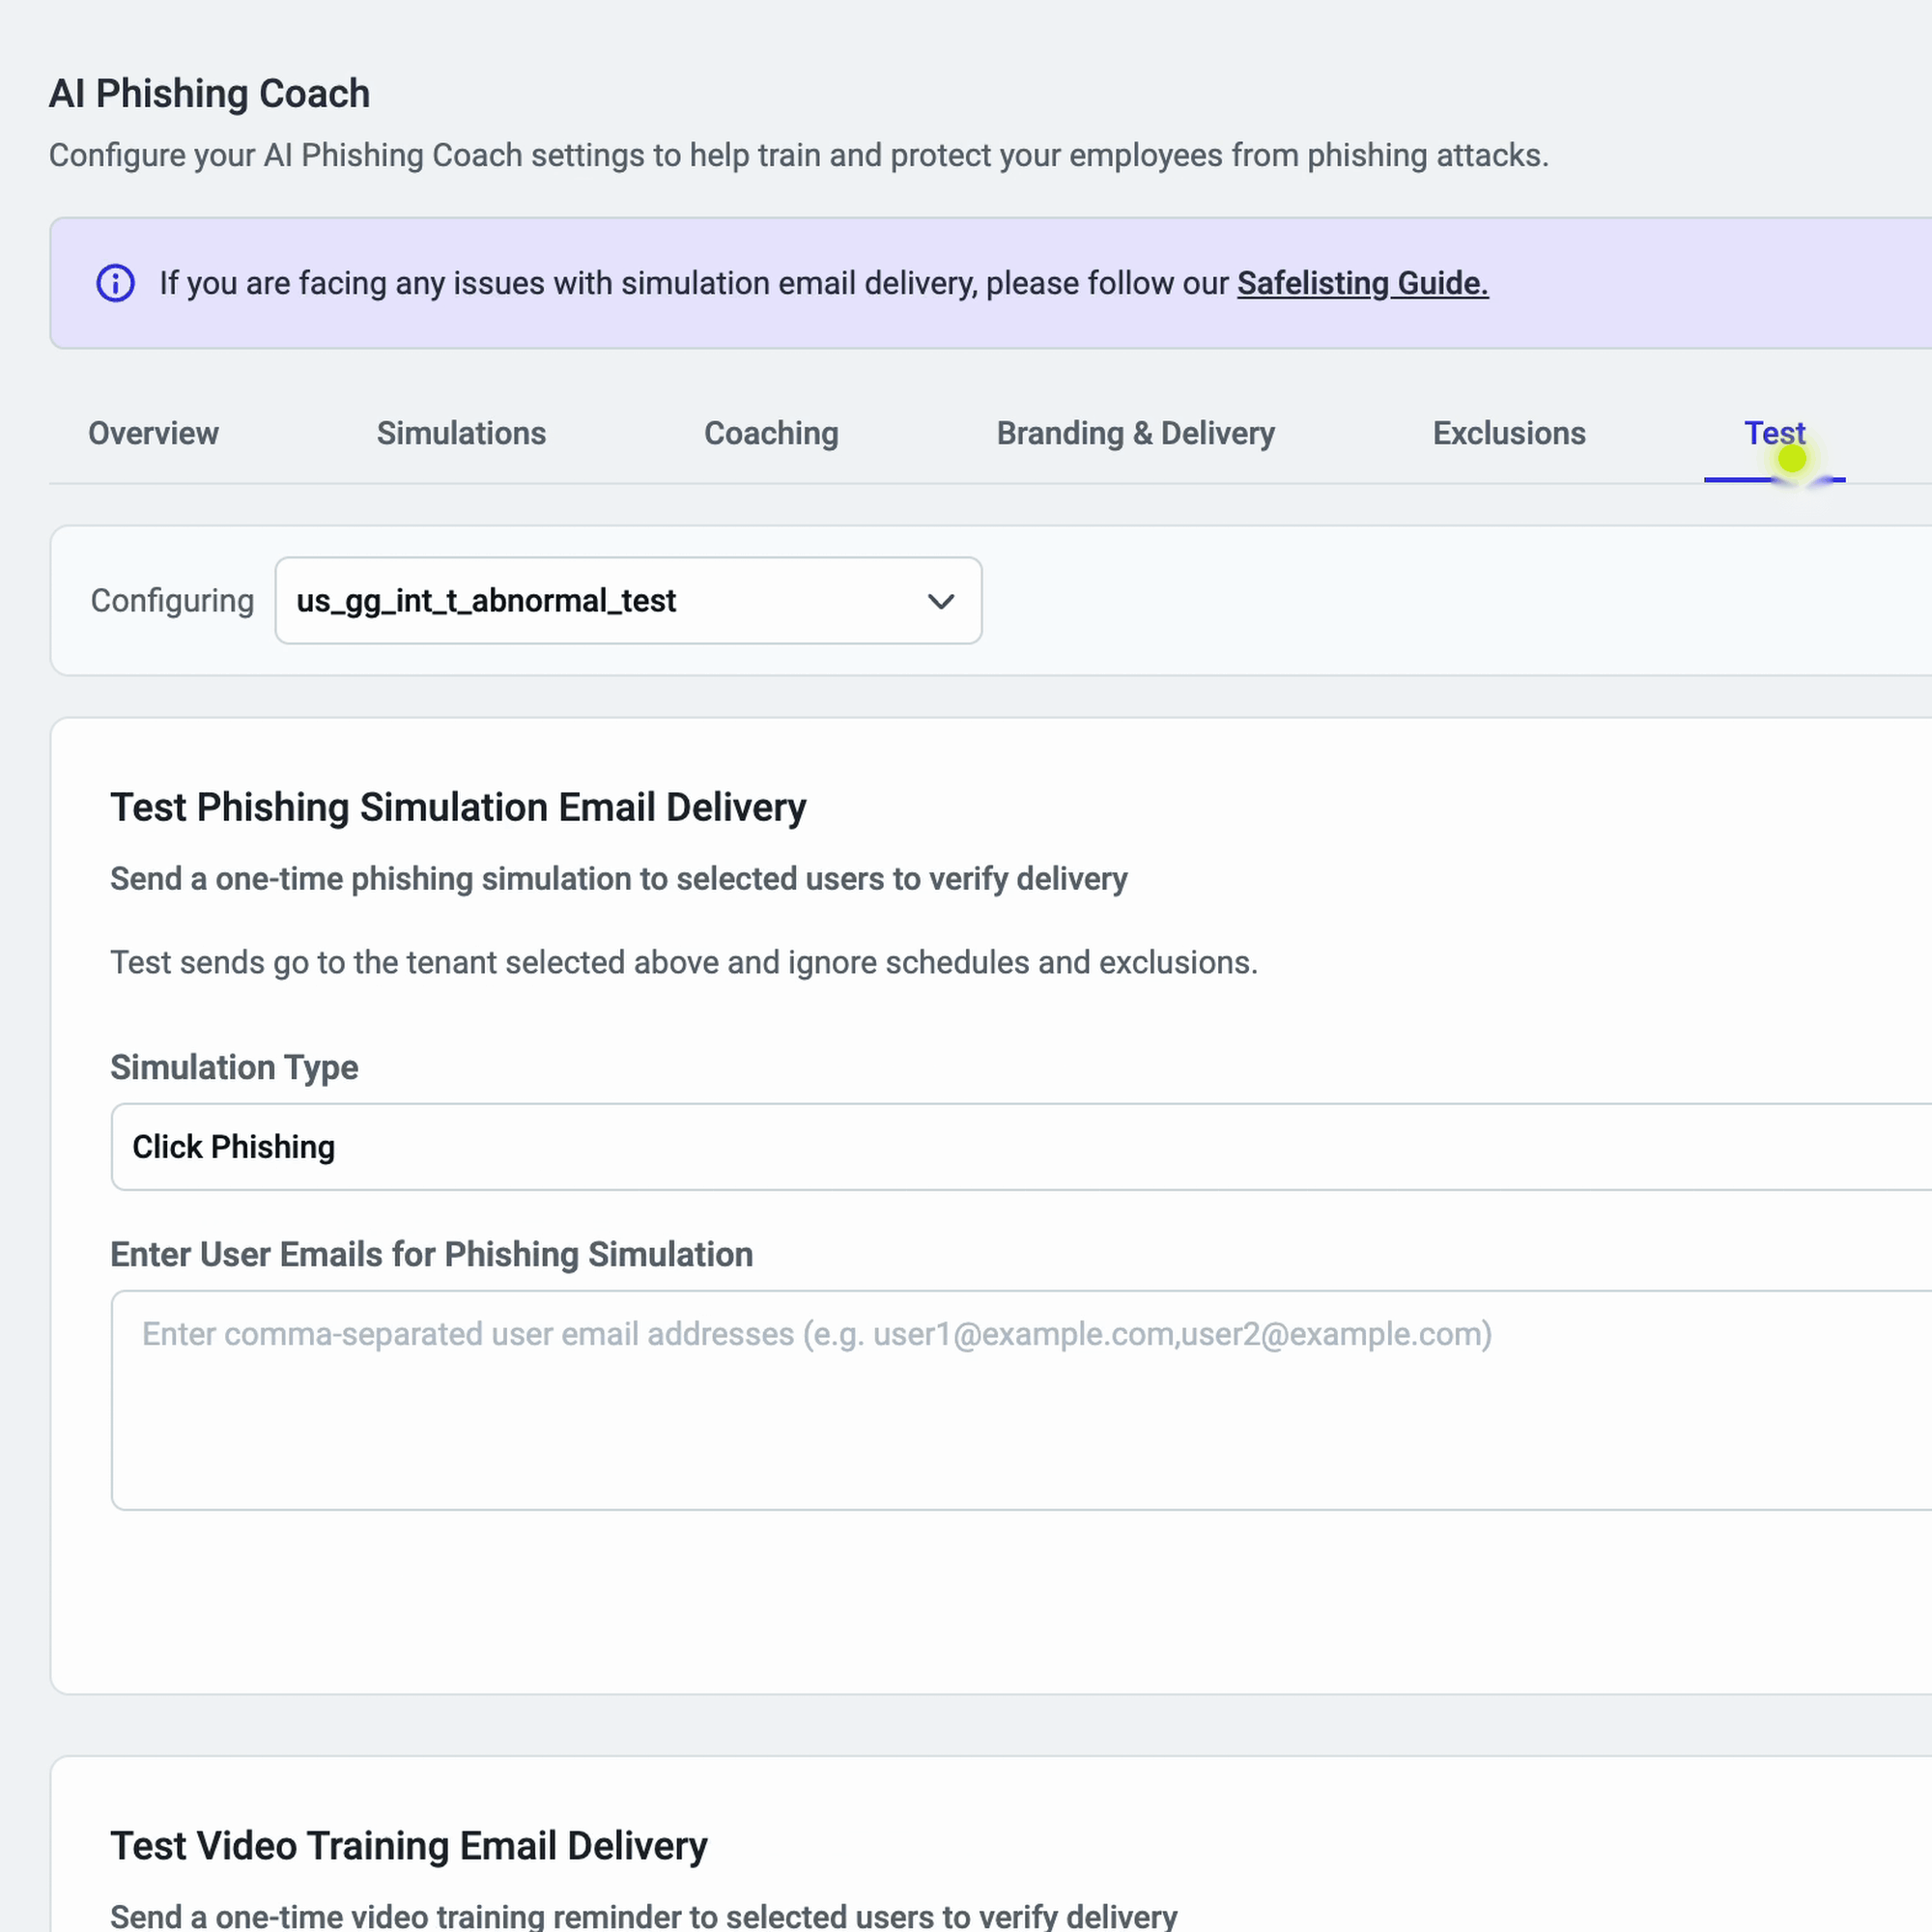
The AI Phishing Coach Settings page is now simpler to navigate, with every control grouped into six tabs by topic. Instead of clicking through a tenant table and nested drawers, admins start on an Overview of every tenant’s autopilot status and go straight to Simulations, Coaching, Branding & Delivery, Exclusions, or Test. Every setting is still there, at most two clicks away, with saved configurations unchanged.
With this release:
Settings are grouped by topic, starting with an Overview of every tenant’s autopilot status
- Tenant Level / Account Level labels show what each change affects
- One Save covers edits across every tab, with the option to discard them
Setting up and fine-tuning AI Phishing Coach has never been easier, especially for organizations managing multiple tenants.
- 26 oct 2026PlataformaNueva funcionalidad
Segmented SaaS: Separate Abnormal Tenants on One Email Tenant
Segmented SaaS is built for organizations whose business units, subsidiaries, regions, or agencies share one email tenant but need to be managed separately. Each segmented tenant has its own admins, views, alerts, and data, giving these organizations a clear path to meeting business and compliance requirements for separation without running multiple cloud email tenants.
With Segmented SaaS:
Create a separate Abnormal tenant for each group, with users assigned by email domain, directory group, or a list of user principal names
Give each tenant its own admins, so every team sees only its own users, alerts, and data
Keep one integration across every segmented tenant, with nothing new to authorize
Segmented SaaS lets security teams align Abnormal with how their organization is structured and governed, while keeping a single email tenant to manage.
Semana del 19 oct 2026
- 23 oct 2026DetectionMejora
Esta semana en detección
Weekly Detection Enhancements - Week of October 23
Improved detection of malicious links by factoring URL verdicts into message scoring, with new coverage for Google Sites-hosted attacks
Launched a visual detection model that catches brand-impersonation attacks hidden in email screenshots and other image-based content
Semana del 12 oct 2026
- 16 oct 2026DetectionMejora
Esta semana en detección
Weekly Detection Enhancements - Week of October 16
Improved graymail classification of promotional messages disguised as replies, distinguishing them from genuine conversations
- 13 oct 2026Security Posture ManagementMejora
CIS Microsoft 365 v7.0.0 Support in Security Posture Management
Security Posture Management now checks your Microsoft 365 configuration against the latest CIS Microsoft 365 Foundations Benchmark, v7.0.0.
As Microsoft 365 changes, CIS revises its benchmark: it adds controls, rewrites others and retires ones that no longer apply. This release brings SPM’s checks up to v7.0.0 and labels every change. Security teams can see which findings are new, which have refreshed guidance and which checks are going away.
With this release:
- 28 new checks based on the latest CIS guidance, marked NEW
- 121 existing checks moved to v7.0.0. The 47 with refreshed guidance are marked UPDATED
- 14 checks that CIS withdrew are marked DEPRECATED and will be removed in 30 days
- A v7 filter on the Evaluations page lets you review the new benchmark on its own
Teams that report against CIS can trust that SPM results match the current benchmark, without remapping controls by hand. The tags also make it easier to explain changes in posture results to auditors and leadership.
Read More
Semana del 5 oct 2026
- 9 oct 2026DetectionMejora
Esta semana en detección
Weekly Detection Enhancements - Week of October 9
Strengthened detection of emails from newly registered domains, expanding coverage of live domain-age and registration signals
- 9 oct 2026AI Phishing CoachMejora
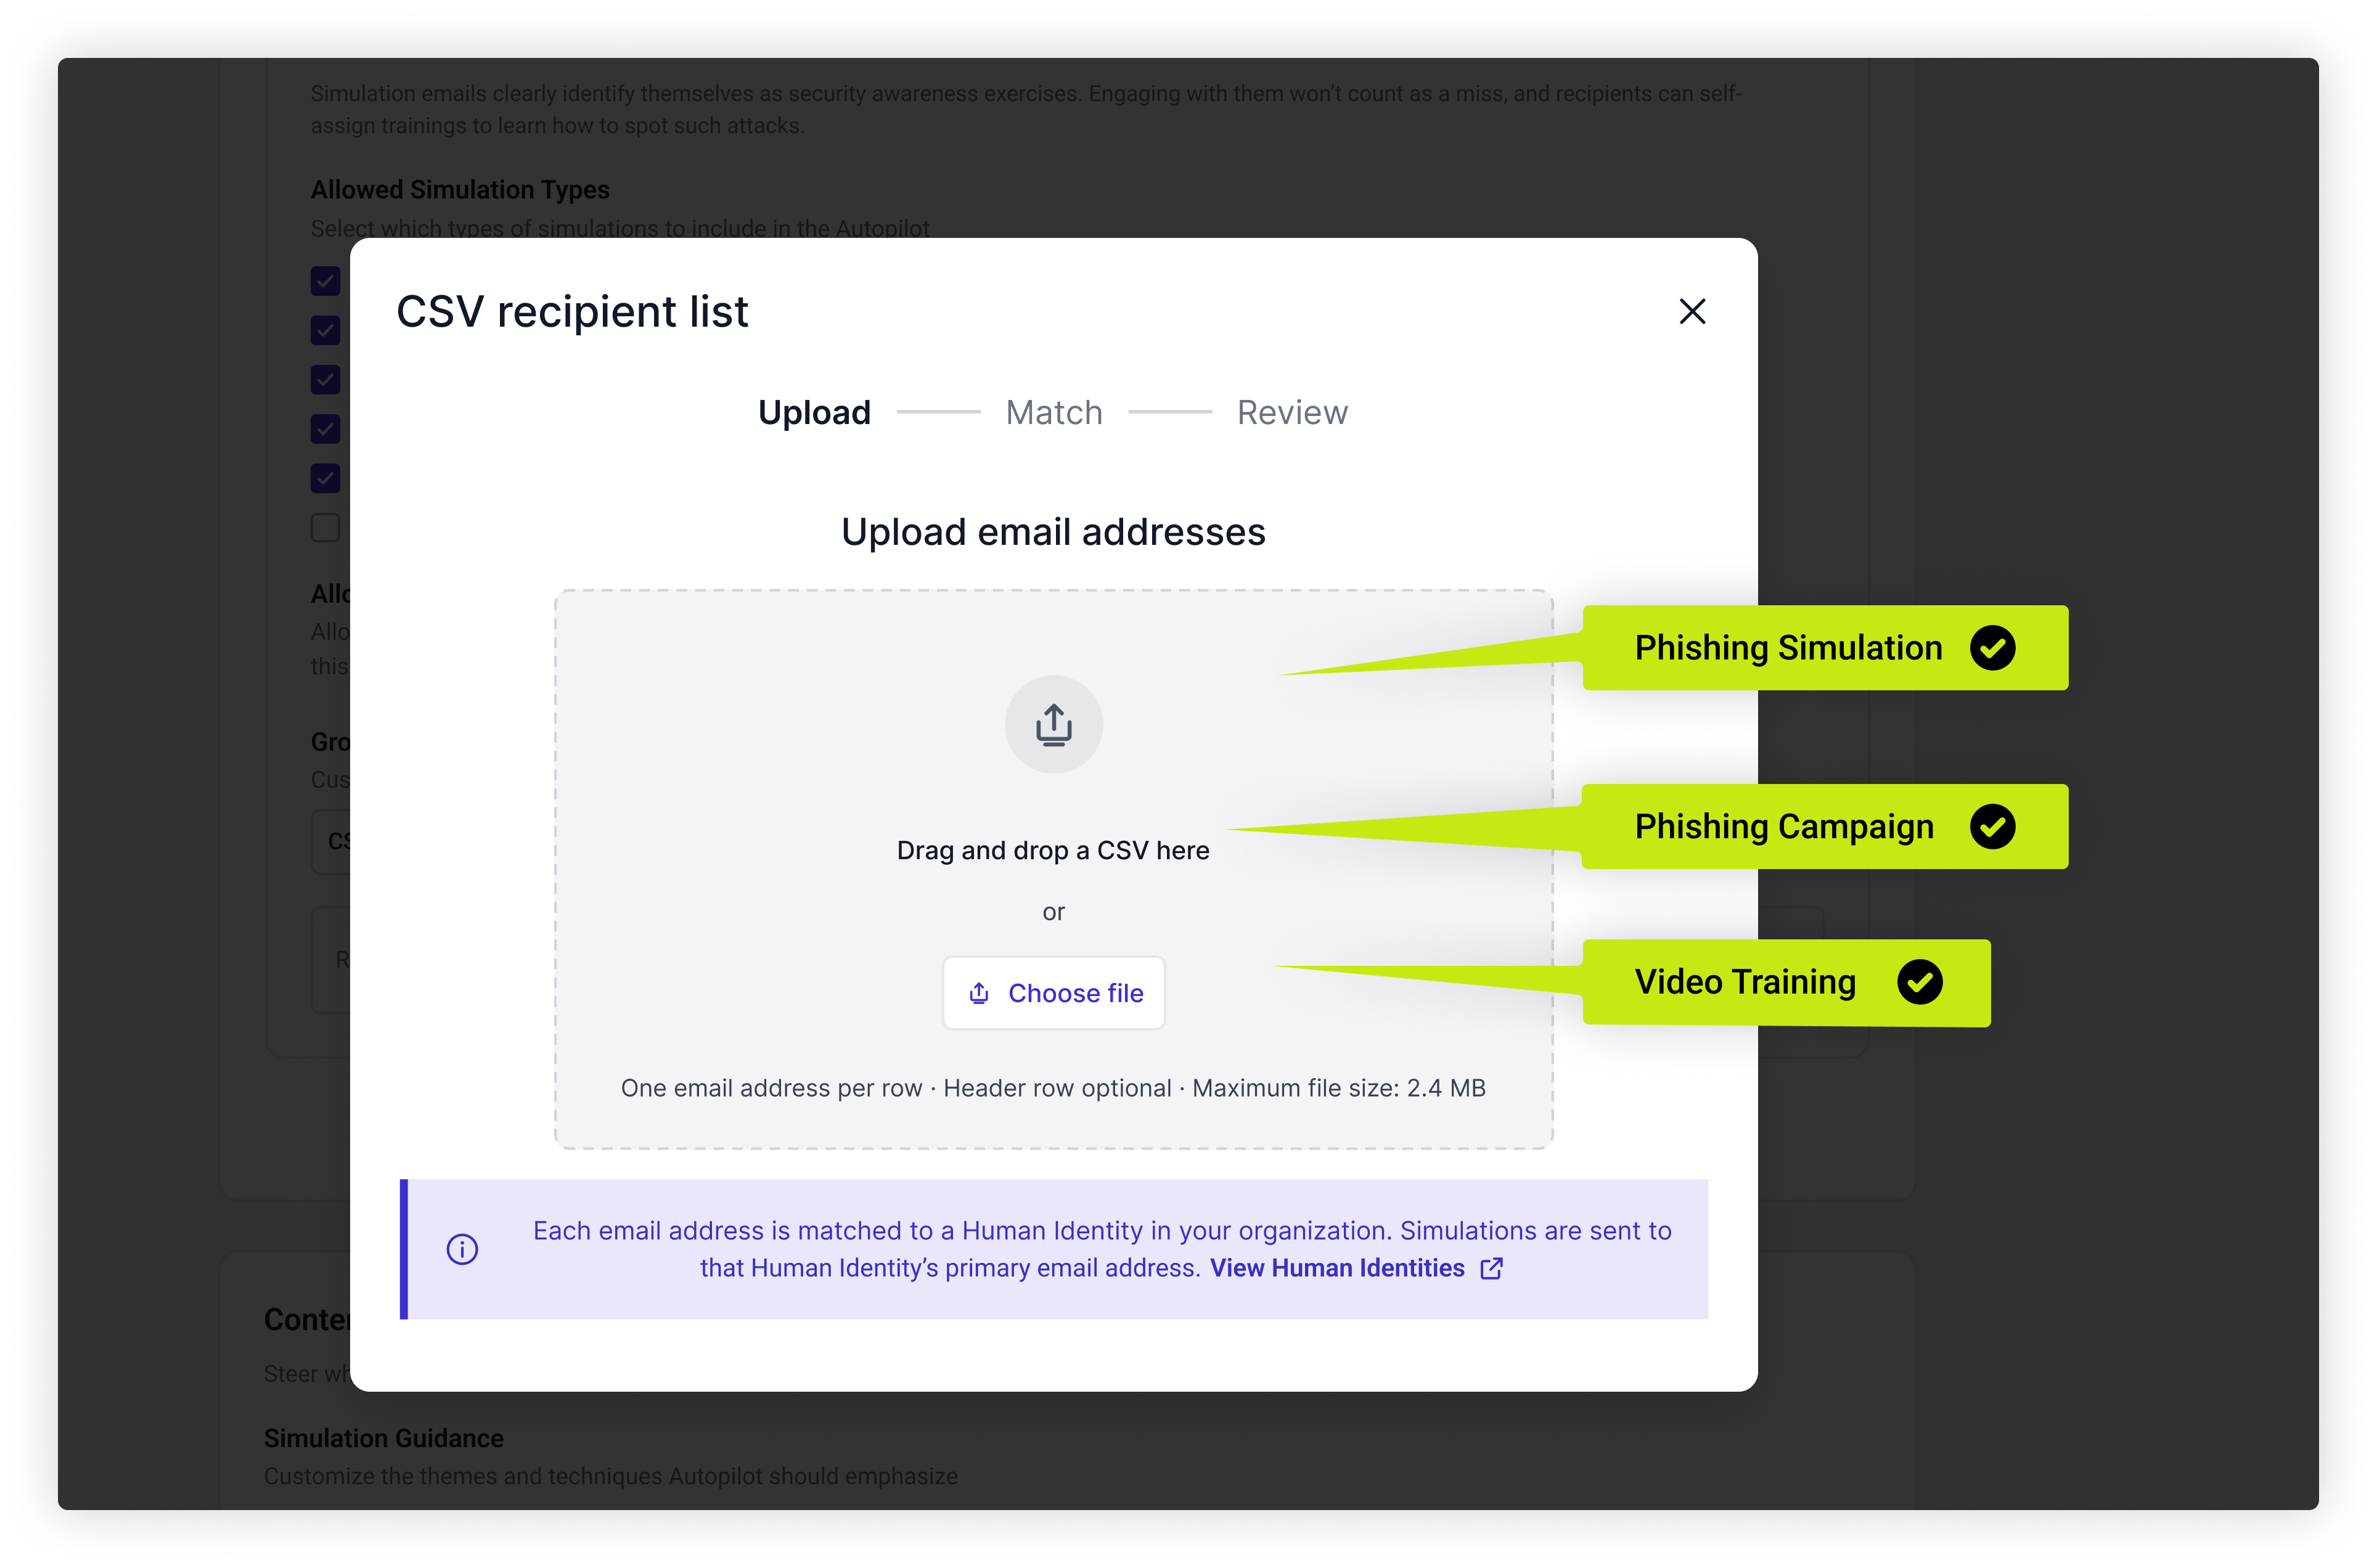
Bring Your Own CSV
Not every directory reflects how a company is actually organized. Now admins can upload their own list of recipients via CSV instead of relying on Departments or Entra and Google Groups, and review exactly who’s included before anything goes out.
With this release:
Upload a CSV to simulation schedules, one-off campaigns, or video training assignments
Review matched, unmatched, and redirected addresses before applying the list
Edit and re-upload the file anytime to keep membership current (one email per row, up to 2.4 MB)
Security teams can now reach every subsidiary, brand, and pilot group with the right simulations and training, no matter how their directory is structured.
- 8 oct 2026PlataformaNueva funcionalidad
New Threats API Message Endpoints
Abnormal now offers two new REST API endpoints that provide direct access to threat message data: one retrieves threat message data in bulk, and the other retrieves full details for a single message.
With this Release:
- Retrieve threat messages in bulk over a selected timeframe with core metadata, pagination, and the same filters available in the Threat Log.
- Retrieve full details for one message, including attachment analysis, insights, and URLs.
Semana del 28 sept 2026
- 2 oct 2026DetectionMejora
Esta semana en detección
Weekly Detection Enhancements - Week of October 2
Enhanced detection of lateral phishing from compromised senders, strengthening protection for internal-to-internal messages
- 30 sept 2026AI Security MailboxNueva funcionalidad
AI Detection Engineer: A Faster, More Visible Response to Every Report
AI Detection Engineer acts as an extension of your SOC: when a report in Detection 360 or AI Security Mailbox is confirmed a misjudgment, AIDEN investigates it the way an analyst would, builds a sophisticated, customer-specific detector, tests it against your own traffic, and deploys it once it clears Abnormal's efficacy bar, no rule-writing required.
With this release:
See AIDEN’s fast, visible response to confirmed misjudgments reported via Detection 360 and AI Security Mailbox in one unified dashboard
Get faster turnaround from report to live fix, as AIDEN investigates, builds, tests, and deploys automatically
Track every deployed detector with full traceability to every message caught and false positive suppressed
AI Detection Engineer turns reports into faster, fully traceable responses, no rule-writing, no waiting. It's live today for all US and EU commercial customers, no configuration required.
- 30 sept 2026AI Phishing CoachNueva funcionalidad
Executive-Ready PDF Report
AI Phishing Coach's new Executive Report turns your training program results into a leadership-ready PDF in one click. The branded report covers program performance, where risk concentrates, and which employees to coach or recognize, with AI-generated analysis alongside key charts.
With this release:
Share results with leadership using Export Executive Report on the Executive Dashboard or the Reports page
Apply any date range or filters to show a broad or targeted view
Find past and new reports in Recent Reports on the Reports page
The Executive PDF Report turns program data into a story leaders can act on, with no screenshots and no manual prep. It's live today for all AI Phishing Coach customers.