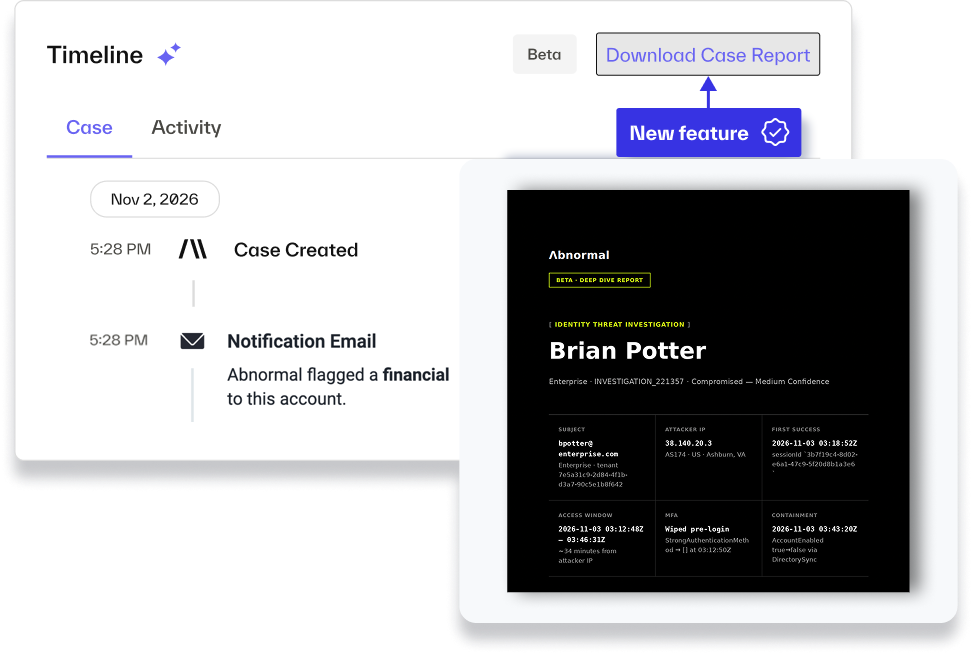
Identity Threat Protection now includes an AI agent that investigates every case after detection. It reviews the user’s recent activity, including interactive and non-interactive sign-ins, suspicious email, and admin changes. It pulls signals the initial detection didn’t weigh and re-evaluates the ones already on the case. When it finds that a low-confidence case looks like a real compromise, it can raise that case to medium confidence.
With this release:
Find compromise activity in signals the initial detection didn’t weigh, such as non-interactive sign-ins, email, and admin activity in one view.
Based on investigation, the AI agent may raise case confidence from low to medium confidence and sends the associated notifications
Understand why a case was raised, with case promotion added to the case timeline and a plain-language reason drawn from the agent’s investigation
Review the agent’s verdict, key evidence, timeline, and primary indicators of compromise (IOCs) in one report, without rebuilding the investigation yourself
Download the report as a PDF from the case view to share with your team or attach to an email
The AI investigation agent helps analysts focus on the cases most likely to be real and shows its work. If you’ve configured auto-remediation for medium-confidence cases, promoted cases follow that configuration.