Principais insights
User-reported phishing can strengthen enterprise email defense or overwhelm your security operations center (SOC). Employees flag suspicious emails each day, and most security teams struggle to keep pace with the resulting queue. AI automates triage and turns employee reports into threat intelligence, helping determine whether a security incident response stays contained or grows into a breach.
Getting the intake, triage, and feedback workflow right is what decides which of those outcomes an organization actually gets. This guide explains how traditional reporting workflows break down at scale, where AI can automate triage and campaign remediation, and which metrics show whether the program is reducing risk.
This article draws from insights shared during an Abnormal Innovate session about transforming cybersecurity with AI. Watch the full recording to see how leading security teams are transforming their phishing response workflows.
Key Takeaways
Manual user-reported phishing investigations can consume substantial analyst time.
AI-powered triage can help security teams reclaim operational capacity.
Automated campaign correlation supports organization-wide remediation.
Contextual responses can turn phishing reports into personalized training moments.
Clear metrics help security leaders measure risk reduction and workflow efficiency.
What Is User-Reported Phishing?
User-reported phishing is the process by which employees identify suspected malicious emails and submit them to their security team for investigation. It is the human layer of a detection strategy: employees spotting something that feels wrong and flagging it for review, even when they cannot articulate exactly what tipped them off.
Common submission methods include:
Phishing Report Buttons: Dedicated phishing report buttons embedded in email clients let employees submit suspicious messages.
Training Buttons: Security awareness training buttons enable reporting through established training workflows.
Native Reporting: Microsoft native reporting lets employees submit messages through familiar email controls.
Security Mailboxes: Custom security mailboxes provide a dedicated destination for suspected malicious emails.
Easy submission methods tend to generate more reports and support several benefits:
Early Detection: Employees act as distributed sensors across the business, catching attacks that automated systems might miss, particularly social engineering attempts that lack obvious indicators of compromise (IOCs) such as a known-bad domain or a flagged attachment.
Business Context: When a sales employee sees an invoice from an unfamiliar address, or a finance team member notices unusual urgency in an urgent payment request, those reports become intelligence the security team can act on.
Threat Intelligence: Organizations that operationalize user-reported emails effectively can turn them into one of their most valuable sources of threat intelligence.
Efficient processes make the difference. Without them, user reports become a bottleneck. With the right systems, they become a force multiplier for your security program.
Why Your Security Team Needs User-Reported Phishing
Employees will encounter novel attacks before automated filters have any signature for them. Their reports are often the first signal that a live campaign has reached the organization
AI has changed how attackers build campaigns. Attackers now craft hyper-personalized messages that mirror legitimate business communications, including generative AI-powered attacks with flawless copy and credential phishing campaigns that often evade traditional detection.
Generic training modules do not prepare employees for messages that reference real projects, mimic familiar contacts, and contain no obvious red flags. These tactics make familiar phishing indicators less useful to employees.
Despite years of security awareness training, standard annual and embedded programs, as commonly deployed, have shown little measurable effect on employees' ability to distinguish phishing from safe emails. A randomized trial of 19,500 UC San Diego Health employees found no significant relationship between recent training and the likelihood of falling for a phishing simulation. The researchers concluded that anti-phishing training, in its current and commonly deployed forms, is unlikely to offer significant practical value in reducing phishing risk.
The detection gap persists for two related reasons:
Reporting Friction: Reporting friction and low confidence often prevent employees from acting on their awareness.
Gateway Coverage: Your email gateway (SEG) targets known threats but may struggle with novel, socially engineered messages. Your employees encounter those novel threats.
A working user-reported phishing program bridges the two and determines whether emerging threats get identified or ignored.
Handled well, user reports give early warning on emerging attack patterns, validate detection accuracy, and build feedback loops that improve employee vigilance. Handled poorly, they waste analyst time on false positives while real threats sit in inboxes.
How Traditional Reporting Workflows Work
The traditional user-reported phishing workflow runs through sequential, largely manual steps.
User Identification: An employee notices something suspicious, such as an unusual sender, an unexpected request, or simply a gut feeling.
Submission: The employee forwards the message to a phishing mailbox or clicks a report button.
Ticket Creation: The report generates a help desk ticket for tracking.
SOC Analyst Triage: The analyst examines individual attributes: sender information, attachments, links, and whether the user opened or clicked anything.
Campaign Search: The analyst searches for similar emails across the environment, since one report often indicates a broader campaign.
Remediation: The security team removes malicious emails from inboxes, assuming users have not already interacted with them.
Resolution: The security team notifies the user and closes the ticket.
Each investigation can consume up to thirty minutes of analyst time. At a sustained volume of submissions, sequential manual review cannot keep up. The math is unforgiving.
Common Challenges with User-Reported Phishing Programs
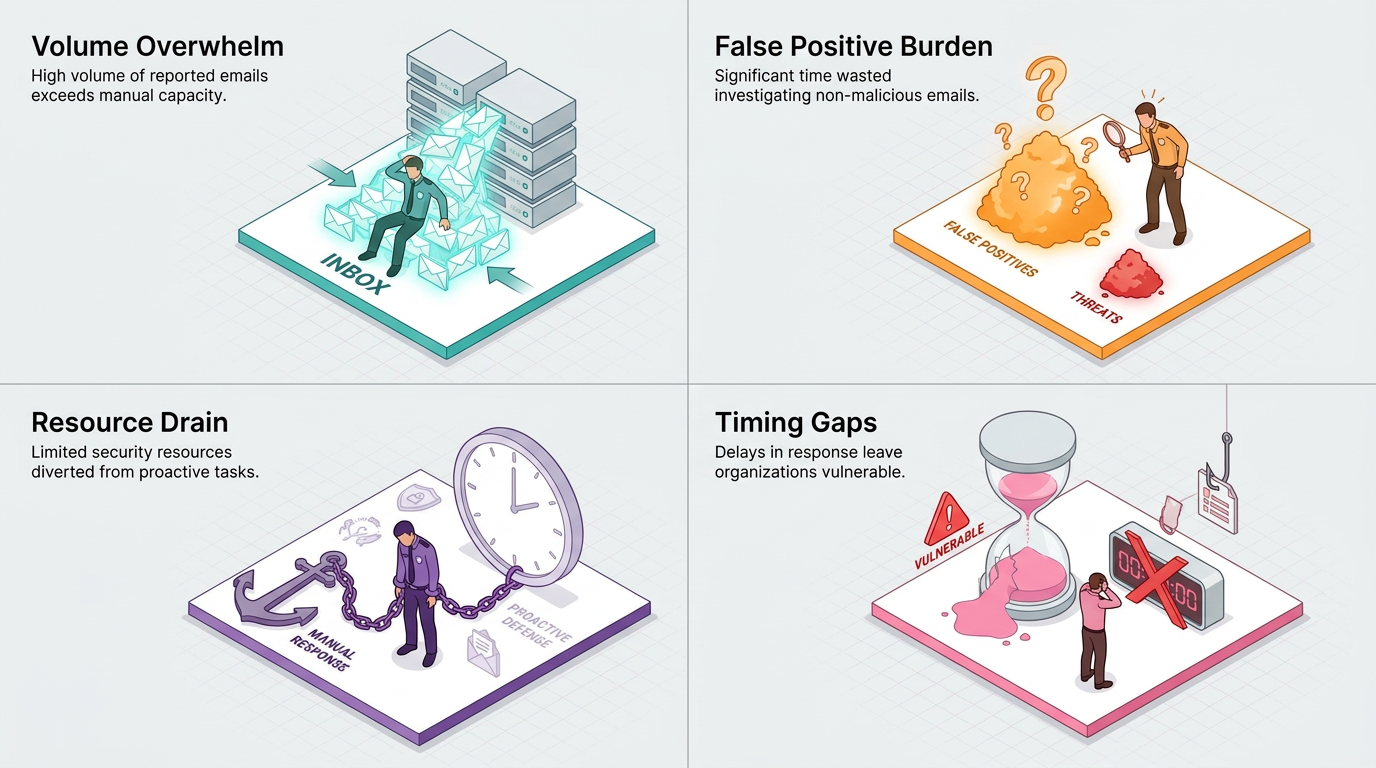
Security teams running manual programs face several compounding problems that erode both response times and analyst morale. The most common ones fall into four categories:
Volume Overwhelm: Teams face an endless queue of user-reported messages, and most are not threats. A research preprint analyzing live enterprise reporting operations found that roughly 88% of user-reported submissions are non-malicious. Each one still requires review.
False Positive Burden: When most reports prove benign, analysts experience fatigue from alert noise, and critical signals become harder to identify.
Resource Drain: Organizations hire new analysts expecting fresh capacity, only to find that email security absorbs much of their time immediately. Third-party managed services add expense without solving the underlying efficiency problem, which is why the push to automate SOC operations keeps intensifying.
Timing Gaps: Running scripts to remediate malicious emails in user inboxes takes time. Meanwhile, users may have already opened those messages, clicked links, or downloaded attachments. The window between report and remediation determines how much risk the program actually reduces.
Together, these challenges create pressure to reduce repetitive review without removing human oversight from consequential decisions.
As Lane Billings, Product Marketing Lead at Abnormal, explained in the webinar about one client: "Their SOC analysts, prior to AI Security Mailbox, were overwhelmed by the volume of user-reported phishing emails. And now that the AI is handling submissions, they've reclaimed 40,000 operational hours."
How to Automate User-Reported Phishing Triage and Response
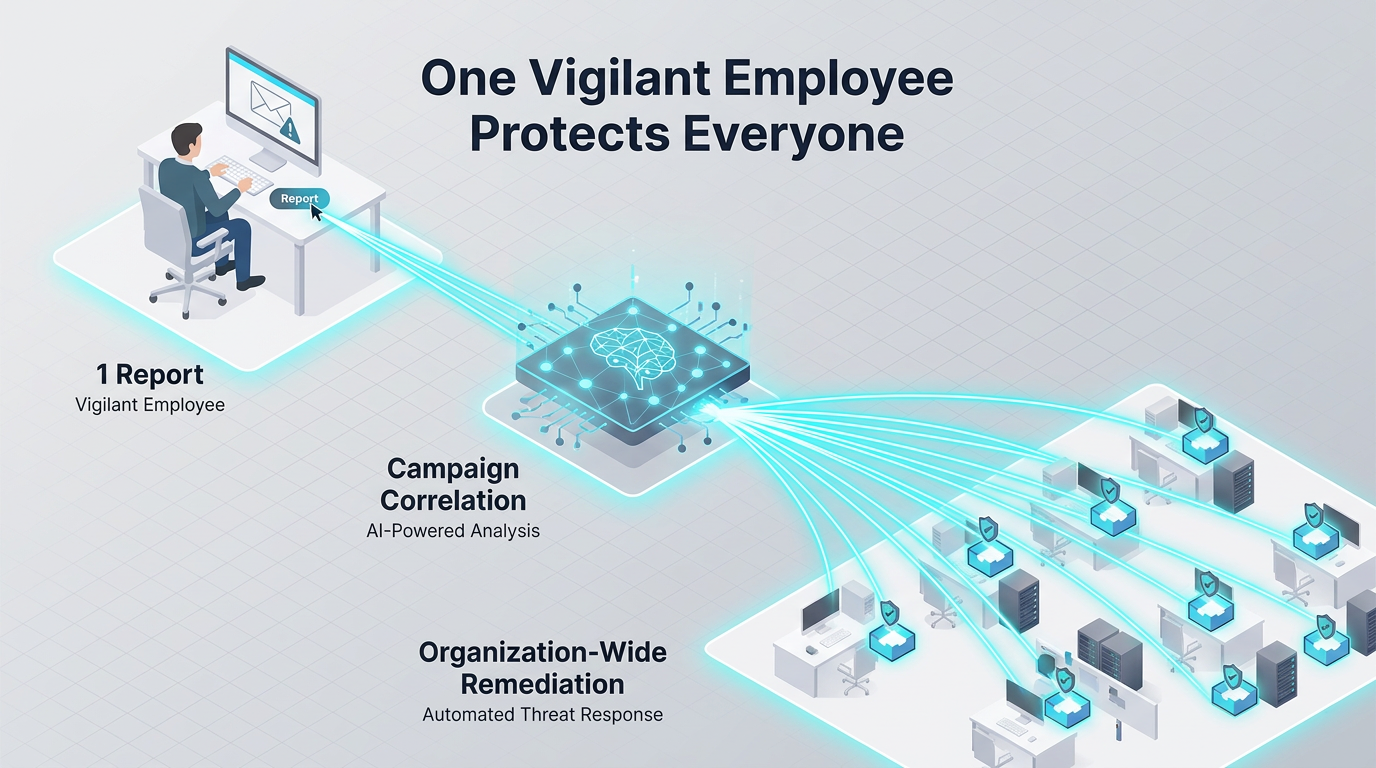
Automation can turn user-reported phishing into a workflow in which AI supports classification, campaign correlation, and first-line employee communication while analysts handle edge cases.
Consolidate User Reports
The first efficiency gain comes from ingesting user-reported emails into a single view. An effective consolidation layer should work with existing phishing-report buttons, Microsoft native reporting, abuse mailboxes, Google Workspace alerts, and third-party reporting tools, so security teams can improve the back-end workflow without disrupting established reporting habits.
This approach helps analysts reduce switching among a shared mailbox, a ticketing system, and the mail administration console when reviewing what employees have flagged. Centralized visibility gives analysts a consistent place to review verdicts, employee interactions, and related messages before deciding whether a report needs escalation.
Look for solutions that integrate with Microsoft 365 and Google Workspace through an application programming interface (API), requiring no mail exchange (MX) record changes. AI Security Mailbox, for example, deploys in minutes without disrupting mail flow and preserves familiar employee workflows without additional retraining.
Classify Reports with AI
Rather than requiring an analyst to inspect attributes one by one, AI can examine reported emails and classify them as malicious, safe, spam, or part of a security training exercise. Safe and spam reports can receive an automated response without an analyst opening the ticket, which reduces much of the manual review those reports would otherwise require.
Classification is most reliable when it moves beyond signatures, blocklists, and static rules to analyze communication patterns, sender behavior, and relationship context. Effective systems model how the organization normally communicates through workflow cadences, vendor interaction patterns, recipient behavior, and timing.
A reported invoice email from a vendor who has not previously emailed that department about billing, or a wire request email sent outside business hours from an executive who does not usually handle payments, can stand out against that baseline even without a technical indicator. Abnormal's behavioral AI is one example of this approach, and configurable response policies and guardrails help keep human oversight in place.
Correlate Campaigns and Automate Remediation
When an employee reports a malicious email that also landed in other inboxes, AI can correlate the wider campaign and help security teams remove related messages across the organization. Bulk remediation can reduce the need for an analyst to run a search and script by hand, whether the threat is a malware attachment delivery attempt, a vendor email compromise attempt, or a lateral phishing message sent from a compromised internal account.
This approach addresses the timing problem directly. A vigilant employee protects colleagues who received the same email and never reported it, because the report supports organization-wide remediation rather than a one-off fix for one inbox.
Integration with downstream systems, including extended detection and response (XDR) platforms and security information and event management (SIEM) tools, can feed user-report data into the systems the SOC already monitors.
Best Practices for Program Success
Effective user-reported phishing programs pair automation with deliberate configuration, clear escalation criteria, and familiar employee workflows. Here's how to do it:
Preserve Existing Workflows: Employees should not need retraining. Effective implementations can build automation on top of current phishing buttons and mailboxes so the reporting habit stays intact.
Configure Category-Specific Responses: Security teams can define a separate response policy for each verdict, including phishing simulation exercises, and reserve detailed next-step guidance for malicious email.
Define Escalation Paths for Edge Cases: Security teams can define which reports require human review. Reports involving executives, finance, or a suspected compromised account can route to a named analyst queue with the context already attached.
Evaluate Verdict Accuracy Separately: Security teams can ask triage automation vendors for false-positive and false-negative performance as distinct measures. A false negative leaves a live threat sitting in inboxes, while a false positive consumes analyst time, so a blended accuracy figure can hide the more consequential error.
Enable Downstream Integrations: Connecting user-reported phishing insights to SIEM logging and correlation, security orchestration, automation, and response (SOAR), and XDR platforms gives the wider team visibility into what employees report and what the system remediates.
Configuration decisions like these determine what the employee sees after reporting an email, which is where the program either builds reporting habits or discourages them.
How to Close the Loop With User Feedback and Education
The feedback an employee receives after reporting often determines whether they report again, and the traditional binary response wastes that moment. "We reviewed this email; it's safe" or "This was malicious; we've removed it" closes a ticket without teaching anything.
A phishing report shoudl support three response functions:
Explain Threat Indicators: Instead of a classification notice, the response can spell out the specific signals that identified the email, such as sender reputation, authentication results, and content anomalies. AI Phishing Coach extends this into contextual education built from the real manager, colleague, and vendor fraud scenarios employees encounter.
Translate Technical Concepts: Generative AI can adapt each response to the specific email, employee role, and organizational policy rather than reuse a static template. It can also translate terms like DKIM and DMARC into plain language, with tone and guardrails set in advance.
Answer Follow-Up Questions: The AI security analyst can handle follow-up questions inside the reporting workflow. An employee who asks what email authentication means gets an answer without an analyst joining the thread.
Together, these functions turn a phishing report into a personalized training moment within the employee's existing workflow.
How to Measure Success
A user-reported phishing program earns continued investment when its metrics show risk going down and analyst time moving to more valuable work. These measures give chief information security officers (CISOs) board-ready evidence and give security managers the signals they need to tune the workflow.
Essential metrics include:
Classification Distribution: The breakdown between malicious, safe, spam, and simulation reports shows what attackers are sending and how accurately employees are reporting. It also gives compliance reviewers a documented record of reported and remediated messages.
Time Savings: Teams can quantify hours reclaimed through automation. Reclaimed operational time allows analysts to study attack patterns, address insider risk investigations, and advance security initiatives instead of clearing a queue.
Top Reporters: Recognizing employees who consistently report suspicious messages can reinforce participation and show where targeted training may pay off.
Response Time: Teams can track report submission and remediation as a core operational metric.
Speed of First Report: SANS recommends measuring how quickly the first employee reports a suspected phishing email rather than counting total reporters, because an earlier report gives the security team more time to respond to the wider campaign.
Tracked together over several quarters, these measures show whether reports are arriving sooner and clearing faster than they did before automation.
Build a Scalable Phishing Response Program
The gap between a reactive user-reported phishing program and a strategic one comes down to how the work behind each report gets done. When triage is automated and one report supports campaign remediation workflows, analysts can spend their time on security incident investigations instead of sorting. Employees become more capable threat detectors, and the organization gains intelligence that improves defenses continuously.
Abnormal is built for exactly this shift. AI Security Mailbox applies behavioral AI to triage user reports, correlate wider campaigns, and remediate related messages across the organization, so analysts can focus on incidents that need human judgment rather than clearing benign submissions. Abnormal was also named a Customers' Choice in the 2026 Gartner® Peer Insights™ Voice of the Customer for Email Security, the only platform to do so three years in a row.
Ready to see these capabilities in action? Request a demo to explore how Abnormal can cut manual steps from your phishing response workflow.
Frequently Asked Questions
How Does User-Reported Phishing Differ from Automated Email Detection?
Automated detection acts on messages before or as they arrive, using the signals and controls available to the organization's enterprise email security stack. User-reported phishing captures what reached the inbox and what an employee found suspicious after reading it. That human signal can reveal context that automated controls did not classify as malicious when the message arrived.
The two approaches work together. Automated detection provides broad, consistent coverage, while employee reporting gives security teams another source of intelligence on novel social engineering attacks that may carry few obvious technical indicators. A mature workflow evaluates the reported message, searches for related emails, records the verdict, and uses the result to guide remediation and employee feedback.
What Should Happen When an Employee Reports a Phishing Simulation?
The system should recognize the message as a training exercise and respond with a simulation-specific template. Treating a simulation as a real threat can trigger unnecessary remediation and confuse the employee, while treating it as a safe email misses the chance to reinforce the correct behavior.
Security teams can define a separate classification and response policy for simulations within their security awareness training program. That policy can preserve the integrity of the exercise, acknowledge the employee's report, and avoid escalating the message into the malicious-email queue. It also gives program managers a clearer record of employee participation without mixing simulation activity with live threat data or operational response metrics.
How Quickly Should a Reported Phishing Email Be Remediated?
Security teams should remediate a reported phishing email as quickly as the verdict and established response policy allow. Programs can track report-to-remediation time as a core operational metric and define escalation paths for reports that involve executives, finance teams, or suspected account compromise.
Use campaign remediation workflows to support action across affected inboxes after one confirmed report, with human oversight for edge cases, disputed verdicts, and messages that require additional investigation.