Organizations can implement advanced threat protection (ATP) for email using proven best practices that guard against phishing threats, malware, and targeted attacks. Email remains a frequent entry point for social engineering and business email compromise, even as attackers increasingly pair it with software vulnerabilities and voice-based tactics, and static, rule-based filters are struggling to keep pace.
Key Takeaways
- Generative AI lets attackers craft convincing, context-aware emails that often evade traditional filters, which is why layered detection and real-time threat intelligence matter more than static signature updates.
- Business email compromise (BEC) attacks and vendor fraud increasingly rely on impersonation and fraudulent invoices, making context-aware detection essential rather than optional.
- Connecting advanced threat protection to security information and event management (SIEM) systems, endpoint detection and response (EDR) tools, and security orchestration, automation, and response (SOAR) platforms supports coordinated, automated containment that can reduce response time.
- Role-based training, clear reporting procedures, and rehearsed incident response playbooks turn employees into an active layer of defense instead of the last line of it.
- Continuous monitoring and tuning, including behavioral analytics, helps detection models adapt as AI-driven attacks evolve.
Why Advanced Threat Protection for Email Matters
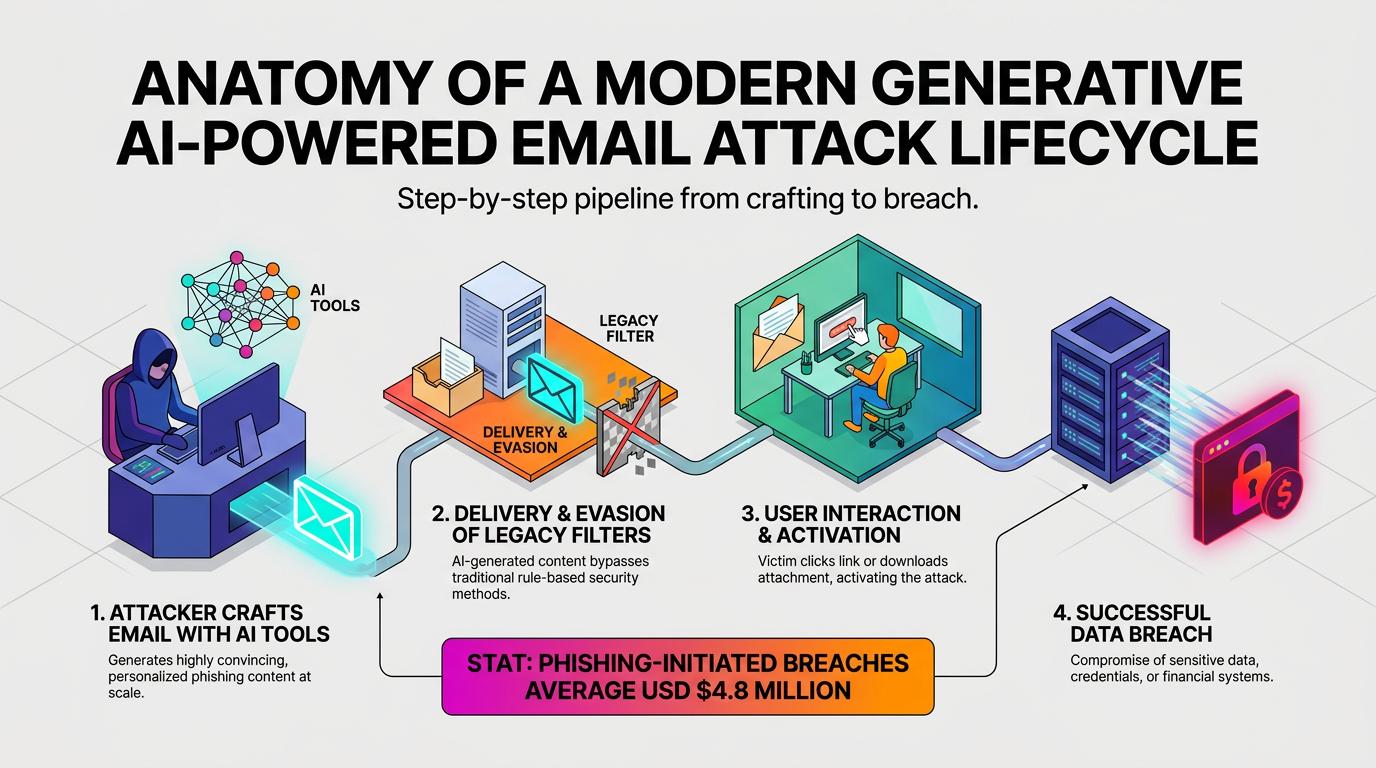
Email security needs advanced protection because attackers now use automation, impersonation, and trusted relationships to create messages that legacy filters often struggle to evaluate. The 2026 Verizon DBIR found that software vulnerability exploitation and voice-based social engineering are both gaining ground as attack vectors industry-wide, but email remains a steady channel for these campaigns, and signature-based filters aren't built to catch behaviorally sophisticated attempts. The U.K.'s National Cyber Security Centre (NCSC) assesses that generative AI has increased the speed, scale, and polish of social engineering, letting criminals rely on language models, deepfakes, and zero-day exploits that adapt faster than signature updates can catch. The stakes keep rising: IBM's Cost of a Data Breach report found phishing was the most common initial attack vector in its 2025 dataset, with phishing-initiated breaches averaging USD $4.8 million each.
The sheer volume of email only adds to the challenge. Inboxes receive heavy spam, while new malware variants appear daily, overwhelming rule-based gateways. Since email is such a central communication tool, attackers continue to see it as their best way in.
Modern campaigns often center on BEC, vendor fraud, and account takeover. According to the FBI's Internet Crime Complaint Center (IC3), reported BEC losses exceeded $3 billion. These threats often hinge on impersonation, fraudulent invoices, or trusted relationships, so legacy filters can miss them. Advanced, behavior-driven protection fills this gap by analyzing context, intent, and relationship patterns, keeping pace with attackers who already rely on AI.
Choose the Right Solution for Your Environment
Advanced threat protection platforms should deliver layered detection, real-time intelligence, flexible policies, native integration, and detailed reporting that align with your organization's risk profile.
Critical capabilities to evaluate include:
- Layered Detection: It combines sandboxing, URL rewriting, and contextual analysis to catch sophisticated threats.
- Real-Time Threat Intelligence Feeds: These continuously update detection rules to close zero-day attack windows.
- Granular Policy Controls: These allow per-user or per-department tuning, supporting more aggressive protection for high-risk teams like finance.
- Native Integration: This works with your existing cloud or hybrid infrastructure without requiring architectural changes.
- Detailed Reporting and Forensics: These provide context for security decisions and blocked messages.
Organizations can match these security capabilities to their industry's threat patterns and email volume. In environments with heavy traffic, speed, accuracy, and minimal false positives are equally essential. Testing the right solution in real conditions with phishing simulations can show how it performs across detection, latency, and operational impact.
Integrate with Existing Security Tools
Advanced threat protection delivers the most value when it strengthens existing security investments through direct integration. Organizations can connect ATP to complementary tools in a few key ways:
- SIEM Correlation: Connecting ATP event data to SIEM logging lets detections correlate with network, cloud, and identity logs. Standardized formats such as Syslog or STIX/TAXII let analysts pivot quickly from a suspicious message to related indicators, which can help reduce response times.
- Endpoint Detection Integration: Linking ATP with endpoint detection and response (EDR) closes the gap between the inbox and the device. When a malicious attachment slips past initial filters, endpoint agents can isolate the host while ATP retracts the email from affected mailboxes, coordinated through bidirectional APIs to help maintain both speed and accuracy.
- SOAR Automation: Security orchestration, automation, and response (SOAR) platforms or custom scripts can automate repetitive containment step. Quarantines, credential resets, and ticket creation happen automatically, which can lower mean time to respond and free analysts for deeper threat hunting.
This kind of coordination helps security teams turn isolated detections into connected response workflows that scale with organizational needs.
Train Your Users to Recognize Threats
Technology alone may not stop every attack, and strong email security programs pair technical controls with trained people. When employees can identify and report suspicious messages, they help close the gap that filters may miss.
Build Role-Based Training Programs
Training should be risk-based, continuous, and relevant to the threats each team sees in daily work. The Cybersecurity and Infrastructure Security Agency (CISA) advises that because threats evolve constantly, once-a-year training isn't enough. Organizations can tailor content to each team's exposure: finance teams practice wire-fraud scenarios, while developers focus on credential-phishing lures. Regular phishing simulations with varied payloads help employees face realistic threats tied to their daily work. This approach keeps training practical, reduces generic awareness fatigue, and helps employees connect email security habits to the business processes attackers commonly target.
Establish Clear Reporting Procedures
Training only works when employees know how to act after they see a suspicious message. A one-click reporting process gives users a consistent path, and regular practice reduces uncertainty about where to forward a message, who to notify, or how much context to include. Clear escalation paths help your security team hear about malicious emails quickly and triage them with consistent information. Reporting procedures should also explain what employees can expect after submission, such as whether security will acknowledge the report, remove similar messages, or request more detail. That feedback loop reinforces participation and turns user reports into a reliable input for investigation.
Track Performance and Optimize
Security teams can evaluate training with core metrics such as click-through rates on simulations, report rates for real threats, and median reporting time. Recurring reviews help teams adjust content as needed to maintain progress. If one team repeatedly misses credential-phishing lures, refresh that group's examples and include screenshots that mirror its actual workflows. If report rates improve but reporting time remains slow, simplify the submission process or clarify escalation expectations. These measurements help security leaders show whether awareness efforts reduce risk, and they give security managers a practical way to tune training without relying on anecdotal feedback.
When employees are trained effectively, they become an active line of defense that complements technical controls and strengthens your organization's overall resilience.
Establish Clear Incident Response Procedures
Effective incident response for email threats requires structured playbooks tailored to the unique risks of phishing, BEC, and other email-borne attacks. The National Institute of Standards and Technology (NIST) recently revised its incident response guidance to align with the current Cybersecurity Framework, and strong programs typically address it across a few core areas:
- Defined Roles and Escalation Paths: Step-by-step protocols for different scenarios keep each team member clear on their role during an incident.
- Automated Containment: Automated detection and remediation tools handle routine containment, reducing the need for manual intervention and accelerating recovery.
- Post-Incident Analysis: Reviewing each case afterward helps uncover vulnerabilities, evaluate the effectiveness of response actions, and strengthen future strategies.
- Clear Communication: Internal teams and external stakeholders receiving timely updates and transparent reporting builds trust and supports smooth coordination.
Regular training exercises, including tabletop simulations built on frameworks like the European Union Agency for Cybersecurity's (ENISA) exercise methodology, validate these plans and prepare teams to act decisively under pressure.
Continuously Monitor and Tune Your Protection
Email threats evolve daily, and static defenses quickly lose effectiveness. Advanced threat protection remains effective only when organizations commit to ongoing measurement and refinement. Without this process, false positives frustrate users, true threats slip through, and security teams fall behind.
Track Key Metrics
Organizations can track detection efficacy, false positive rate, mean time to remediate, and user-reported misses. Maintaining a high signal-to-noise ratio is essential because excessive quarantines erode trust and slow business operations. Security teams can correlate attack spikes with policy changes or new campaigns, then validate that adjustments reduce false positives without introducing gaps. Recurring reviews with operations teams and documented progress help tie improvements directly to actions. This keeps tuning accountable: security teams can see which policy changes improved precision, which detections still need review, and which user-reported misses deserve deeper investigation.
Automate Tuning with Behavioral Analytics
Manual rule updates often struggle to keep pace with AI-driven phishing or deepfake-assisted BEC schemes flagged by the Financial Crimes Enforcement Network (FinCEN). Behavioral analytics helps teams move beyond static conditions by using observed email patterns and analyst feedback to prioritize suspicious activity. Modern tools ingest live threat intelligence and behavioral pattern data to continually adjust detection models, so defenses can adapt as attackers change tactics. Automation should support tuning decisions rather than hide them. Analysts still need visibility into why detections changed, which alerts were suppressed, and where new policies affect high-risk users or departments.
Balance Automation with Human Oversight
Organizations can pair self-optimizing capabilities with periodic threat hunting sessions to keep automation aligned with organizational risk tolerance. Results can feed into centralized reporting for unified visibility across endpoints, networks, and email. Concise updates on emerging attack methods and changes to detection models help security teams stay aligned. Human oversight also gives analysts a structured way to validate edge cases, review executive or finance-related detections, and identify places where automation needs tighter guardrails. The goal is not to slow response, but to keep automated decisions explainable, auditable, and connected to the way the organization actually works.
Building Advanced Threat Protection Into a Continuous Program
Advanced threat protection for email works best as an ongoing discipline, not a one-time deployment. Organizations that pair layered detection with tight integration, role-based training, and clear incident response playbooks close the gaps attackers rely on most. As generative AI keeps changing how phishing and business email compromise are crafted, the programs that hold up are the ones built to keep tuning, testing, and adapting rather than the ones that treat email security as solved.
Frequently Asked Questions
What Is Advanced Threat Protection for Email?
Advanced threat protection for email is a layered approach to detecting and stopping phishing, malware, and targeted attacks that go beyond what signature-based spam filters can catch. It typically combines detection technology such as sandboxing and contextual analysis with integration into existing security tools, user training, and defined incident response procedures.
How Is Advanced Threat Protection Different from a Standard Secure Email Gateway?
A standard email gateway generally relies on known signatures, reputation data, and static rules to block recognized threats. Advanced threat protection adds context-aware and behavioral analysis on top of that baseline, which helps it catch novel or highly targeted attacks, such as business email compromise, that don't carry a malicious link or attachment for a signature-based tool to flag.
How Often Should Organizations Run Phishing Simulations?
Most security teams run simulations on a recurring basis, often quarterly or more frequently for high-risk teams such as finance, rather than treating training as a single annual event. Varying the payloads and scenarios between rounds keeps the exercises realistic as attacker tactics change.
What Metrics Show Whether Advanced Threat Protection Is Working?
Detection efficacy, false positive rate, mean time to remediate, and user-reported misses are the core signals security teams track. Watching these together, rather than any single metric in isolation, helps distinguish a genuinely well-tuned program from one that's simply quarantining more email.