Key Insights
Security teams lack the time and capacity to improve detection manually. Every reported false negative or false positive deserves an investigation and a real fix before the same issue occurs again, but more than half of security teams (55%) report being understaffed, and 65% report unfilled cybersecurity roles. As a result, the work gets distributed across team members as capacity allows, which means it rarely happens consistently.
AI Detection Engineer handles that process directly. It investigates reports submitted through Detection 360 or AI Security Mailbox, identifies the underlying pattern, and, where it meets the required efficacy threshold, builds and deploys a detection designed to catch or suppress similar emails in the future.
AI Detection Engineer builds on the expanded Detection 360 capabilities we launched earlier this year, which provide greater visibility and deeper evidence, as well as extended AI Security Mailbox coverage. AI Detection Engineer takes this further with sophisticated new detectors, faster response, and deeper evidence of impact, including every new message caught or false positive suppressed by a detector.
Schedule a Demo
What AI Detection Engineer Does
Now generally available to US and EU commercial customers, AI Detection Engineer runs on top of Attune, Abnormal's behavioral foundation model, and turns confirmed false negatives and false positives reported by your team into opportunities to improve detection. Here's what that work looks like end to end.
It Investigates Reports Like an Analyst
A reported miss is only useful if someone digs into why it happened. Left in a queue, that investigation can be delayed or never happen at all.
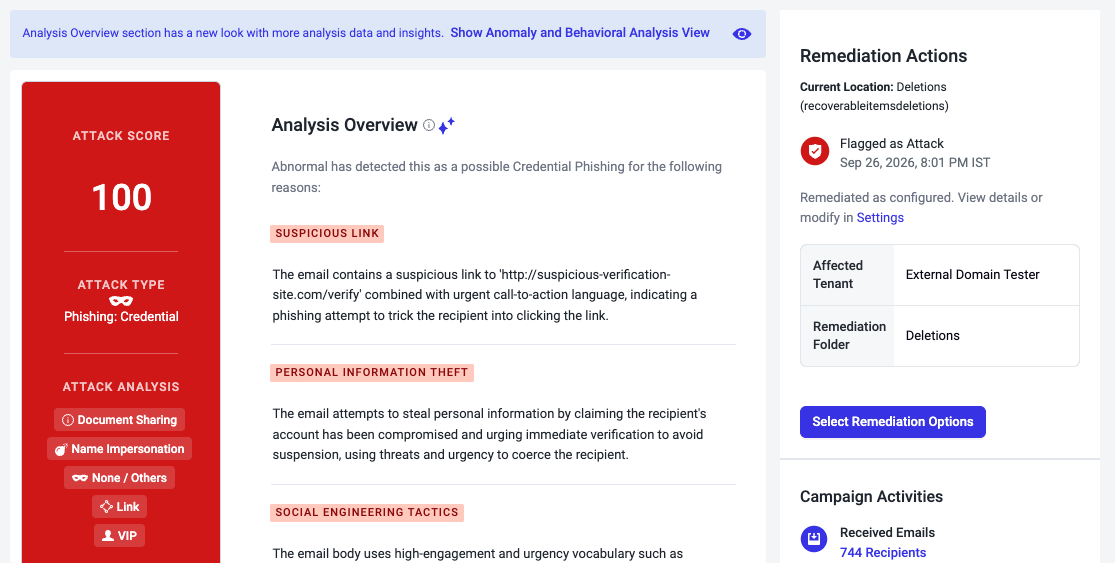
AI Detection Engineer investigates confirmed false negatives or positives from Detection 360 and false negatives from AI Security Mailbox, analyzing the message and its context to understand what makes the attack distinct from normal traffic in your environment.
Outcome: Confirmed misjudgments get a deep investigation without straining your team’s capacity or calling for additional headcount.
It Writes and Validates a Detection Built for Your Environment
A generic rule template doesn't account for how attacks actually show up in an individual organization's mail flow.
AI Detection Engineer writes a detection that generalizes to the underlying attack pattern or is tuned to catch semantic variants of the threat, rather than simply filtering the single reported message. Before anything goes live, it tests the detection against your own historical traffic to confirm it performs reliably.
Outcome: Each detection is built and tested against your own environment, extending an Abnormal foundation where the typical customer achieves 99.999%+ efficacy, or about one missed attack per 100,000 emails analyzed. 1
It Deploys and Reports on What Changed
When a SOC analyst flagged a miss through Detection 360, customers could see that their feedback was shaping detection, but not with enough detail to fully understand or verify the impact.
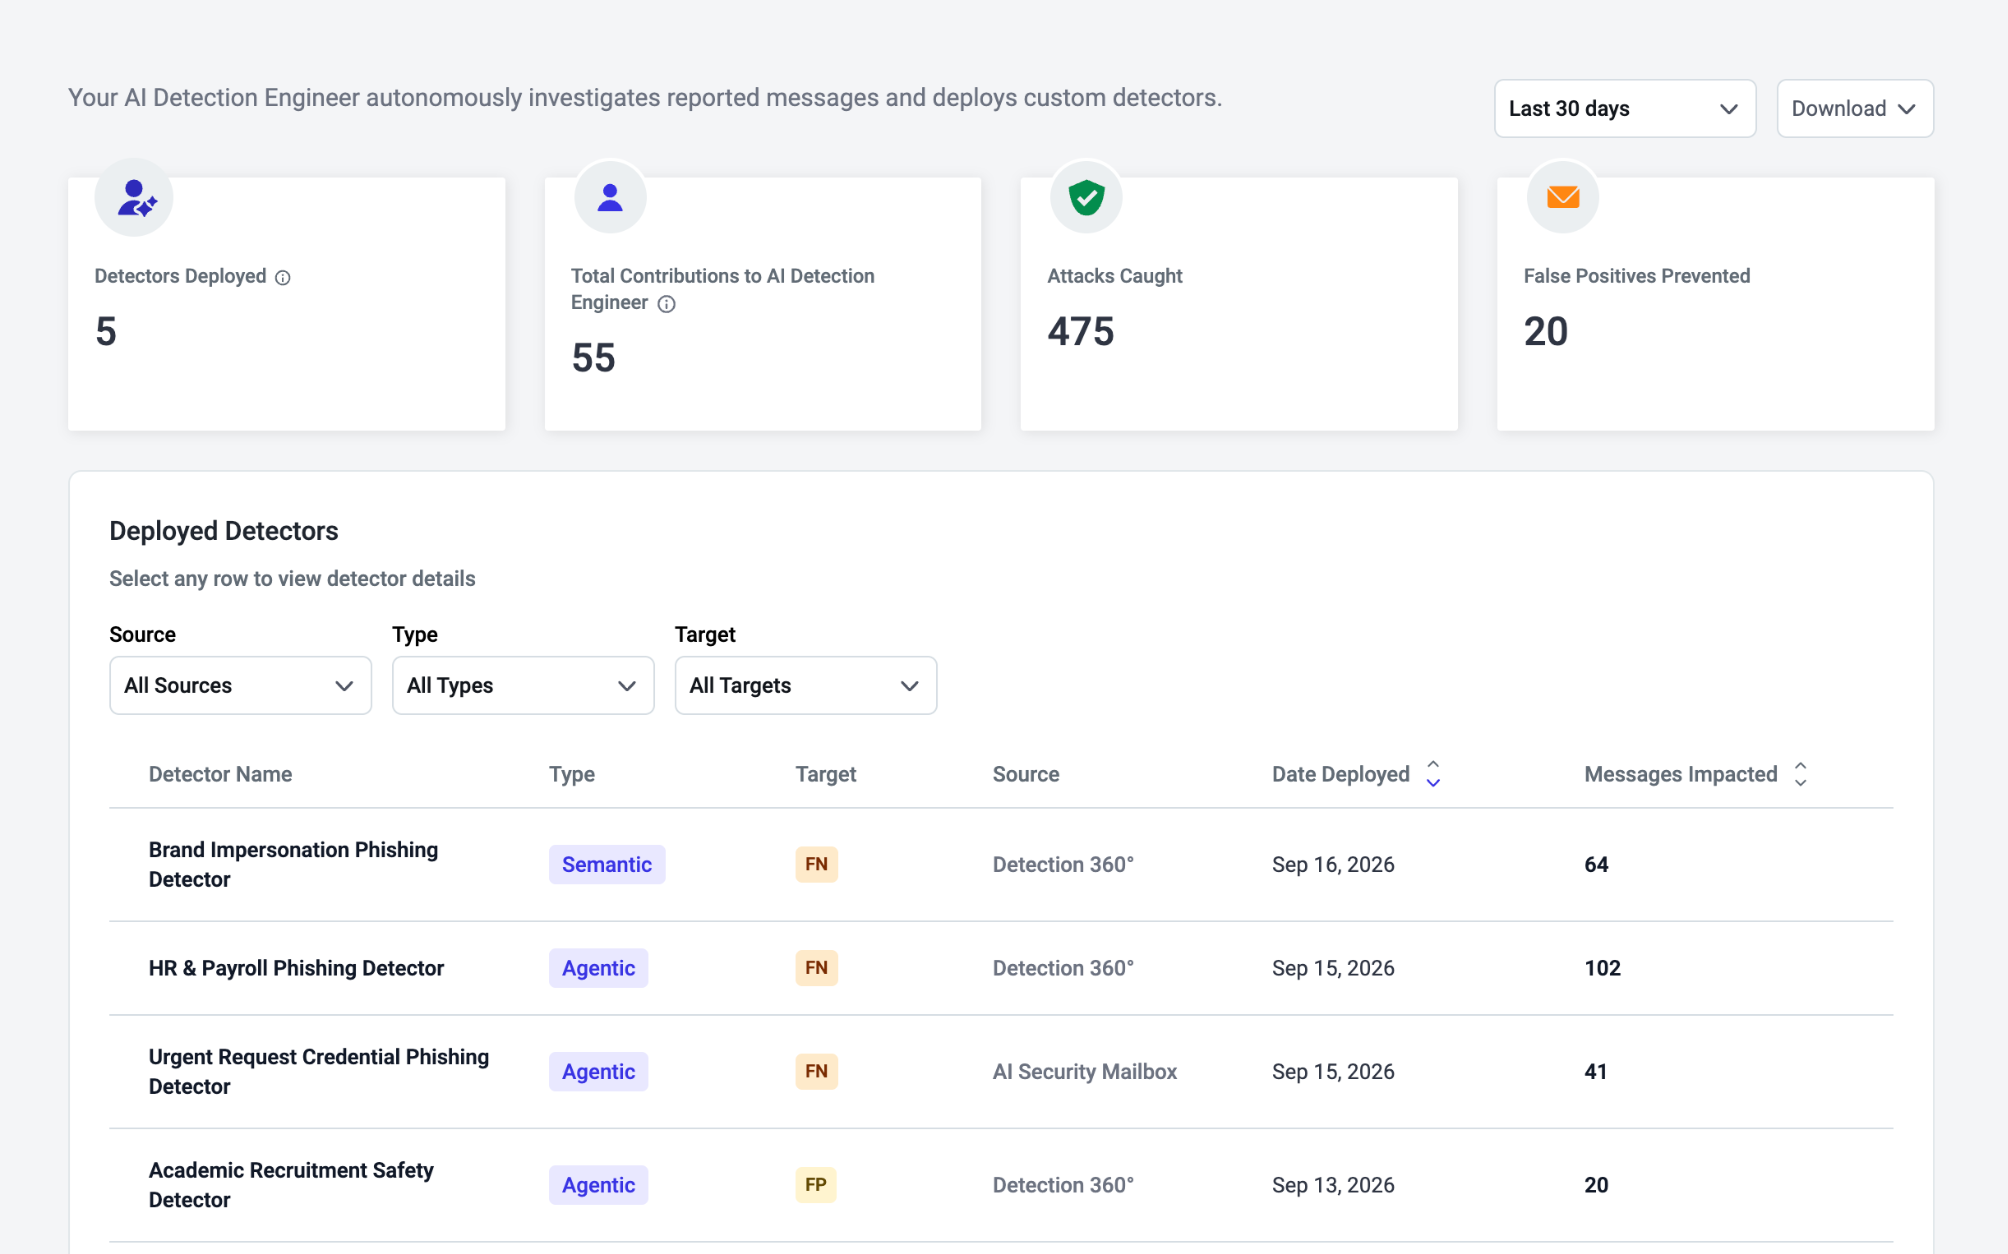
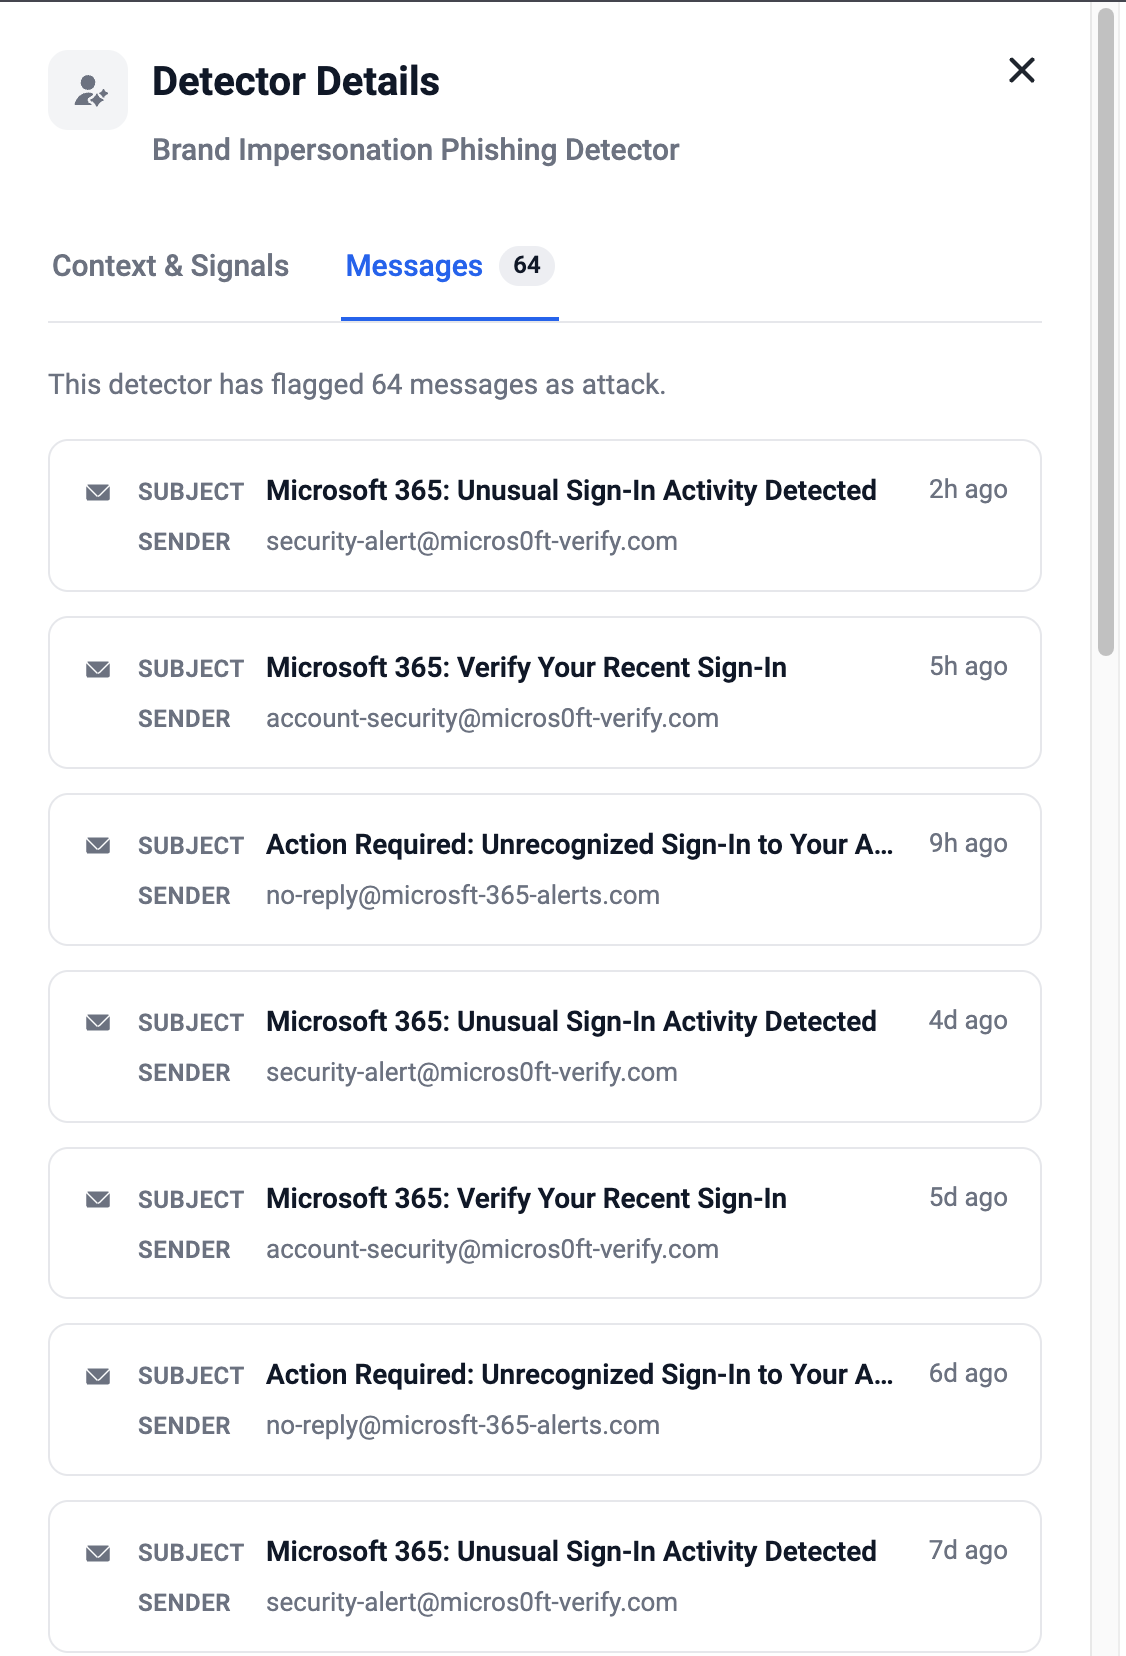
AI Detection Engineer addresses this by providing full visibility from its dashboard, including a high-level view of Abnormal’s response and detector-level detail that analysts can drill into.
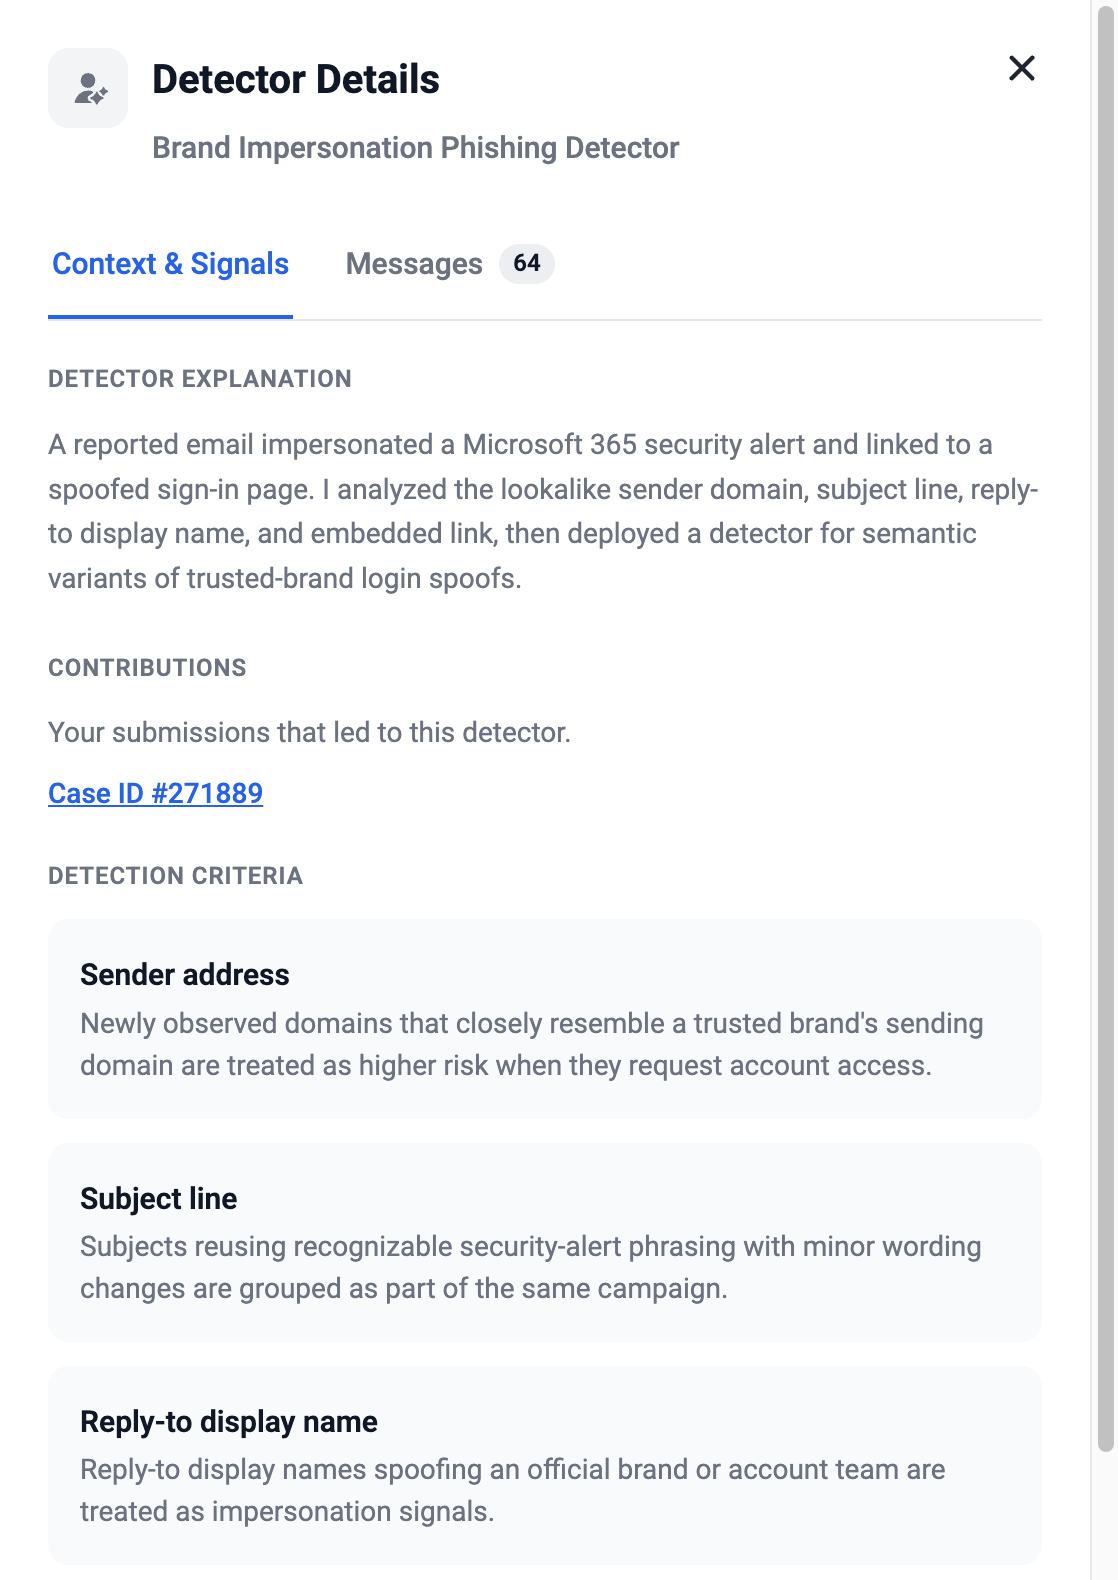
Once a detection proves that it can reliably catch an attack or suppress a false positive without impacting safe emails, AI Detection Engineer deploys it automatically and adds the details to your dashboard: a plain-language explanation, the signals it's watching for, and the full list of messages it has caught or false positives it has suppressed.
Outcome: Every deployed detector reports back with verifiable proof of impact and full traceability to the report that triggered it.
AI Detection Engineer: From Reported Miss to Better Protection
For the analyst, a confirmed miss becomes an investigated, tested, deployed detection, with a record of every message it catches afterward. For the security leader, that means reported misses turn into measurable protection without adding headcount to a team already stretched thin.
AI Detection Engineer handles the detection engineering that follows a report, acting as an extension of your SOC. Custom AI Models and Custom Rules remain available when your team wants to proactively shape detection for your environment.
See what a dedicated detection specialist can catch that a backlog can't. Schedule a demo.
Schedule a Demo
1Based on Abnormal internal data.