Key Insights
Red team cybersecurity is the practice of simulating a real adversary against your own organization to find out whether your defenses actually hold up under attack. Most security programs are measured by what they block in theory.
A red team measures what happens in practice, when a skilled attacker is actively trying to get in and stay hidden. Email is where that pressure usually lands first: Verizon's 2025 Data Breach Investigations Report found that the human element factors into roughly 60% of breaches, and a large share of those start with a message someone was never supposed to trust. This guide walks through how to plan a red team program, staff it, and measure whether it is producing findings your organization can act on.
Key Takeaways
- Red team cybersecurity validates defenses against a realistic adversary rather than a checklist, exposing gaps that vulnerability scans and audits routinely miss.
- A useful engagement starts with tight scope and clear rules of engagement, so the exercise stays safe, legal, and focused on the risks that matter.
- The strongest red teams pair technical range with people who can explain why a finding matters to the business, not just how the exploit worked.
- Measuring outcomes like detection lag and time to contain, instead of raw exploit counts, is what turns a one-time test into an ongoing security improvement.
What Red Team Cybersecurity Is and Why It Matters
A red team is a group of security professionals authorized to emulate a real attacker against an organization's systems, people, and processes, with the goal of finding weaknesses before a genuine adversary does. Where a vulnerability scan lists what could theoretically be exploited, a red team shows what an attacker would actually do with those weaknesses once inside.
The distinction that trips people up is red team versus penetration testing. A penetration test is usually scoped to find and prove as many vulnerabilities as possible in a defined target, within a set window.
A red team engagement is quieter and goal-driven: operators pick an objective an attacker would care about, such as reaching a finance mailbox or exfiltrating a sample of sensitive data, then try to achieve it without being caught. The point is not a long list of findings. It is a realistic answer to the question of whether the organization would detect and stop a determined intruder.
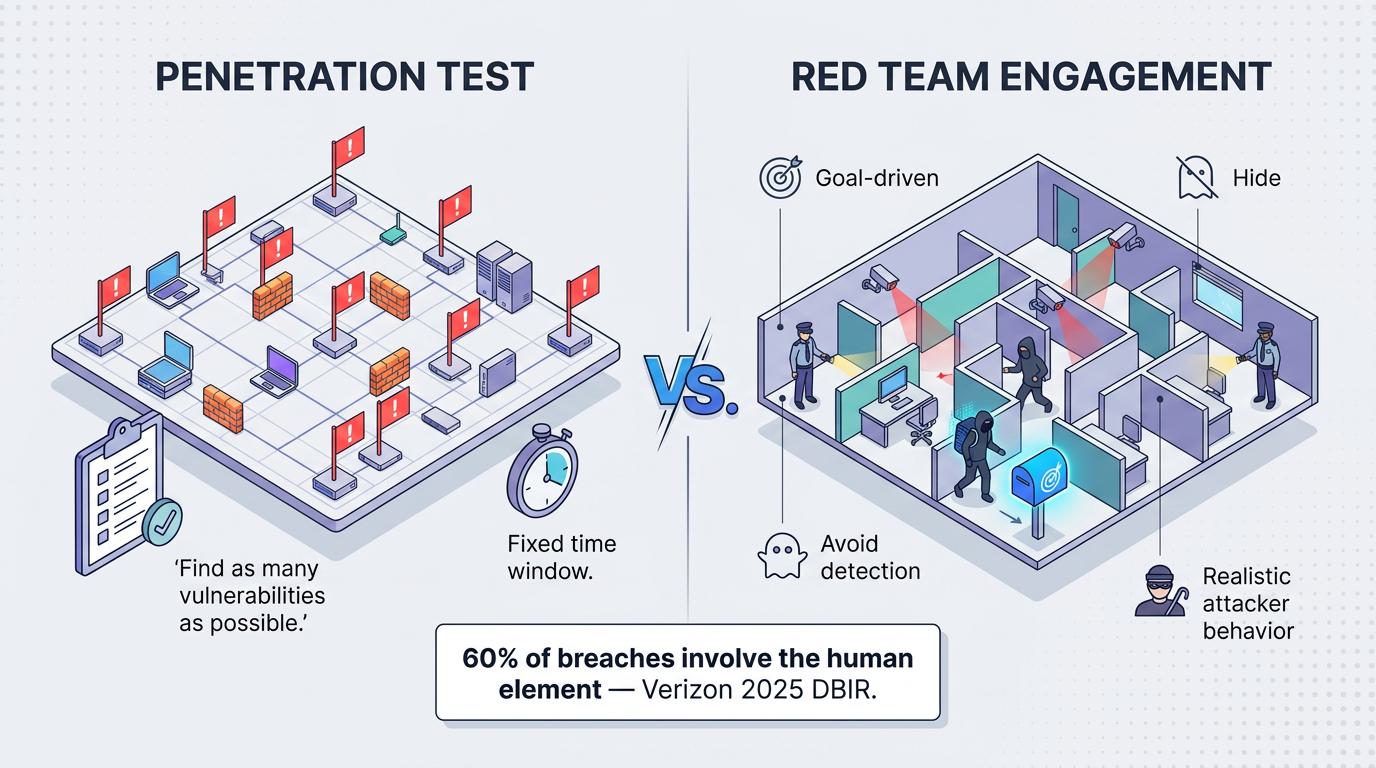
That answer carries weight at the executive level. Red team exercises translate technical risk into terms leadership understands, like how quickly an intrusion is detected and what a successful breach would cost.
In the US, the average cost of a data breach reached a record $10.22 million in 2025, according to IBM's Cost of a Data Breach report. A red team that shortens the gap between compromise and detection is directly reducing that exposure, and framing findings that way is often what earns a program continued funding.
7 Steps to Build an Effective Red Team Program
A red team program only produces useful results when it's planned, staffed, and run with the same discipline as the attack it's simulating. Skip any part of that discipline and the outcome tends to be the same: a report full of findings that never get fixed, or worse, an exercise that creates real business risk because nobody defined the boundaries first.
The steps below cover the full lifecycle, from planning the engagement to turning what it finds into lasting improvement.
1. Define the Goals and Scope
Clear goals and a focused scope are what separate a red team exercise that produces action from one that produces a report nobody reads. Before the first simulated phishing email goes out, the team and its stakeholders should agree on a short planning document that captures the essentials.
That planning document works best when it names a few specifics:
- Objectives: The concrete outcomes an attacker would pursue, such as gaining access to a specific system or intercepting a payment approval.
- Targeted Assets and Channels: The systems, mailboxes, and collaboration platforms in play, and any that are explicitly off-limits.
- Success Criteria: What counts as a successful action, so results can be judged consistently rather than argued about afterward.
- Sponsorship and Approvals: Who authorized the engagement and who has the authority to pause or stop it.
This step can feel slow when the team is eager to start testing. In practice, an hour spent agreeing on scope prevents days of confusion later, and it keeps the exercise pointed at the risks the business actually cares about. Mature cybersecurity programs treat this planning discipline as part of the test, not a delay before it.
2. Map Objectives to Attack Frameworks
Attack frameworks give a red team a shared vocabulary for turning a business objective into repeatable, comparable attacker behavior. Instead of improvising, operators map each goal to documented techniques, which makes results easier to compare across engagements and easier for defenders to line up against their detection coverage.
MITRE ATT&CK is the common reference point. For an email-led scenario, a team might map its activity to a spear phishing technique for initial access, then to a credential or token-theft technique for what happens after a user takes the bait. The value of naming the technique is not the identifier itself. It is that the defending team can later check whether they had any detection for that specific behavior, and if not, that gap becomes a concrete thing to fix.
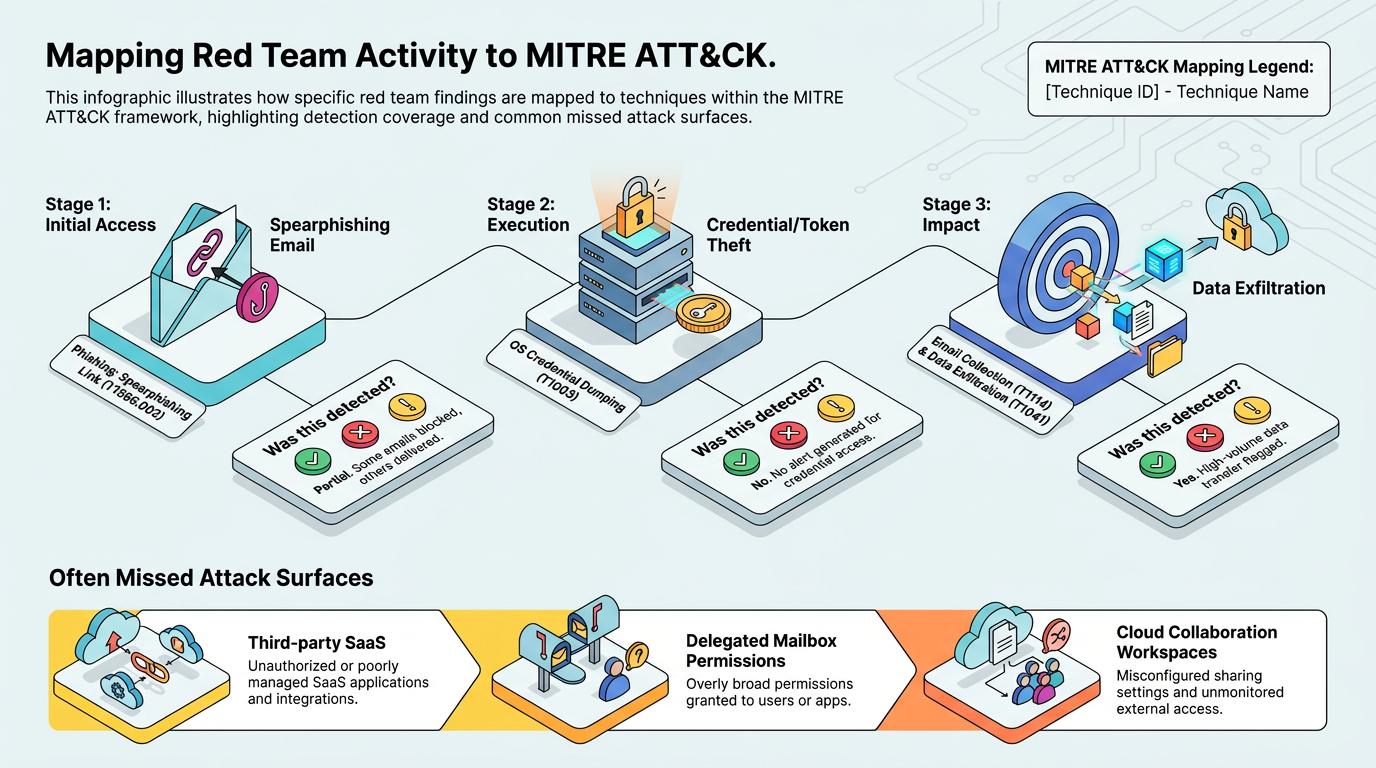
Framework mapping also surfaces the parts of the attack surface teams tend to forget. Third-party SaaS access, delegated mailbox permissions, and cloud collaboration workspaces rarely show up in a traditional network-focused test, yet they are exactly where modern intrusions move. Documenting the mapping and the authorizations behind it means findings can move into remediation without a scramble to reconstruct what was tested and why.
3. Build the Right Skills and Mindset
An effective red team needs operators who can both replicate a current threat and explain its business impact in plain language. Technical range matters, but so does the judgment to know which attack path is worth pursuing and the communication skill to make a finding land with people who will never read a packet capture.
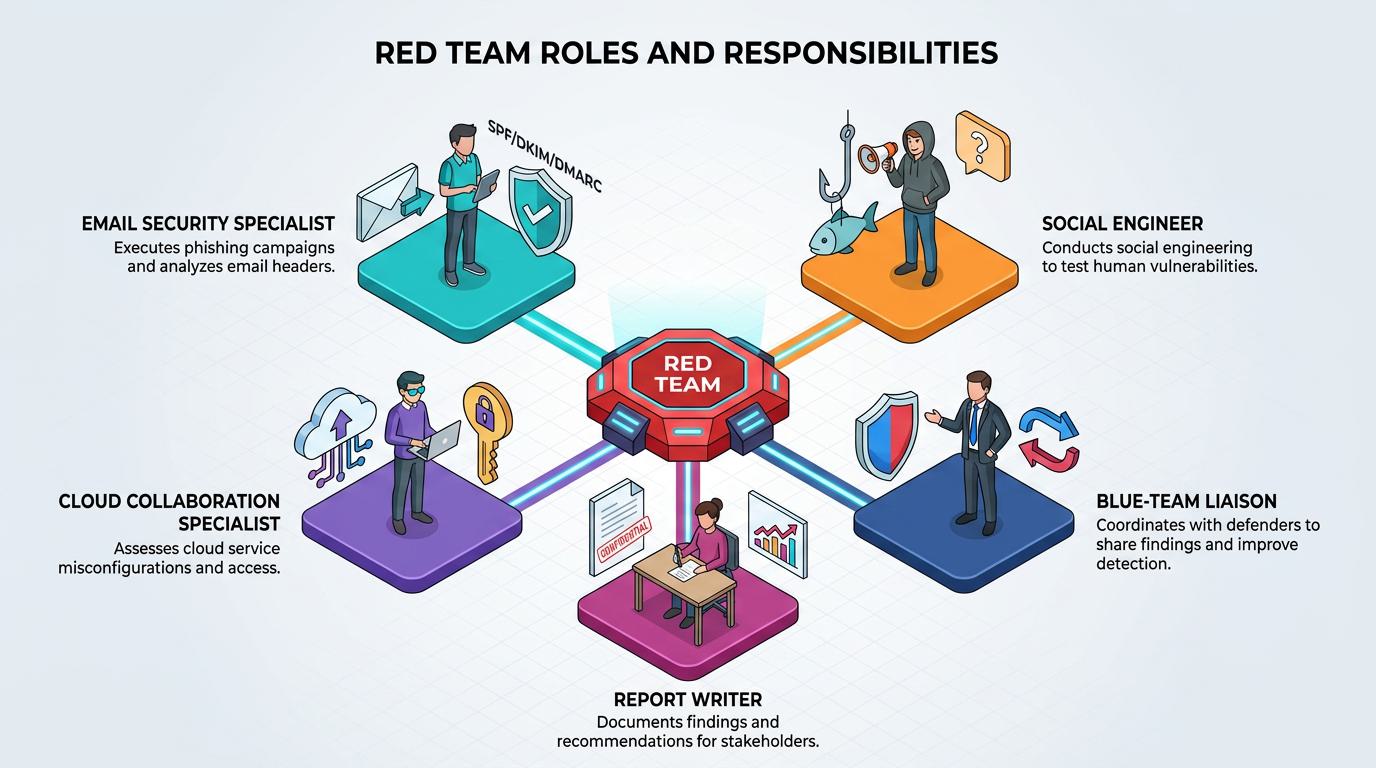
Most well-rounded teams cover a handful of complementary roles:
- Email Security Specialist: Evaluates the email authentication controls that verify a sender is who they claim to be, including Sender Policy Framework (SPF), DomainKeys Identified Mail (DKIM), and Domain-based Message Authentication, Reporting and Conformance (DMARC), and probes for weaknesses in how messages are filtered and trusted.
- Social Engineer: Builds realistic phishing and business email compromise (BEC) scenarios that reflect how employees actually interact with executives and vendors.
- Cloud Collaboration Specialist: Tests how an attacker could abuse shared workspaces, delegated access, and account permissions.
- Blue-Team Liaison: Coordinates timing and safety with defenders and manages post-exercise analysis.
- Report Writer: Turns technical findings into business risk and remediation priorities leadership can act on.
Beyond the roles, the traits that make a red teamer effective are discipline, curiosity, and the ability to tell the story of an attack. Discipline keeps activity quiet and within scope. Curiosity finds the unexpected path a checklist would never suggest, including the emerging threats that older playbooks miss. And the storytelling is what connects a technical weakness to a consequence a CISO cares about, whether that is financial loss, a compliance failure, or an operational outage.
Teams that mix backgrounds, spanning incident response, application security, and social engineering, tend to anticipate a wider range of attacker moves than a group drawn from a single specialty.
4. Establish Rules of Engagement
Rules of engagement (ROE) protect the organization by defining exactly what the red team may do, what it must never touch, and who can halt the exercise. It is a written, mutually agreed contract created before any attack reconnaissance starts, and it is the single most important safety mechanism in the entire engagement.
A complete ROE spells out the operating window, including permitted hours and any blackout dates when testing must pause. It lists the techniques that are allowed, such as phishing or domain spoofing, and the systems that are strictly out of bounds. It names the people authorized to stop activity and how to reach them immediately. It also sets rules for the sensitive situations that inevitably come up: how to handle simulated malware, whether executives can be targeted, and how far testing can go near production systems.
Once it is signed by security, IT, legal, compliance, and the executive sponsor, the ROE gives everyone legal protection, operational clarity, and an audit trail. It is also what lets the red team operate realistically while staying inside firm limits, so the exercise tests genuine attacker behavior without creating business, regulatory, or safety risk.
5. Coordinate Communications During the Exercise
Structured, secure communication keeps a red team coordinated without tipping off defenders or losing control of the exercise. Before testing starts, the team agrees on the encrypted channels it will use during the engagement and, critically, how it will escalate if something goes wrong.
Good operational communication usually covers a few standing practices:
- Situation Reports: Regular summaries of what objectives were achieved, what defenders detected, and any unexpected operational impact.
- Safeword Process: A simple, agreed signal that immediately halts activity if a real incident or a critical system is affected.
- Simulated-Incident Handling: A way to route simulated threats so defenders can measure their response without confusing an exercise with a genuine attack.
- Debrief Workflow: A secure post-engagement conversation that moves findings into remediation planning while the details are fresh.
The goal is to preserve the realism that makes the exercise valuable while keeping a hand on the brake. When a team knows how to pause, how to report unexpected effects, and how to tell a drill apart from the real thing, it can push hard on the organization's defenses without risking the organization itself.
6. Turn Findings Into Remediation
A red team exercise creates value only when its findings become prioritized fixes. Immediately after the engagement, the team maps each attacker action to the defensive gap it exposed, noting which control failed, which alert fired, and which step in the response slowed things down.
From there, the work follows a repeatable cycle: identify the techniques that succeeded, confirm the gap they exploited, remediate it, and then re-test to verify the weakness is actually closed. Re-testing is the part teams most often skip, and it is the part that proves remediation worked rather than assuming it did.
Organizing the fixes by effort and impact keeps the conversation productive. Quick wins might include tightening email authentication alignment or restricting mailbox forwarding. Medium-term work often involves alert routing, access reviews, or targeted user training. Larger initiatives can mean stronger DMARC enforcement, tighter identity controls, or new detection logic for cloud collaboration abuse. Tying each item to a real attack path the red team demonstrated, and to the specific email security gaps it exposed rather than to abstract risk language, is what gets remediation prioritized and funded.
7. Measure Red Team Progress Over Time
Outcome-focused metrics show whether a red team program is actually improving detection, containment, and resilience. Counting how many times operators got in tells you very little on its own. The more revealing measures track how the defense performs: how long an intrusion goes unnoticed, how quickly it is contained once detected, and how many objectives the red team completes before defenders respond.
Metrics like detection lag, mean time to contain, and objective completion rate give leadership a clear read on progress in language they already use. For email-focused programs, measures such as phishing detection rates and reductions in false positives connect the exercise to the day-to-day work of the security team.
The final step is to close the loop after every engagement. Update threat models with what the exercise revealed, refine the framework mappings, retrain staff where a scenario found a gap, and adjust policies accordingly. Testing that repeats on a cadence, with each round measured against the last, is what moves a security program away from one-time assessments and toward steady, demonstrable improvement.
Testing Is How Confidence Becomes Evidence
A red team turns assumptions about your defenses into evidence. Done well, it does more than surface weaknesses; it shows how an attacker would move, how fast your team would notice, and what a real breach would cost if no one did. The organizations that get the most from red teaming treat it not as an audit to pass but as a recurring habit, measuring each engagement against the last and letting the findings reshape their priorities. Build that habit, and every exercise makes the next attacker's job harder.