Key Insights
Cloud attacks are accelerating at a pace that demands immediate attention. According to the CrowdStrike 2025 Threat Hunting Report, cloud intrusions increased 136% in H1 2025 alone compared to all of 2024. Most of these breaches trace back to preventable gaps: environments that expand faster than the controls meant to secure them.
The seven attack vectors below account for most of that gap, and each has a defense that fits into the security controls teams already run.
Key Takeaways
- Misconfigured cloud resources and overly permissive access controls remain the most common entry point for attackers, which is why automated posture management and least-privilege enforcement matter more than any single tool.
- Compromised credentials drive account takeover, lateral movement, and business email compromise, and phishing-resistant multi-factor authentication paired with session monitoring is the most effective way to contain that risk.
- Insecure APIs, vulnerable supply-chain integrations, and unmonitored insider activity each open a distinct entry point that traditional perimeter defenses were never built to catch.
- Ransomware and phishing increasingly move through cloud storage and collaboration platforms rather than the traditional inbox, which is why layered, behavior-based monitoring across identity, email, and file activity has become necessary.
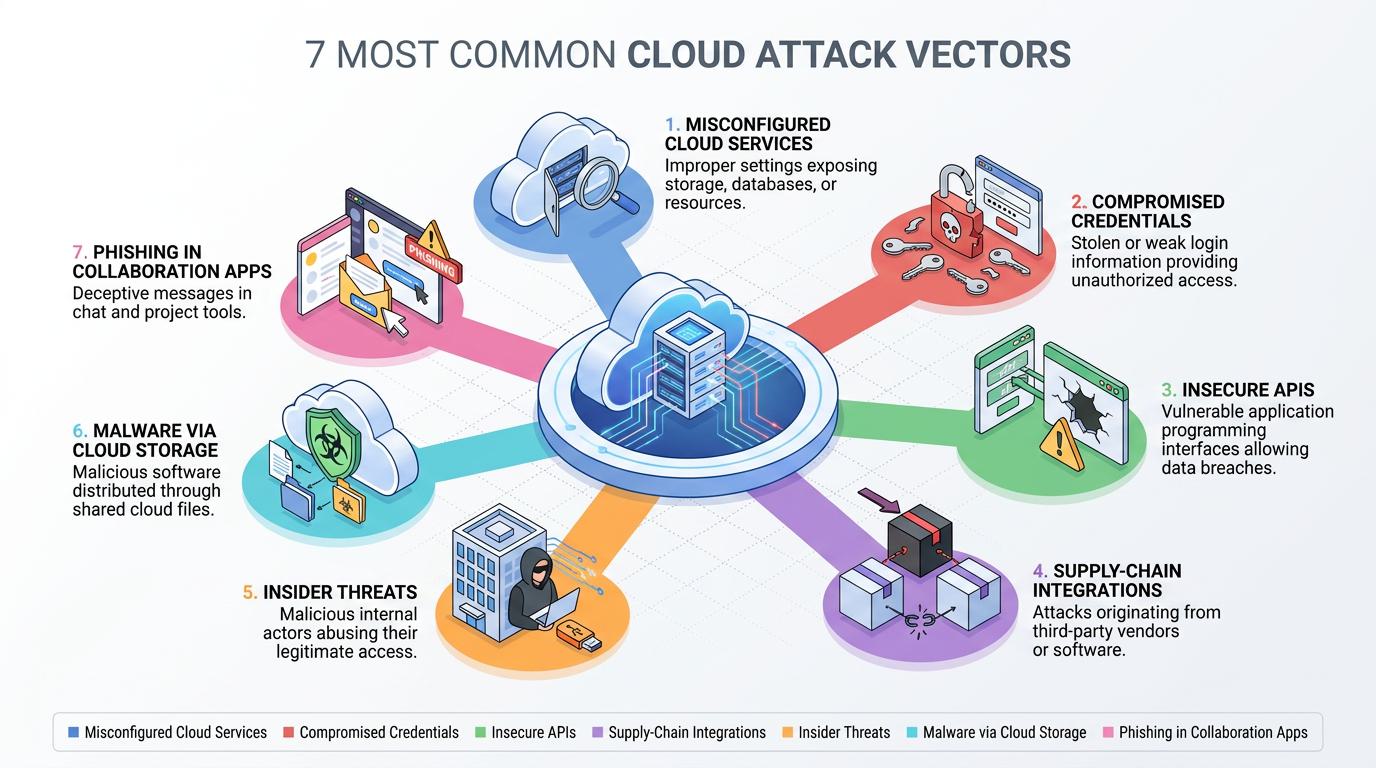
1. Misconfigured Cloud Services
Misconfigured cloud resources remain the fastest path for attackers to establish initial access, whether through exposed storage buckets or overly permissive Identity and Access Management (IAM) roles.
Publicly accessible storage, default-open security groups, and forgotten test instances are common misconfigurations that occur more frequently than most teams acknowledge. Attackers continuously scan for these vulnerabilities because a single error can expose entire datasets.
Teams can dramatically reduce this risk with a few coordinated practices:
- Automated Drift Detection: Tools that flag configuration drift and remediate risky settings before they're exploited.
- Infrastructure-as-Code Templates: Ensures every resource launches in a secure state by default, rather than depending on manual setup.
- Least-Privilege Access and Key Rotation: Limits what a single compromised credential can reach and shortens the window it stays useful to an attacker.
- Continuous Compliance Scanning: Surfaces new gaps as environments change, instead of relying on periodic audits.
Proactive posture management costs far less than incident response and keeps your cloud environment resilient as workloads scale.
2. Compromised Credentials and Account Takeover
Stolen or abused credentials open the door to your entire cloud estate. Account takeover is the fastest route to lateral movement, data theft, and business email compromise (BEC).
Credential stuffing campaigns recycle leaked username-password pairs until one works, while phishing lures harvest fresh logins and session cookies for immediate use. Attackers then hijack active sessions, spin up rogue resources, or exfiltrate sensitive data, actions that drive the average breach cost.
Once inside, they rarely stop at a single workload. With valid keys in hand, they abuse Open Authorization (OAuth) tokens. They create backdoor IAM users, and they reroute email flows to execute sophisticated BEC fraud, all before legacy controls notice anything amiss.
Protecting against account takeover requires layered identity defenses that start with eliminating password-only authentication. Phishing-resistant multi-factor authentication (MFA) built on WebAuthn can block credential-based attacks at the source. Conditional access policies that weigh device health, geolocation, and risk signals before granting sessions can create dynamic barriers that adapt to threat conditions.
Identity threat detection and response tools can catch privilege escalations or token misuse in real-time, while session anomaly monitoring flags impossible travel, vendor logins at unusual hours, and sudden OAuth grants. These systems can automatically revoke suspect tokens before attackers establish a persistent presence.
3. Insecure APIs and Interfaces
Application programming interfaces (APIs) sit at the core of every cloud workload. A single insecure endpoint becomes an immediate attack vector for data theft and service disruption.
You can rely on these interfaces to automate provisioning, integrate partners, and expose functionality to customers, yet each call widens the attack surface. Attackers exploit common issues, including broken authorization, excessive data exposure, and mass assignment, to bypass traditional perimeter defenses.
Strategic access controls and validation layers can mitigate this risk:
- Deploying least-privilege tokens that only allow necessary methods and resources.
- Using strict schema validation to reject unexpected parameters, rate limiting to absorb brute-force attempts, and zero-trust segmentation to isolate API tiers from back-end data stores.
- Embedding automated security testing into continuous integration/continuous deployment (CI/CD) pipelines to catch issues before production deployment.
Treating API security as a first-class discipline, on par with code quality and uptime, keeps your services open for business, not for attackers.
4. Supply-Chain and Third-Party Integrations
Compromised supply chains and third-party integrations create direct pathways for attackers to infiltrate production cloud workloads. Every vendor relationship inherits its security posture. A single poisoned update, abused OAuth token, or overly broad API permission can cascade across your entire environment. The scale of this risk is growing fast: the Verizon 2026 Data Breach Investigations Report found that third-party involvement in breaches reached 48%, up from 30% the prior year, a 60% increase in a single year.
Rigorous vendor risk assessments form the first line of defense:
- Require every partner to document secure development practices, disclose vulnerabilities promptly, and meet the same controls you enforce internally.
- Grant Open Authorization (OAuth) scopes according to least privilege; automation bots requiring only read access should never receive write permissions.
- Monitor connected apps continuously using automated tooling that flags unusual API calls or configuration drifts in real time.
- Demand a Software Bill of Materials (SBOM) for every packaged artifact, verify digital signatures before deployment, and run runtime code-integrity checks that quarantine binaries when hashes change.
These layered controls close the trust gaps attackers exploit and prevent third-party innovation from becoming a security liability.
5. Insider Threats (Malicious and Accidental)
Insider threats come in two forms: malicious actions, such as privilege misuse or data theft, and accidental errors, including oversharing public links or misconfiguring sensitive storage.
Because insiders operate with valid credentials, their activity blends in naturally. Detection becomes far harder than spotting external attackers. The challenge multiplies in cloud environments where permissions sprawl quickly and access extends to contractors, service accounts, and third-party applications.
Security awareness training helps, but it won't catch a rogue administrator siphoning data at midnight. Behavior-driven controls that surface anomalies in real time can close that gap:
- User behavior analytics can establish baselines for normal activity to promptly identify deviations.
- Deploy data loss prevention tools that inspect files, chat logs, and email for sensitive content before it leaves your environment.
- Zero-trust least-privilege policies can minimize the access any single identity has. Just-in-time access can also be used so that elevated permissions expire automatically after tasks are completed.
- Monitor each employee's typical patterns across email and collaboration platforms, alerting when seemingly legitimate sessions deviate from course, whether that involves mass-downloading source code or quietly creating public links.
These layered defenses turn insider behavior from a blind spot into a continuously monitored control point.
6. Malware and Ransomware via Cloud Storage and SaaS
Malware and ransomware now spreads through cloud storage and software-as-a-service (SaaS) platforms. It hides in collaborative drives and pivots to cloud virtual machines for crypto-jacking attacks that drain budgets while obscuring visibility.
Attackers place loaders inside shared drives and rely on synchronization to overwrite clean versions before moving to cloud workloads for persistent access. Once inside, modern strains disable version history, delete snapshots, and encrypt customer files, placing personal information and entire SaaS workspaces at risk. These infections often spread across connected systems well before a manual response team can react, which is why automated containment matters more than detection speed alone.
Teams can reduce this exposure with layered defenses:
- Object-level malware scanning on every upload and download.
- Immutable backups with routine restore tests to guarantee clean recovery, and runtime endpoint detection and response (EDR) agents on cloud workloads that halt encryption processes.
- Network segmentation to block east-west traffic between storage zones and compute nodes, and threat-intel-enriched detections to surface emerging ransomware families in SaaS logs.
Automatic isolation of any bucket, share, or virtual machine flagged as infected prevents cascade effects across your environment.
7. Phishing and Business Email Compromise in Cloud Collaboration Apps
Phishing-driven account takeover thrives in cloud suites because attackers impersonate trusted colleagues inside Microsoft 365, Google Workspace, Slack, and Teams. They quietly redirect funds and data before detection.
Once an inbox or channel is breached, threat actors stay invisible by replying within existing threads, manipulating SharePoint links, or requesting wire transfers through spoofed approvals, tactics that slip past legacy email security tools.
Modern attackers weaponize legitimate services, hijacked sessions, and look-alike domains that escape static rules. They abuse multi-channel workflows: a phishing link arrives in an email, the rogue invoice follows in Teams, and confirmation happens over Slack, creating an illusion of legitimacy across channels.
Legacy defenses fail because they focus on pre-delivery signatures rather than analyzing behavior patterns that reveal compromised accounts operating within your environment. Layered behavioral controls can help close that gap:
- Email security that learns typical sender-recipient patterns and flags deviations in real time.
- Strict Domain-based Message Authentication, Reporting, and Conformance (DMARC) policies that reject unauthenticated domains attempting to spoof your organization.
- Adaptive MFA that steps up verification when the login context changes.
- Mailbox-level anomaly monitoring to spot lateral movement across folders and rules.
- Real-time coaching that warns users the moment they click suspicious messages.
What It Takes to Stay Ahead of Cloud Threats
Staying ahead of these seven vectors comes down to one shift: treating detection and remediation as continuous, automated processes rather than periodic reviews. Configuration drift, credential abuse, and phishing all move faster than manual review cycles can track, and the organizations that close these gaps fastest are the ones that connect identity, email, and file-activity monitoring into a single response loop instead of managing each in isolation.