Product Updates
What's New
Recent Launches
Right Message, Wrong Person: When Legitimate Emails Become Data Breaches
A trusted contact can still be the wrong recipient. Discover how Abnormal’s Misdirected Email Prevention uses behavioral AI to catch recipient mistakes before confidential information reaches the wrong person.
Read the Launch BlogThe AI Security Suite Powered by Behavioral AI
Abnormal’s AI Security suite gives enterprises visibility and governance over the AI running in their business, control over the AI their employees use, and protection against AI-driven attacks being used against them.
Read the Launch BlogProactive Identity Risk Reduction for the Attacks That Matter
ISPM prioritizes identity misconfigurations based on real attack risk, helping security teams address the gaps attackers are most likely to exploit.
Read the Launch BlogEmail Security Evolved: Protect What Comes In, What Goes Out, and the People in Between
Protect what comes in, what goes out, and the people in between with new Abnormal capabilities for threat detection, data protection, and phishing training.
Read the Launch BlogDaily Updates
Week of Oct 26, 2026
- Oct 30, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of October 30
Strengthened detection of malicious links across supported URL-hosting platforms, with stronger remediation of URL-based attacks.
Improved detection of brand impersonation messages that use visual deception to evade text-only analysis.
Expanded detection coverage for compromised-sender attacks with a newly launched Sender Compromise model.
- Oct 29, 2026Identity SecurityNew Feature
Track Identity Posture Over Time
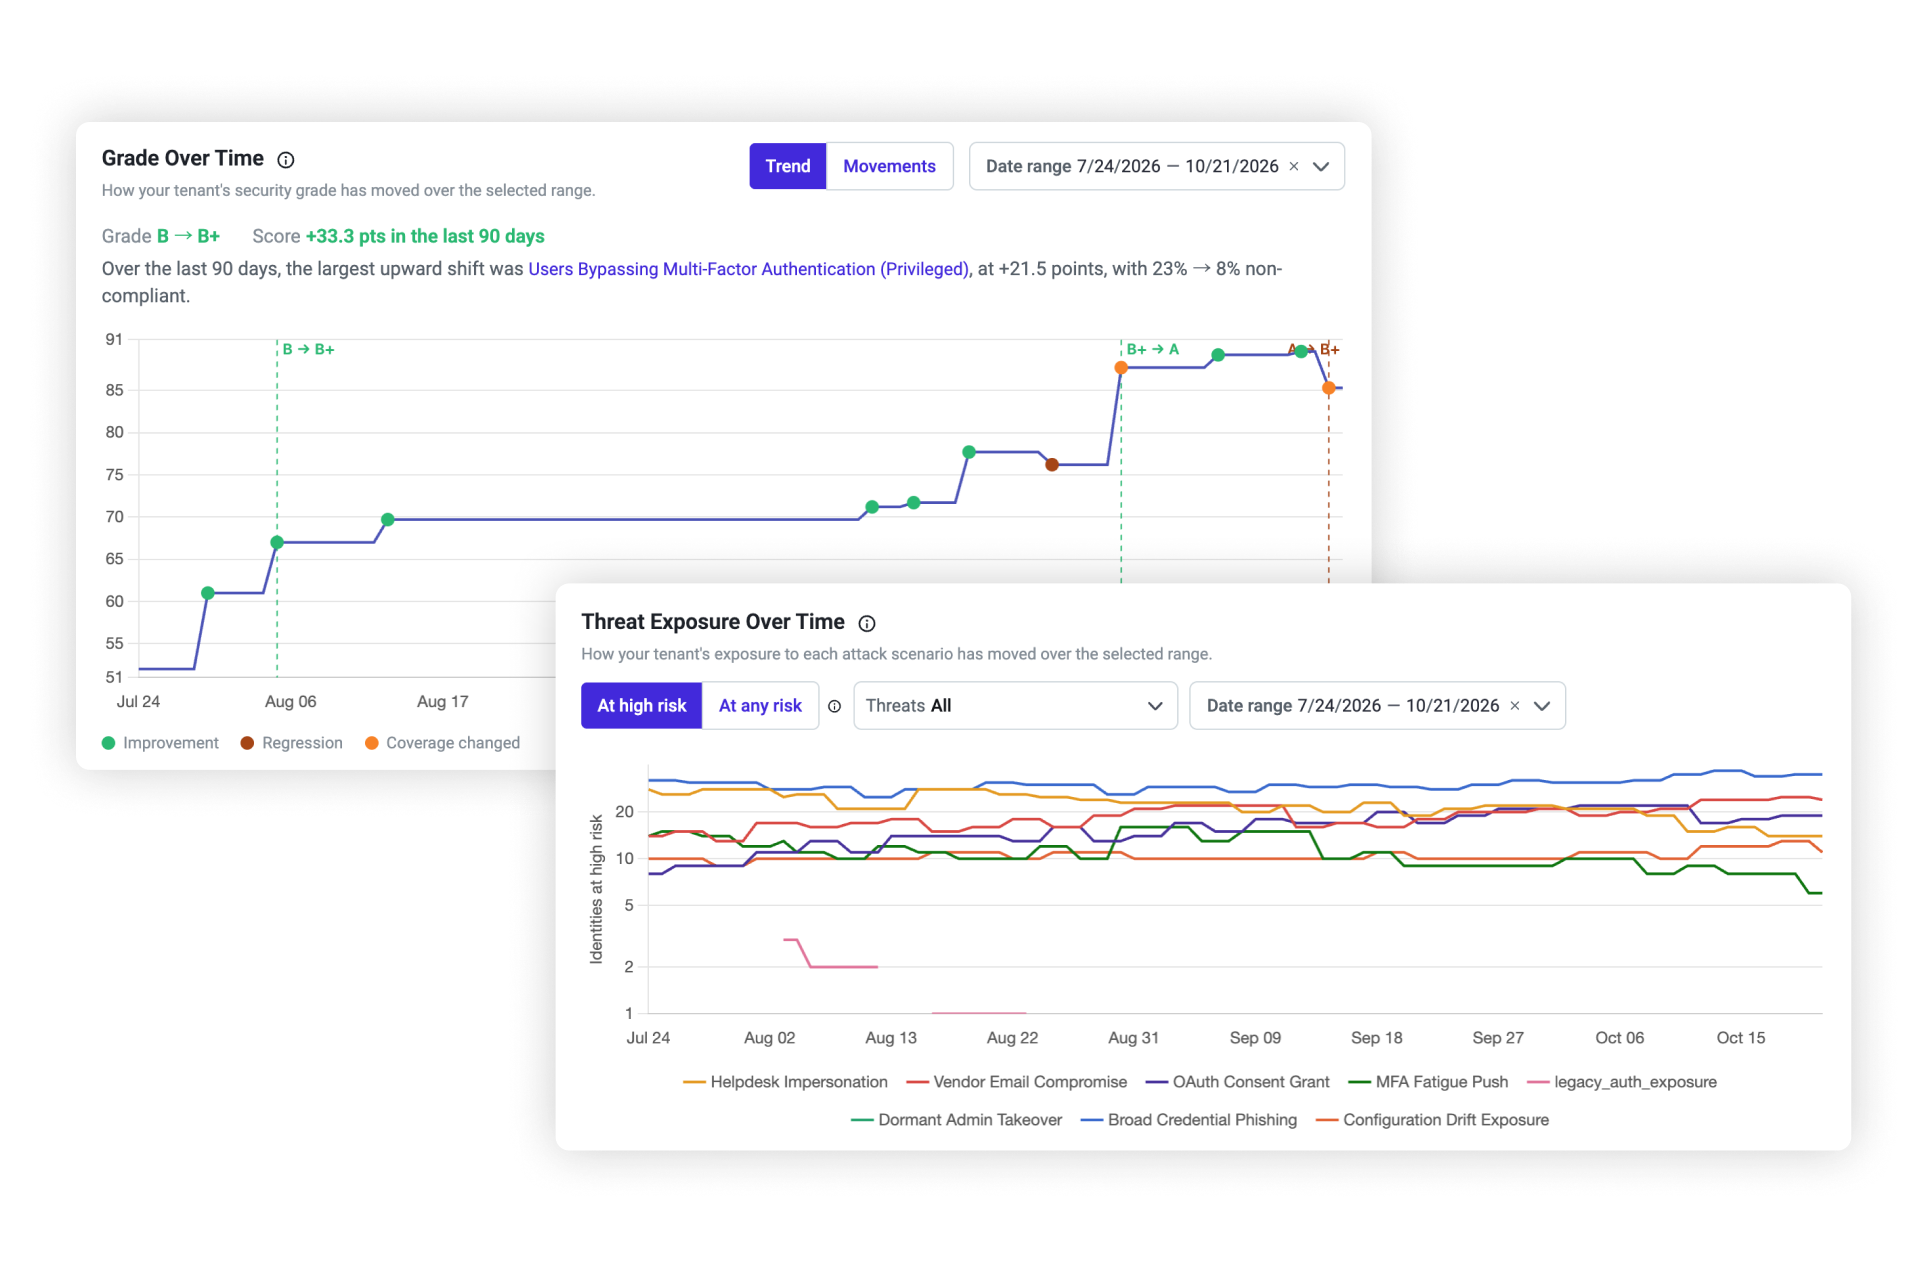
Identity Threat Protection now shows how your ISPM security grade and threat exposure change over time.
A point-in-time grade tells you where you stand today, but not whether your remediation work is paying off. Now admins can see how their posture has moved across a date range and how exposure to each attack scenario has changed along the way.
With this release:
— Track your security grade and score over time, with markers for improvements, regressions, and coverage changes
— See identities at high risk or at any risk for each attack scenario, such as Helpdesk Impersonation, Vendor Email Compromise, and MFA Fatigue Push, and filter by threat
— Review up to 180 days of history, or less if you deployed Identity Threat Protection more recently
Security teams can now show leadership measurable progress and catch regressions as they happen.
- Oct 29, 2026Identity SecurityNew Feature
Helpdesk Reset Risk Factors
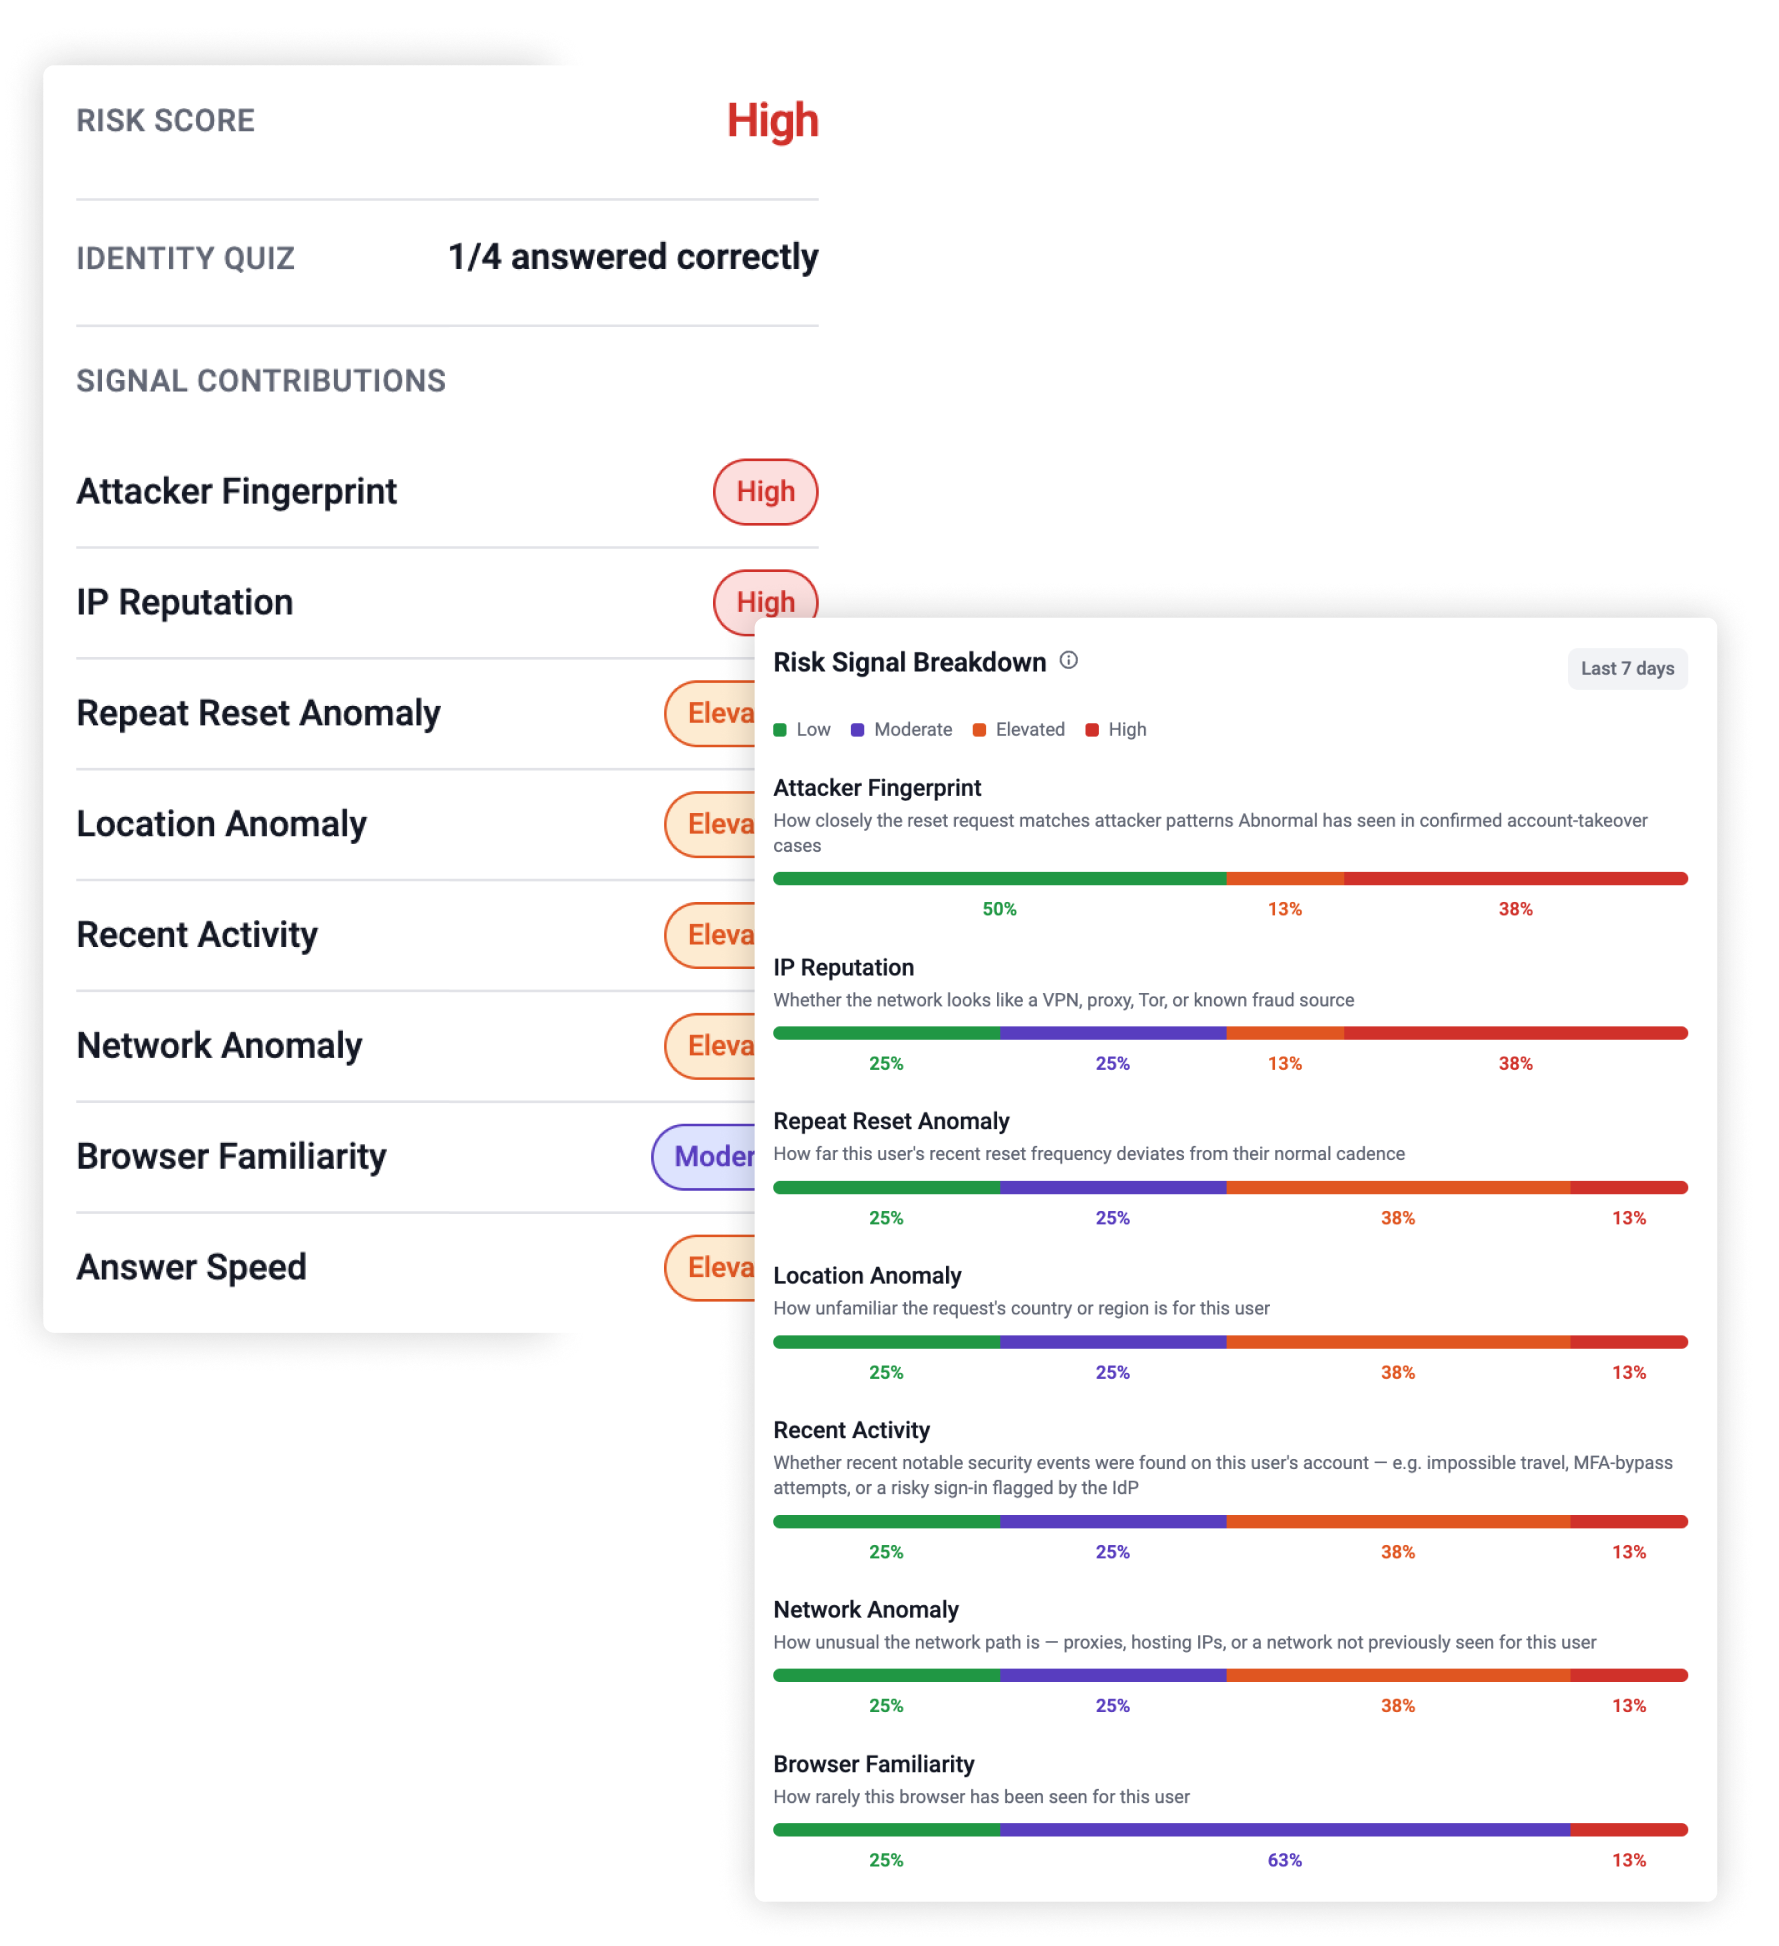
Identity Threat Protection now shows the risk signals behind each Adaptive Identity Reset risk score.
A risk rating is only useful if your team can see what’s behind it. Now help desk and security teams can expand any reset and see which signals contributed to the score, without having to guess why a request was flagged.
With this release:
— Expand any reset to see the signals behind its risk score, alongside the identity quiz result
— Review each signal’s rating (Low, Moderate, Elevated, or High), with plain-language definitions of what each one measures
— See the overall reset risk score on the same four-tier scale
Help desk teams can act with confidence on every reset request and explain why a request was flagged.
- Oct 27, 2026AI Data AnalystNew Feature
New and Enhanced AI Data Analyst Experience
AI Data Analyst is the conversational AI data analyst built into the Abnormal platform: ask a question by email or work conversationally in the portal, and get an answer grounded in your own Abnormal environment, typically within 15 minutes. Every response ties back to your actual threats blocked, people protected, and risk surfaced.
With this release:
Schedule recurring or one-time reports with smart defaults, or turn any question into an ongoing report with Schedule as Custom Report. Pick a frequency and AI Data Analyst derives the reporting window.
Track every report and conversation in one place with the new Report Repository, including versioned downloads and full history.
Manage reporting across every tenant from a single view, built for MSSPs and multi-tenant customers.
AI Data Analyst turns the questions your CISO and security team ask every day into answers you can act on, and turns those answers into reports that keep running on their own.
- Oct 26, 2026AI Phishing CoachImprovement
Simplified Settings for AI Phishing Coach
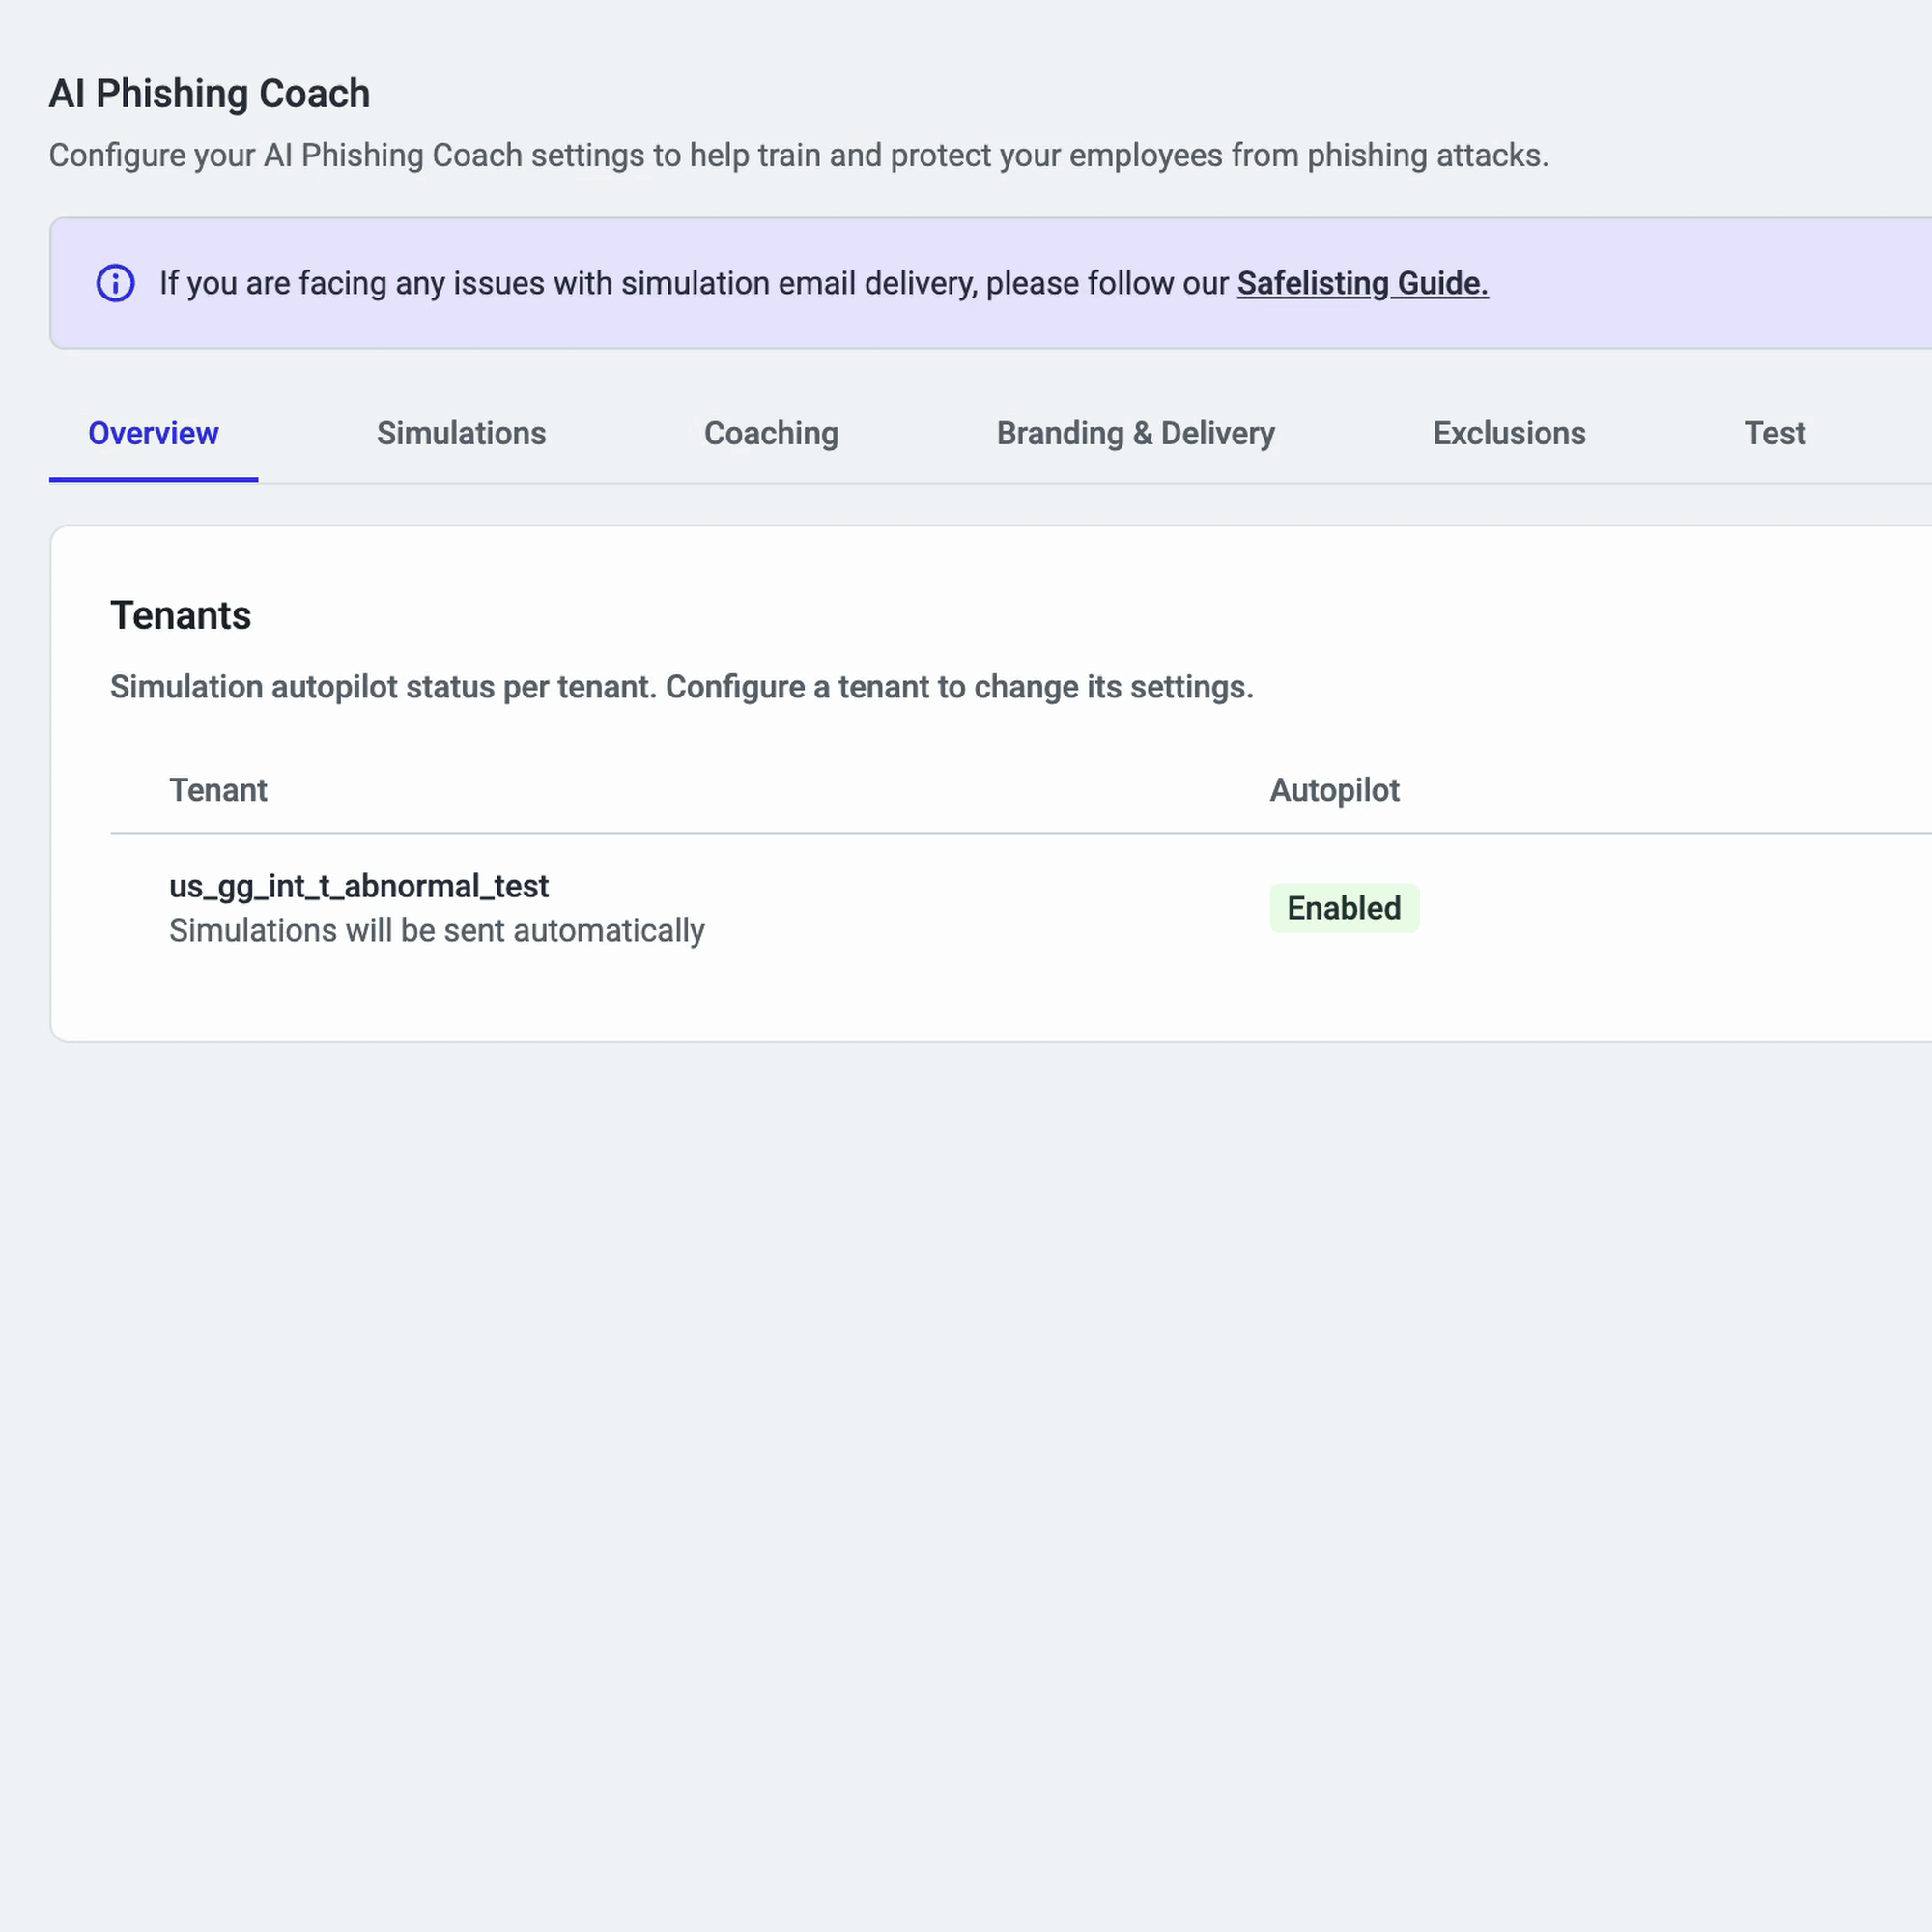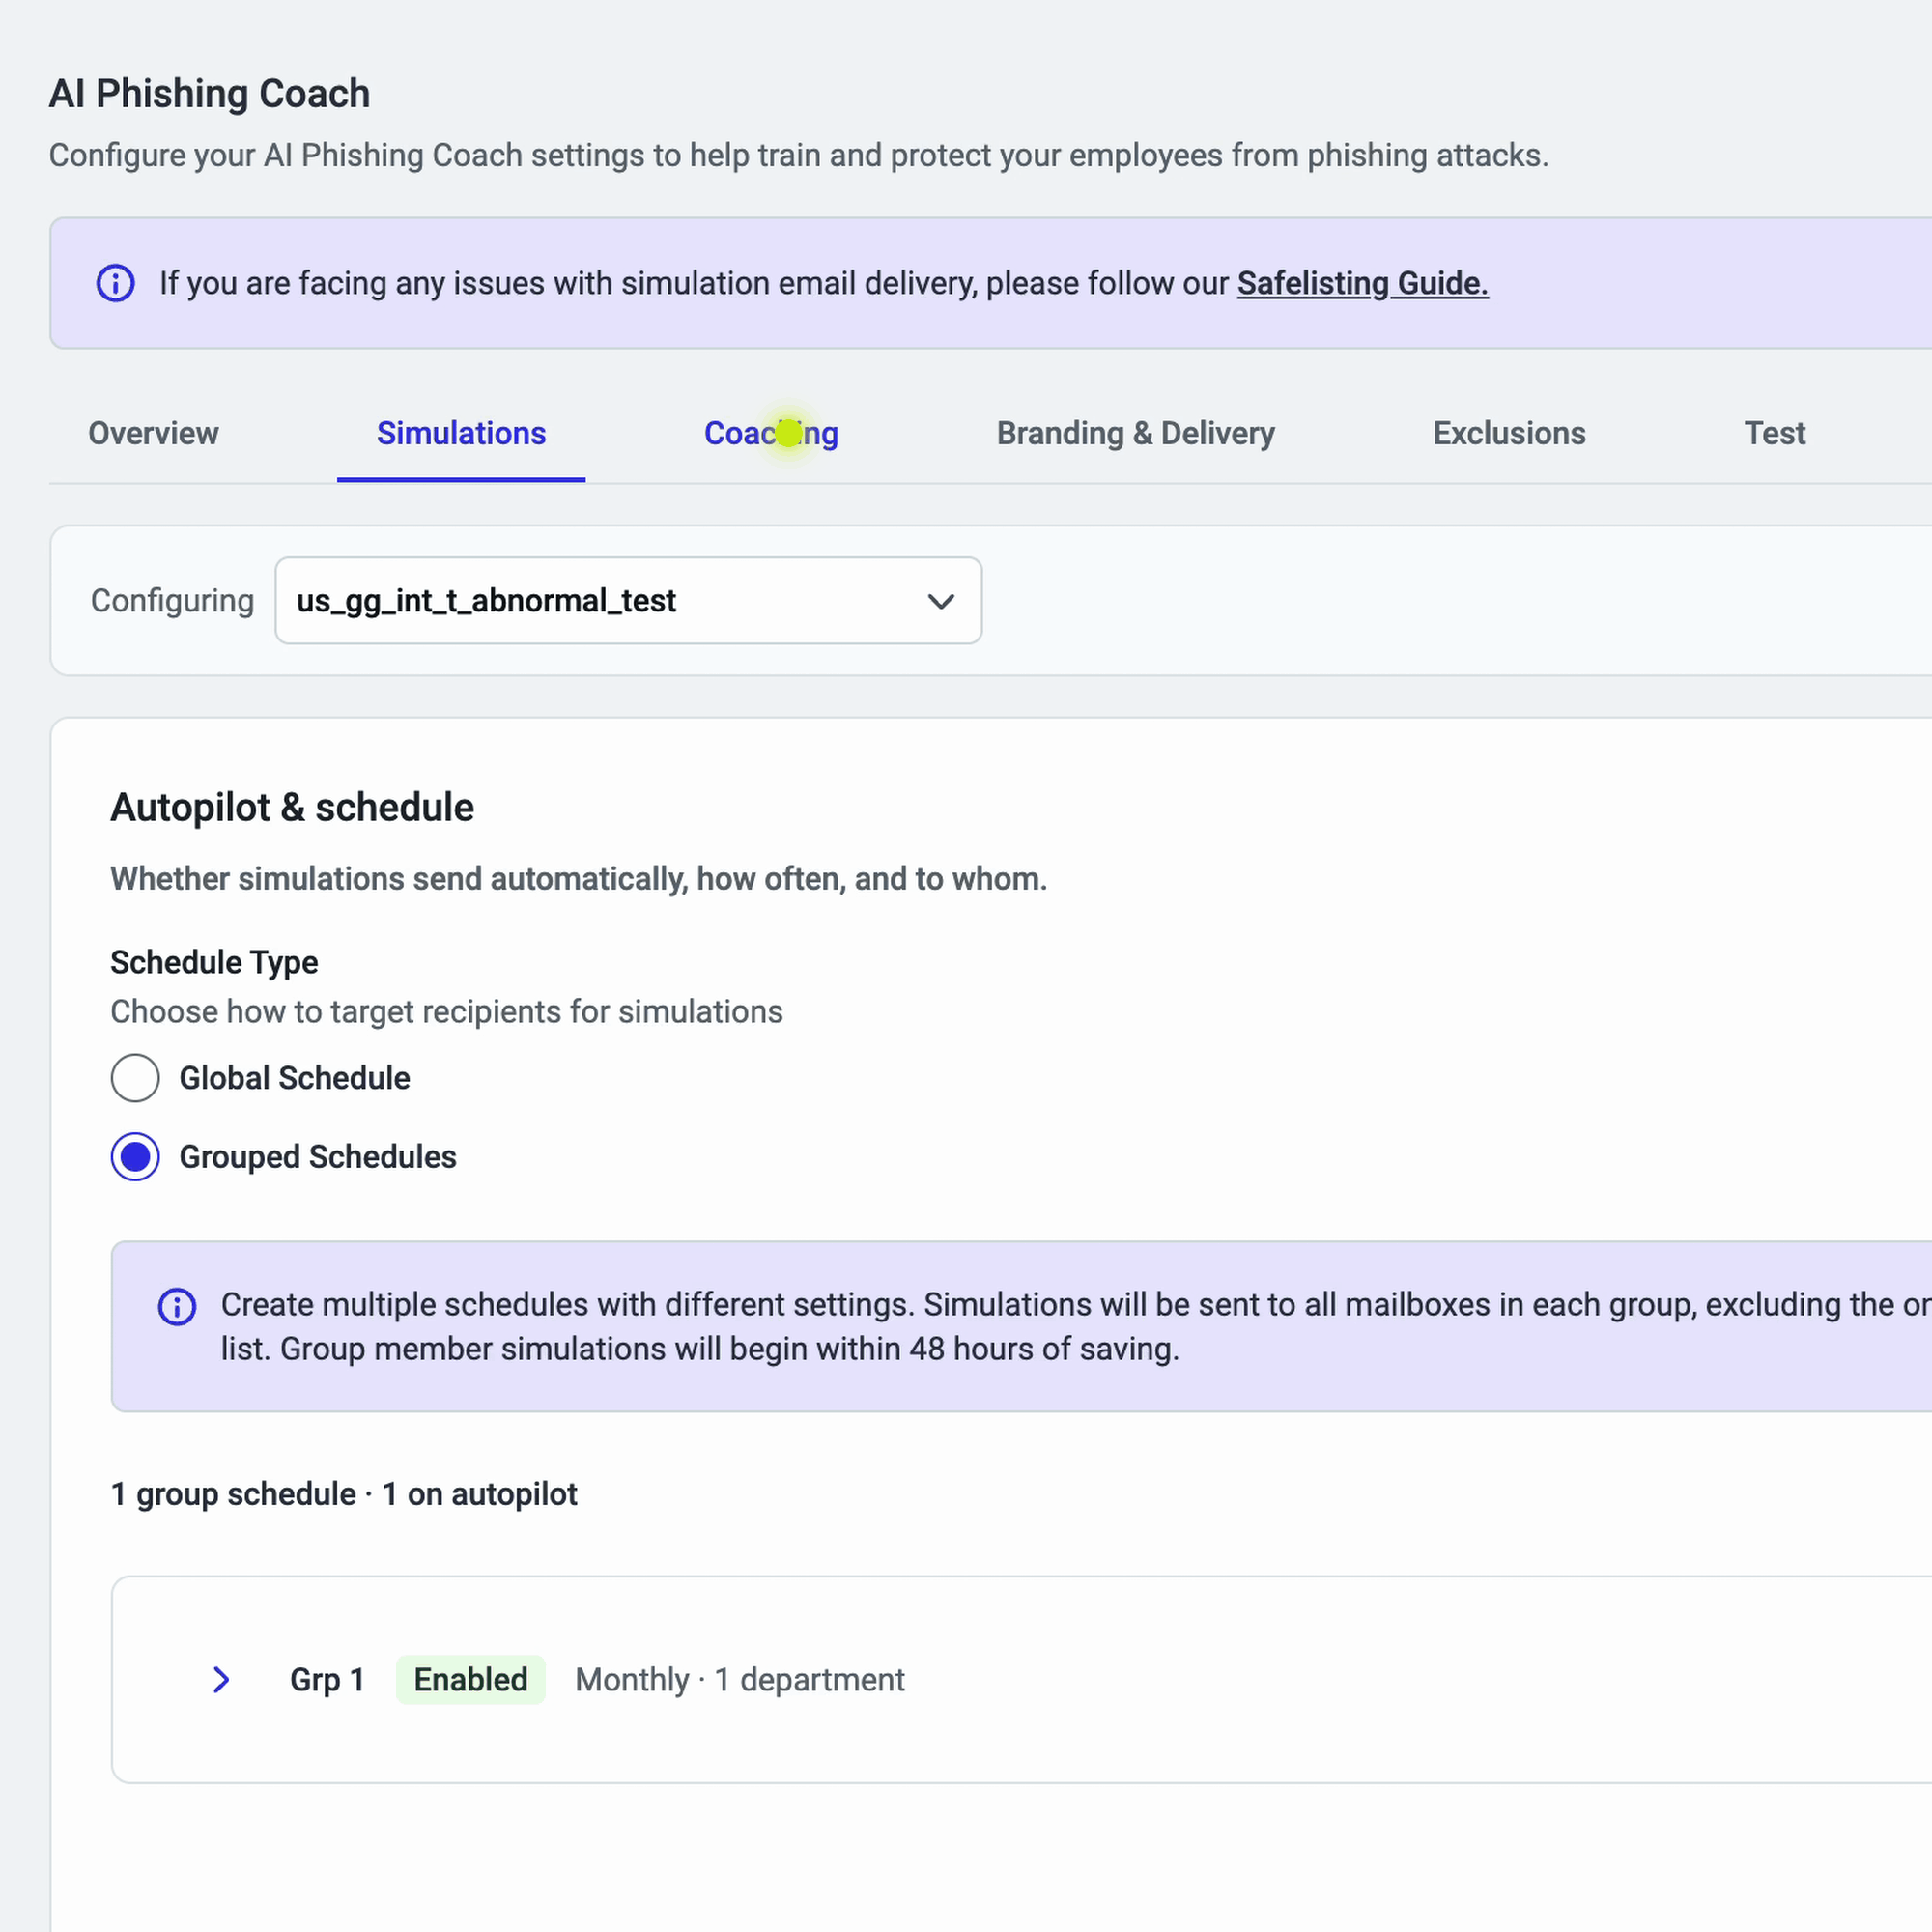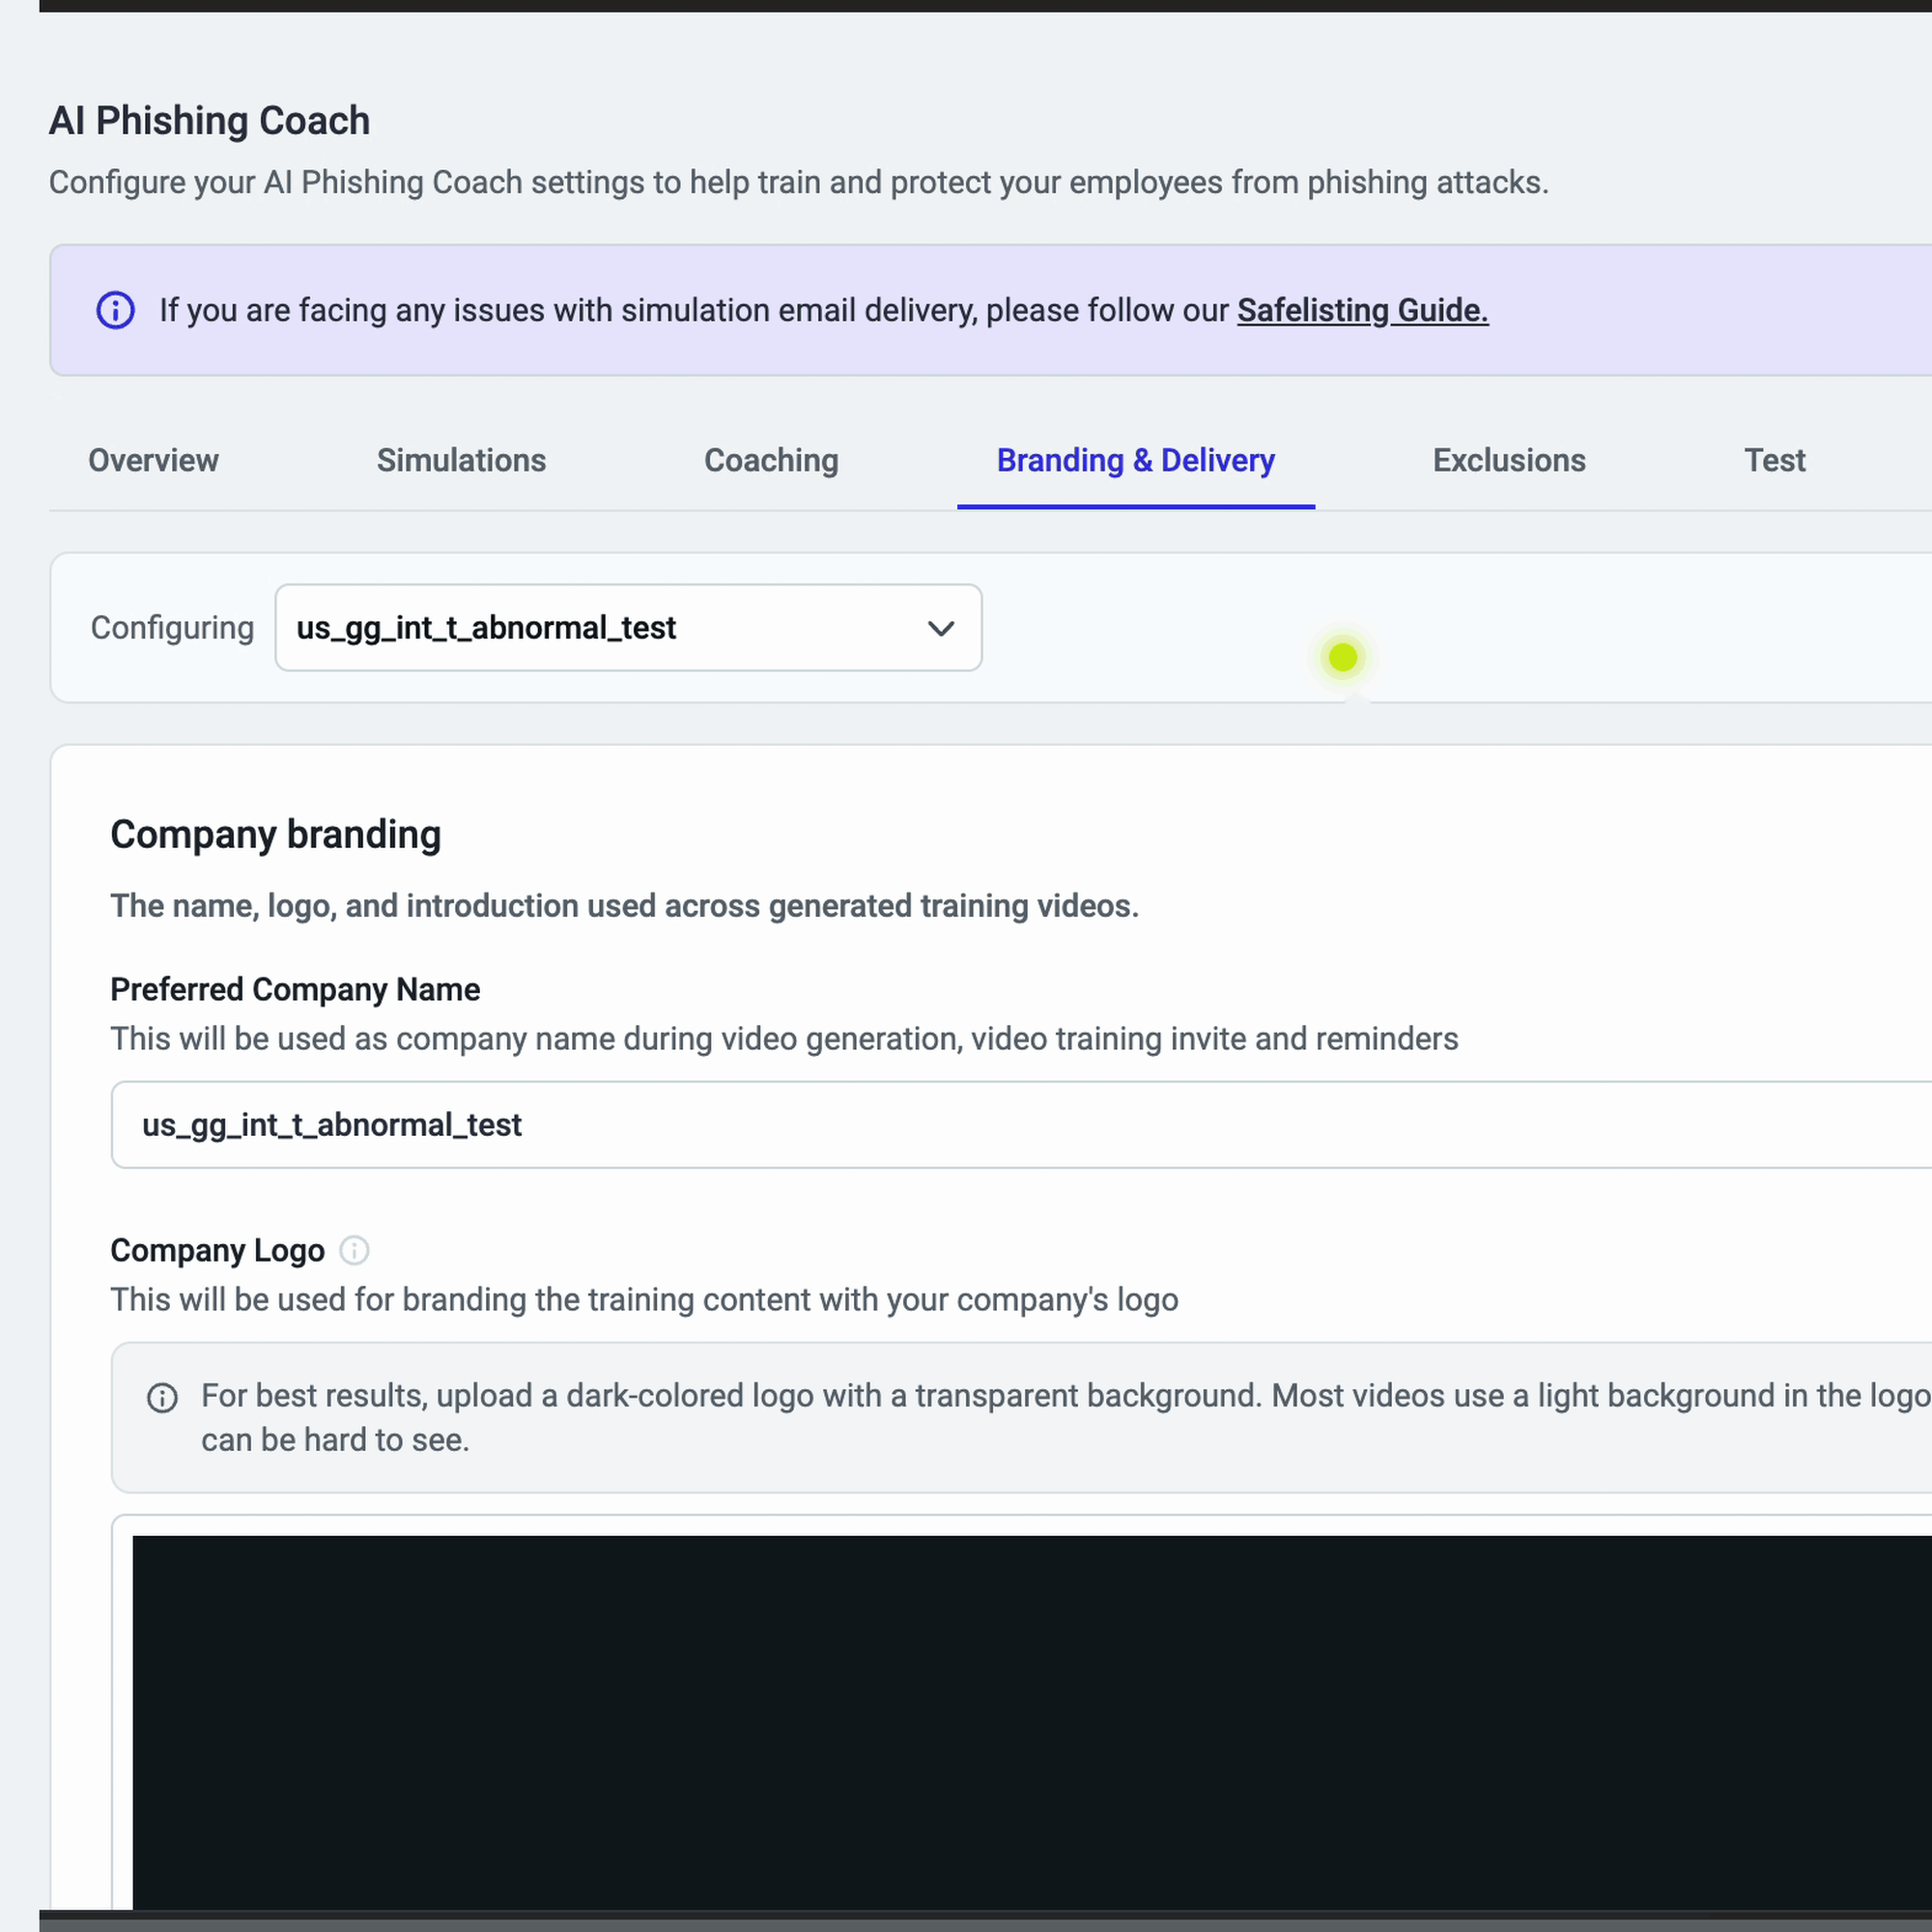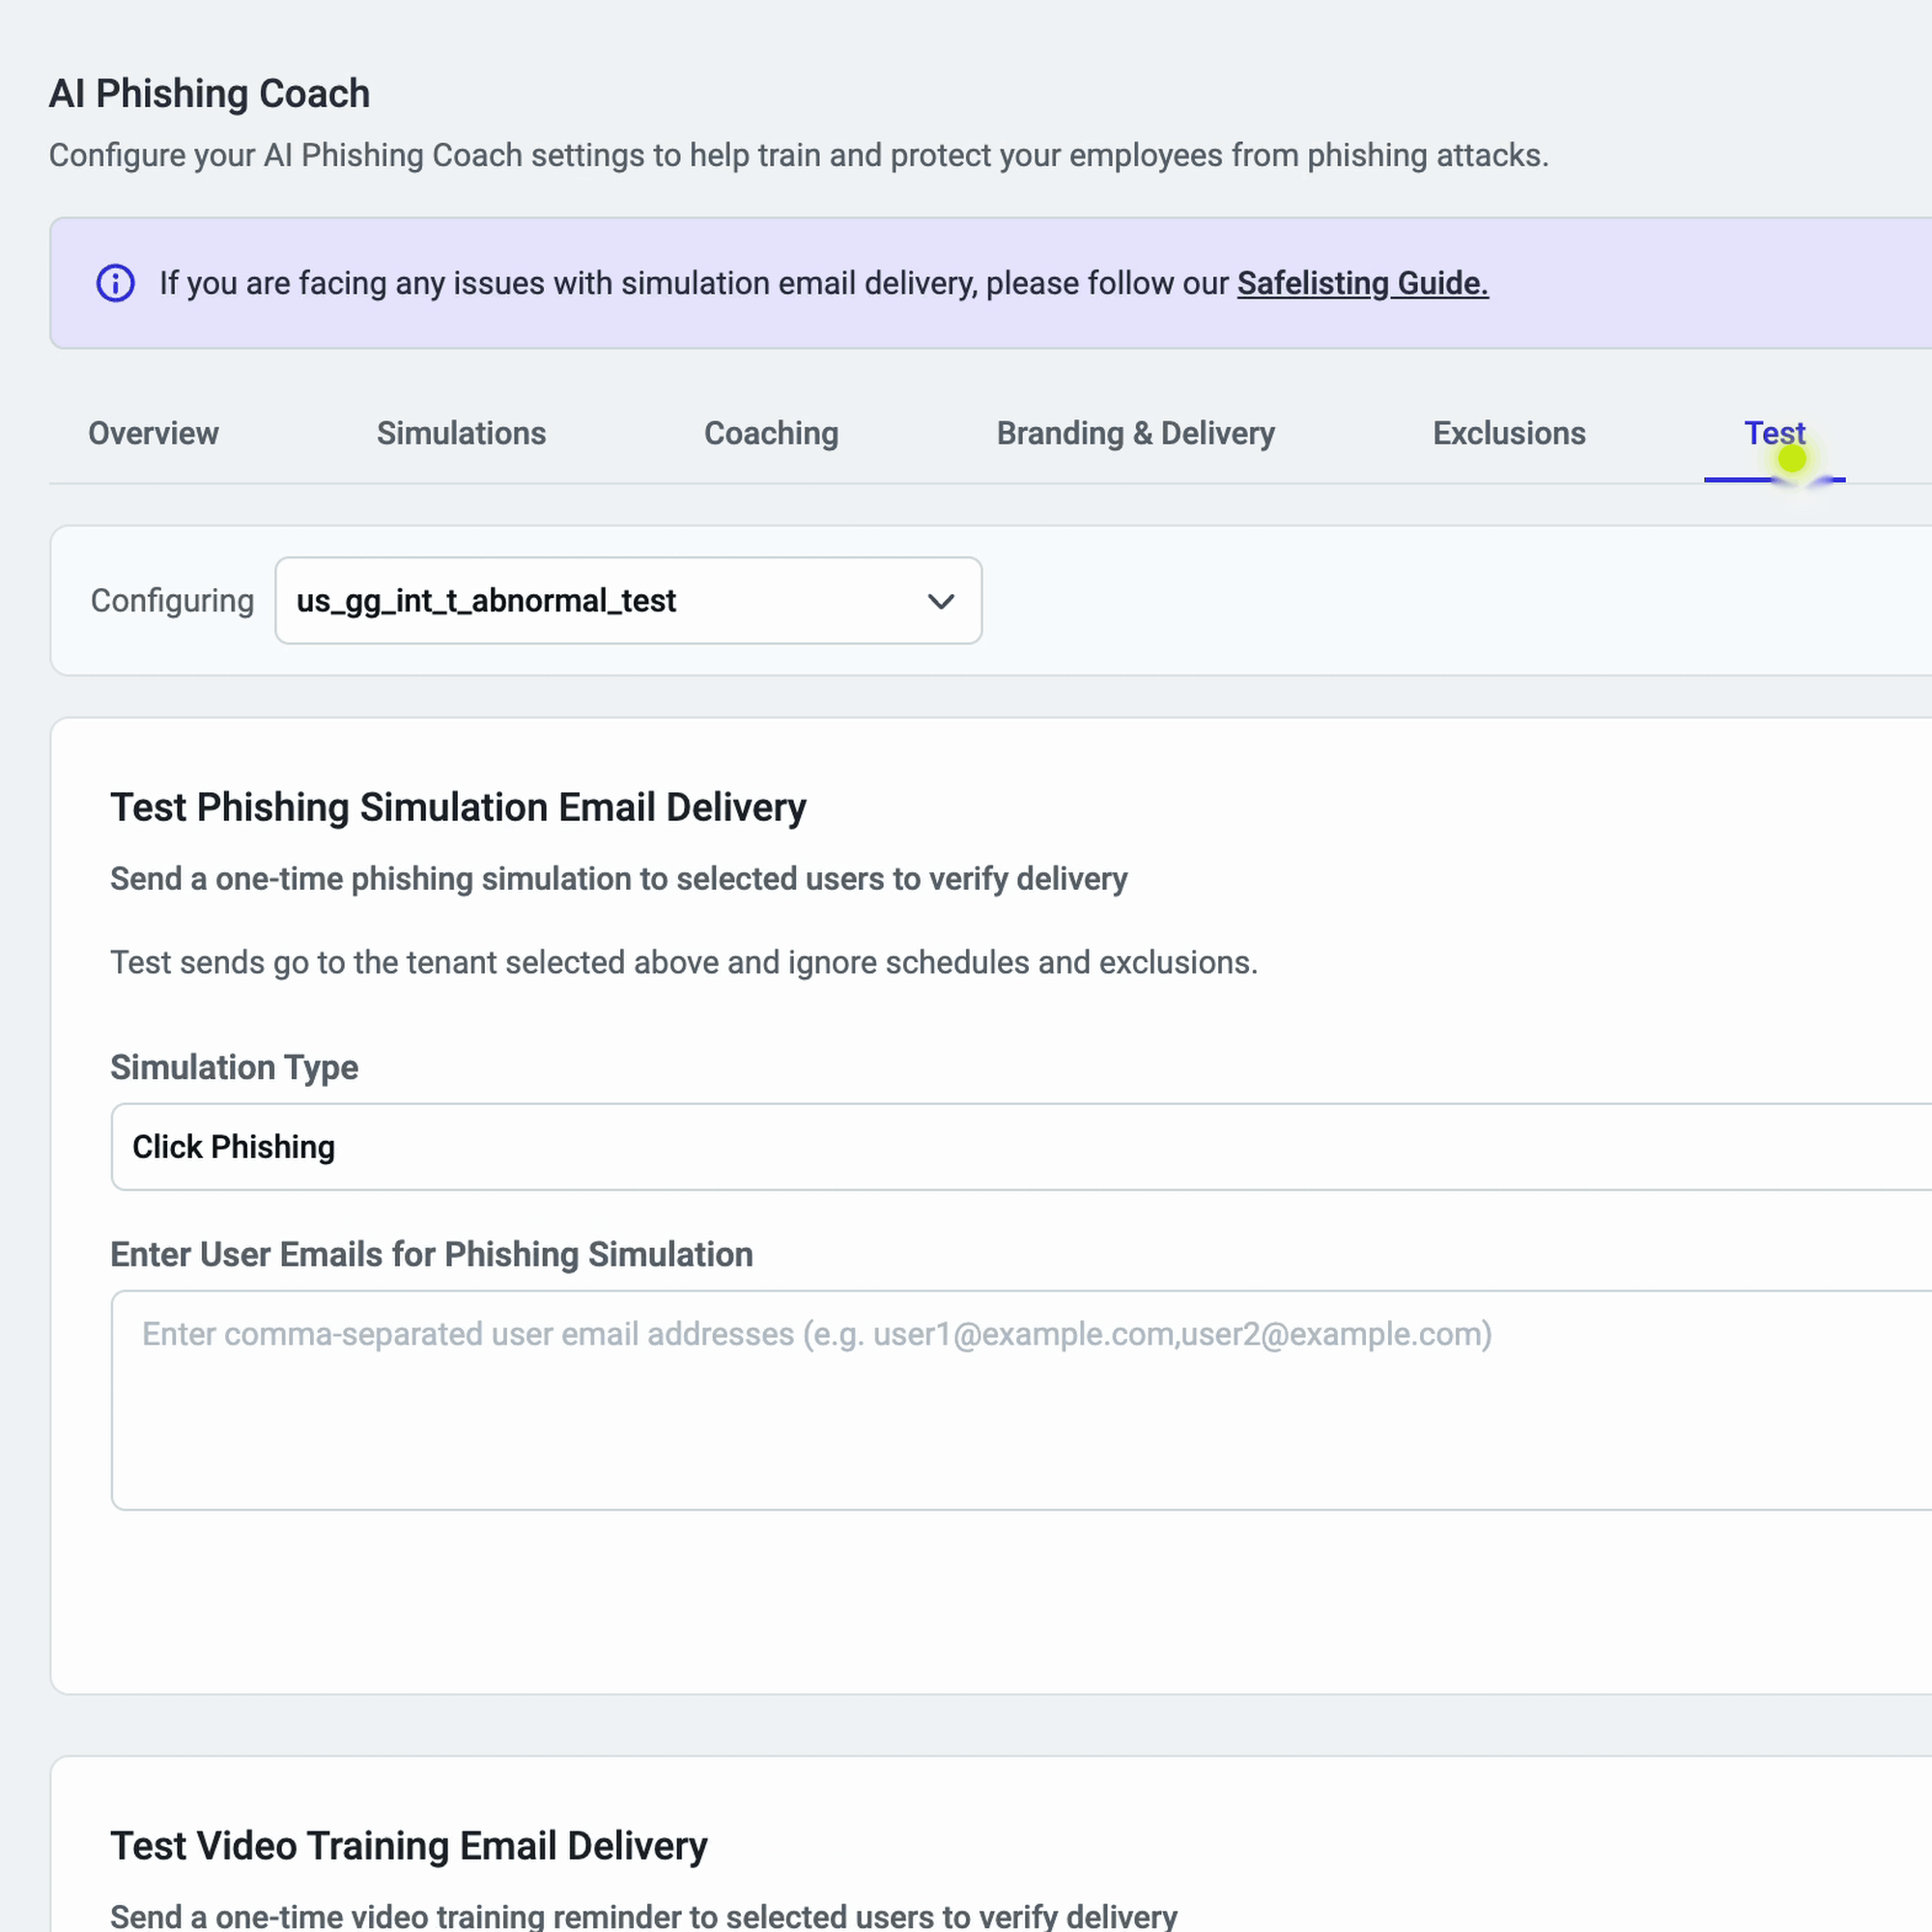
The AI Phishing Coach Settings page is now simpler to navigate, with every control grouped into six tabs by topic. Instead of clicking through a tenant table and nested drawers, admins start on an Overview of every tenant’s autopilot status and go straight to Simulations, Coaching, Branding & Delivery, Exclusions, or Test. Every setting is still there, at most two clicks away, with saved configurations unchanged.
With this release:
Settings are grouped by topic, starting with an Overview of every tenant’s autopilot status
- Tenant Level / Account Level labels show what each change affects
- One Save covers edits across every tab, with the option to discard them
Setting up and fine-tuning AI Phishing Coach has never been easier, especially for organizations managing multiple tenants.
- Oct 26, 2026PlatformNew Feature
Segmented SaaS: Separate Abnormal Tenants on One Email Tenant
Segmented SaaS is built for organizations whose business units, subsidiaries, regions, or agencies share one email tenant but need to be managed separately. Each segmented tenant has its own admins, views, alerts, and data, giving these organizations a clear path to meeting business and compliance requirements for separation without running multiple cloud email tenants.
With Segmented SaaS:
Create a separate Abnormal tenant for each group, with users assigned by email domain, directory group, or a list of user principal names
Give each tenant its own admins, so every team sees only its own users, alerts, and data
Keep one integration across every segmented tenant, with nothing new to authorize
Segmented SaaS lets security teams align Abnormal with how their organization is structured and governed, while keeping a single email tenant to manage.
Week of Oct 19, 2026
- Oct 23, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of October 23
Improved detection of malicious links by factoring URL verdicts into message scoring, with new coverage for Google Sites-hosted attacks
Launched a visual detection model that catches brand-impersonation attacks hidden in email screenshots and other image-based content
Week of Oct 12, 2026
- Oct 16, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of October 16
Improved graymail classification of promotional messages disguised as replies, distinguishing them from genuine conversations
- Oct 13, 2026Security Posture ManagementImprovement
CIS Microsoft 365 v7.0.0 Support in Security Posture Management
Security Posture Management now checks your Microsoft 365 configuration against the latest CIS Microsoft 365 Foundations Benchmark, v7.0.0.
As Microsoft 365 changes, CIS revises its benchmark: it adds controls, rewrites others and retires ones that no longer apply. This release brings SPM’s checks up to v7.0.0 and labels every change. Security teams can see which findings are new, which have refreshed guidance and which checks are going away.
With this release:
- 28 new checks based on the latest CIS guidance, marked NEW
- 121 existing checks moved to v7.0.0. The 47 with refreshed guidance are marked UPDATED
- 14 checks that CIS withdrew are marked DEPRECATED and will be removed in 30 days
- A v7 filter on the Evaluations page lets you review the new benchmark on its own
Teams that report against CIS can trust that SPM results match the current benchmark, without remapping controls by hand. The tags also make it easier to explain changes in posture results to auditors and leadership.
Read More
Week of Oct 5, 2026
- Oct 9, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of October 9
Strengthened detection of emails from newly registered domains, expanding coverage of live domain-age and registration signals
- Oct 9, 2026AI Phishing CoachImprovement
Bring Your Own CSV
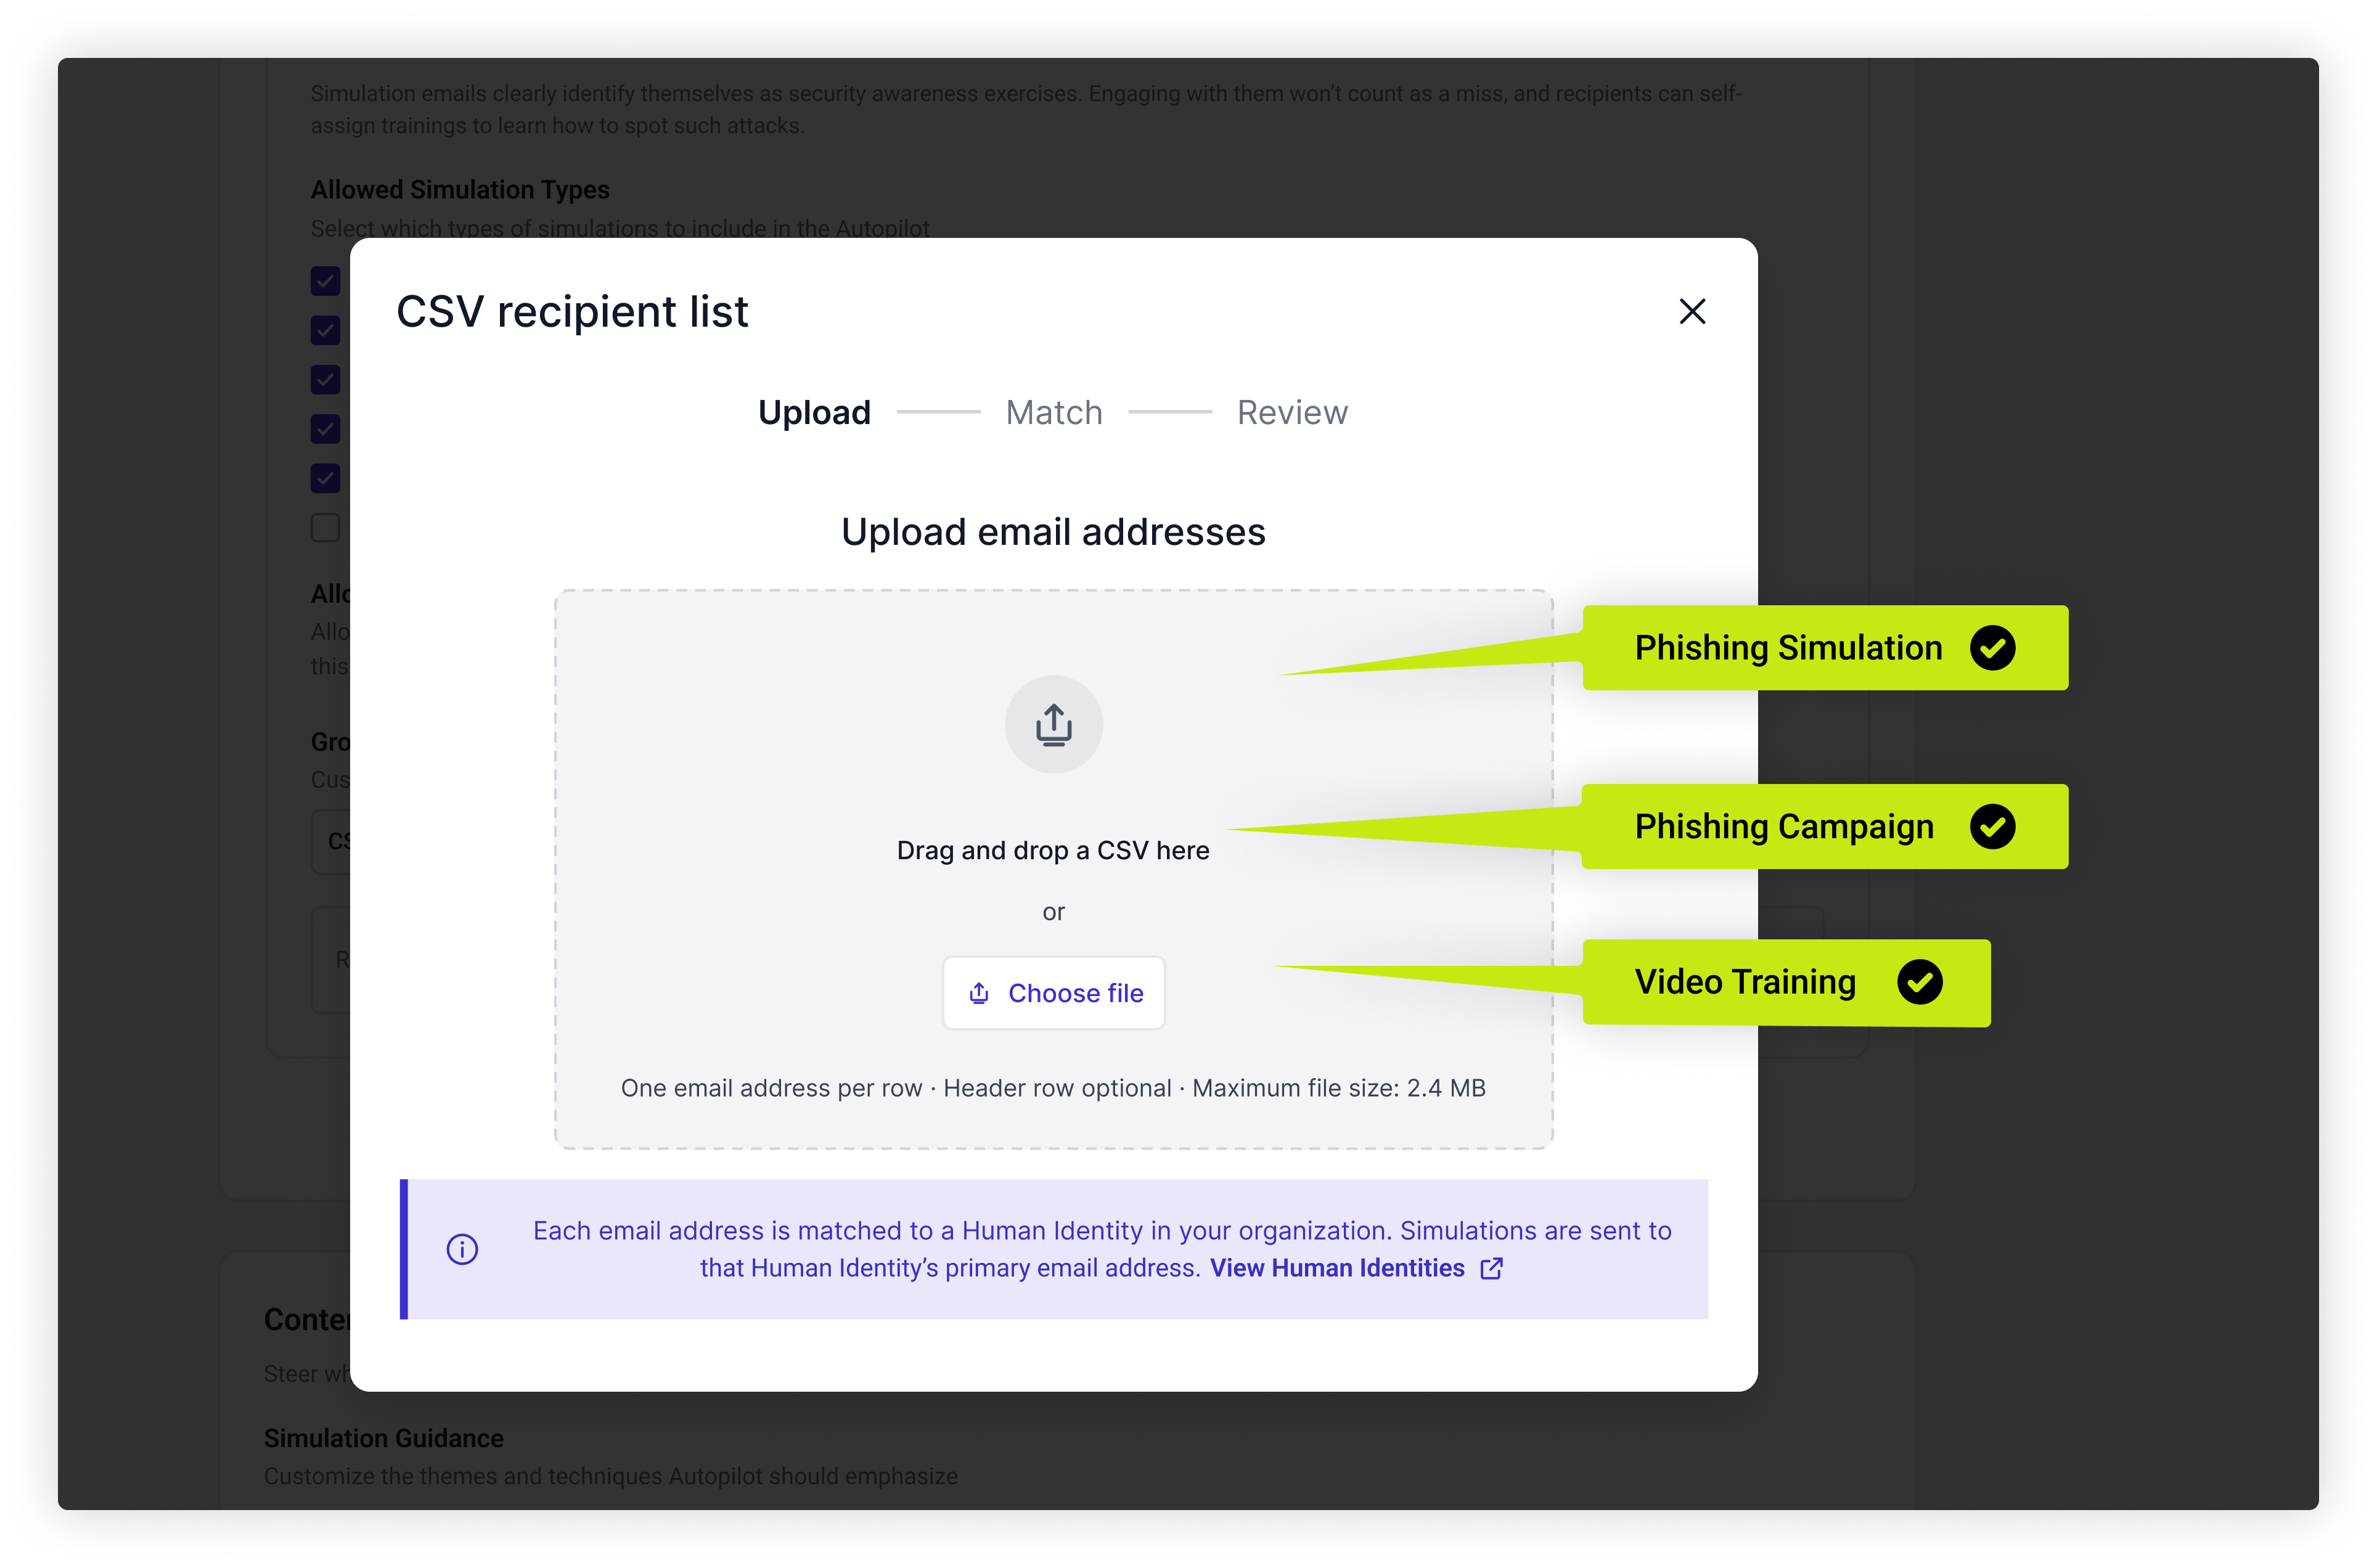
Not every directory reflects how a company is actually organized. Now admins can upload their own list of recipients via CSV instead of relying on Departments or Entra and Google Groups, and review exactly who’s included before anything goes out.
With this release:
Upload a CSV to simulation schedules, one-off campaigns, or video training assignments
Review matched, unmatched, and redirected addresses before applying the list
Edit and re-upload the file anytime to keep membership current (one email per row, up to 2.4 MB)
Security teams can now reach every subsidiary, brand, and pilot group with the right simulations and training, no matter how their directory is structured.
- Oct 8, 2026PlatformNew Feature
New Threats API Message Endpoints
Abnormal now offers two new REST API endpoints that provide direct access to threat message data: one retrieves threat message data in bulk, and the other retrieves full details for a single message.
With this Release:
- Retrieve threat messages in bulk over a selected timeframe with core metadata, pagination, and the same filters available in the Threat Log.
- Retrieve full details for one message, including attachment analysis, insights, and URLs.
Week of Sep 28, 2026
- Oct 2, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of October 2
Enhanced detection of lateral phishing from compromised senders, strengthening protection for internal-to-internal messages
- Sep 30, 2026AI Security MailboxNew Feature
AI Detection Engineer: A Faster, More Visible Response to Every Report
AI Detection Engineer acts as an extension of your SOC: when a report in Detection 360 or AI Security Mailbox is confirmed a misjudgment, AIDEN investigates it the way an analyst would, builds a sophisticated, customer-specific detector, tests it against your own traffic, and deploys it once it clears Abnormal's efficacy bar, no rule-writing required.
With this release:
See AIDEN’s fast, visible response to confirmed misjudgments reported via Detection 360 and AI Security Mailbox in one unified dashboard
Get faster turnaround from report to live fix, as AIDEN investigates, builds, tests, and deploys automatically
Track every deployed detector with full traceability to every message caught and false positive suppressed
AI Detection Engineer turns reports into faster, fully traceable responses, no rule-writing, no waiting. It's live today for all US and EU commercial customers, no configuration required.
- Sep 30, 2026AI Phishing CoachNew Feature
Executive-Ready PDF Report
AI Phishing Coach's new Executive Report turns your training program results into a leadership-ready PDF in one click. The branded report covers program performance, where risk concentrates, and which employees to coach or recognize, with AI-generated analysis alongside key charts.
With this release:
Share results with leadership using Export Executive Report on the Executive Dashboard or the Reports page
Apply any date range or filters to show a broad or targeted view
Find past and new reports in Recent Reports on the Reports page
The Executive PDF Report turns program data into a story leaders can act on, with no screenshots and no manual prep. It's live today for all AI Phishing Coach customers.
- Sep 28, 2026PlatformNew Feature
CSV Export for Supply Chain
Security and risk teams often need vendor data outside the platform, for compliance audits, board reporting, or cross-referencing with other systems. Supply Chain now supports one-click CSV export, giving teams instant, flexible access to their full vendor dataset for analysis wherever they need it.
Navigate to Behavioral Intelligence > Supply Chain and click Export to CSV
Receive your download automatically, including a Tenant column for multi-tenant environments
Simplify audits, compliance reporting, and vendor risk analysis
Week of Sep 21, 2026
- Sep 25, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of September 25
Added internal-account compromise detections to catch targeted attacks disguised as routine coworker email
Improved precision of subject-matching detection, reducing false positives without sacrificing threat coverage
- Sep 25, 2026Identity SecurityNew Feature
Adaptive Identity Reset Enrollment
Identity Threat Protection admins can now filter the Adaptive Identity Reset enrollment roster by department, job title, VIP status, and admin status, sort by name or title, and search across the complete directory.
This makes enrollment easier to manage at scale, helping admins quickly find the users they need without manually working through large rosters.
- Sep 23, 2026AI Phishing CoachImprovement
Targeted Video Training by Groups or Departments
AI Phishing Coach admins can now assign Video Training to specific AD / Entra ID groups, Google Groups, or departments instead of manually selecting and maintaining recipients. As employees join or leave a targeted group or department, they are automatically added to or removed from the training assignment.
This gives admins more control over who receives training while making targeted programs easier to manage at scale. Training stays aligned with changing teams and organizational structures without requiring admins to continually update recipient lists.
Week of Sep 14, 2026
- Sep 18, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of September 18
Strengthened detection of internal account takeover, using sender-behavior signals to catch hijacked accounts blasting phishing links to unfamiliar domains
Enhanced detection of file-share phishing from unknown senders that abuse SharePoint