Key Insights
Infostealer malware marks a major shift in how attackers steal credentials. Cybercriminals have moved past capturing individual keystrokes toward mass identity theft that scoops up entire logins in one pass. In June 2025, researchers revealed a cache of 16 billion records gathered by infostealers, though security experts later clarified the figure was a cumulative compilation of previously stolen data rather than a single breach.
Keyloggers still cause real damage, but infostealers put a wider set of stored credentials and live sessions at risk. Understanding where the two diverge is what lets a defender see why a password reset stops one threat and barely slows the other.
Key Takeaways
- Infostealer malware collects stored credentials, browser data, and session material in a single pass, while a keylogger only captures what a user physically types.
- Session theft is the sharpest dividing line: stolen authentication cookies let an attacker resume a logged-in session and slip past multi-factor authentication.
- Infostealers evade signature-based tools because each build looks different, runs in memory, and imitates trusted software.
- A single infection rarely stays contained, since harvested credentials are resold and bundled by brokers into larger intrusions.
What Keyloggers Do and How They Work
Keyloggers capture typed input, handing attackers raw text they still have to sort through for anything useful.
These programs record the keystrokes a user makes, so an attacker receives a stream of characters and has to extract passwords, payment details, or personal information from it. Keyloggers hide deep in the operating system and intercept keyboard activity through system hooks, attaching to the input functions on Windows and using equivalent techniques on Mac and Linux.
Because a keylogger only needs to capture text, it stays small and lightweight. Most variants store encrypted logs locally, then send them to the attacker in batches over email, FTP, or web requests. The attacker analyzes that data offline, either by hand or with simple scripts that hunt for patterns like @, cc, or pwd=.
That design carries a built-in tradeoff. A small footprint helps keyloggers slip past routine security scans, but it also means they miss the browser cookies, session tokens, and stored passwords that infostealer malware collects on its own. They stay dangerous in targeted campaigns all the same: one recent variant spread through phishing emails and used scripting to stay quiet, logging keystrokes and lifting saved browser credentials before exfiltrating the data through SMTP and Telegram bots. The limitation is scope, not severity, and a keylogger that lands on a finance manager's machine during invoice season can still do real harm.
What Makes Infostealer Malware Different
Infostealer malware differs from a keylogger because it harvests a broad slice of identity data at once instead of waiting for a user to type a specific secret.
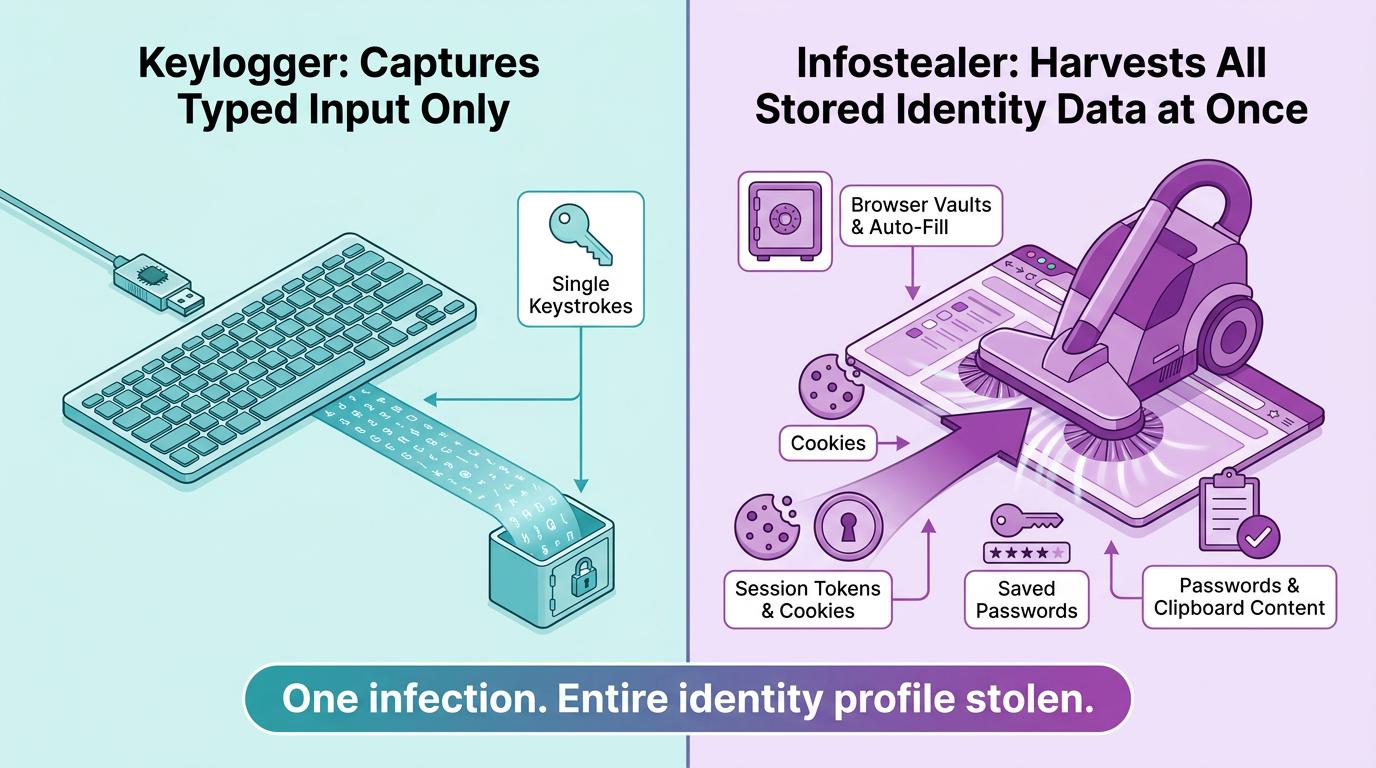
Where a keylogger listens for typed input, an infostealer behaves like a credential theft machine that sweeps the whole device. In one pass it pulls saved browser logins along with the session material that lets an attacker replay those accounts across cloud and business systems.
Large-scale credential theft has been escalating as threat actors trade noisy smash-and-grab tactics for quieter, more thorough collection, and that shift is exactly what separates this class of malware from older tools. Three traits define how it works.
Modular Malware Architecture
An infostealer runs as a set of specialized modules, each aimed at a different kind of data such as browser cookies, cryptocurrency wallets, or saved application logins. That structure makes the malware adaptable, because an operator can switch modules on or off and swap them out depending on how valuable the target looks and how much scrutiny they want to avoid.
Many of these tools are sold on a malware-as-a-service (MaaS) model, which puts advanced data theft within reach of operators who could never build it themselves. The business model is what keeps the threat moving: sellers ship frequent updates and buyers test new delivery tricks in the wild, so collection logic changes faster than defenders can catalog it.
Expanded Data Collection
An infostealer is not limited to typed input, and that changes the risk profile completely. Beyond saved browser credentials, it can reach into autofill data, clipboard contents, and whichever applications happen to be open. A keylogger captures a password only if the victim types it while the malware is running, whereas an infostealer can lift stored credentials with no login event at all.
That reach is what makes a single infection so hard to bound. The attacker walks away not with one password but with the surrounding context that makes it usable: which services the victim relies on, which sessions are still live, and which accounts share the same reused login.
Enterprise Compromise Risk
The scope of infostealer malware runs well past simple password theft, reaching files, applications, browser sessions, and sensitive business data. What might have been an isolated theft becomes a full system compromise, and the cleanup looks nothing like a routine reset.
Picture a mid-level employee who clicks a fake software update over lunch. Within the hour, the malware has copied their saved logins and an active session cookie, then quietly closed. Nothing looks wrong to the user.
Days later, an attacker replays that session cookie to open the employee's mailbox and send a convincing payment-change request from a trusted internal account. A password reset would not have helped, because the attacker never needed the password. That is why responding to an infostealer means weighing session validity and account behavior, not just the credential itself.
Why Session Hijacking Sets Infostealer Malware Apart
Session hijacking is the single capability that most clearly separates infostealer malware from keyloggers.
A keylogger can record a password as it is typed, but it cannot reproduce an active authenticated session. An infostealer can. When it captures a live session cookie, an attacker can pick up the victim's logged-in session and act as them without ever entering a secondary authentication code.
This is the mechanics behind a growing share of multi-factor authentication (MFA) bypass. A session cookie is proof that a login already succeeded, so an attacker who replays a stolen one never faces the second prompt that MFA is supposed to enforce. Session theft is what lets a single infection escalate so fast, because the attacker's access outlives any password change the victim makes as long as the token stays valid.
Would you notice if one of your own logged-in sessions were being used from somewhere else right now? For most people the honest answer is no, and that blind spot is what session theft exploits. Email is usually where the consequences surface first, since a hijacked mailbox becomes the launchpad for the fraud that follows.
Why Infostealers Are Harder to Spot Than Keyloggers
Infostealers are hard to spot because each stage of the attack is built to look like ordinary system activity.
The malware hides its malicious code, imitates trusted programs, and runs in memory, so antivirus and endpoint tools often miss it until the data is already gone. The techniques below explain why detection so often arrives too late:
- Layered Obfuscation: The malware arrives in encrypted or encoded scripts padded with junk functions, and because each victim receives a unique build, hash-based detection has little to match against.
- Software Impersonation: Once running, the malware borrows familiar names like update.exe or executes through trusted system utilities, so it blends in without dropping obvious files.
- Memory-Only Execution: Some stealers decrypt and run entirely in memory, take what they want, and disappear when the process closes, leaving few file-based traces to inspect.
- Environment Awareness: The malware checks for sandboxes or virtual machines and shuts down if it senses analysis, and it can read local signals like time zone and user activity to fire only on higher-value targets.
- Community Development: Crime-as-a-service markets speed the whole cycle, as developers ship updates and buyers test them against live defenses faster than defenders can adapt.
Put together, these tricks mean the infection often completes before a single alert fires. That is what pushes defenders toward behavior-based visibility that can catch small deviations early, rather than waiting for a signature that may never arrive.
Real-World Risks in the Infostealer Economy
Infostealers create enterprise risk by turning one infected device into a renewable source of access.
A single infection can surrender everything from browser vaults and password managers to VPN credentials and live session tokens in one haul. With that material, an attacker can impersonate an executive, launch a business email compromise (BEC) scheme, or move laterally through a network while drawing far less scrutiny than a brute-force intrusion would.
Session hijacking sharpens the damage. If valid tokens or cookies stay active, an attacker keeps their foothold even after the victim resets passwords, and a single infection stretches into a long-term breach that widens over time.
Stolen credentials rarely stay with whoever collected them. They sell cheaply on underground markets and feed ransomware, fraud, and espionage, while initial-access brokers bundle them for resale and turn isolated infections into supply-chain intrusions. This resale economy is how a figure like that 16-billion-record cache accumulates in the first place: not one breach, but millions of infected devices feeding the same market over months.
The link between infostealers and follow-on attacks is measurable: the Verizon DBIR found that 54% of ransomware victim domains appeared in infostealer logs or marketplace postings before the attack, based on 2024 data.
The stakes climb higher in critical sectors, where a quiet compromise at an energy, finance, or healthcare organization can turn into a major operational outage. That operational and regulatory fallout is what convinces many teams that static defenses cannot contain infostealer risk on their own.
Why Legacy Tools Miss These Threats
Legacy defenses struggle against infostealers because static indicators cannot capture the shifting behavior of identity theft.
Antivirus and endpoint detection lean heavily on signatures, file hashes, and static rules. Those methods often fall short against credential-stealing malware that changes its appearance with every build and frequently runs without writing files to disk, and attackers usually update their code faster than defenders can push new detections.
Context is the other gap. Cookie harvesting, clipboard access, and a burst of outbound data transfer each look harmless on their own, and only together do they reveal an infostealer at work. Without a way to correlate those signals, a legacy system reads each event in isolation and never sees the pattern. The problem is not that these tools are useless; it is that they were built to recognize known files, and infostealers work hard to never look like one.
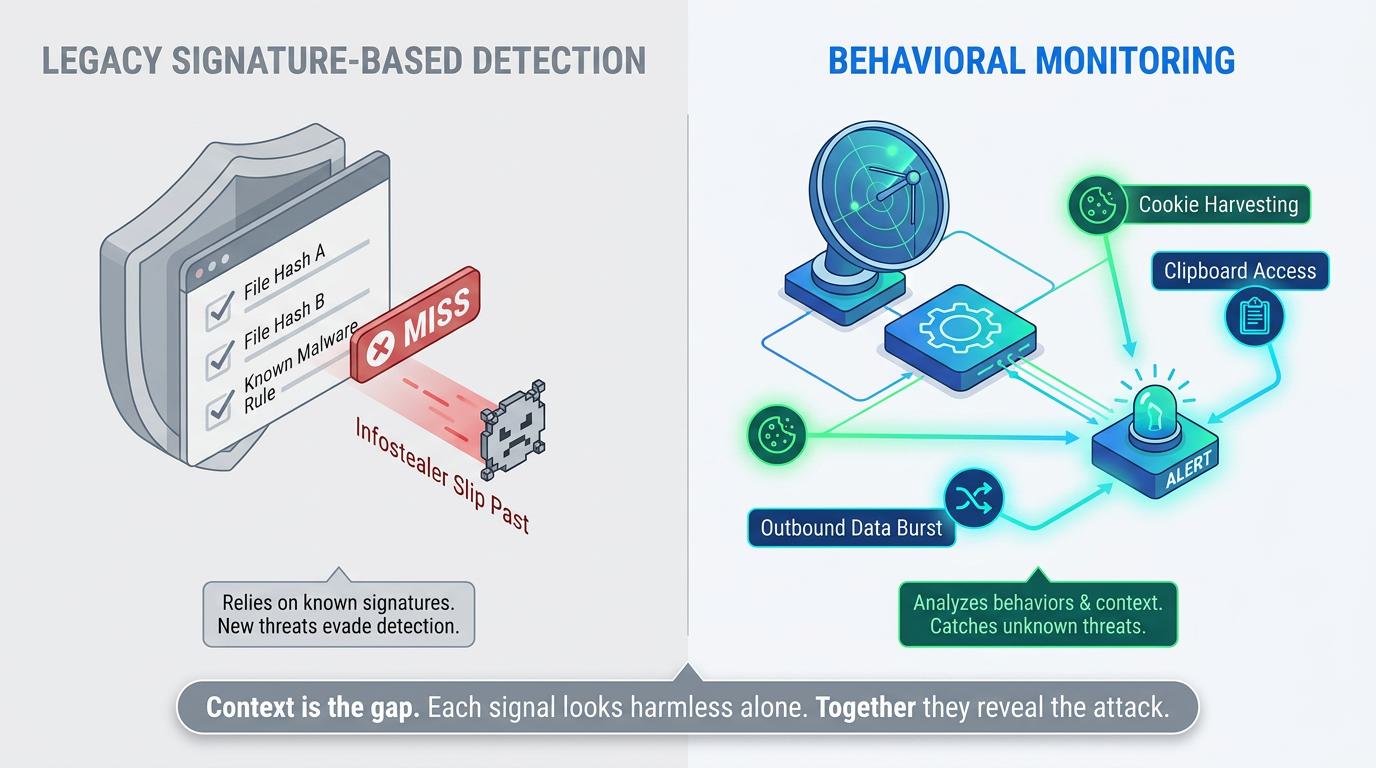
Closing that gap calls for adaptive monitoring that watches for behavioral patterns across several signals at once instead of relying on outdated indicators. That shift is what moves defenders from spotting yesterday's malware to catching the identity misuse an infostealer sets in motion.
Turning the Difference Into a Defense
Infostealer malware and keyloggers both steal credentials, but they demand different responses. A keylogger problem may end with a password reset. An infostealer problem rarely does, because the attacker is likely holding a live session and a wider bundle of harvested logins.
Treating the two as interchangeable is how a contained incident quietly becomes a breach. The teams that stay ahead plan for session validity and behavioral signals now, before the next unique build lands and the old signatures come up empty.