Product Updates
What's New
Recent Launches
The AI Security Suite Powered by Behavioral AI
Abnormal’s AI Security suite gives enterprises visibility and governance over the AI running in their business, control over the AI their employees use, and protection against AI-driven attacks being used against them.
Read the Launch BlogProactive Identity Risk Reduction for the Attacks That Matter
ISPM prioritizes identity misconfigurations based on real attack risk, helping security teams address the gaps attackers are most likely to exploit.
Read the Launch BlogEmail Security Evolved: Protect What Comes In, What Goes Out, and the People in Between
Protect what comes in, what goes out, and the people in between with new Abnormal capabilities for threat detection, data protection, and phishing training.
Read the Launch BlogAI Phishing Coach Gets Smarter: Training That Responds to Employee Behavior
Abnormal AI Phishing Coach adapts training to employee behavior, using real-world threats and behavioral signals to personalize simulations, measure risk, and build stronger security habits.
Read the Launch BlogDaily Updates
Week of Oct 12, 2026
- Oct 13, 2026Security Posture ManagementImprovement
CIS Microsoft 365 v7.0.0 Support in Security Posture Management
Security Posture Management now checks your Microsoft 365 configuration against the latest CIS Microsoft 365 Foundations Benchmark, v7.0.0.
As Microsoft 365 changes, CIS revises its benchmark: it adds controls, rewrites others and retires ones that no longer apply. This release brings SPM’s checks up to v7.0.0 and labels every change. Security teams can see which findings are new, which have refreshed guidance and which checks are going away.
With this release:
- 28 new checks based on the latest CIS guidance, marked NEW
- 121 existing checks moved to v7.0.0. The 47 with refreshed guidance are marked UPDATED
- 14 checks that CIS withdrew are marked DEPRECATED and will be removed in 30 days
- A v7 filter on the Evaluations page lets you review the new benchmark on its own
Teams that report against CIS can trust that SPM results match the current benchmark, without remapping controls by hand. The tags also make it easier to explain changes in posture results to auditors and leadership.
Read More
Week of Oct 5, 2026
- Oct 9, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of October 9
Strengthened detection of emails from newly registered domains, expanding coverage of live domain-age and registration signals
- Oct 9, 2026AI Phishing CoachImprovement
Bring Your Own CSV
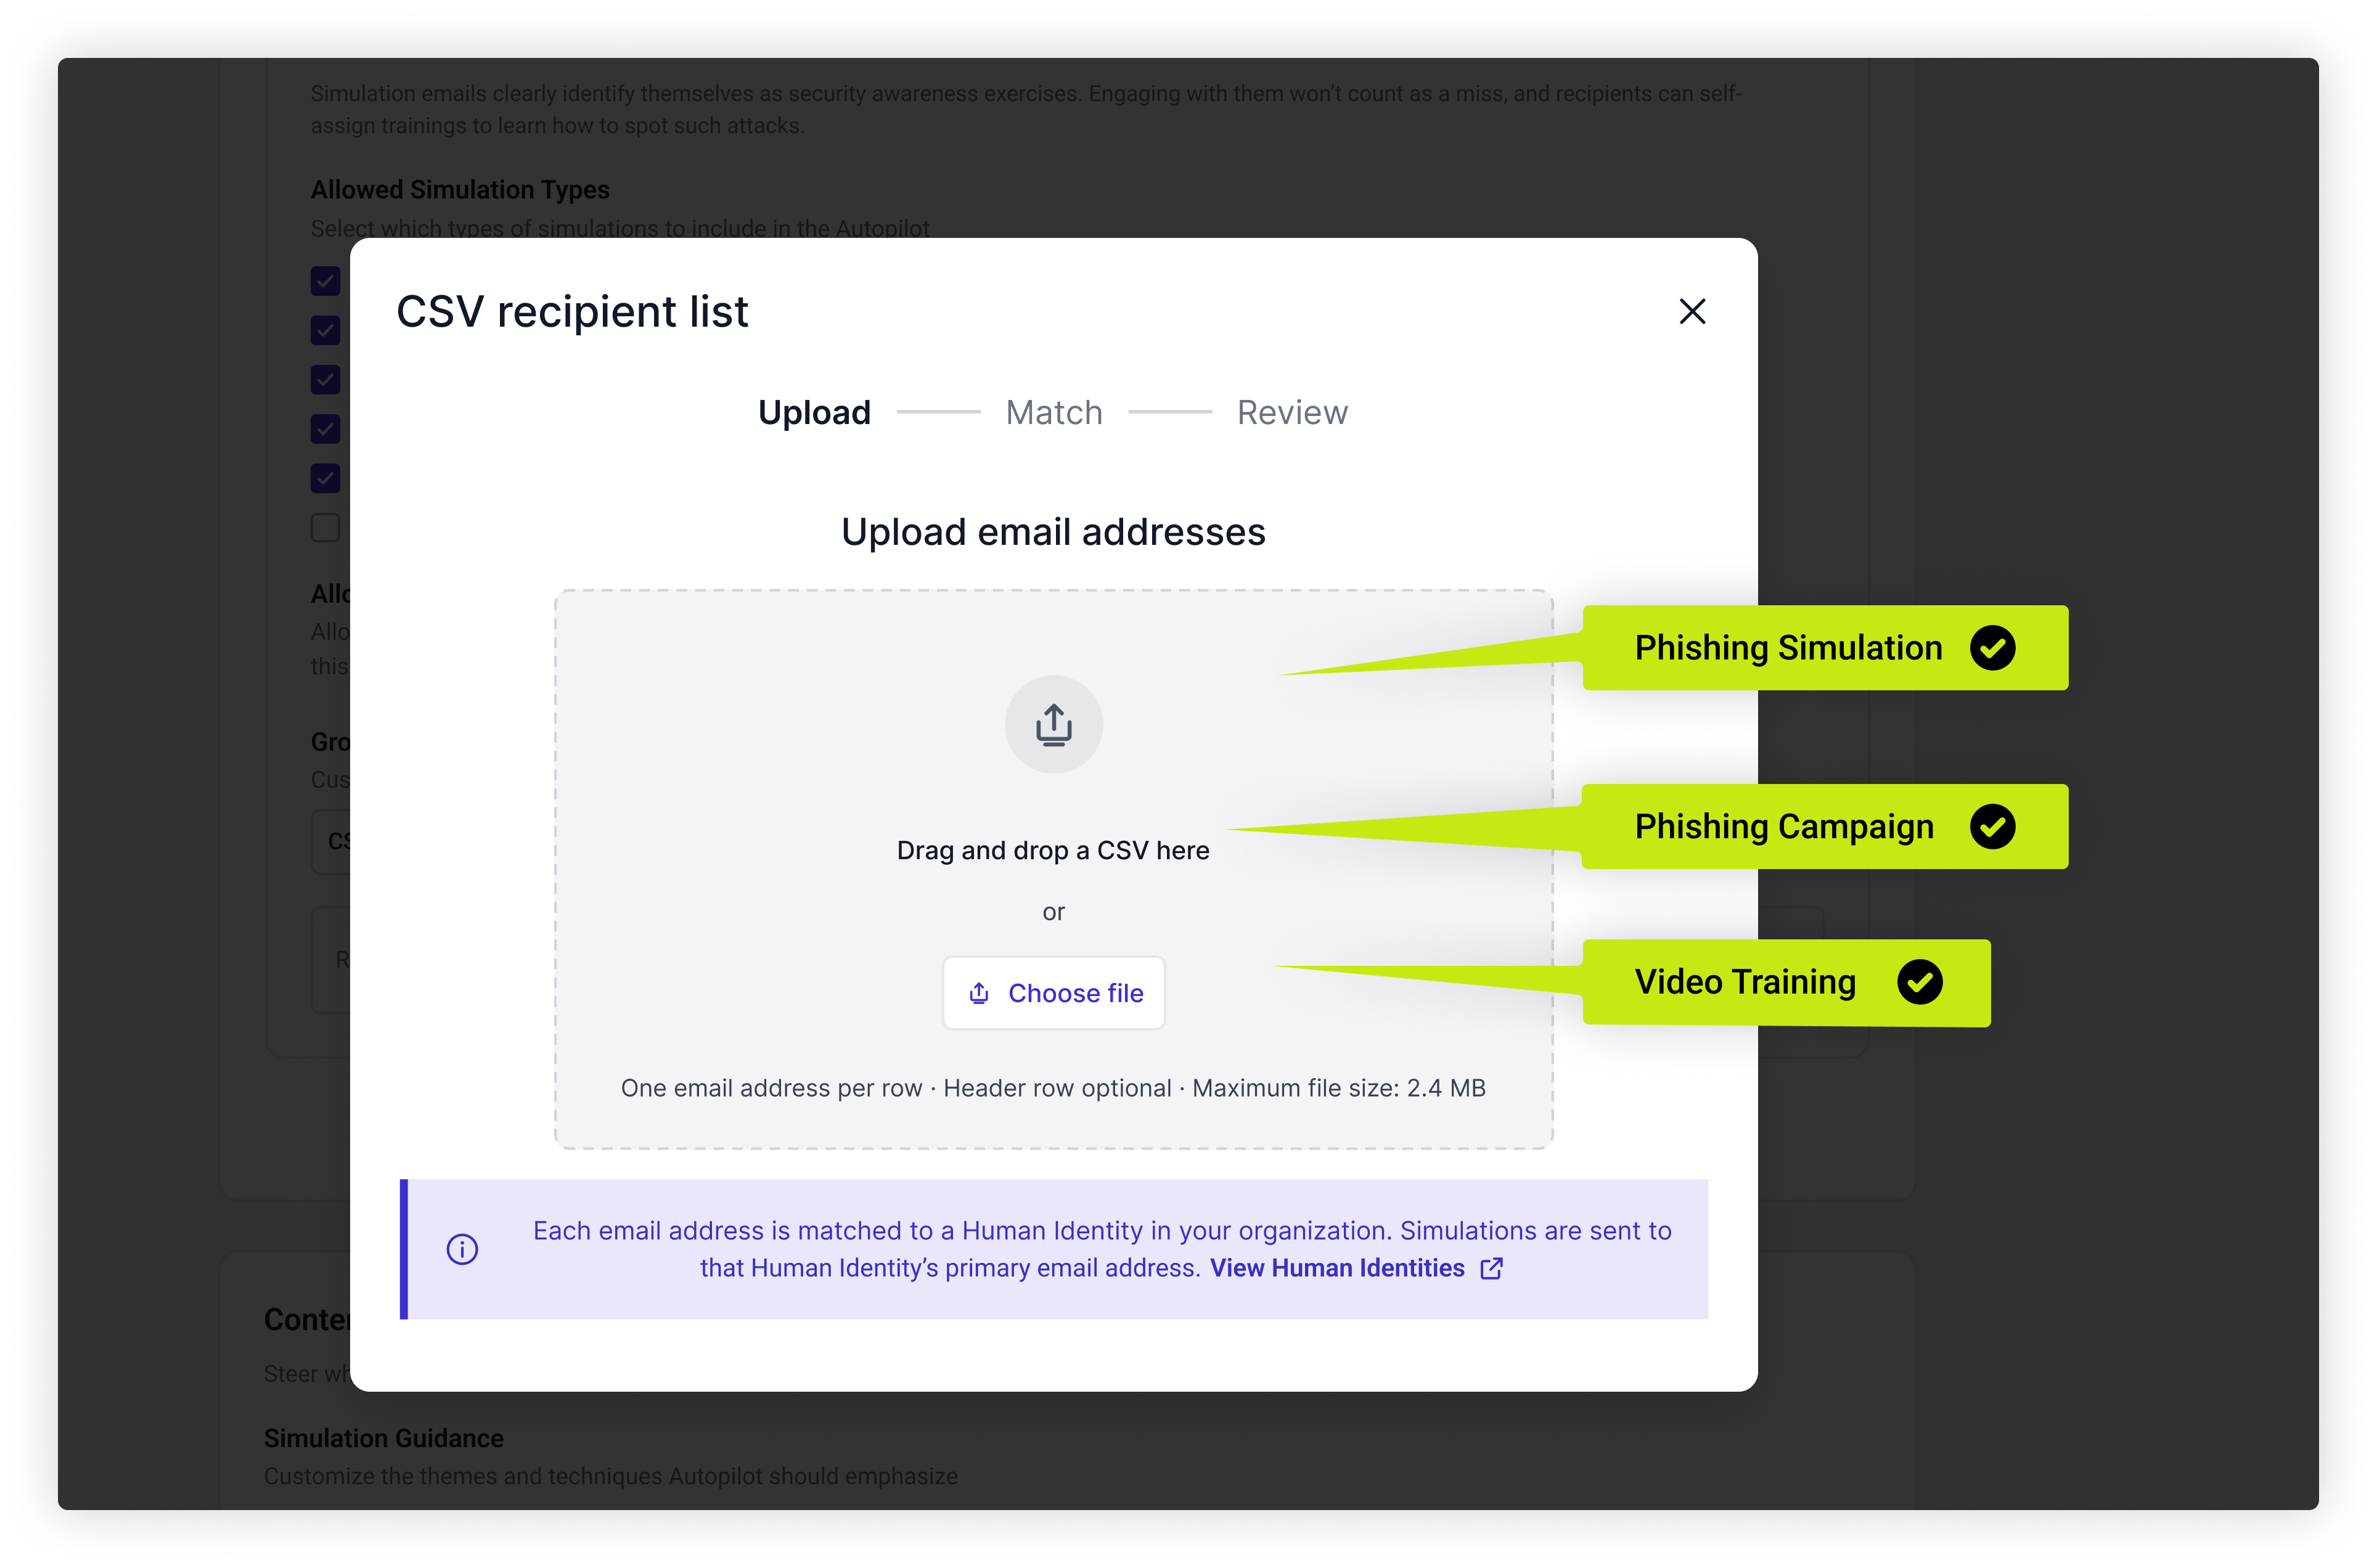
Not every directory reflects how a company is actually organized. Now admins can upload their own list of recipients via CSV instead of relying on Departments or Entra and Google Groups, and review exactly who’s included before anything goes out.
With this release:
Upload a CSV to simulation schedules, one-off campaigns, or video training assignments
Review matched, unmatched, and redirected addresses before applying the list
Edit and re-upload the file anytime to keep membership current (one email per row, up to 2.4 MB)
Security teams can now reach every subsidiary, brand, and pilot group with the right simulations and training, no matter how their directory is structured.
- Oct 8, 2026PlatformNew Feature
New Threats API Message Endpoints
Abnormal now offers two new REST API endpoints that provide direct access to threat message data: one retrieves threat message data in bulk, and the other retrieves full details for a single message.
With this Release:
- Retrieve threat messages in bulk over a selected timeframe with core metadata, pagination, and the same filters available in the Threat Log.
- Retrieve full details for one message, including attachment analysis, insights, and URLs.
Week of Sep 28, 2026
- Oct 2, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of October 2
Enhanced detection of lateral phishing from compromised senders, strengthening protection for internal-to-internal messages
- Sep 30, 2026AI Security MailboxNew Feature
AI Detection Engineer: A Faster, More Visible Response to Every Report
AI Detection Engineer acts as an extension of your SOC: when a report in Detection 360 or AI Security Mailbox is confirmed a misjudgment, AIDEN investigates it the way an analyst would, builds a sophisticated, customer-specific detector, tests it against your own traffic, and deploys it once it clears Abnormal's efficacy bar, no rule-writing required.
With this release:
See AIDEN’s fast, visible response to confirmed misjudgments reported via Detection 360 and AI Security Mailbox in one unified dashboard
Get faster turnaround from report to live fix, as AIDEN investigates, builds, tests, and deploys automatically
Track every deployed detector with full traceability to every message caught and false positive suppressed
AI Detection Engineer turns reports into faster, fully traceable responses, no rule-writing, no waiting. It's live today for all US and EU commercial customers, no configuration required.
- Sep 30, 2026AI Phishing CoachNew Feature
Executive-Ready PDF Report
AI Phishing Coach's new Executive Report turns your training program results into a leadership-ready PDF in one click. The branded report covers program performance, where risk concentrates, and which employees to coach or recognize, with AI-generated analysis alongside key charts.
With this release:
Share results with leadership using Export Executive Report on the Executive Dashboard or the Reports page
Apply any date range or filters to show a broad or targeted view
Find past and new reports in Recent Reports on the Reports page
The Executive PDF Report turns program data into a story leaders can act on, with no screenshots and no manual prep. It's live today for all AI Phishing Coach customers.
- Sep 28, 2026PlatformNew Feature
CSV Export for Supply Chain
Security and risk teams often need vendor data outside the platform, for compliance audits, board reporting, or cross-referencing with other systems. Supply Chain now supports one-click CSV export, giving teams instant, flexible access to their full vendor dataset for analysis wherever they need it.
Navigate to Behavioral Intelligence > Supply Chain and click Export to CSV
Receive your download automatically, including a Tenant column for multi-tenant environments
Simplify audits, compliance reporting, and vendor risk analysis
Week of Sep 21, 2026
- Sep 25, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of September 25
Added internal-account compromise detections to catch targeted attacks disguised as routine coworker email
Improved precision of subject-matching detection, reducing false positives without sacrificing threat coverage
- Sep 25, 2026Identity SecurityNew Feature
Adaptive Identity Reset Enrollment
Identity Threat Protection admins can now filter the Adaptive Identity Reset enrollment roster by department, job title, VIP status, and admin status, sort by name or title, and search across the complete directory.
This makes enrollment easier to manage at scale, helping admins quickly find the users they need without manually working through large rosters.
- Sep 23, 2026AI Phishing CoachImprovement
Targeted Video Training by Groups or Departments
AI Phishing Coach admins can now assign Video Training to specific AD / Entra ID groups, Google Groups, or departments instead of manually selecting and maintaining recipients. As employees join or leave a targeted group or department, they are automatically added to or removed from the training assignment.
This gives admins more control over who receives training while making targeted programs easier to manage at scale. Training stays aligned with changing teams and organizational structures without requiring admins to continually update recipient lists.
Week of Sep 14, 2026
- Sep 18, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of September 18
Strengthened detection of internal account takeover, using sender-behavior signals to catch hijacked accounts blasting phishing links to unfamiliar domains
Enhanced detection of file-share phishing from unknown senders that abuse SharePoint
- Sep 18, 2026Infiltration PreventionImprovement
Per-Applicant PDF Export
Infiltration Prevention admins can now download a PDF report for an individual flagged applicant. The report summarizes what prompted the review, the applicant’s identity and standing, and the supporting evidence in clear language.
This gives security teams a simple way to share relevant findings with people or HR teams without requiring them to access the Abnormal Portal.
- Sep 18, 2026Infiltration PreventionImprovement
Filter Flag by Reason
Infiltration Prevention admins can now filter flagged candidates by one or more flag reasons, such as Submission via VPN or Known Threat Indicator. The new Filter By control works alongside existing filters, and CSV exports reflect the filtered results.
This makes it easier to investigate groups of candidates associated with the same underlying signal without reviewing the flagged candidate list row by row.
- Sep 16, 2026AI GovernanceImprovement
Personal and Logged-Out AI Usage
The AI Governance browser extension can now detect ChatGPT conversations from personal, free, and logged-out accounts and distinguish personal usage from enterprise usage. Captured conversations are also analyzed for sensitive-data exposure.
This closes an important visibility gap by helping teams understand AI usage that enterprise provider APIs alone cannot see.
- Sep 14, 2026AI GovernanceNew Feature
AI Chat Attachment Content Scanning
AI Governance Chat Insights can now read and analyze text and images within files attached to ChatGPT and Claude conversations. Previously, AI Governance could identify that a file was attached but could not inspect its contents.
This extends visibility beyond chat text, helping teams identify sensitive information employees may be sharing with AI tools through uploaded files.
- Sep 14, 2026AI GovernanceNew Feature
SIEM Feed for AI Tools
AI Governance can now send events to existing SIEM or SOAR destinations when new AI tools are discovered, governance statuses change, or risk incidents are updated. It can also provide block and unblock instructions for customer-managed enforcement workflows.
This helps teams operationalize AI Governance without requiring analysts to continuously monitor another security console.
Week of Sep 7, 2026
- Sep 11, 2026DetectionImprovement
This Week in Detection
Weekly Detection Enhancements - Week of September 11
Enhanced detection of credential-phishing lures disguised as fake voicemail and media-player attachments
Added detections for HR-themed phishing sent from compromised internal accounts at educational institutions
Added detections for password-spray attacks that succeed on dormant, unmonitored shared mailboxes
- Sep 9, 2026AI Phishing CoachNew Feature
Per-Schedule Attack Selection
AI Phishing Coach admins can configure allowed simulation types and employee impersonation at the Group schedule level, making it possible to tailor attack mixes for different AD groups and departments instead of being tied solely to a Global schedule. (i.e. Finance only receives Credential phishing while HR receives BEC and VEC).
This gives admins more granular control over which attack types different employee groups receive. As different threats often target different parts of the organization disproportionately, programs must reflect that reality.
- Sep 7, 2026AI Phishing CoachImprovement
Attack Library Grid View
Admins can switch to a new thumbnail-based Grid view in the Attack Library to visually scan attacks and enable or disable them without opening each attack individually. Every simulation (either automatically created by AI Phishing Coach or built via Attack Creator) displays at once right in the Attack Library without extra clicks, saving time and extra steps when curating custom campaigns.