Key Insights
AI email security for financial services can help protect sensitive data, reduce fraud exposure, and support regulated email workflows. Financial institutions depend on email for approvals, client service, payment coordination, and vendor communication, which makes inbox protection a core business-control issue. Financial services teams face concentrated email risk that traditional defenses often struggle to address, and seven AI-driven strategies can help security leaders strengthen protection across high-value workflows without disrupting existing operations.
Key Takeaways
- Business email compromise cost organizations $3.05 billion in 2025, and the average financial-industry data breach now costs $6.08 million, making financial institutions a uniquely high-value target.
- Legacy secure email gateways often miss BEC attacks because these emails carry no malicious payload and still pass standard authentication and reputation checks.
- Attackers exploit settlement deadlines, FX cutoffs, and funding pressure to push staff past normal verification steps.
- Vendor and partner relationships create additional entry points for fraud, making supply-chain-aware protection as important as securing executive mailboxes.
- Behavioral AI can help identify unusual sender, recipient, and workflow patterns, flagging risky requests before employees act on them.
A recent ransomware attack involving Evolve Bank & Trust, an Arkansas-based financial institution, showed activity associated with the LockBit threat group. In the May 2024 incident, an employee clicked a malicious link, giving attackers access to internal systems and exposing sensitive data — including names, Social Security numbers, and bank account information — for roughly 7.6 million people, with the fallout also reaching customers of fintech partners Affirm, Mercury, and Wise. After Evolve refused to pay the ransom, attackers published the stolen data online.
The incident shows why email security for financial services is now a board-level priority. Cybercriminals increasingly target financial institutions for their high-value data and direct access to funds. This article outlines seven AI-driven strategies that can help you defend against evolving cyber threats.
Why Email Security Matters in Financial Services
Email security matters in financial services because email remains a primary entry point for attacks that can disrupt payments, expose customer data, and trigger regulatory scrutiny.
Financial institutions are prime targets for email attacks that go straight after customer funds, sensitive data, and core operations. A BEC attack can lead to wire transfer fraud, leaked client information, and disrupted trading systems.
When attackers compromise key email accounts, they can delay daily wire transfers, slow securities transactions, and lock customers out of their accounts. This hits revenue directly and shakes market confidence. Since most financial workflows run through email, a compromised account can create access to payment requests, internal approvals, and sensitive customer communications.
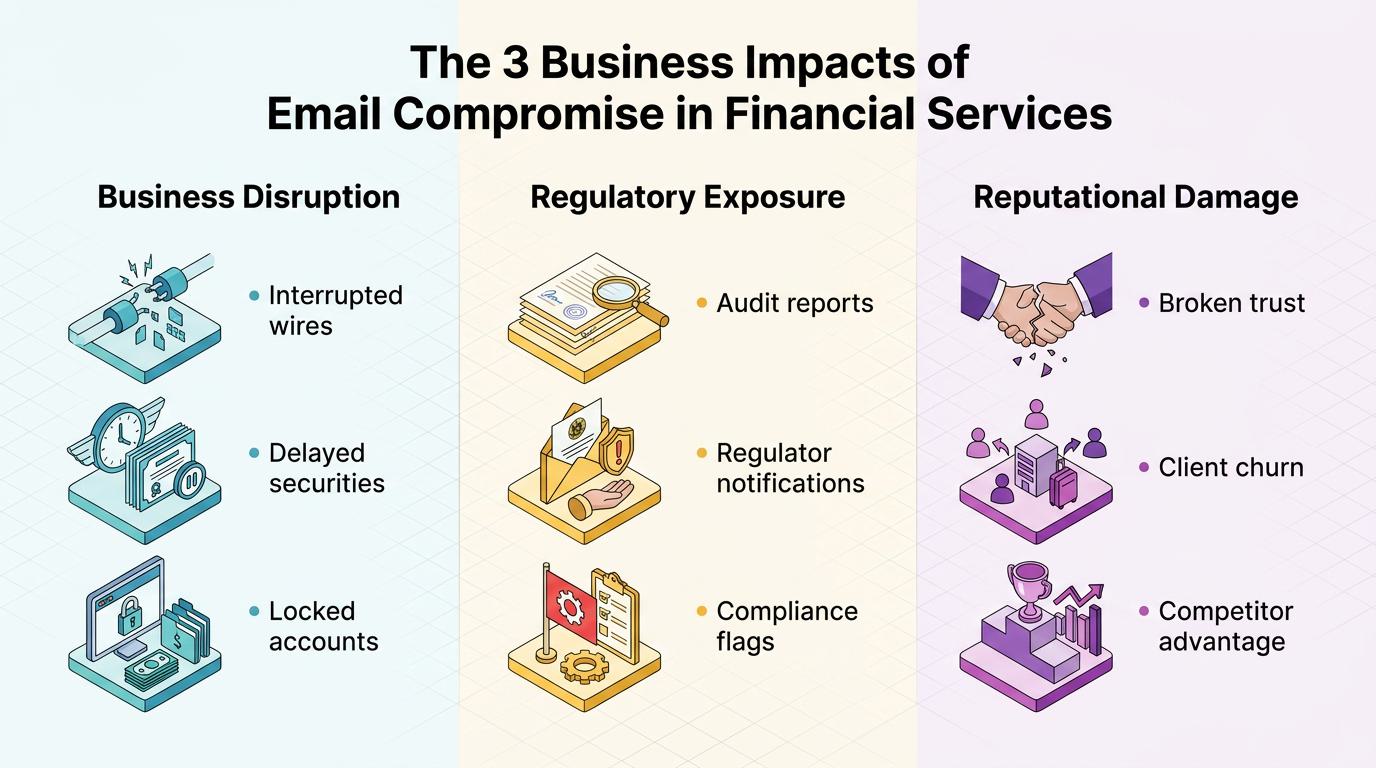
The impact usually falls into three areas:
- Business Disruption: Compromised inboxes can interrupt wires, client service, securities processing, and back-office operations.
- Regulatory Exposure: Data breaches trigger reporting obligations, regulator questions, and additional evidence requests from auditors.
- Reputational Damage: Clients expect financial institutions to protect money and data, so a visible email compromise can weaken trust quickly.
The regulatory fallout comes fast, but the real damage is often reputational. When clients see that their bank experienced a public email compromise or breach, they lose trust and may move their money elsewhere. That gives competitors a lasting edge in an industry built on credibility.
What Makes Financial Services a Target
Financial institutions face concentrated email threats because they control immediate access to funds, store high-value data, and operate under time pressure that attackers systematically exploit.
Direct Monetization Opportunities
Threat actors target direct monetization opportunities through credential phishing and sophisticated impersonation attacks. A well-timed email can redirect wire transfers, approve fraudulent payments, or push a user toward a fake login page during a busy workday.
Financial institution mailboxes become prime targets because they often contain payment templates, beneficiary instructions, trading context, and recurring approval language. According to the FBI's IC3, BEC losses reached $3.05 billion in 2025, the second-largest source of reported cybercrime losses after investment fraud. Attackers do not need malware when they can convince a trusted employee to act. A message that appears to come from a client, executive, or operations lead can move quickly through normal approval workflows, especially when the request aligns with existing business processes. That direct route from inbox to money movement makes financial services especially attractive to social engineers.
High-Value Data Repositories
Email systems contain data that criminals monetize immediately. Customer PII, account credentials, trading algorithms, and M&A intelligence frequently travel through standard business communications. Financial institutions routinely exchange payment templates, beneficiary instructions, proprietary algorithms, market-moving research, KYC documents, statements, tax forms, board minutes, audit reports, and stress-test results.
This concentration of sensitive information makes email one of the most attractive entry points for cybercriminals targeting financial services. Data breaches in the financial industry now cost an average of $6.08 million, 22% higher than the global average. Attackers can use stolen documents for identity fraud, sell credentials, or study internal communications to improve future impersonation attempts. Even when an email compromise does not immediately move funds, it can give attackers the context they need to craft more convincing follow-on requests.
Operational Deadline Pressure
Settlement windows, FX cutoffs, and end-of-day funding create natural urgency that social engineering attacks exploit effectively. When a spoofed CFO sends an urgent beneficiary update before market close, the timing aligns with normal business operations.
Staff focus on meeting critical deadlines rather than verification protocols, which makes these precisely timed attacks particularly effective. Attackers understand that treasury, operations, and client-service teams often work under strict processing windows. They use that pressure to make unusual requests feel routine, especially when the email references known counterparties, familiar transaction language, or a legitimate business process. Effective email security for financial services needs to account for this operational context, not just suspicious links or attachments.
Hierarchical Vulnerability Structures
Clear reporting chains mean staff rarely question executive directives. Attackers hijack email threads or spoof domains that pass authentication protocols, inserting requests that can reach approval workflows directly.
This account takeover risk increases with organizational complexity. Large financial institutions rely on distributed teams, delegated authority, and specialized approval paths. Attackers exploit that structure by impersonating senior leaders, client relationship managers, legal teams, or finance stakeholders who naturally make time-sensitive requests. The attack succeeds when the message fits the recipient's expectations, even if the sender identity or requested action deviates from normal behavior.
Extended Partner Networks
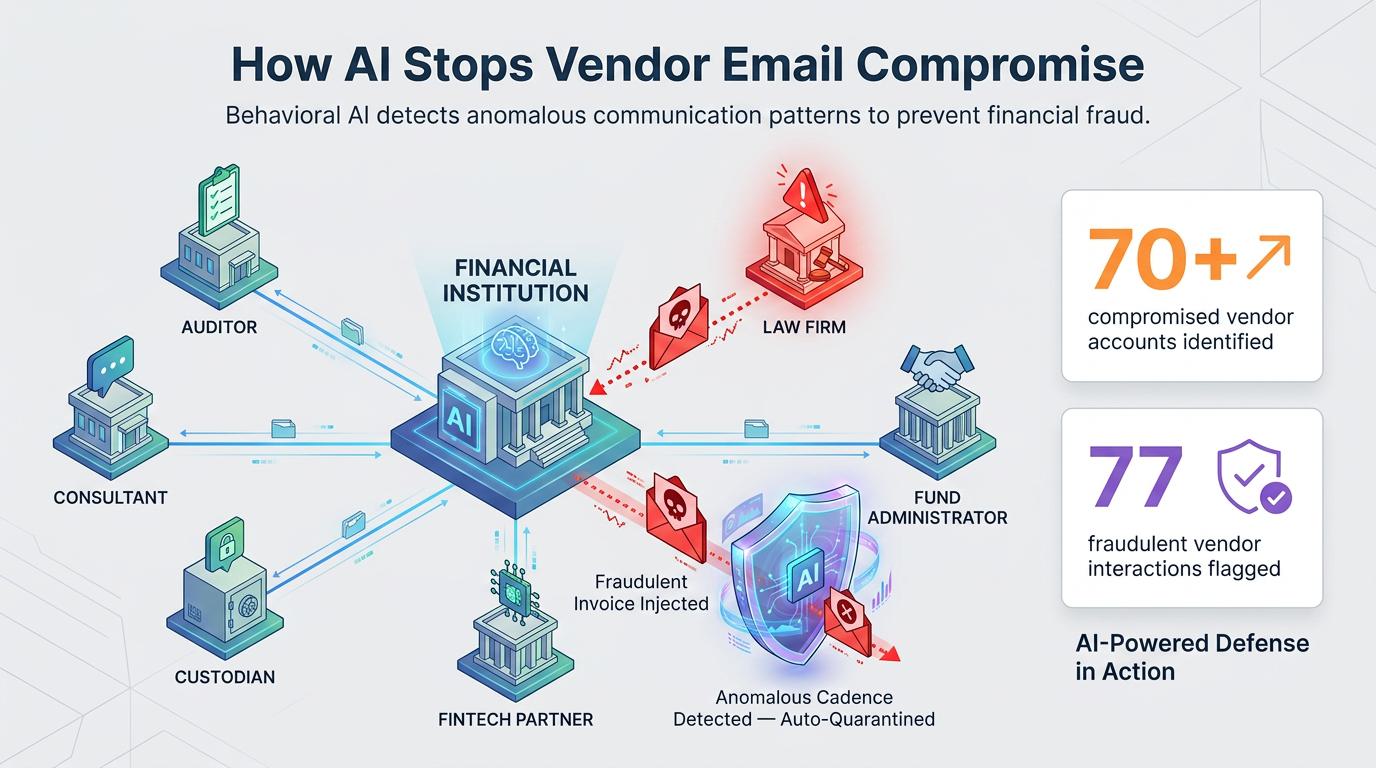
Each vendor relationship creates potential entry points where compromised suppliers can insert fraudulent invoices into ongoing conversations. Partner domains appear trustworthy, so bank detail changes seem routine until funds disappear.
Vendor email compromise is a critical risk for financial institutions because custodians, law firms, fund administrators, consultants, and fintech partners all create legitimate email traffic that attackers can abuse. Once a trusted vendor account is compromised, the attacker can join existing threads, reference real projects, and request payment changes that look operationally normal. That makes partner risk a core email security concern, not just a procurement or vendor-management issue.
Why Traditional Defenses Fall Short
Traditional email defenses often struggle in financial services because modern attacks rely on trusted relationships, business timing, and intent rather than known-bad payloads.
Missing Intent-Based Fraud
Legacy email gateways depend on static indicators, yet modern attacks in financial services hinge on human trust and business context that these tools were not designed to analyze. Content filters flag known-bad links and malware attachments, but BEC often arrives clean, with only a request to change a vendor's bank account or expedite a wire.
A technically legitimate message can still reach the inbox when it passes authentication and reputation checks. Email-based fraud can still affect firms running layered filtering stacks because the message itself may look routine. Treasury teams routinely exchange last-minute payment instructions, so urgency alone may not raise a rule-based alarm. Without behavioral context for sender-recipient patterns, workflow timing, and vendor interaction history, traditional controls struggle to distinguish routine business from high-risk fraud.
Struggling With PhaaS Evasion
PhaaS kits now serve bank-branded templates, real-time verification pages, and adversary-in-the-middle logic that can steal session cookies to bypass multifactor authentication. These campaigns also embed QR codes that victims scan on mobile devices, which can evade gateway URL rewriting.
These attacks reduce the usefulness of static URL analysis because the risky interaction may occur outside the original email inspection path. A message may contain little more than a branded prompt, an image, or a QR code, leaving few traditional indicators for rules to match. Without email, identity, and collaboration context, legacy tools can misclassify these low-signal attacks as benign, leaving account takeover and downstream fraud risk unresolved. Modern AI-enabled attacks require defensive capabilities that adapt to behavior, not just known indicators.
Overlooking Operational Blind Spots
Banks depend on sprawling networks of custodians, fund administrators, and fintech vendors. A compromised supplier can inject fraudulent invoices that look entirely legitimate. Rule-based defenses often lack the behavioral context to spot a supplier suddenly emailing outside its usual cadence or requesting payment changes outside its usual pattern.
Controls that detect threats only after delivery force employees to act as the last line of defense, an approach that often fails under quarter-end and funding pressure. Compliance controls such as encryption and DLP satisfy auditors, yet they do not validate payment intent. That creates security gaps between policy enforcement and fraud prevention. Financial institutions need email defenses that complement existing controls by analyzing identity, language, vendor behavior, and communication patterns together.
7 Ways to Use AI Email Security to Protect Your Financial Services Business
AI email security helps financial services teams identify the subtle behavioral shifts that often precede wire fraud, data exfiltration, and account takeover.
AI-driven security excels at spotting what legacy filters often miss: changes in sender behavior, recipient patterns, and workflow context. By learning how your people, partners, and clients normally communicate, modern models surface behavioral anomalies and can act before risky requests reach employees.
1. Deploy Behavioral Anomaly Detection Across Identity, Content, and Context
Abnormal's behavioral AI builds living baselines for mailboxes, vendors, and workflows, tracking who emails whom, when messages arrive, and how requests usually flow. When an off-hours message arrives from a client relationship manager instructing a large transfer to an unrecognized account, the system can flag the deviation and hold the email for review.
The model evaluates identity signals, content cues, and relational context to help detect fraud that passes SPF, DKIM, and SEG checks. For financial services teams, this matters because the riskiest messages often look normal at the infrastructure layer. Behavioral analysis adds the missing context: whether the sender usually makes that kind of request, whether the recipient usually approves it, and whether the timing fits established workflow patterns.
2. Implement AI-Native BEC and Vendor Fraud Prevention
Machine learning models can map executive communication habits, supplier invoicing cadence, and vendor interaction patterns to flag payment-related requests that deviate from trusted partner behavior. This approach helps stop silent, no-malware fraud that slips past traditional gateways.
AI can score requests based on email behavior, surface risk levels, and route suspicious messages for out-of-band verification. That helps reduce exposure without slowing legitimate payouts. Detection operates independently of links or payloads, which helps block sophisticated impersonation attacks that fool well-tuned rules engines. For finance teams, the goal is to focus review on messages that deviate from normal sender, recipient, timing, and vendor patterns without adding unnecessary approval burden.
3. Counter Generative AI-Powered Impersonation Attacks
Attackers now use large language models to draft phishing messages faster, reach a wider set of victims, and reduce the grammatical errors that once made these emails easier to spot, per an FBI–CISA advisory on AI-enabled fraud. The risk extends beyond text: fraudsters can pair email with digitally cloned senior managers on video calls to pressure staff into authorizing transfers.
While these campaigns increasingly blend email with deepfake video and voice, the primary control point remains the inbox. Abnormal's behavioral AI helps detect the email and account-based components of these scams, and organizations should pair it with additional controls for voice and videoconferencing channels. Defense must pivot from content analysis to sender-recipient relationships and historical thread behavior. Behavior-first models can flag sudden funding requests, even when they match an executive's writing style, by focusing on relational deviations rather than text alone.
4. Establish End-to-End Protection Across Cloud Email and Collaboration Tools
Banks exchange passports, tax forms, and payment instructions over email continuously. AI can monitor the same conversational graph across cloud email and connected collaboration tools such as Teams and Slack, allowing clients to send KYC documentation inbound while flagging compromised insiders who suddenly forward sensitive documents outbound.
The platform can quarantine, strip attachments, or throttle delivery based on confidence levels. Continuous learning across internal traffic helps expose lateral attacks that legacy tools often ignore, reducing dwell time through automated email remediation. This approach is especially useful for financial institutions because sensitive work rarely stays inside a single inbox. Teams discuss transactions, documents, and approvals across multiple collaboration surfaces. Email security works better when it understands those connected workflows without claiming visibility into systems outside its integrations.
5. Deploy Payment and Finance Workflow Safeguards With Contextual Intelligence
Treasury operations depend on predictable approval chains, including who requests, reviews, and approves payment changes. AI can model observable email patterns such as recurring sender-recipient behavior, vendor communication cadence, and timing around payment workflows, then intervene when something drifts. New requests to update SWIFT codes for long-standing counterparties can trigger automatic holds, while approvers receive contextual banners explaining the anomaly.
These safeguards help reduce account-takeover losses by flagging suspicious fund-transfer requests in the email workflow. While payment execution occurs in financial systems that require separate controls, email remains where many fraudulent requests begin. Contextual intelligence helps security teams evaluate whether a message fits the relationship and workflow that it claims to represent. That creates tighter payment security without adding unnecessary friction to routine client disbursements or liquidity operations.
6. Implement Supply Chain and Partner Risk Modeling
AI can model partner-originated email behavior across the financial services network, including normal domains, cryptographic posture, and communication cadence. It can then flag shifts such as newly registered look-alike domains or compromised vendors emailing outside normal business patterns.
Since vendor compromise can seed multi-company fraud, modeling supply-chain behavior protects partner communications as critically as executive mailboxes. When the system identifies sudden changes in invoice-attachment behavior or domains failing DMARC after a history of compliance, it can auto-quarantine threads and alert procurement leads to validate authenticity. This gives financial institutions a practical way to evaluate vendor-originated messages using relationship context, not just domain reputation. It also helps security teams coordinate with procurement and finance without asking employees to manually inspect every supplier request.
7. Enable Automated, Closed-Loop Response for Rapid Containment
Detection without speed often fails to stop fraud. AI triages alerts, retroactively retracts delivered threats, and disables malicious links across affected inboxes, shrinking response windows dramatically.
The platform can purge high-confidence attacks without human review, while medium-confidence cases arrive pre-correlated for analyst review. Closed-loop response gives financial services teams a scalable defense without expanding headcount. This matters because BEC, credential phishing, and vendor compromise often spread across multiple users once a campaign lands. Automated containment helps reduce analyst workload, limits user exposure, and keeps investigations focused on the highest-risk events. For overextended security teams, the value comes from faster triage, fewer repetitive tasks, and clearer evidence for post-incident review.
How Abnormal Supports Financial Services Teams
Abnormal enhances existing security stacks with AI-driven email security that analyzes cloud email, identity signals, and connected collaboration activity for high-risk financial services workflows.
Abnormal delivers AI-driven email security built for the high-stakes demands of financial services. Credential phishing attacks often target executives, payroll teams, and finance staff. Abnormal is designed to evaluate suspicious language, tone, style, and sender behavior, even when messages contain no links or attachments, helping stop phishing before it reaches inboxes.
Supply chain compromise is another critical risk. Abnormal's VendorBase™ identifies and continuously monitors vendors, assigning risk scores that help block fraudulent payment requests from compromised accounts. For account takeover attempts, Abnormal analyzes behavioral signals, login patterns, and identity signals to help auto-remediate compromised accounts. The platform complements existing email gateways, SIEMs, and SOAR workflows rather than requiring teams to rip and replace their current stack.
Abnormal's behavioral AI changed a Global 500 financial services organization's email security posture. The organization, which manages nearly $1 trillion in assets across insurance, investment, and advisory services, already ran two existing layers of email security but had no visibility into what was slipping past them.
Once enabled, Abnormal's intelligence engine delivered measurable results:
- Advanced Attack Detection: The platform surfaced 11,000+ advanced email attacks per month that had bypassed the organization's two existing security layers.
- Vendor Fraud Detection: Abnormal identified 70+ compromised vendor accounts and flagged 77 fraudulent vendor interactions within the first six months.
- Fraud Loss Prevention: These detections helped prevent an estimated $14 million in fraud losses.
- Automated Remediation: Auto-remediation of high-confidence threats reduced the security team's response time, catching attacks their other two security platforms missed.
The solution also reduced the security team's reliance on manual triage by auto-remediating the organization's largest threats. "As we move into a 'digital everything' world, protecting our customers and employees is the top priority … Abnormal makes that happen," said the organization's Associate VP of Security Operations. "Abnormal autoremediates our largest threats. It's immediate and proactive rather than reactive." A security engineer on the same team put it more simply: "Abnormal is catching things that our other two security platforms should've caught. It's like this big wall of safety."
Protect Against Evolving Email Threats
Financial services teams can strengthen email security by pairing existing controls with behavioral AI that understands trusted relationships, vendor patterns, and high-risk workflows.
Abnormal was named a Leader in the 2025 Gartner® Magic Quadrant™ for Email Security for the second consecutive year, placed furthest on the Completeness of Vision axis. It has also been named a Customers' Choice in the 2026 Gartner® Peer Insights™ Voice of the Customer for Email Security.
See how Abnormal's behavioral AI helps detect attacks that legacy defenses miss. Request a demo to see Abnormal in action, or explore customer stories for real-world results from leading financial institutions.